THE GREATEST GAMBLING STREAM OF ALL TIME!
@TheGoobr RAN UP $11.5 MILLION ON GAMDOM PLAYING JUST TWO GAMES.
I THINK WE HAVE TO CROWN HIM THE LUXE KING 🙇♂️
Two Bitcoin wallets that hadn't moved since 2010 just sent a combined 100 BTC, roughly $6.9M, after more than 16 years untouched 👀
OG coins waking up always gets people talking.
⚡️ LATEST: Two Bitcoin wallets dormant since 2010 transferred a combined 100 $BTC worth approximately $6.9 million after more than 16 years of inactivity.
LIQD co-founder Peter Kolui says he's done handing out personal gambling loans to streamers, after years of lending to the likes of TheGoobr, sometimes millions at a time.
Going forward, he says loans will only come as markers on LIQD, and only for streamers he knows and trusts.
Some of you know me as the guy who has loaned @TheGoobr and many other streamers over the years large amounts, sometimes millions at a time.
But not anymore.
1/3 🧵
Bybit has put out a security advisory over a reported Telegram for Android vulnerability, telling users to update the app right away.
Avoid unknown bots and chats, and don't open suspicious links.
Bybit Warns of Telegram Android Vulnerability, Urges Users to Update Immediately
Bybit issued a security advisory on November 13 following reports of a vulnerability in Telegram for Android, warning that a compromised device could also put other applications at risk. Bybit urged users to update Telegram to the latest version immediately, avoid unfamiliar chats and unknown bots, refrain from opening suspicious links, and trust only verified official channels.
Earlier this week, security research firm V12 disclosed a remote code execution vulnerability in Telegram’s Widgets feature, demonstrating how a bot message could launch the Calculator app on an Android device. Telegram subsequently confirmed that the vulnerability had been fixed and the update rolled out to users. Separately, on November 10, Binance warned of an iOS vulnerability known as worse_query that could allow malicious apps to read files belonging to other applications, potentially exposing crypto wallet seed phrases, private keys and login credentials.
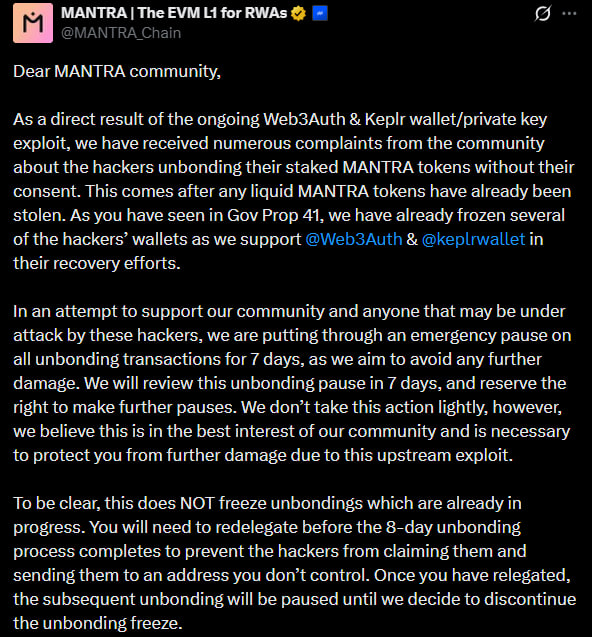
MANTRA says hackers are unstaking users' tokens after a Web3Auth-Keplr wallet exploit
emergency 7-day unbonding pause now in place. if you hold $OM via Keplr, check your wallet
Machi(@machibigbrother) has been liquidated an unbelievable 2,100+ times on @papertrade_xyz!
He's now lost $2.22M trading on the platform.
https://t.co/QvJczaX8SL
A New York federal judge has denied Novig's request to block the state from enforcing its sports betting laws against it.
Prediction markets keep running into state gambling regulators.
New York judge rejects Novig bid to block state sports betting enforcement www.yogonet.com/international/news/2026/11/12/127272-new-york-judge-rejects-novig-bid-to-block-state-sports-betting-enforcement #SportsBetting#GamblingNews#NewYork#CourtRuling#LegalNews
Mercado Bitcoin has reopened accounts in read-only mode, a week after attackers drained an estimated $49M. Customers can see balances from Nov 2, the day of the hack, but withdrawals are still frozen with no date given.
NEW: Brazilian exchange Mercado Bitcoin reopens accounts in read-only mode, a week after attackers drain an estimated $49M.
Customers can see balances as of November 2, the day of the hack, but cannot withdraw and have no date for when they can.
The exchange, which claims 4.8M customers, says it covers all losses with company funds.
It still has not explained how the attackers reached its wallets.
Withdrawals return via Pix only after users reconfirm their details, and only to accounts in their own name.
Roughly 1,816 BTC (~$116M) has now been drained through the Coldcard seed bug. Firmware 4.0.1 and later bypassed the hardware RNG, and updating won't fix seeds already made on it. Coldcard users: generate a fresh seed.
NEW: Coinkite CEO Rodolfo Novak (NVK) says it took a new AI model to find the Coldcard flaw human reviewers missed, and Bitcoin developers are pushing back.
The bug, in firmware 4.0.1 and later, bypassed the hardware random number generator and drained about 1,816 BTC, roughly $116M, from 5,200+ addresses between July 30 and August 4.
NVK cites at least 15 prior review efforts. James O'Beirne says he privately flagged Coldcard's randomness in May 2025.
A firmware update fixes new devices, not old seeds. Affected users need a fresh seed.
Polymarket traders were pricing this in all morning. Jensen Huang has resigned as Nvidia CEO and board member, effective immediately, with CFO Colette Kress named interim CEO.
Indian exchange Unocoin says "no user funds have been lost" after a Nov 9 server breach, calling its ongoing service suspension a proactive security measure.
NEW: INDIAN CEX @Unocoin DENIES "ALL FUNDS STOLEN" CLAIMS AS ITS SERVICES REMAIN SUSPENDED AFTER A NOV 9 SERVER BREACH
IT SAYS "NO USER FUNDS HAVE BEEN LOST" AND CALLS THE SUSPENSION "A PROACTIVE SECURITY MEASURE"
🔥 NEW: Tron and Tether have teamed up with Chainalysis to flag suspicious USDT transfers on Tron and help law enforcement trace and freeze funds.
https://t.co/aXTvrCBydS
SCOOP: @Gemini sells its U.K. and European operations to stablecoin payments firm @KASTxyz for under $10 million, according to a source.
@willcanny99 reports.
https://t.co/lvqTIeqXf7
TSMC Confirms Hacker Obtained Employee Data and Demanded 3 BTC, Says Internal Systems Uncompromised
According to Jiemian News, Taiwan Semiconductor Manufacturing Company (TSMC) responded on November 12 to reports of a hacker attempting to sell an alleged 6.9GB database containing 46,000 TSMC employee records on an underground forum for 3 BTC; TSMC confirmed that personal data belonging to certain current and former employees was exposed without authorization, noting that preliminary investigations link the leaked records to a third-party cloud service provider's system rather than an intrusion into TSMC's own internal IT infrastructure. The chipmaker emphasized that production operations and customer data remain completely unaffected, adding that it is notifying impacted staff and working closely with the cloud vendor, law enforcement, and external cybersecurity firms to investigate the breach.