Our founder, Edward Wu, breaks down how Dropzone AI’s SOC Analyst automates tier-one work on the Risky Business Podcast. Listen Now 🎙️ https://t.co/WcOUFJJO5h
#AI#SOCAutomation#AlertFatigue#Podcast
The Agentic SOC Alliance is bringing CISOs and vendors together on how far to trust AI agents in the SOC.
Dr. Edward Amoroso (@hashtag_cyber) of TAG Infosphere is coordinating the growing Alliance of CISO-led working groups build its blueprint. Reference architectures will be shared at RSA Conference in April 2027.
Dropzone AI is a founding member, alongside @ExtraHop and 13 other companies.
https://t.co/JakCsjvTeJ
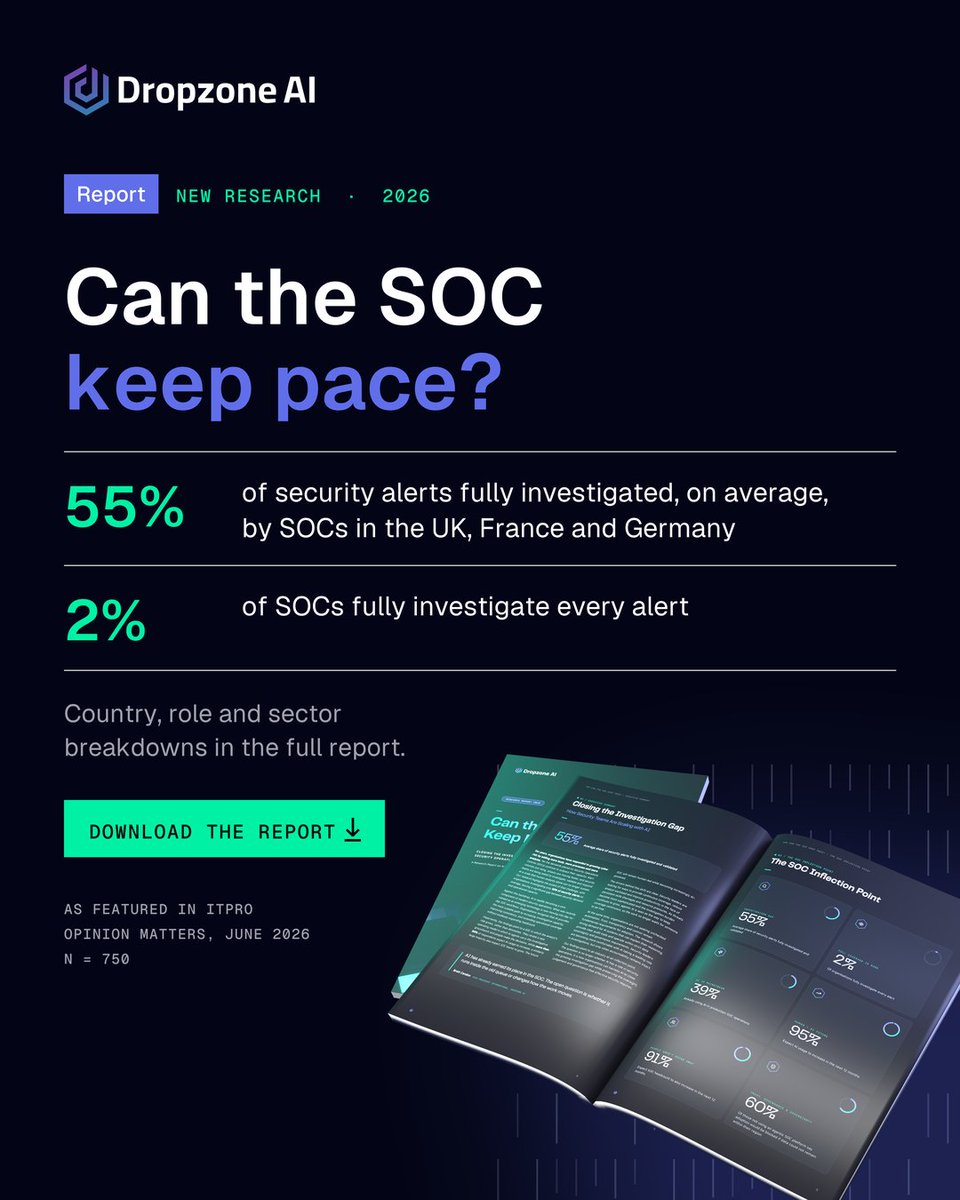
SOCs in the UK, France and Germany fully investigate 55% of their security alerts on average. Only 2% investigate every one.
New Dropzone AI research, conducted by @OpinionMatters_ with 750 security decision-makers.
Speaking to @ITPro, Brett Candon shared that "simply deploying AI is not enough. It needs to actually take workload off you".
Full report: https://t.co/HNGVRmcZfT
ITPro article: https://t.co/lp385XEjJT
#AgenticSOC #SecOps
Hosts exposing AI-related tools online grew more than 63% from October 2025 to July 2026, per the @censysio 2026 State of the Internet Report.
Censys and @DropzoneAI walk through what it means for security teams on Tuesday, December 1st, 11:30 AM ET.
Register to attend 👉 https://t.co/vurMNWiJji
We're hiring at Dropzone AI. Three remote roles in the US:
Federal Regional Sales Manager https://t.co/fVcJ5xYA9g
Account Executive, North Central (Detroit, Chicago, Minneapolis, Indianapolis) https://t.co/l2NTF2AjeC
Senior Software Engineer, Integrations (SIEM, EDR, SOAR connectors) https://t.co/yZtwIN961G
Know someone who'd fit? Send it their way.
Chisel is an open-source tunneling tool. Developers use it to reach systems behind a firewall, attackers to move data out of a network. When SentinelOne flags it, Dropzone AI investigates with your team's context.
Walk through it on the SentinelOne tab → https://t.co/dx3FdLy9V3
Monday, 8:02 AM. The overnight work is already done.
AI Threat Intel Analyst built the hunt pack.
AI Threat Hunter ran it across SIEM, EDR, and cloud.
AI SOC Analyst investigated every alert.
You decide what matters. The agents do the digging.
79% of respondents to the 2026 @SANSInstitute SOC Survey use AI or ML tools. Only 36% have built them into a defined SOC workflow. If your team is in that gap, you're in good company.
The report suggests starting with vendor AI tools that cover gaps you've documented.
A privileged AWS role just logged in from a country it's never used.
Watch Dropzone's AI SOC Analyst check identity, check behavior, and confirm what actually happened, with every step shown, not just the score.
Take the tour: https://t.co/rQk3IpHGmQ
What is an agentic SOC? An operating model, not a product. AI agents do the investigating alerts around the clock. Your analysts own every verdict.
Learn about the Agentic SOC 📖 https://t.co/fpAj0e1I1K
Cyber defense takes collective action.
@DropzoneAI is supporting @OpenAI open letter calling on organizations across technology, government, and security to strengthen cyber defenses and help make effective tools and support accessible to more defenders.
https://t.co/DuVZweyrl3
Why would a security team want AI agents to investigate fewer alerts, on purpose?
On the @TEISS teissTalk panel, Dropzone AI Founder and CEO Edward Wu explains a mode some customers asked for. It sends about 1% of alerts straight to the analysts, and the AI agents leave those alone.
The idea comes from airport security, where staff slip test items into luggage to check if TSA screeners are paying attention.
The full episode is on demand here 👉 https://t.co/w3Zu86OUPy
"I didn't need a rep to explain what an agentic SOC does. The booth explained it to me while I was still walking in."
A Black Hat attendee on the AI SOC Diner, where AI SOC Analyst and AI Threat Hunter worked real alerts, live and unscripted, all week.
The question of the week moved from "does it work" to "show your work."
If you were there, what would it take for an AI agent to earn a spot in your SOC?
36.090622, -115.179115
Course locked. Destination: Black Hat USA 2026.
Droppert grabbed his diner cap, fired up the thrusters, and set a course for Mandalay Bay. The @DropzoneAI AI SOC Diner opens Aug 4th-6th in the Business Hall at Booth 3740.
Reinforcements have arrived. 🔊
Turn on @CNBC at 5:15pm ET today because @DropzoneAI made it on national TV! 🚀
We're also in a segment on @AllAccessGarcia on the 27th. We'll share the details next week.
Dropzone AI set out to build the agentic SOC when others called it a someday idea. Now it's real, and on the national stage. 🚀
Reinforcements have arrived.
Deterministic verdicts from a non-deterministic model.
From RSAC 2026, @SecWeekly talks with Edward Wu, Founder and CEO of Dropzone AI, on how a coordinated AI agent team investigates and hunts at machine speed, and why the reasoning stays visible.
Link to the Edwards segment👉 https://t.co/Qv4UoK1Fxi
"What just happened?" Here's how the AI SOC Analyst answers it: alert → collect evidence → reason recursively → verdict in plain English → contain confirmed threats → remember.
No black box. Just the reasoning, on the record, for your team to sign off on.
See it investigate on real alerts → https://t.co/W03uoMyJ8N
AI in the SOC is going from assisting analysts to acting on its own, and the proof just hasn't caught up yet.
The 2026 Gartner® Hype Cycle™ for Security Operations maps the shift and warns hard about "GenAI washing" and "agent washing."
Download your copy 👉 https://t.co/84T3aM9ISH
The AI Threat Hunter gives you 280+ prebuilt hunt packs, ready on demand or on a schedule. Start one and it surfaces only what matters. In one real environment it caught web shell tunneling that would've taken an analyst over a week.
See what it finds 👉 https://t.co/VcHuMs8ot7
#ThreatHunting
The AI SOC Analyst shows its work. Every query, every reason behind the verdict.
You set the direction; it executes at machine speed. The AI Threat Hunter hunts what never trips an alert.
Try it on a real alert. Link to our self-guided demo 👉 https://t.co/dgdgZ2uRvj
Reinforcements have arrived.
A quiet alert queue isn't a clean environment. Lateral movement, living-off-the-land, and valid-account abuse sit below the detection threshold and surface only when someone hunts. A thorough hunt is hours of cross-tool work, so teams manage a few a quarter.
Autonomous hunting makes it hypothesis-driven, federated, and continuous, with analysts directing instead of querying.
See how autonomous threat hunting works → https://t.co/VcHuMs8ot7