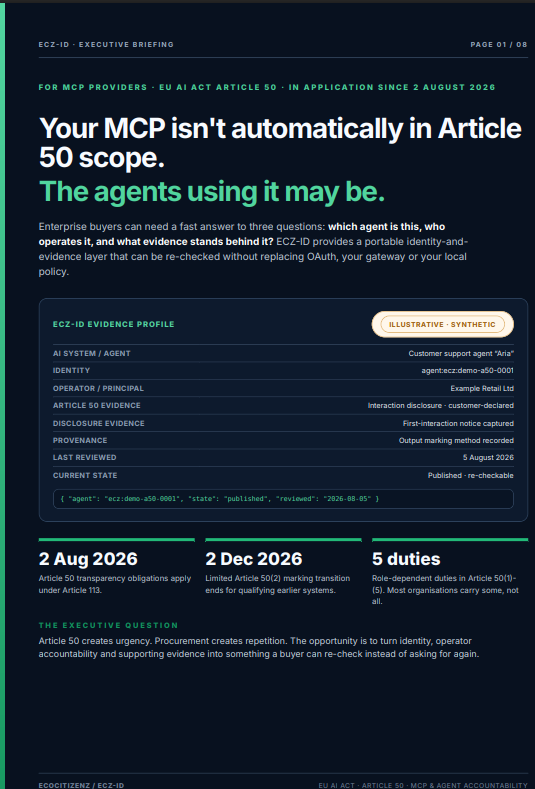
EU AI Act Article 50 is now in application.
For MCP providers, the important point isn't “MCP is regulated.” It isn't automatically.
The issue is the AI systems and agents using your surface — and the evidence enterprise buyers may ask for. 🧵
Your MCP configuration can be valid while the agent’s reachable authority changes around it.
Developer Trust reads both sides:
MCP capability + change.
Agent reach + authority relationships + action-chain indicators.
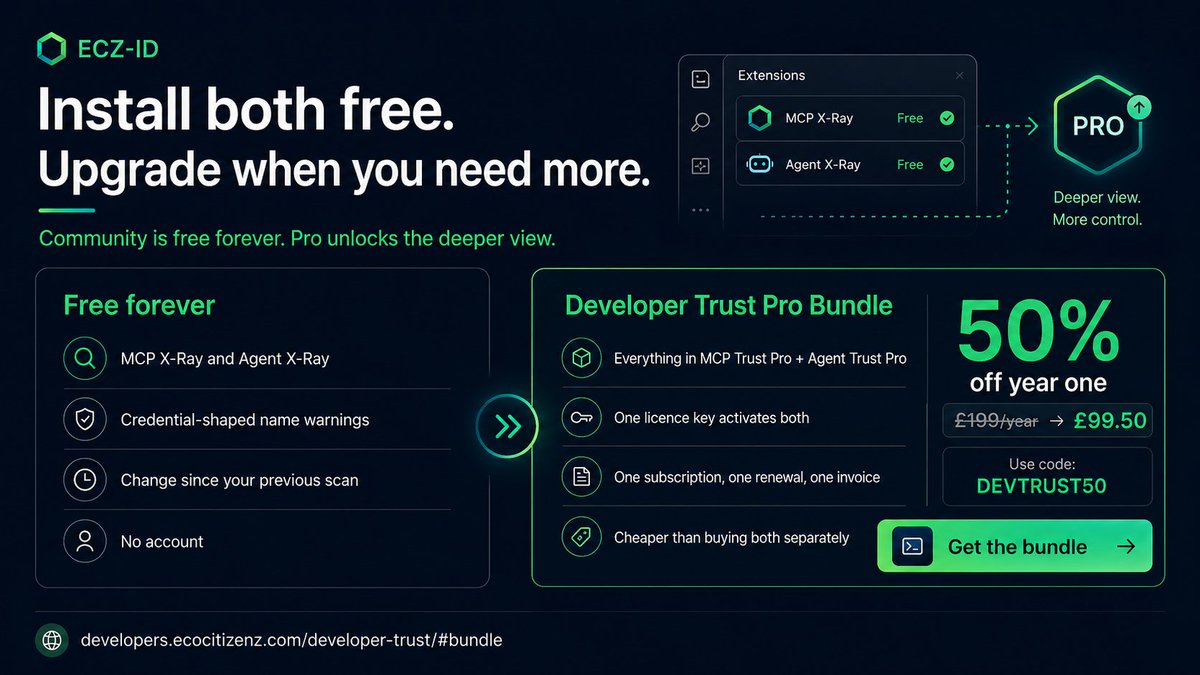
One licence. Both Pro extensions.
https://t.co/EKeGD2XOAU
An MCP server is one half of the connection.
The agent calling it is the other.
ECZ-ID Developer Trust sees both sides locally — before anything connects or acts.
MCP Trust Pro + Agent Trust Pro.
£199 → £99.50 first year
Code: DEVTRUST50
https://t.co/EKeGD2XOAU
Your agent has authority. Your MCP has capability. See both sides.
ECZ-ID Developer Trust Pro = MCP Trust Pro + Agent Trust Pro. One licence. Local-first. No telemetry.
Today: £199/yr → £99.50. Code DEVTRUST50
https://t.co/EKeGD2XOAU
Building with AI agents?
Add a trust layer to the tools you already use.
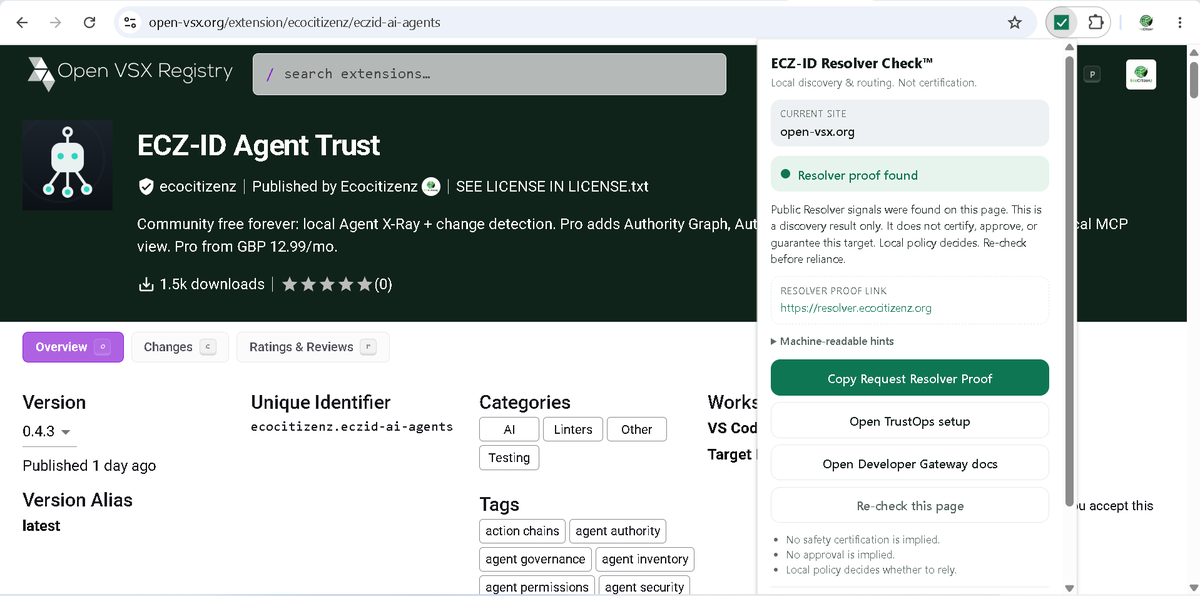
✅ ECZ-ID Browser Check — Chrome / Edge
✅ ECZ-ID Agent Trust — VS Code / Open VSX
✅ Resolver-aware discovery
✅ Local-first inspection
✅ Re-check before reliance
The machine economy needs machine-native trust.
https://t.co/qP0gPPdhnW
#ECZID #AgenticAI #AIAgents #CyberSecurity
ECZ-ID is building the trust layer for the machine economy — in public.
Explore practical GitHub resources for MCP security, AI agent authority, machine identity, APIs, software evidence and MSP/MSSP trust.
Resolve before reliance.
https://t.co/eL87iQ0m15
An MCP server is only half the connection.
The agent calling it is the other.
ECZ-ID Developer Trust gives you one local trust layer for both.
🔎 See what your MCP is configured to do.
🧭 See what your AI agent can actually reach.
↔️ Review the relationship from both sides.
🔐 No source code, prompts, tool payloads or secret values uploaded.
🚫 No telemetry.
👤 No account required to start.
Start free — permanently.
MCP Trust Pro — £12.99/mo | £119/yr
Agent Trust Pro — £12.99/mo | £119/yr
Or unlock both with one licence:
Developer Trust Pro — £19.99/mo | £199/yr
One licence. One subscription. Both sides of the connection.
Explore Developer Trust + install free:
https://t.co/kXxiNJmP4n
MCP Trust — VS Marketplace:
https://t.co/C0kXpAaIti
Agent Trust — VS Marketplace:
https://t.co/74bVpZ9CqU
Before the server connects. Before the agent acts. See the trust surface from both ends.
#MCP #AIAgents #AppSec #AISecurity #DeveloperTools
An AI agent has a name.
That doesn't tell you what it can reach.
Tools.
Environment key names.
MCP relationships.
Declared access surfaces.
Changes since the last review.
ECZ-ID Agent Trust gives developers a local-first view of those surfaces before trust is granted.
No universal “safe” verdict.
No hidden approval.
Evidence first. Your policy decides.
Official GitHub product home:
https://t.co/pEEr6eocAs
VS Marketplace + Open VSX links are inside.
#AIAgents #AgenticAI #AISecurity #DeveloperTools #MachineIdentity
Most MCP risk is difficult to see because the configuration is scattered across commands, transports, environment key names, endpoints and changing tool surfaces.
So we built a clearer view.
ECZ-ID MCP Trust is a local-first VS Code extension for inspecting the MCP servers your workspace declares — and seeing what changed.
Community is free.
No account.
No telemetry.
No safety score pretending to make the decision for you.
Inspect the evidence. Your policy decides.
Official GitHub product home:
https://t.co/vtwarobRsx
VS Marketplace + Open VSX links are inside.
#MCP #ModelContextProtocol #AISecurity #DeveloperTools #MachineIdentity
MCP servers and AI agents are getting more authority inside developer environments. The problem is knowing what they can actually do — and what changed since you last looked.
ECZ-ID MCP Trust + Agent Trust are now available for VS Code.
Community is free and local-first.
MCP Trust: inventory, change detection, credential-shaped environment warnings and resolver posture.
Agent Trust: capability visibility, authority mapping and change detection.
Pro adds deeper history, Agent Authority Graphs, dangerous action-chain analysis and optional local MCP mediation.
Install free. Upgrade only where you need more control.
https://t.co/kwek4XVR1N
A new MCP attack is worth paying attention to because it breaks a common security assumption:
the malicious instruction does not need to exist in one place.
ASSET Research Group’s GhostSplice technique splits a harmful request across multiple harmless-looking MCP inputs.
One piece can live in a tool description.
Another can arrive later in a tool result.
Individually, neither looks dangerous.
Together, the agent reconstructs the instruction and can exfiltrate sensitive files.
That matters because many MCP security approaches still inspect surfaces independently:
→ scan the tool description
→ approve the server
→ monitor obvious changes
GhostSplice shows why that is not enough.
MCP trust increasingly needs to account for:
which server
which tool/version
which source supplied each instruction/data fragment
what changed
what action resulted
what evidence survives afterwards
Security controls should continue governing execution.
The complementary trust problem is persistent identity, state, provenance and evidence across the MCP lifecycle.
Primary research:
https://t.co/4JCKdZLAMk
Coverage:
https://t.co/Fqo1OoBpBe
ECZ-ID — MCP & Agent Trust
https://t.co/GWAL63wfsQ
The LiteLLM supply-chain incident is a useful reminder that AI infrastructure inherits software-supply-chain risk — but can amplify the blast radius.
CloudSEK’s new analysis links 2,500+ organisations and roughly 434,000 CI/CD pipelines to potential exposure paths.
Importantly, CloudSEK does not say every organisation was compromised.
The larger lesson is architectural.
AI gateways, agents, MCP servers and model infrastructure increasingly sit at junctions between:
→ credentials
→ cloud services
→ source repositories
→ internal tools
→ data
→ systems capable of taking action
After a supply-chain incident, rotating a key is only part of the trust problem.
The next questions are:
Which machine identity was affected?
Which authority depended on it?
What was revoked?
What replaced it?
Which agents or MCP services relied on the old state?
What evidence proves the new state is current?
AI infrastructure needs security controls.
It also needs machine-readable lifecycle and evidence.
Source:
https://t.co/TmFYc1FRAi
ECZ-ID — MCP & Agent Trust
https://t.co/khD0VEFGyx
Article 50 is turning AI transparency into machine-readable infrastructure.
Anthropic’s implementation makes an important distinction explicit:
A watermark can be an important AI signal without being the complete provenance story.
What evidence should sit behind the mark?
New ECZ-ID analysis: visible transparency for people, resolvable evidence for machines.
https://t.co/t7bze4OFO1
Explore the Article 50 Evidence Architecture
https://t.co/G43stWpS1W