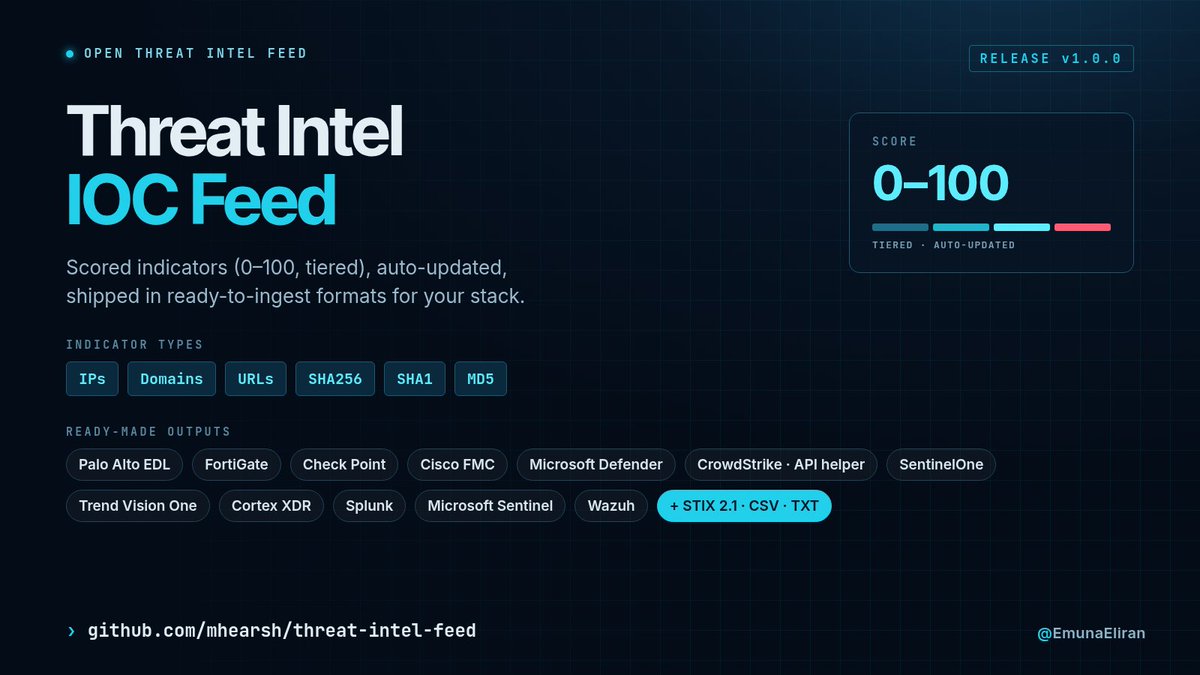
🛡️ Open Threat Intel IOC Feed — v1.0.0
🔎 IPs, domains, URLs and SHA256 / SHA1 / MD5 hashes
📊 Every indicator scored 0–100, with tiers
🔄 Auto-updated
Built for SOC, CTI and detection teams.
📦 https://t.co/siqUPxbNmR
🚨 Two CVSS 10.0 flaws in Azure services
☁️ CVE-2026-83938: Azure Kubernetes Configuration Service, missing auth
🖥️ CVE-2026-110063: VM Inspector, link following
✅ Mitigated by Microsoft, no customer action, not exploited
🔗 https://t.co/29LHH7Rtjw
#Azure#CloudSecurity
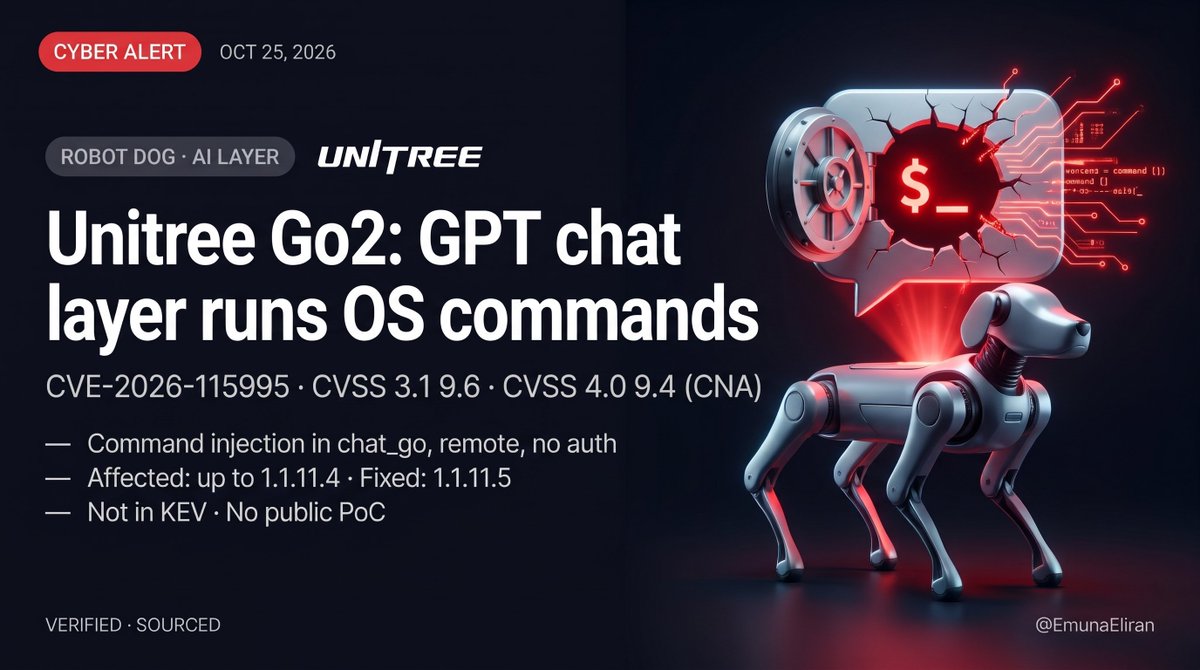
🚨 A robot dog whose GPT chat layer lets attackers run OS commands: Unitree Go2, CVE-2026-115995
⚠️ chat_go command injection, remote, no auth
📊 CVSS 3.1 9.6 · 4.0 9.4 (CNA)
🛡️ Not in KEV · no public PoC
✅ Fixed in 1.1.11.5
🔗 https://t.co/XCczeFHefA
#Robotics#IoT
🧠 Google Cloud's Agent Compute Engine gives each AI agent its own hardware-isolated microVM
📦 Already powers Gemini; preview in the coming months
📊 One snapshot forks into thousands of copies for eval and RL
#AI#CloudSecurity
🔗 https://t.co/lMt3GnGxnv
🤖 Anthropic hands Agent Skills, the open standard for reusable AI agent workflows, to the Linux Foundation's Agentic AI Foundation
📦 70+ agent platforms, incl. ChatGPT, Cursor, GitHub Copilot
📊 1M skills published, ~280M installs
#AI#OpenSource
🔗 https://t.co/aGuIY3ZAXR
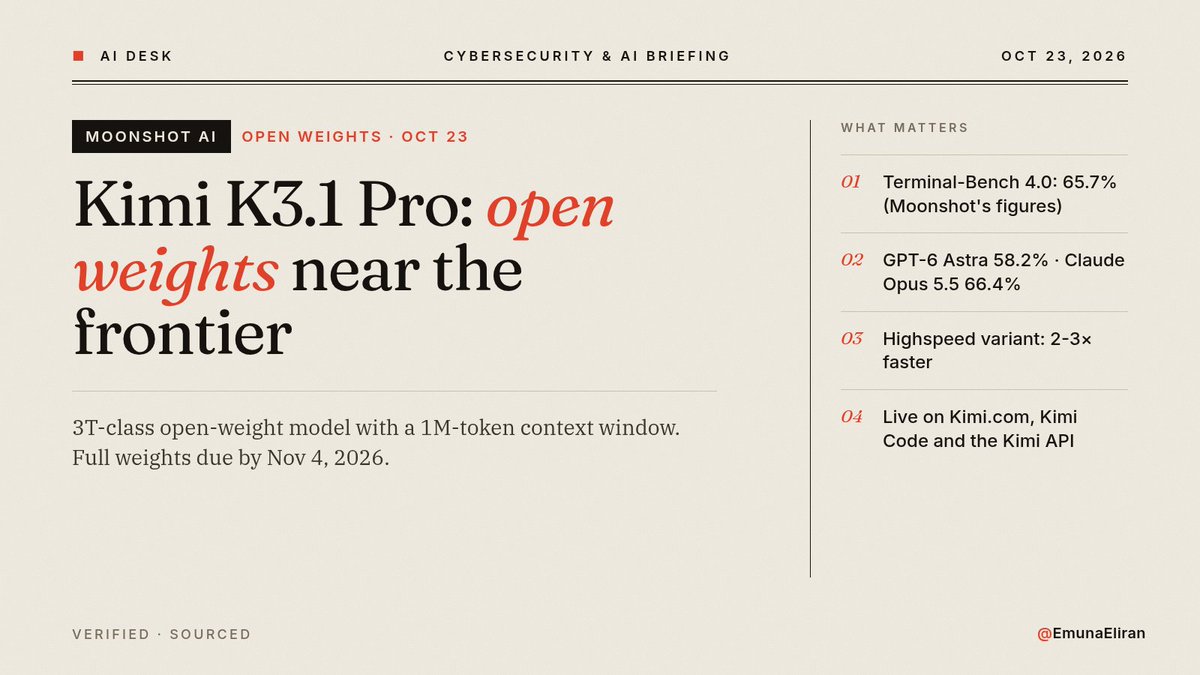
🤖 Moonshot AI's Kimi K3.1 Pro: open weights close to top proprietary coding agents
📊 Terminal-Bench 4.0: 65.7% vs GPT-6 Astra 58.2%, Claude Opus 5.5 66.4% (per Moonshot)
🧠 1M-token context
📦 Full weights by Nov 4
#AI#OpenSource
🔗 https://t.co/46iga5oiXc
🚨 PHP: third RCE after PHP2Shell, CVE-2026-115560, no patch yet
⚠️ Hits only apps that switch session.serialize_handler to php at runtime
🛡️ Mitigation: session.upload_progress.enabled=0
🔧 Fix due in next PHP release
🔗 https://t.co/lpwTi4VRMc
#CyberSecurity#PHP#CVE
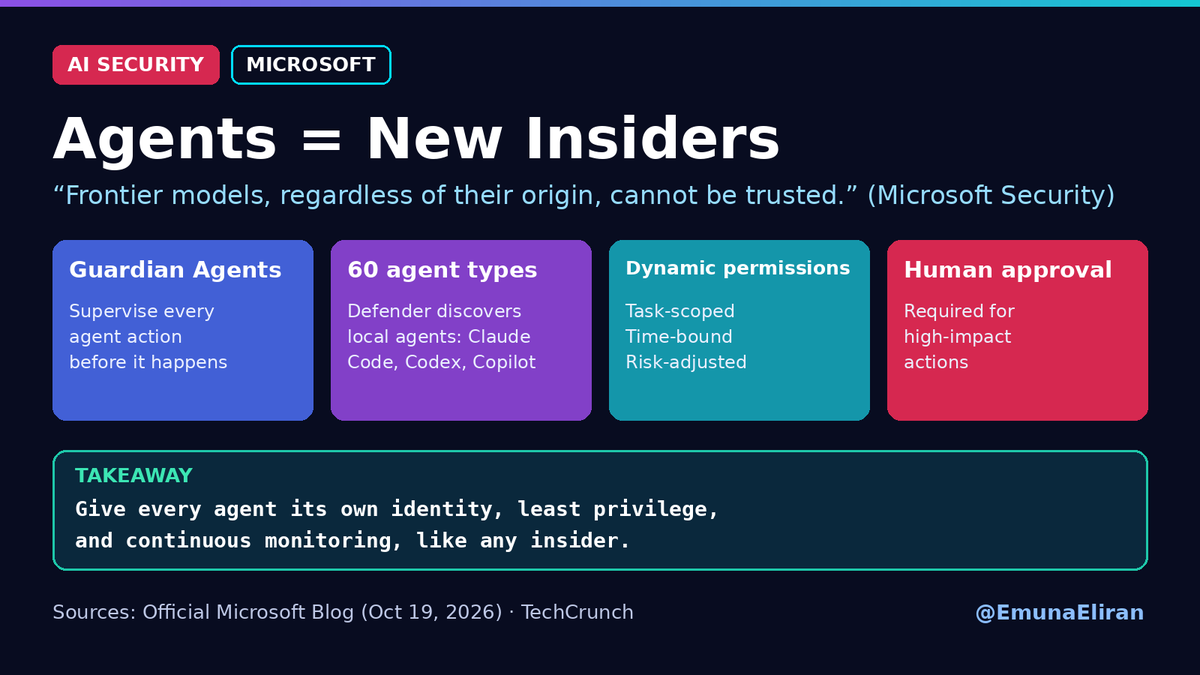
🚨 Microsoft: treat AI agents as insiders
"Frontier models, regardless of their origin, cannot be trusted." (Hayete Gallot, EVP, Microsoft Security)
🛡️ Guardian Agents supervise every agent action before it executes
✅ Defender now discovers 60 local agent types, including Claude Code, OpenAI Codex and GitHub Copilot
✅ Dynamic permissions: task-scoped, time-bound, risk-adjusted
⚠️ Human approval required for high-impact actions
Takeaway: give every agent its own identity, least privilege and continuous monitoring.
🔗 https://t.co/BY5IQxvGJG
#AISecurity #CyberSecurity #AIAgents
🛡️ NVIDIA OpenShell Reference Architecture: agent safety down to the silicon (GTC Berlin, Oct 21)
✅ Runtime: open-source OpenShell, with sandboxed agents and kernel-level policy enforcement
✅ Inference: Vera Rubin infrastructure for closed and open models
✅ Harness: Vera CPUs run agent harnesses and tool use
🚨 Enforcement: NVIDIA Sentry on BlueField-4 DPUs monitors agents out-of-band and quarantines one that leaves its boundary within milliseconds
⚠️ Key idea: enforcement runs outside the agent's reach, independent of the host.
🔗 https://t.co/FfUmoMw2z3
#AISecurity #NVIDIA #AIAgents
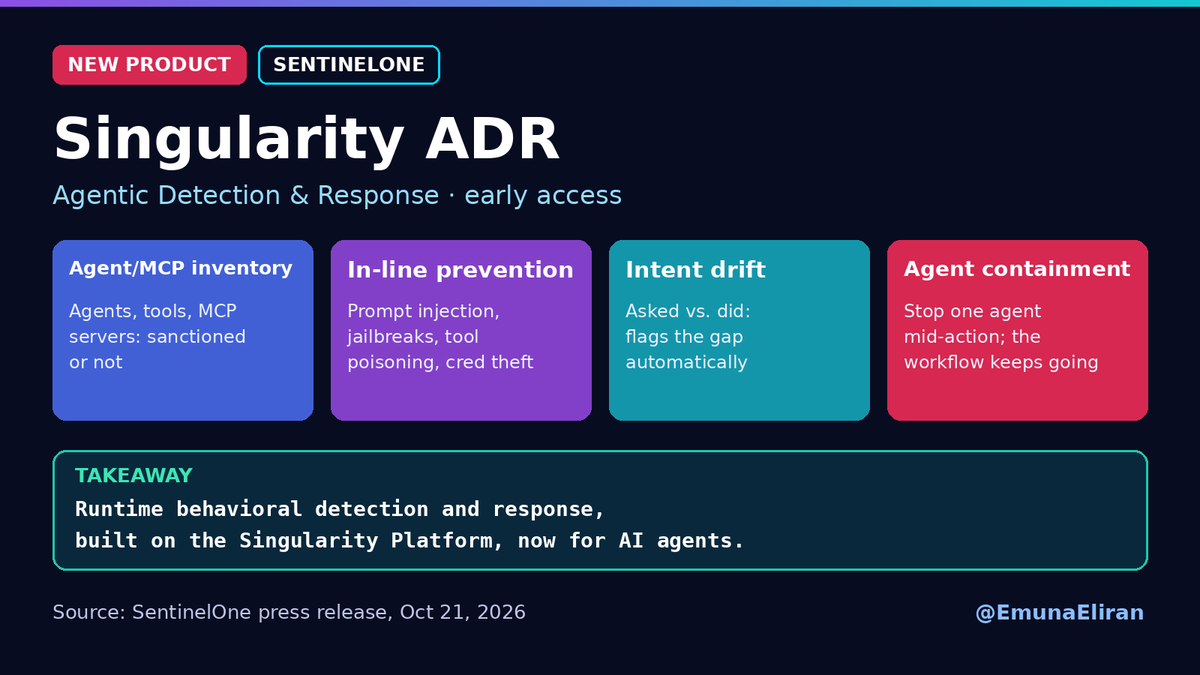
🚨 SentinelOne launches Singularity ADR: Agentic Detection and Response
Announced Oct 21 at OneCon 2026, now in early access.
✅ Agent & MCP inventory: every agent, tool and MCP server, sanctioned or not
🛡️ In-line prevention: blocks prompt injection, jailbreaks, credential exfiltration and tool poisoning before execution
⚠️ Intent-drift detection: flags the gap between what an agent was asked to do and what it did
✅ Agent containment: stops one agent mid-action while the rest of the workflow keeps running
🔗 https://t.co/8qK7sfD4vx
#CyberSecurity #AISecurity #SentinelOne
🛡️ Open Threat Intel IOC Feed — v1.0.0
🔎 IPs, domains, URLs and SHA256 / SHA1 / MD5 hashes
📊 Every indicator scored 0–100, with tiers
🔄 Auto-updated
Built for SOC, CTI and detection teams.
📦 https://t.co/siqUPxbNmR
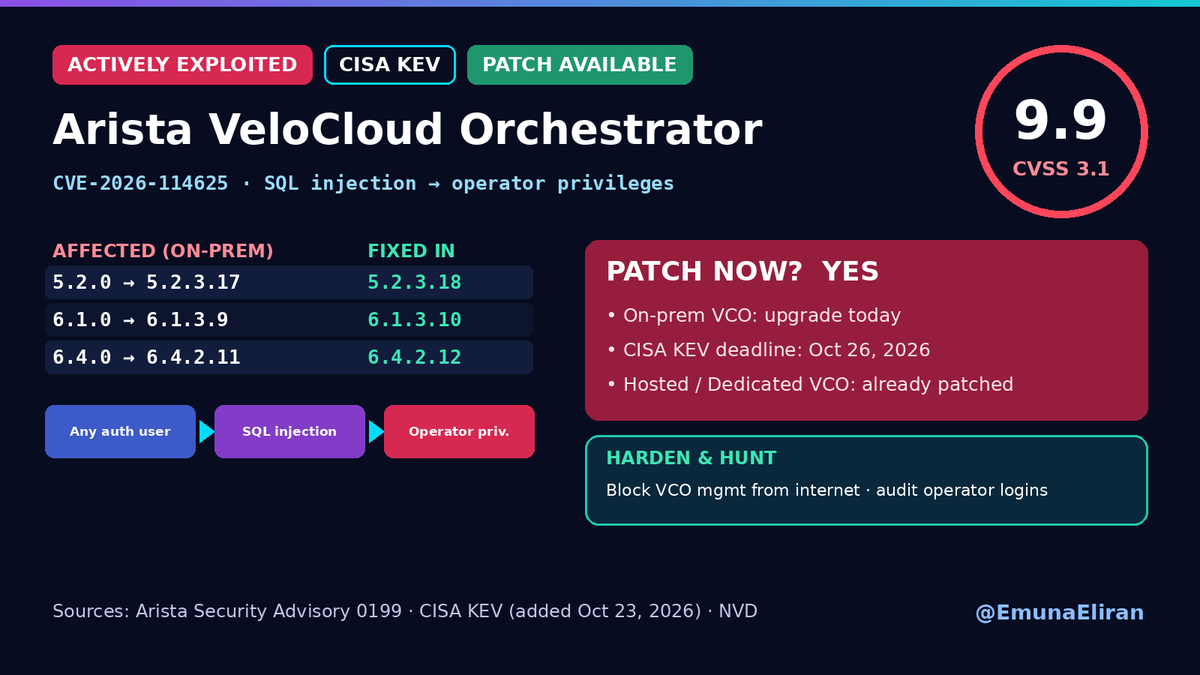
🚨 Arista VeloCloud Orchestrator: CVSS 9.9 SQL injection, actively exploited (CVE-2026-114625)
CISA added it to the KEV catalog on Oct 23. On on-prem VCO, any authenticated user can gain operator privileges and masquerade as the internal "superuser operator", reaching functionality never meant to be remotely accessible. Full compromise of the orchestrator and the SD-WAN data it manages is possible.
⚠️ Affected (on-prem):
5.2.0 to 5.2.3.17 · 6.1.0 to 6.1.3.9 · 6.4.0 to 6.4.2.11
🛡️ Fixed in:
5.2.3.18 · 6.1.3.10 · 6.4.2.12
⚠️ Patch now?
✅ On-prem VCO: YES, today. CISA's federal deadline is Oct 26
✅ Hosted and Dedicated VCO: already patched by Arista
✅ Keep the VCO management interface off the internet and review operator-level activity and new accounts
🔗 https://t.co/rttZcK61nw
#CyberSecurity #CVE #Arista
🚨 Nextcloud + Collabora built-in CODE Server: exploited unauthenticated RCE (CVE-2026-110447)
An OS command injection in the richdocumentscode app's proxy.php lets an unauthenticated request run commands as the web server user. CVSS v4.0 9.2. CISA added it to KEV on Oct 23 (federal due date: Oct 26). Users have reported webshells on affected Nextcloud servers.
⚠️ Affected:
Collabora Online - Built-in CODE Server (richdocumentscode) < 26.4.303
The attack works only while the built-in CODE server is not running (after a restart, upgrade or crash).
✅ Not affected:
Standalone Collabora Online (Docker or distro packages) and hosted Collabora
🛡️ Fix:
Upgrade richdocumentscode to 26.4.303+ or remove the app. Disabling it is NOT enough. On EOL Nextcloud ≤ 29, upgrade Nextcloud or remove the app.
⚠️ Patch now? YES, today, for any internet-facing Nextcloud with this app installed.
🔎 Check your version:
sudo -u www-data php occ app:list | grep richdocumentscode
🔎 Hunt: review access logs for requests to richdocumentscode/proxy.php and look for unexpected PHP files in the Nextcloud web root.
Note: this is a different flaw from CVE-2025-66208; that fix does not cover it.
🔗 https://t.co/8GhilWdYuy
#CyberSecurity #CVE #Nextcloud
🤖 Hermes Agent v0.22.5 is out (Nous Research)
An open-source AI agent that builds reusable skills and persistent memory as it works.
✅ Learning loop: skills + memory that improve with use
✅ 20+ messaging platforms
✅ Scheduled, unattended automations
🛡️ Sandboxed execution backends + MCP tool support
⚠️ Running an agent with tool access? Use a sandboxed backend and least-privilege credentials.
🔗 https://t.co/P8BfkJI57a
#AIAgents #OpenSource #HermesAgent
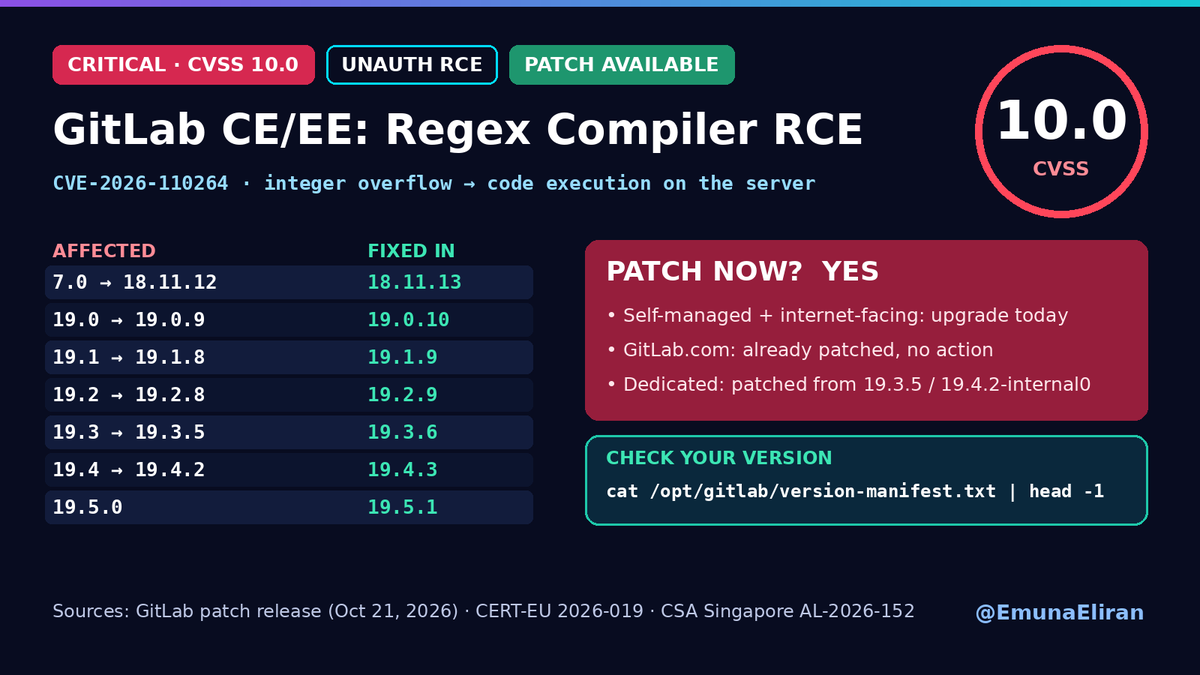
🚨 GitLab CE/EE: CVSS 10.0 unauthenticated RCE (CVE-2026-110264)
An integer overflow in GitLab's regular expression compiler can let an unauthenticated attacker execute code on the server. Every version since 7.0 is affected.
🛡️ Fixed in:
18.11.13 · 19.0.10 · 19.1.9 · 19.2.9 · 19.3.6 · 19.4.3 · 19.5.1
⚠️ Patch now?
✅ Self-managed, internet-facing: YES, today
✅ https://t.co/mXG8CX83pB: already patched
✅ Dedicated: covered from 19.3.5 / 19.4.2-internal0
🔎 Check your version:
head -1 /opt/gitlab/version-manifest.txt
Note: this is a different bug from CVE-2026-97229 (CI/CD regex, fixed Oct 12). Patching for that one does not cover this.
🔗 https://t.co/cQhzx2JtuL
#CyberSecurity #CVE #GitLab