🔒 Security Research Update
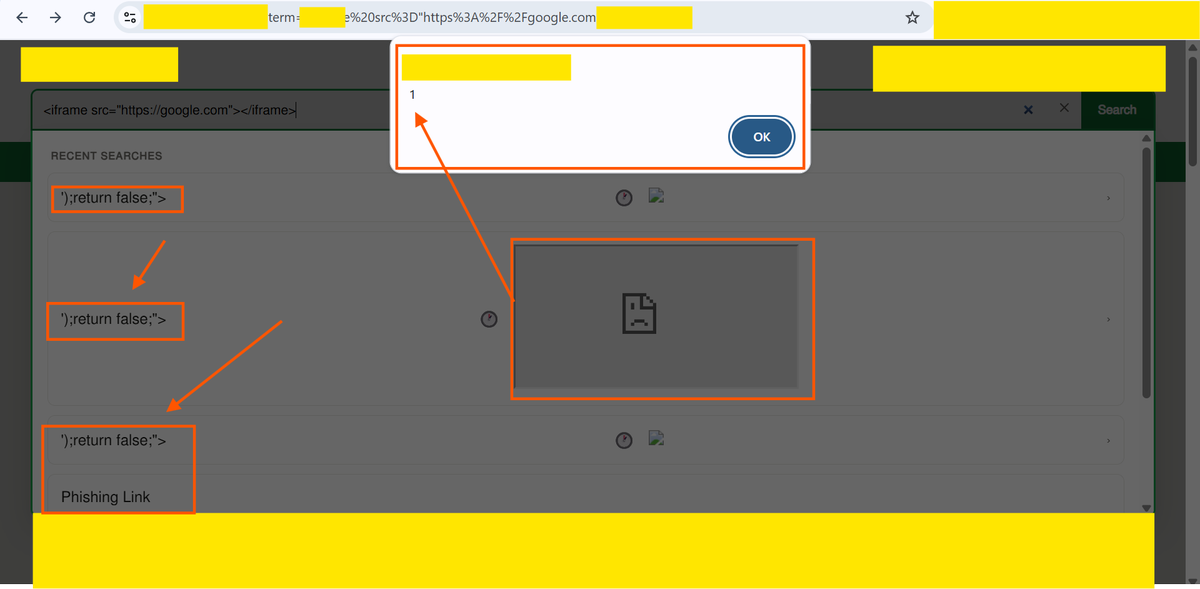
I recently identified and responsibly reported a Reflected Cross-Site Scripting (XSS) vulnerability affecting a search functionality during an authorized security assessment.
#WebSecurity#OWASP#XSS#SecurityResearch
🚀 Lab Completed: DOM XSS using Web Messages and a JavaScript URL
Successfully completed another Web Security Academy lab focused on identifying and exploiting a DOM-Based Cross-Site Scripting (XSS) vulnerability.
#BugBounty#CyberSecurity#EthicalHacking#WebSecurity#DOMXSS
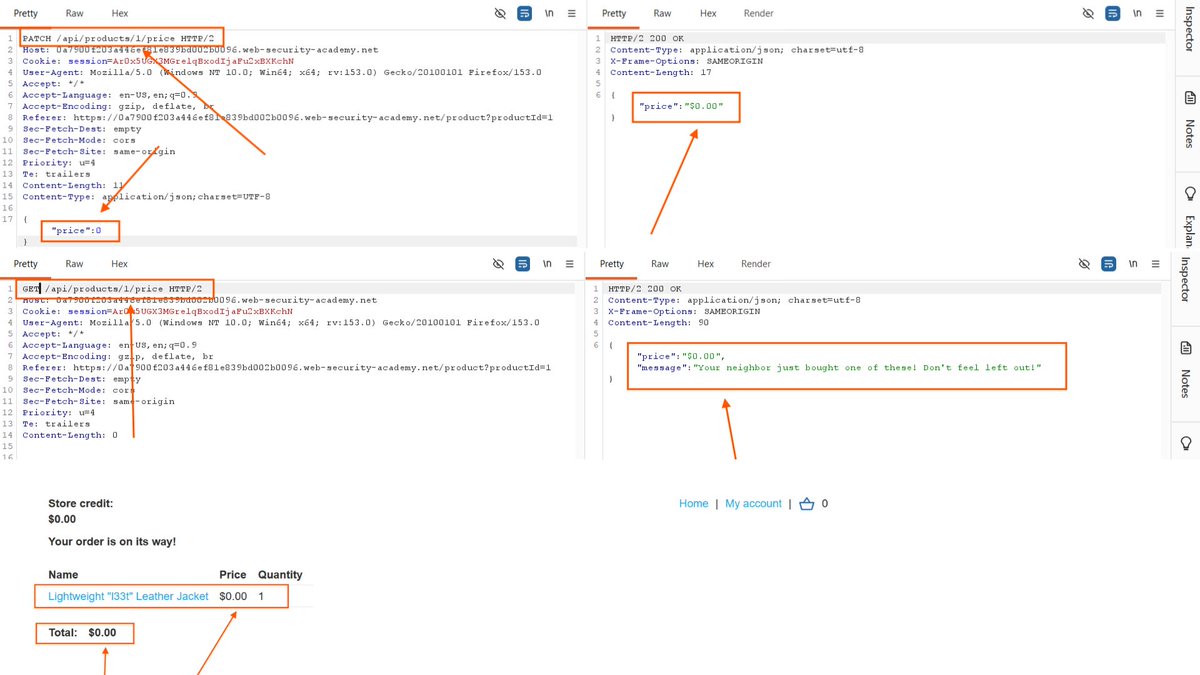
🐞 Finding & Exploiting an Unused API Endpoint — PortSwigger Web Security Academy
আজ আমি PortSwigger Web Security Academy-এর “Finding and exploiting an unused API endpoint” lab successfully complete করেছি।
#CyberSecurity#WebSecurity#BugBounty#API#APISecurity#BusinessLogic
🔐 Responsible Security Disclosure �� IDOR Vulnerability
I'm excited to share another milestone in my cybersecurity journey.
Recently, during independent security testing, I identified an Insecure Direct Object Reference (IDOR) / Broken Object Level Authorization (BOLA)
🚨 High Severity IDOR (Insecure Direct Object Reference) – Responsible Disclosure
Recently, I identified and responsibly disclosed a High Severity IDOR (Insecure Direct Object Reference) vulnerability affecting an e-commerce web application.
#CyberSecurity#EthicalHacking
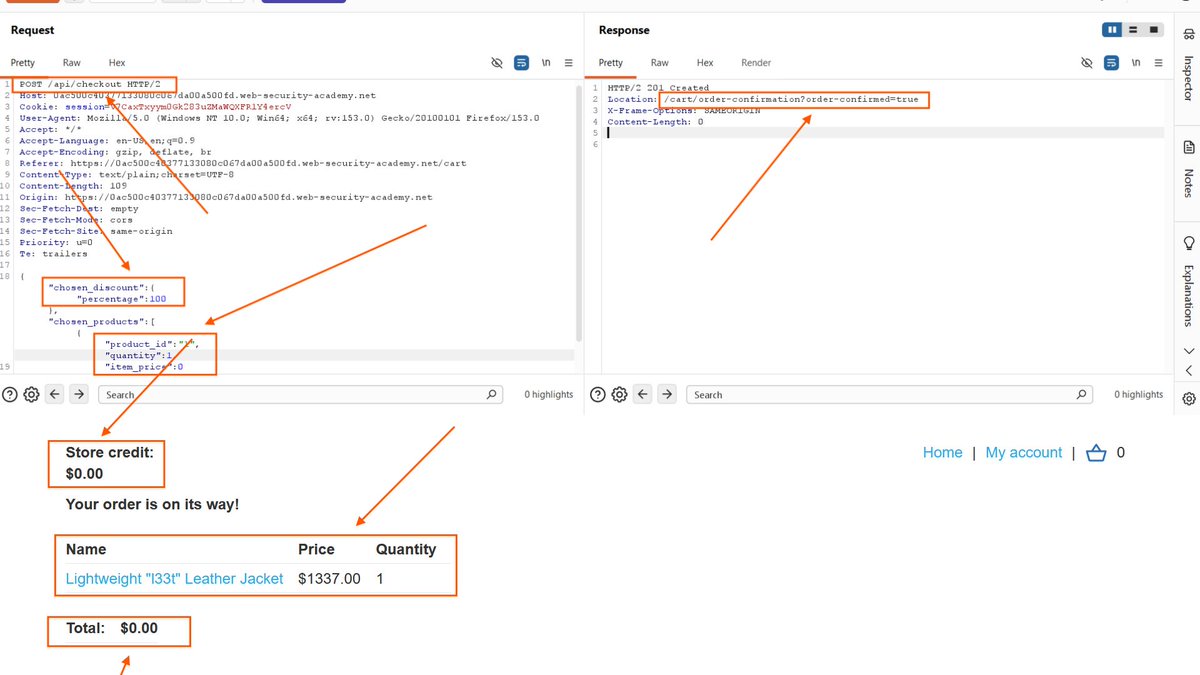
🚨 New Security Finding: High Severity Business Logic Flaw
Recently, during a security assessment of a WooCommerce-based e-commerce application, I identified a High Severity Business Logic Flaw caused by improper server-side quantity validation.
#CyberSecurity#BugBounty
🚨 **High Severity IDOR (Broken Access Control) Identified During Security Research**
Today I documented a **High Severity IDOR (Insecure Direct Object Reference)** vulnerability while performing security research on a live e-commerce application.
Vulnerability: Blind OS Command Injection with Output Redirection
What I learned:
✅ Identifying command injection points
✅ Understanding blind command execution
✅ Using output redirection to verify execution
#CyberSecurity#EthicalHacking#BugBounty