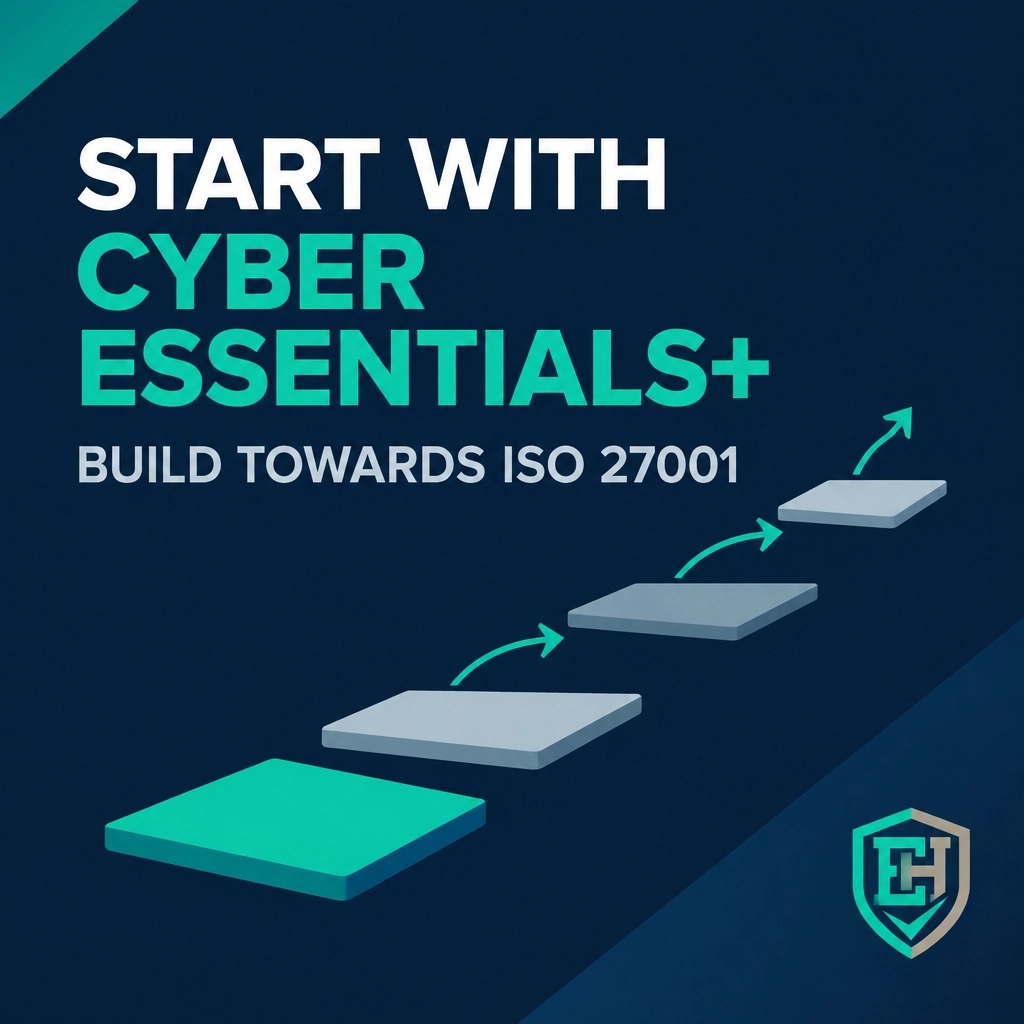
Cyber Essentials+ is a practical first certification for SMEs. Evidence gathered now can give you a head start on ISO 27001-building forward, not starting from scratch. #CyberEssentialsPlus#ISO27001
An AI incident plan is only as good as its answers: Who decides? What evidence is preserved? Who is notified? How is use paused? And how do lessons improve what happens next? #AIGovernance
If one person’s absence can stop a critical process, that’s not just a staffing concern. It’s a continuity risk. Include key-person dependency in your business impact analysis. #BusinessContinuity
Growing fast? Save access checks, backup logs and change approvals as they happen. A small evidence habit now means less chasing later, without adding busywork. EvidentHarbour #StartupCompliance
Following data protection law is one thing. Proving it is another.
ISO 27701, explained in plain English in 5 minutes. Free video:
https://t.co/vV9G1QTH1N
#Privacy#Compliance
Keeping records forever isn’t safety; it’s exposure. Defensible disposal means knowing what to delete, when to delete it, and being able to prove you did.
AI agents can do real compliance work. At EvidentHarbour, we believe human oversight only counts when it leaves a trace: record what AI did, who reviewed it, and how you prove it happened. #AIGovernance#Compliance
A quality management system should be usable, not shelfware: measurable objectives, prompt problem records, root-cause action, regular reviews and short, current documents. If nobody reads a procedure, it controls nothing. #QMS
Run IT or managed services? Customers may soon ask about ISO 20000-1.
ISO 20000-1, explained in plain English in 5 minutes. Free video:
https://t.co/jPDbNaDish
#ITSM#Compliance
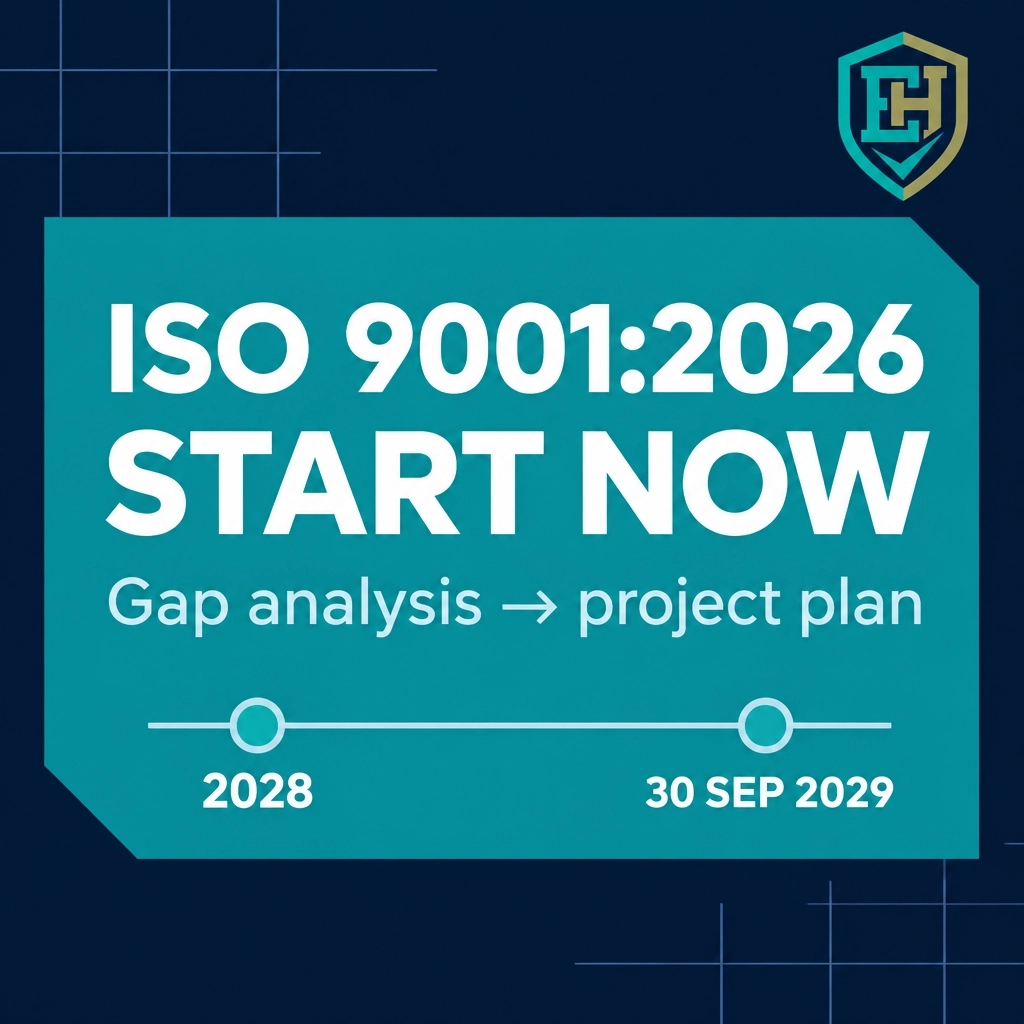
ISO 9001:2026 is a project, not a three-year pause. New 2015 certificates are expected to stop around April 2028; existing certificates are expected to expire on 30 September 2029. Start with a gap analysis. #ISO9001
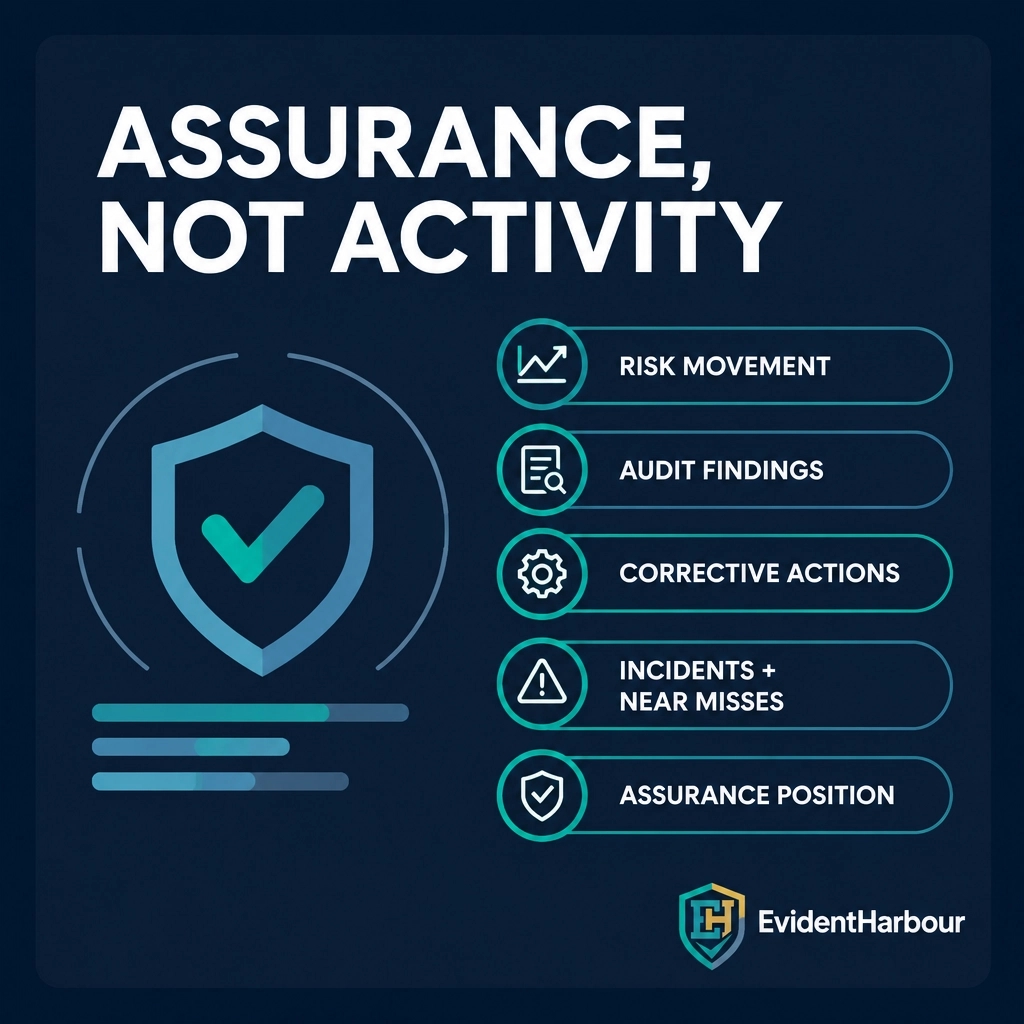
Boards don't need longer GRC activity logs. They need assurance: risk movement, audit findings, corrective actions, incidents and near misses, and the assurance position. Activity is what you did; assurance is what you can prove works.
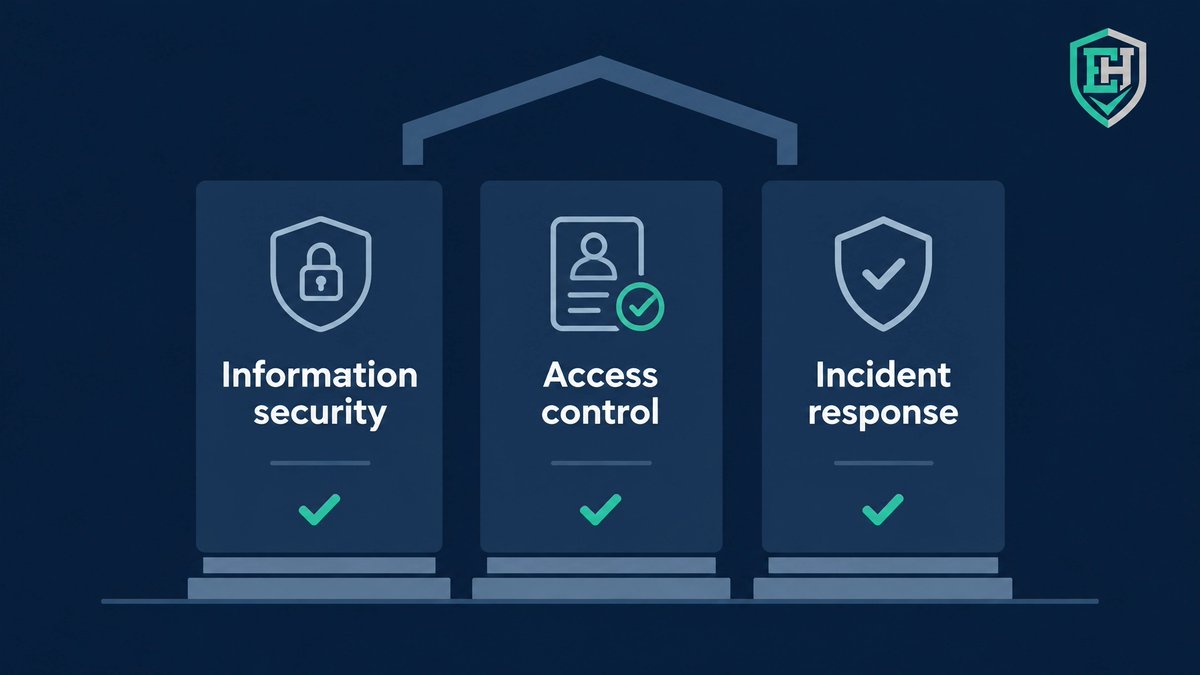
Day one compliance isn't 30 policies. Start with three: information security, access control, incident response. Name an owner for each, write them in plain English, and capture evidence from the start. Build up, don't overbuild. EvidentHarbour #ISO27001#Startups
A risk should connect to its control, evidence, finding and corrective action. Break the chain, and an auditor, or buyer, may find the gap first. #GRC#Compliance
Your AI register is the new asset register. Track the tools, purpose, owner, data, supplier, approval status and review date. Better oversight starts with knowing what you use. EvidentHarbour #AIGovernance#SMEs
The first hour of a security incident is shaped before the alarm: decide who leads, who to call, and what to preserve. Clarity beats improvisation when every decision matters. #CyberSecurity#RiskManagement
What happens tomorrow if your main system goes down?
ISO 22301, explained in plain English in 5 minutes. Free video:
https://t.co/EQaCtVJ5UY
#BusinessContinuity#Compliance
A business continuity plan that has never been exercised is an assumption, not a capability. Test it, learn from it and improve it before disruption does. #BusinessContinuity#Resilience
ISO 9001:2026 is not a rebuild. Structure remains; emphasis shifts to quality culture, ethical behaviour, split risks/opportunities, controlled change planning and climate context. Start with a gap analysis. #ISO9001
EvidentHarbour: a business continuity plan nobody has exercised is an assumption, not a capability. Test it, record what you learn, and turn the gaps into actions. #BusinessContinuity#Resilience