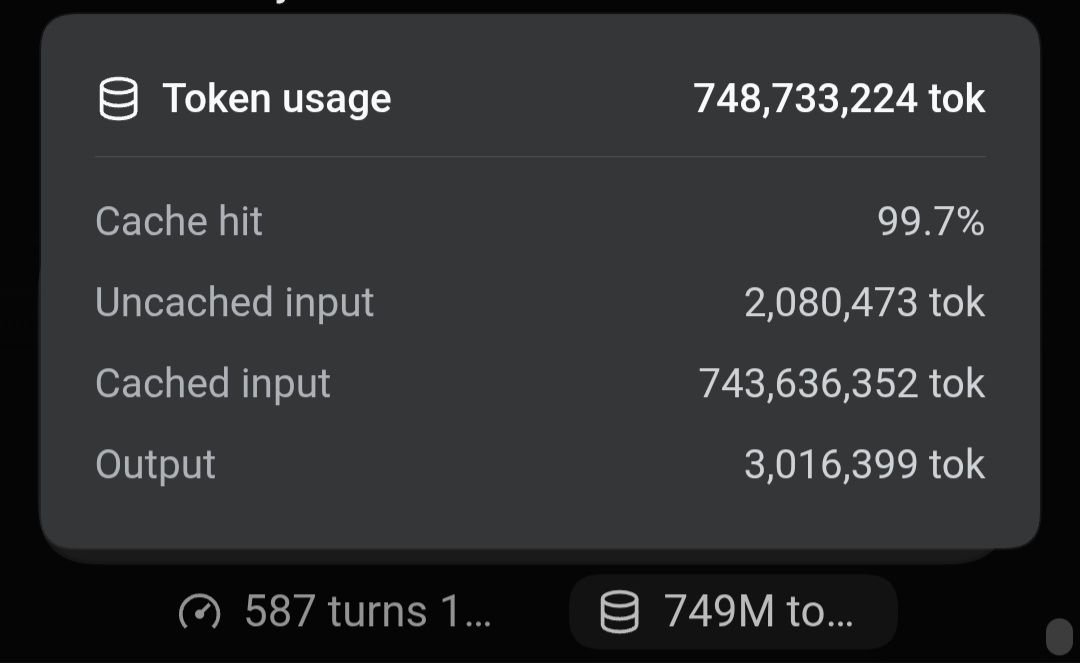
I told Deepseek V4.1 Flash 1017 to build a exploit that escapes Chrome's V8 Sandbox
After 12 hours, it had a multi stage memory corruption exploit that achieves full process read and write.
I told Deepseek V4.1 Flash 1017 to build a exploit that escapes Chrome's V8 Sandbox
After 12 hours, it had a multi stage memory corruption exploit that achieves full process read and write.
@llama_for3ver ahh i saw what u meant... so WSL chrome is really ugly so i decided to overlay the site from wsl window with a normal chrome window, just fucked that a bit up :O
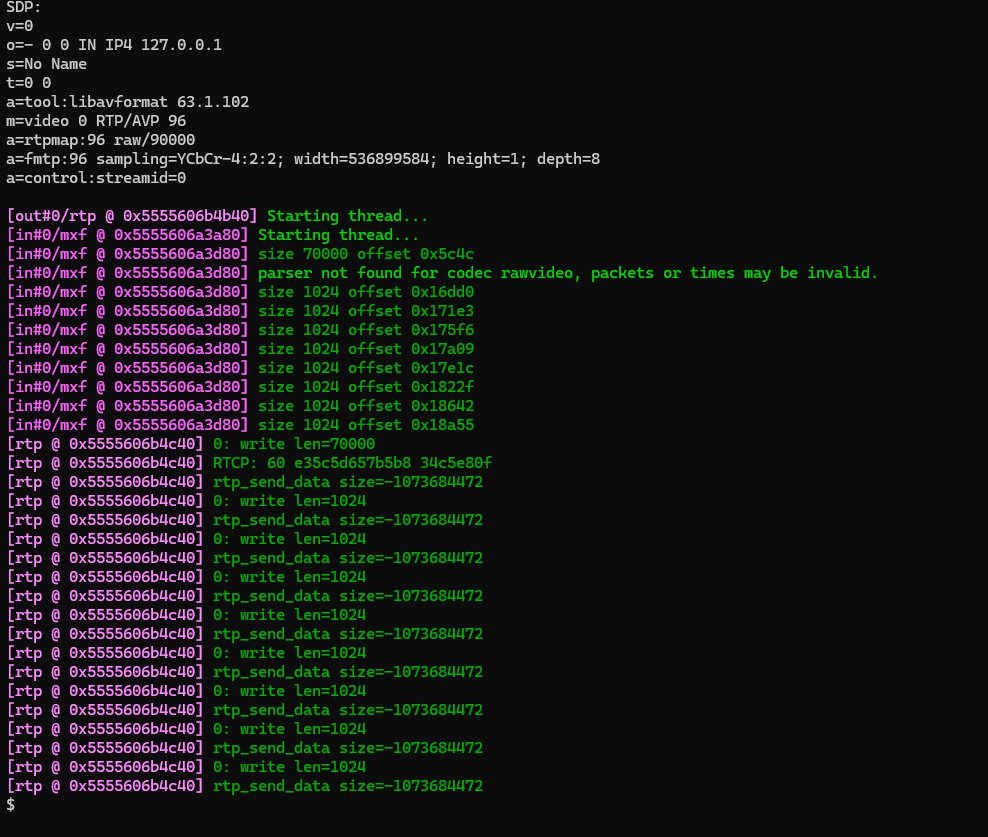
I found a heap buffer overflow in FFmpeg's RFC 4175 Packetizer
A single crafted MXF file makes the packetizer overrun its RTP buffer and corrupt heap memory.
It works on FFmpeg's latest version
With the right heap layout it yields code execution
I told DeepSeek V4.1Flash to find a vuln in Samsungs sgpu GPU Driver
2 days later it found a Race UAF vuln that gives any unprivileged app arbitrary physical write.
@0x_shaq@gmhzxy I didnt use a custom harness, i used Deepseek Harness on PTC mode (although minimal mode may be better), and v4.1 is generally very good in exploit work