In the race to build, launch, and scale, security often gets pushed aside for “more urgent” priorities but one breach is all it takes to undo years of innovation, customer trust, and investor confidence.
The cost of a breach goes beyond dollars, it disrupts operations, damages reputation, and slows growth.
Penetration testing isn’t just about uncovering vulnerabilities, it’s about protecting growth, preserving trust, and ensuring resilience.
If penetration testing feels expensive, consider this:
The average data breach costs over $4.4 million, while a comprehensive pentest averages $15K–$50K, less than 1% of that.
At Exploit Forge, we help organizations identify weaknesses before attackers do, enabling secure, confident growth.
If you’ve been asking us how to learn, how to be an Offensive security professional…
Here’s your cue!
Here’s somewhere you can start from!!
Follow @ExFacademy, set your Reminder and don’t miss this!!!🚨💯.
https://t.co/xEwFQ0mhO3
This Saturday, ExploitForge Academy is hosting a live X Space and we're pulling back the curtain on what getting into offensive security actually looks like.
No gatekeeping. No jargon. Just real talk from people who do this work professionally.
You don’t want to miss this.
Set your Reminders!
https://t.co/7YONa5ZkRj
Security testing that does not keep pace with your environment is not a posture. It is a snapshot with an expiry date.
At Exploit Forge, we help organizations build a testing cadence that reflects how their environment actually changes.
DM ASSESS to find out what the right rhythm looks like for you.
#CyberSec
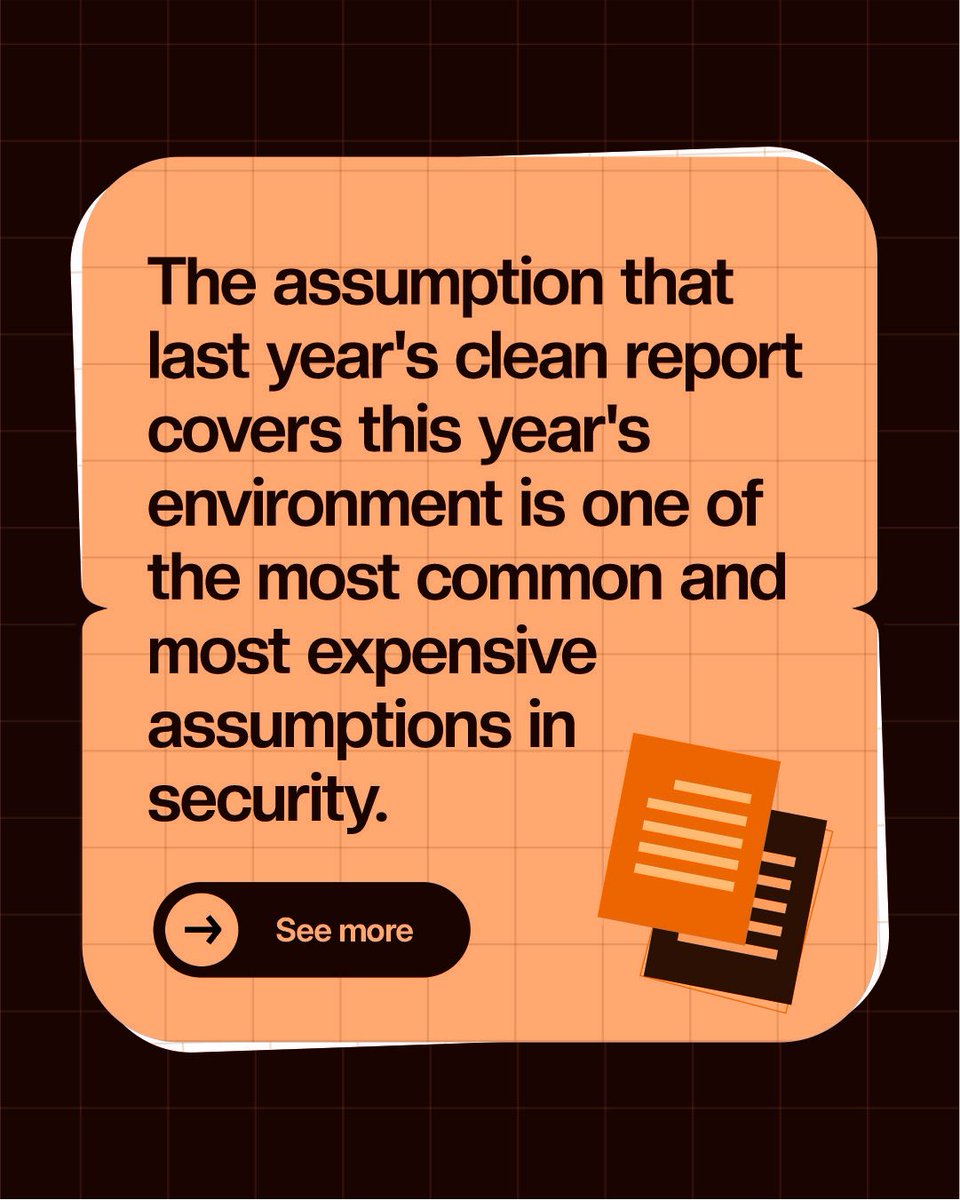
Most organizations still treat security testing like a tax return. Something you do once a year, file away, and forget about until the next cycle.
The problem is that your environment does not stay still between tests. Code ships. Dependencies update. Cloud configurations drift. New people join with new access. Old integrations accumulate permissions nobody has reviewed in months.
The test you ran last year tells you what was true last year. It says very little about what is true today.
#CyberSecurity #InfoSec #OffSec #PenTest
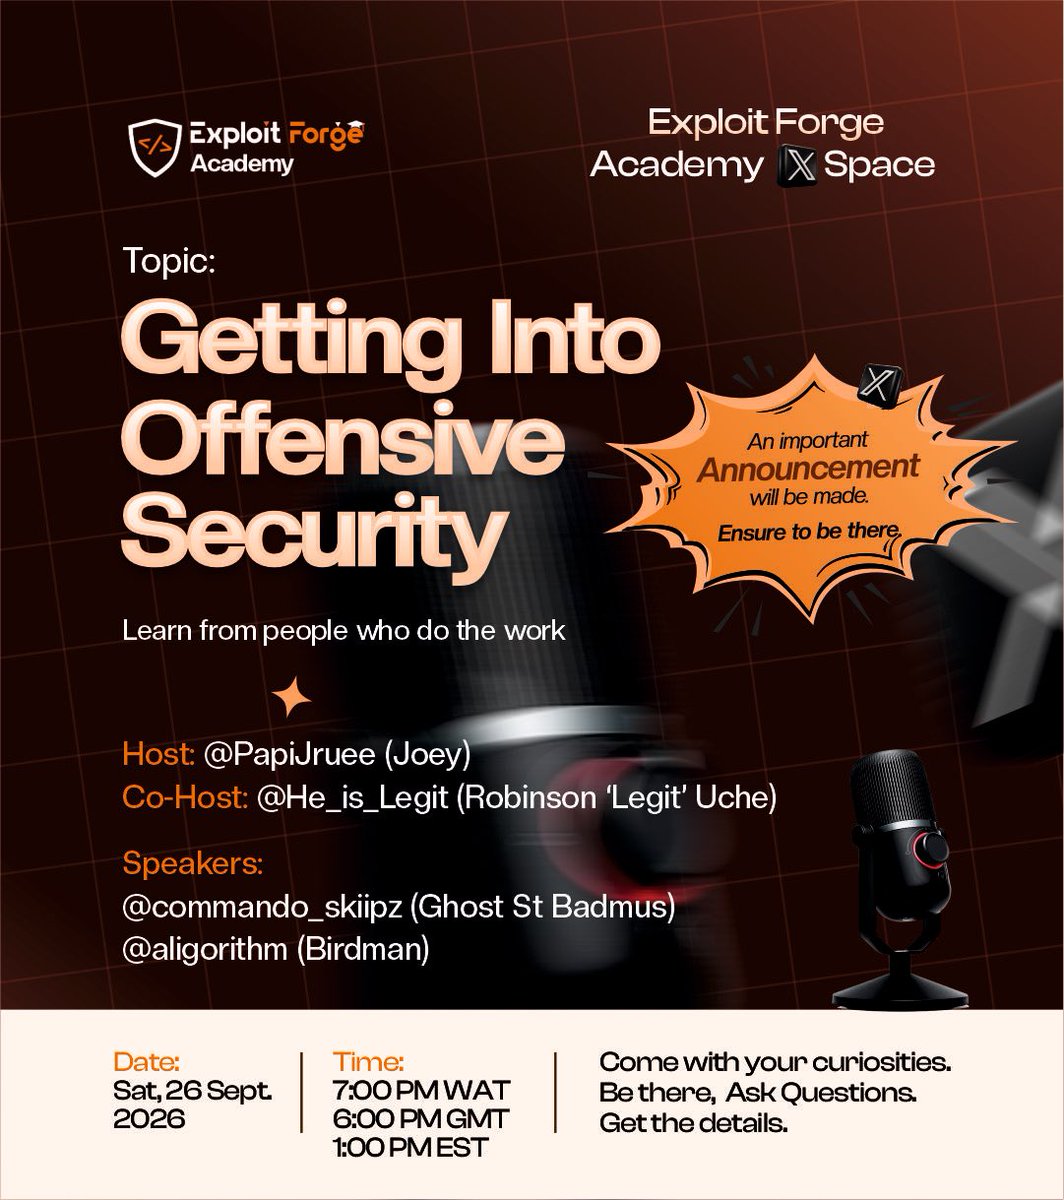
The Academy is hosting its first X Space next Saturday.
Topic: Getting Into Offensive Security: what it is, what it takes, and how to get started.
Straight from people who actually do the work.
📅 Saturday, 26th September 2026
🕙 7PM WAT | 6PM GMT | 1PM EST
Follow @ExFacademy and set a reminder. This is the conversation worth showing up for. 🔥💯
Offensive security doesn't have to feel out of reach.
Next Saturday, we're breaking it down live: what it is, what it takes, and how to get started.
🎙️ X Space · 26 Sept · 7PM WAT
Speakers: @commando_skiipz · @_aligorithm · @He_is_Legit · @PapiJruee
Come with your curiosities.
12 weeks ago, we joined DiSH Cohort 7 alongside 20 startups.
12 weeks of honest conversations, hard questions, and invaluable peer learning.
We leave with sharper thinking, stronger relationships, and a clearer vision of what we’re building.
The accelerator ends. The work continues.
#cybersecurity #Founders #Startups #CyberInnovation #manchester
@Amospikins The small compromise is never small for long.
Foothold - lateral movement - domain compromise - weeks of undetected access.
The gap between "minor issue" and "full breach" is usually just time.
And that’s why we exist, to find it before an attacker does💯🚀..
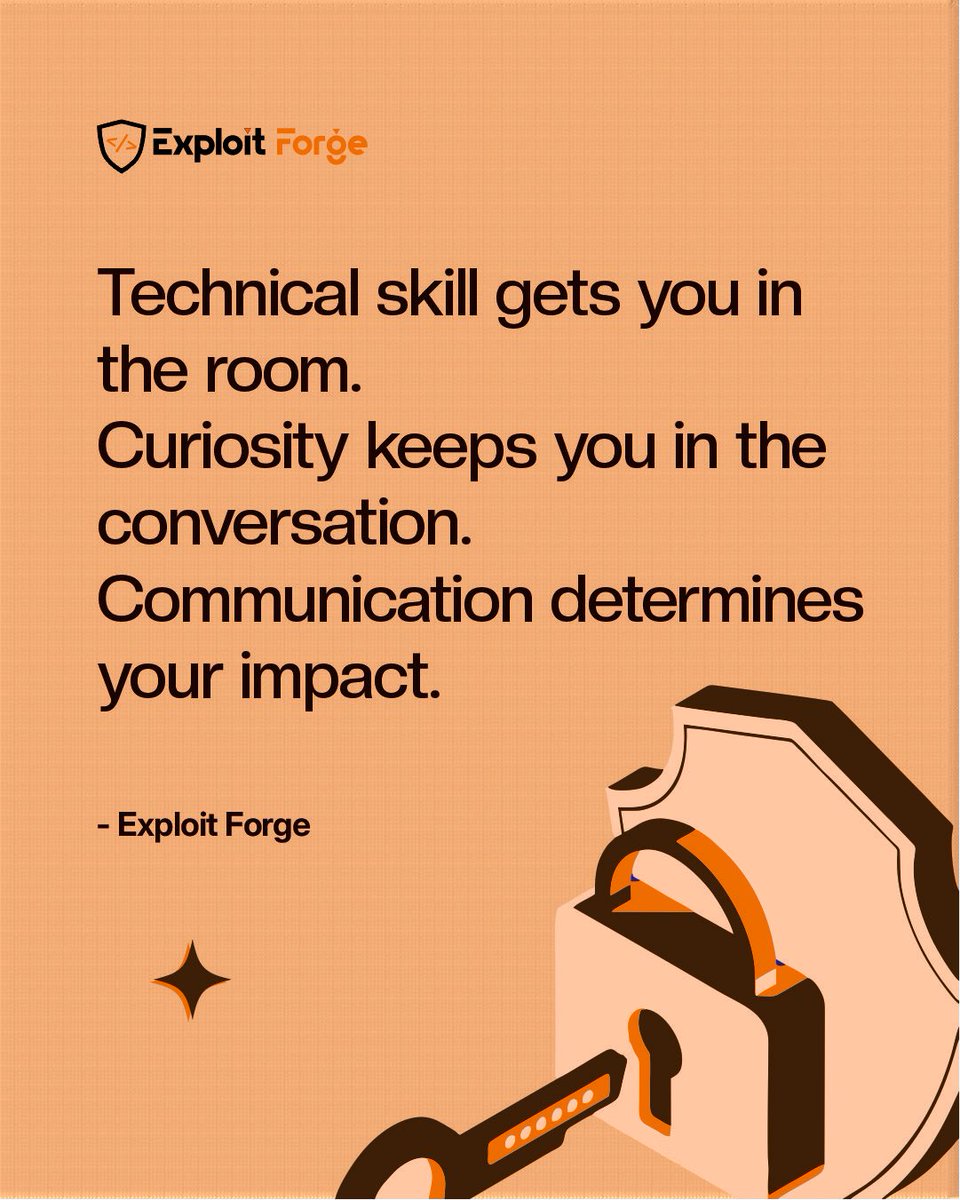
We get asked often what we look for when hiring.
The technical bar matters. But it rarely separates the ones who work out from the ones who don't.
What actually does:
Curiosity beyond the brief.
Communication that translates.
Resilience under ambiguity.
These things can be taught. Most programmes don't teach them.
And we’re changing that. Check out the @ExFacademy page.
#CyberSec #CyberCareers #TechSkills #OffensiveSecurity #CareerDevelopment
Meet the speakers joining us for the Version 2 launch of @threatmindAI .
Agwu Ushiang Kalu: Staff Information Security Engineer at Landytech (CISM, CISSP, CCSP). Making engineers your security team, without them even knowing it.
#UKCyber#CyberSecurity#CyberInnovation
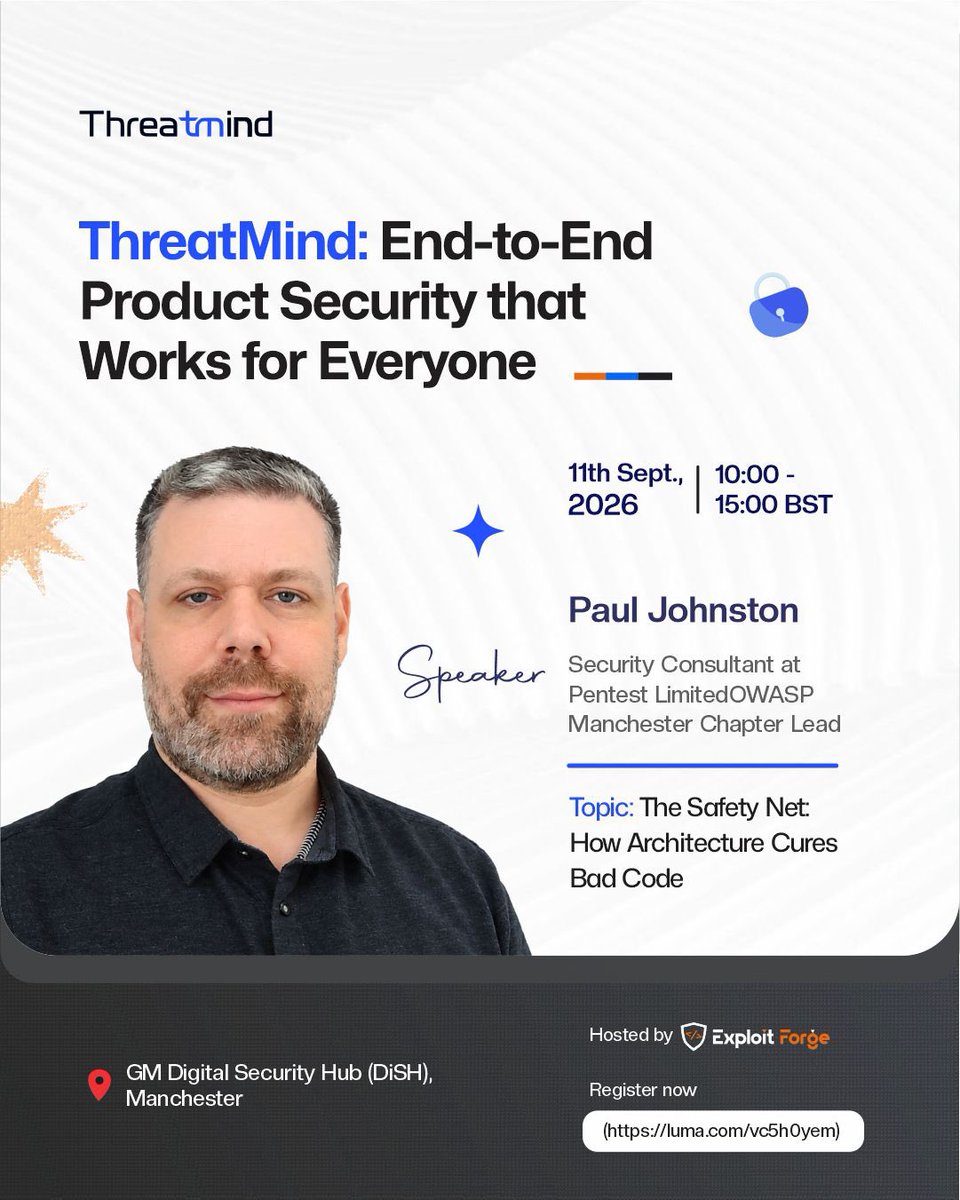
Paul Johnston: Security Consultant at Pentest Limited and OWASP Manchester Chapter Lead. How architecture cures bad code before it ever becomes a vulnerability.
📅 11th September 2026, 10:00–15:00 BST
📍 GM Digital Security Hub (DiSH), Manchester
#CyberSecuritySolution
@onerandomd3v Number 5 is the one that ends careers😭…
A stolen session token shouldn’t hand you the admin panel but here it does. Great catch @onerandomd3v 💯
September has started well for us and we are just getting started.
We are hosting ThreatMind: End-to-End Product Security That Works for Everyone. A live, in-person session in Manchester bringing together security leaders, product managers, founders, and engineers for an honest conversation about product security and how to solve it properly.
Come and get hands-on access, see ThreatMind live, and be in the room where the conversation is happening.
📅 Friday, 11th September 2026
🕙 10:00 – 15:00 BST
📍 GM Digital Security Hub (DiSH), Manchester
🎟️ Reserve your free ticket: https://t.co/U8sKQrWFaG
@threatmindAI
#cybersecurity #UKCyber
@gabbytech01 This is the right breakdown. The four questions are the foundation…but you’re correct that a design can answer all four and still leave critical gaps. No AAA means you can’t control who accesses what, can’t audit what happened, and can’t revoke access when something goes wrong.