We run this continuously for clients as an approved Panorays MSSP partner. Every supplier mapped and rated from the outside, nothing installed on anyone's systems.
Full analysis: https://t.co/qeUf1OfHFA
Why hack a bank when you can hack the company that checks its customers' IDs?
South Africa found out this weekend. Bidvest Bank, EasyEquities, Peregrine Capital and Cell C all wrote to customers. None of the four was hacked. Their suppliers were 🧵
What to do this week:
Ask each critical vendor which subprocessors touch your customer data. Look for names that repeat.
Keep monitoring after onboarding. Posture drifts.
Write the POPIA notification path now.
Contract for notification in hours.
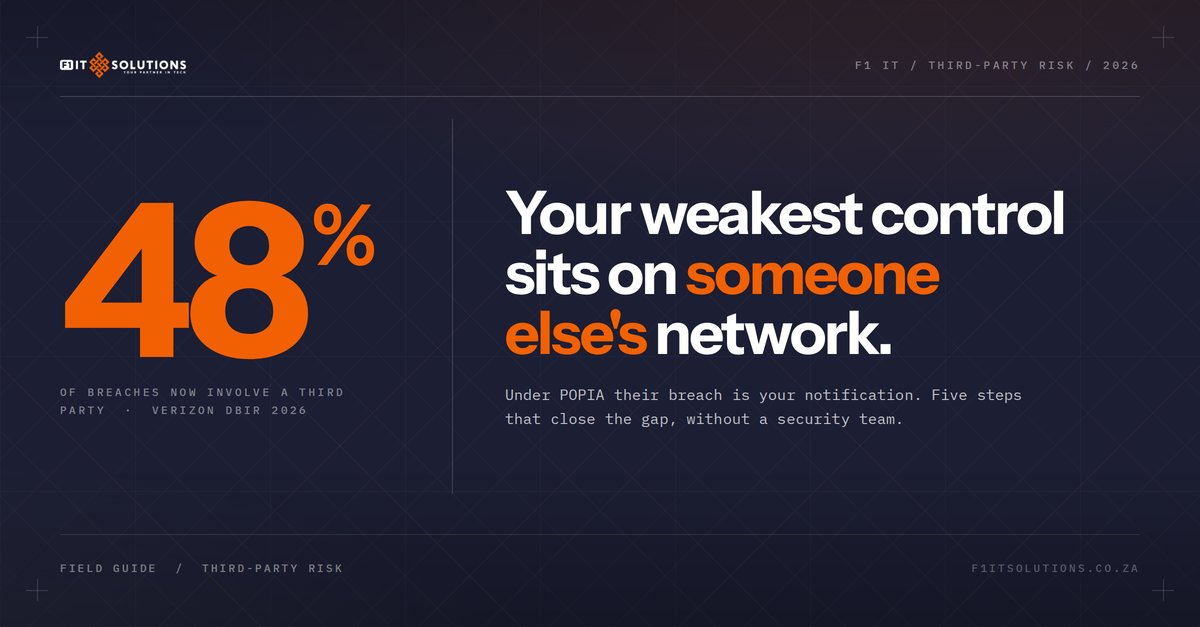
Yesterday: 48% of breaches now involve a third party (Verizon DBIR 2026).
Today: our answer.
F1 IT Solutions is now an approved Panorays MSSP partner. Continuous third-party cyber risk management, fully managed, across SA, the UK and Europe. 🧵
We hold ourselves to the same bar.
F1 has started its own ISO 27001 certification, target Q1 2027, and our own vendor base runs through the same platform we manage for clients.
Full method, including the four-tier table and the ten questions:
https://t.co/C0aRfSG1xj
One more thing. Tomorrow we announce something that changes how we run this for clients.
The clue is already in the article 👀
Your weakest security control sits on someone else's network.
Verizon's 2026 DBIR: third-party involvement in breaches went from 30% to 48% in a year.
Nearly half of all breaches now begin outside the perimeter you control.
How to fix that without a security team 🧵
And the part almost nobody does. Offboarding.
Delete accounts, API keys and integration tokens.
Revoke OAuth consents.
Get written confirmation of deletion, backups included.
Collect the access cards.
The invoices stop. The access does not.