Get more powerful websites and applications with Fastly’s edge cloud platform. We help places like Reddit, Epic Games, the NYT, and GitHub do so every day.
No product pitches—just real solutions for engineering and cybersecurity leaders solving mission-critical problems at scale.
See you at Xcelerate NYC?
📅 Oct 14, 2026 | 9 AM – 5 PM
📍 Convene | 360 Madison Ave, NYC
👉 Reserve your seat: https://t.co/cSah4hfU4f
Not all bots are the enemy. Some are indexing you for search. Some are feeding your content into AI answers. Some are just scraping you for parts.
The hard part isn't picking a side — it's telling them apart, fast enough to matter.
We wrote about how Fastly Bot Management and ContentGuard handle that, at the edge, in a few clicks: https://t.co/Dc4Lf1hksM
2:15 AM. Errors spiking. Attack? Outage? Industry-wide botnet?
Fastly AEDA (built with Google Cloud's Gemini Enterprise) figures it out for you — autonomous root-cause analysis at the edge, before traffic hits your origin.
MTTR: hours → seconds. Early access is open now. 🧵
https://t.co/BAZYz8hQJI
Agents are using your digital front door for customers you never see. API Security holds AI agents to the API contract you already published. Log it or block it, service by service.
Learn more: https://t.co/vHiCw81g0T
The attack arrives as ordinary content and executes in the model downstream.
Stop it with AI Firewall: inline detection of prompt injection at the edge, so malicious prompts are blocked before they reach the models they call.
https://t.co/vHiCw81g0T
Why your AI strategy needs a control plane: Jonathan Speek and Terri Allegretto introduce AI Runtime Control. One endpoint across your models, virtual keys instead of raw credentials, spend attributed per key, automatic failover.
Read: https://t.co/LsC2yNejp7
AI Runtime Control: one gateway across your models. Virtual keys instead of raw credentials. Cost and tokens attributed per key, per session, per person. Bring your own keys. Routing serves your economics, not ours.
Learn more: https://t.co/yRTkGtVSHs
Which model did that call go to, what did it cost, and who authorized it? Austin Spires on AI Runtime Control: one gateway across your models, virtual keys, per-key cost attribution, searchable logs.
👉 Watch on demand: https://t.co/oI22e3DJaJ
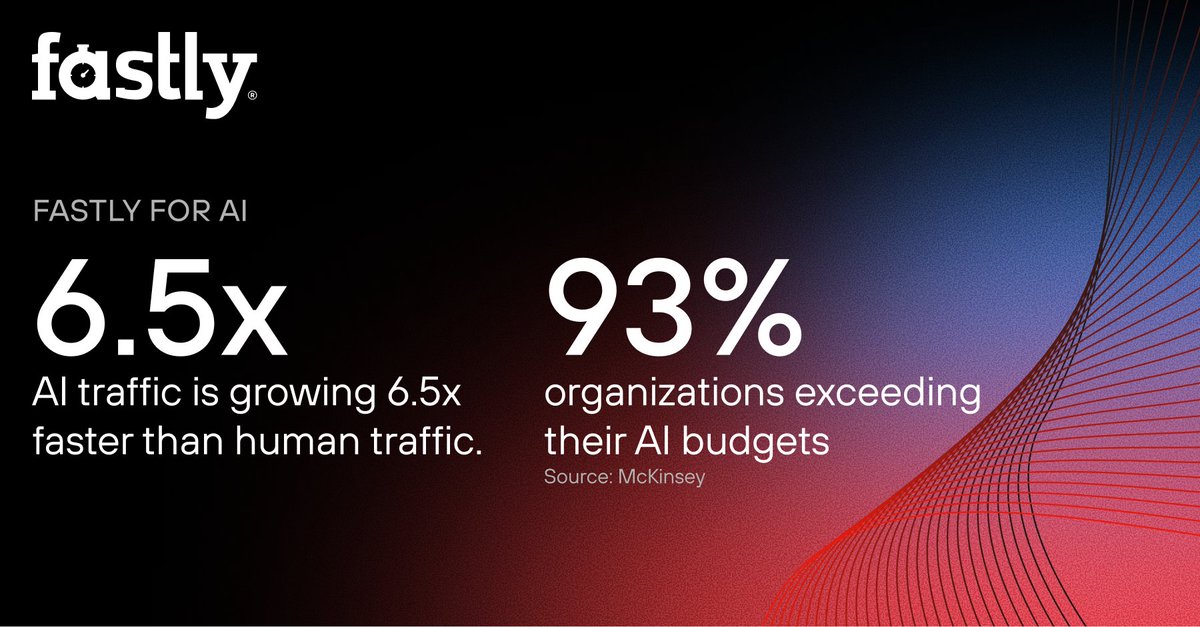
AI traffic is growing 6.5x faster than human traffic. 93% of organizations are exceeding their AI budgets (McKinsey). The question that still gets asked: what did your AI do, and was it authorized to do it?
Answer it with Fastly for AI: every request, under your control.
See how: https://t.co/A0z2mL7FB8
Today we're expanding Fastly for AI: Every request, under your control. AI Runtime Control. AI Firewall. API Security for AI agents. On the platform already in the path of your traffic.
Move fast. Stay safe.
https://t.co/ptfj6AFPWb
New research: "Style Smuggler" (CVE-2026-75650), an unauthenticated SSTI→RCE chain in Magento.
We break down the full exploit chain + share a Nuclei template + our virtual patch 🧵
https://t.co/YhRpKcrzGO
We’re partnering with @Comcast to integrate Fastly’s software directly into Comcast’s nationwide network. ⚡
Together, we’re establishing a new approach for the industry to deliver the biggest moments in streaming with speed, reliability, and quality.
📰 Official Press Release: https://t.co/KjS4EXmW4B
Accelerate data transfers with Direct Fetch
Add one header to a PutObject/UploadPart request and Fastly copies the object server-side from your S3-compatible source, without having to download and upload data through a client.
Also supports pre-signed URLs for private buckets, and Range headers for multipart uploads.
Learn more: https://t.co/DT8le3t0Uo
Attackers use AI at machine speed. Is your security team still bound to human reaction times? Join us & @GoogleCloud on 9/29 in Sunnyvale for the Security Innovations Forum 2026. See agentic AI defense in action.
Register: https://t.co/p84rUL2rTb
Aggregate dashboards show you traffic spiked. Not who's sending the 403s, or why.
Fastly Log Analytics is a new open-source, self-hosted data lake + dashboard for 100% of your raw Fastly logs. No third-party vendor bill.
Read the blog, and visit the repo 👇
https://t.co/16Ko2Yh40q
The Fastly Threat Research team is tracking a sharp escalation in exploitation attempts for CVE-2026-82329, a critical authentication bypass in self-hosted JFrog Artifactory. Since its disclosure on August 28, we’ve observed activity surge from low-level probing to opportunistic mass scanning.
To help mitigate exploitation attempts, Fastly Next-Gen WAF has shipped a virtual patch for CVE-2026-82329 allowing customers to protect their instances immediately. For our full analysis on exploitation trends and critical remediation steps, read the latest blog:
https://t.co/3H9cBrYdkZ
#JFrog #Artifactory #WAF #AppSec #DevSecOps #CVE-2026-82329 #IncidentResponse #NetworkSecurity
Your website doesn’t need to know WebMCP exists.
With Fastly Compute you easily can detect forms, understand what they do, and inject WebMCP attributes at the edge before the page reaches the browser.
Agent-ready, on demand.
https://t.co/tW9Tx2J0mW
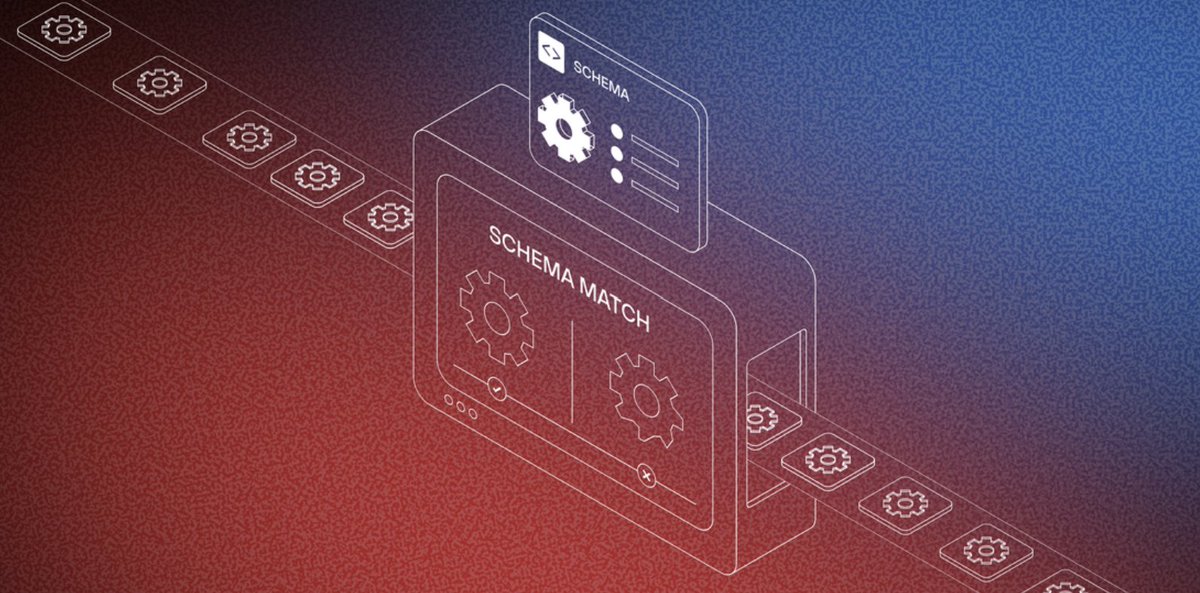
Stop bad API requests before they derail your day.
Fastly API Schema Enforcement validates live traffic against your specs and blocks invalid requests instantly, right at the edge.
Learn more 👉 https://t.co/hR77goAMc2
#APISecurity