July took a lot out of me.
I lost my spark, my peace, and my balance.
But August is a fresh start. 🤍
I’m choosing to slow down, find my rhythm again, keep showing up, and trust God with what I can’t control.
Here’s to finding my way back to myself. 🌱
Happy New Month! ❤️
One infected computer shouldn’t be able to take down an entire organization.
That’s exactly what I learned today.
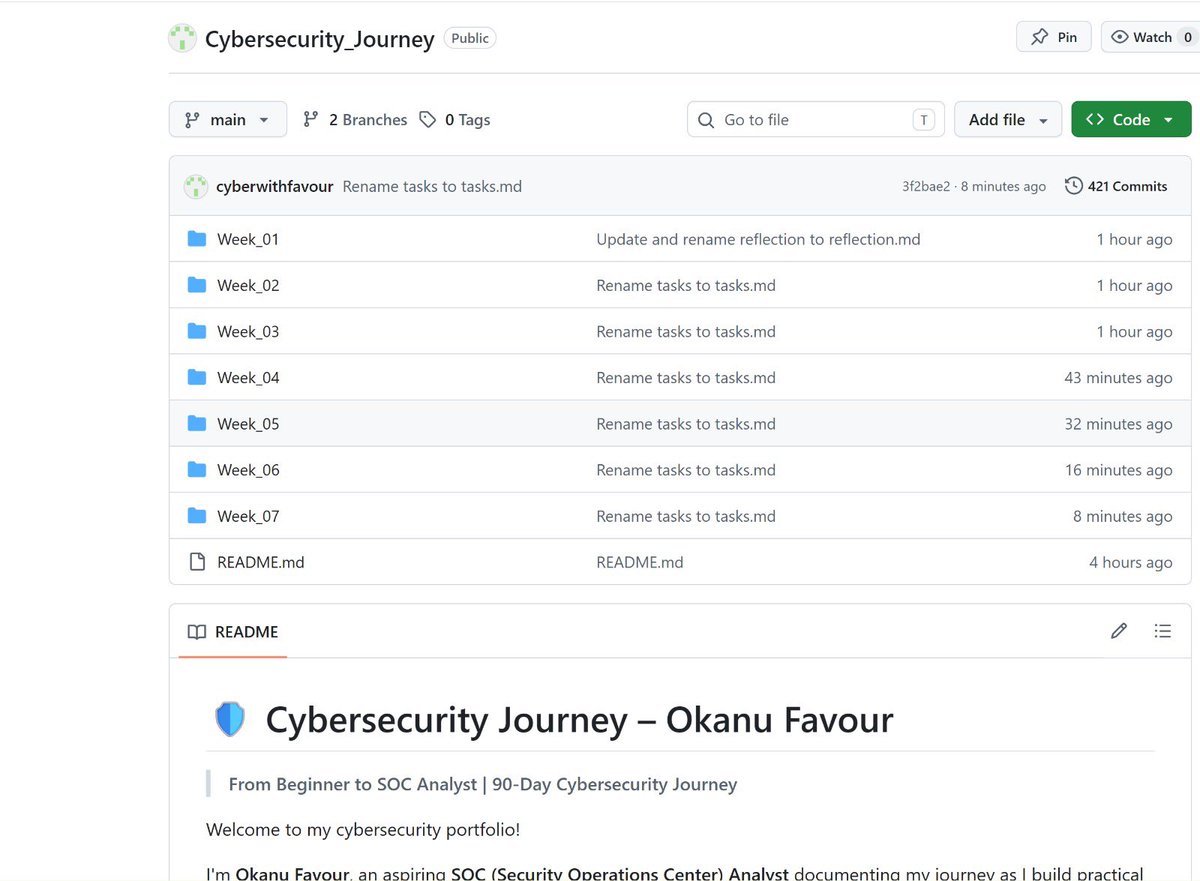
Day 56/90 of becoming a cybersecurity analyst—network segmentation and VLANs.
#Cybersecurity#VLAN#90dayschallenge
The strongest security starts with good design—not expensive tools.
That was my biggest takeaway today.
Day 55/90 of becoming a cybersecurity analyst.
#Cybersecurity#NetworkSecurity#90dayschallenge
You type a website. It loads in seconds.
But there’s a lot happening before that page ever appears.
Day 54/90 of becoming a cybersecurity analyst—today was all about DNS security.
#Cybersecurity#DNSSecurity#90dayschallenge
Sometimes, one security rule is all it takes to stop an attack.
Today I learned how Access Control Lists (ACLs) make that possible.
Day 53/90 of becoming a cybersecurity analyst.
#Cybersecurity#90dayschallenge
I don’t think I’ll ever connect to public Wi-Fi the same way again.
Today’s lesson on wireless security explained why.
Day 52/90 of becoming a cybersecurity analyst.
#Cybersecurity#90dayschallenge
Who should be allowed to connect to a company’s network?
That simple question introduced me to Network Access Control (NAC) today.
Day 51/90 of becoming a cybersecurity analyst.
#Cybersecurity#90dayschallenge
Cybersecurity isn’t just about stopping attacks…
It’s also about controlling who gets access and what they’re allowed to do.
That was my biggest takeaway today.
Day 50/90 of becoming a cybersecurity analyst.
#Cybersecurity#SecurityPlus#90dayschallenge
Hackers don’t always break in…
Sometimes they log in.
Today’s lesson helped me understand why authentication and secure access are some of the strongest defenses an organization can have.
Day 49/90 of becoming a cybersecurity analyst.
#Cybersecurity#90dayschallenge
Day 48/90 🛡️
Today I learned how Windows Event Logs help SOC analysts investigate security incidents.
Key Event IDs:
🔹4624 – Successful Logon
🔹4625 – Failed Logon
🔹4720 – User Account Created
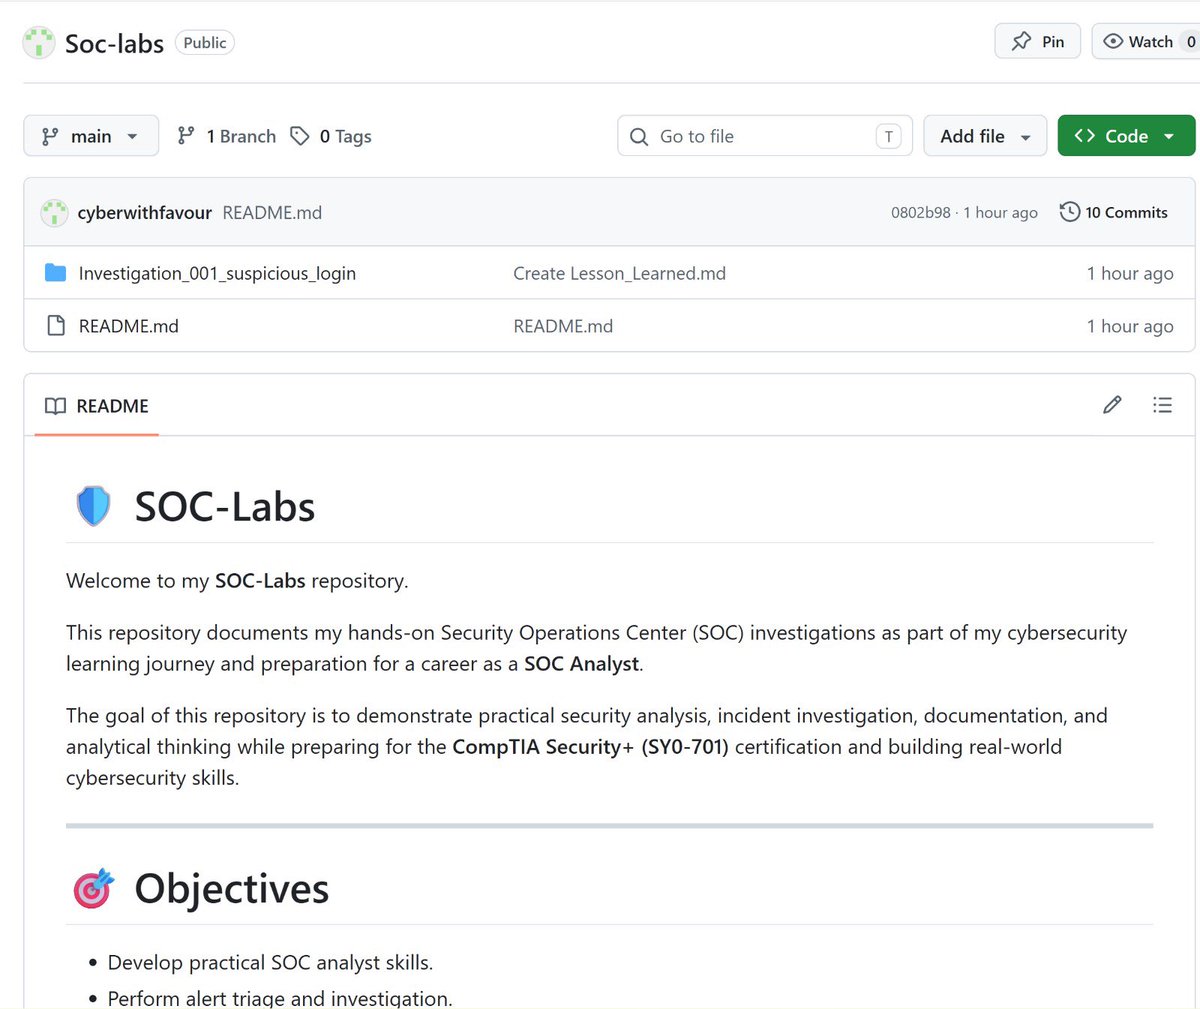
I completed SOC Lab #3
#cybersecurity#socanalyst#90dayschallenge
Day 47/90
Today I learned about SIEM and how SOC analysts use logs to detect threats.
Big takeaway:
Logs → Events → Correlation → Alerts → Investigation
Also completed my second SOC investigation for my GitHub portfolio. 🛡️
One day at a time.
#CyberSecurity#SOC
Day 46/90
Today’s lesson: SOC Fundamentals.
Learned about:
Tier 1, 2 & 3 SOC Analysts
Event vs Alert vs Incident
Alert investigation workflow
Also spent time rebuilding my GitHub and created my SOC-Labs repo.
#CyberSecurity#CompTIA#BuildInPublic#90dayschallenge
Cybersecurity isn’t about hoping attacks never happen. It’s about knowing exactly what to do when they do.
Day 45/90 ✅
Today’s revision:
Malware
Virus vs Worm
Trojans
Ransomware
Antivirus vs EDR
Incident Response
Digital forensics
#IncidentResponse#90DaysOfCybersecurity
Good security isn’t just detecting attacks. it’s making systems harder to attack in the first place. 🔐
Day 44/90 ✅
Today’s revision:
Firewalls
IDS vs IPS
VPN
DMZ
Vulnerability Management
Patch Management
System Hardening
#90DaysOfCybersecurity
Encryption keeps data secret. Hashing proves it hasn’t been changed. Two different concepts. Both essential. 🔐
Day 43/90 ✅
Today’s revision:
AES
RSA
SHA-256
MD5
Encryption vs Hashing
Digital Signatures
PKI
Another step forward.
#Cryptography#90DaysOfCybersecurity
Strong security isn’t just about blocking attackers. It’s also about controlling access.
Day 42/90 ✅
Today’s revision:
AAA
MFA
SSO
RBAC
Least Privilege
Access Control Models
Every topic keeps showing me how important identity is in cybersecurity.
#90DaysOfCybersecurity
Networking is the language every SOC Analyst needs to speak.
Day 41/90 ✅
Revised:
OSI Model
TCP/IP
TCP vs UDP
IPv4 vs IPv6
DNS, DHCP & NAT
Network devices
Common ports & protocols
Finished with Ubuntu networking practicals.
#SOCAnalyst#Networking#90DaysOfCybersecurity
You can’t defend what you don’t understand.
Day 40/90 ✅
Revision Day.
Today I strengthened my understanding of:
CIA Triad
Threats vs Vulnerabilities vs Risks vs Exploits
Security Controls
AAA
Also completed the Ubuntu practical and updated my GitHub.
#90DaysOfCybersecurity
Most cyber attacks don’t start with hacking—they start with one mistake, one weak configuration, or one missed alert. Here’s what I’ve learned from Days 33–37 of my 90-day cybersecurity journey.