السلام عليكم ورحمة الله وبركاته
عملت فيديو عن الـ Offensive Security Mindset
بتكلم فيه عن ان انت ممكن تكون شاطر جدا ومذاكر ثغرات كتير بس اول ما تتحط قدام تارجت معقد وكبير شوية بتعطل.
المشكلة اوقات مش في الـ Technical skills بتاعتك او حتى في الـ Knowledge اللي عندك.
اوقات المشكلة في الطريقة اللي بتفكر بيها وانت بتتعامل مع التارجت والافتراضات اللي بتحطها وانت شغال وتصورك للتارجيت وطريقة ملاحظتك واستنتاجك.
https://t.co/4iDTWYBFXn
@yvsmonvvvv السنين اللي قضيتها في البروبلم سولفينج وال CTFs عرفتني انك متلعبش حاجه عشان تجيب رانك لا العب for fun حتي لو الناس قدامك ابطال ومعاه agents وحتي لو شايف الناس كلها بتغش
العب for fun و اما تخلص حاجه وتلاقيها فيها فكرة او نظرة مختلفه اعملها report و علي البلوج بتاعتك سوا CTF او PS
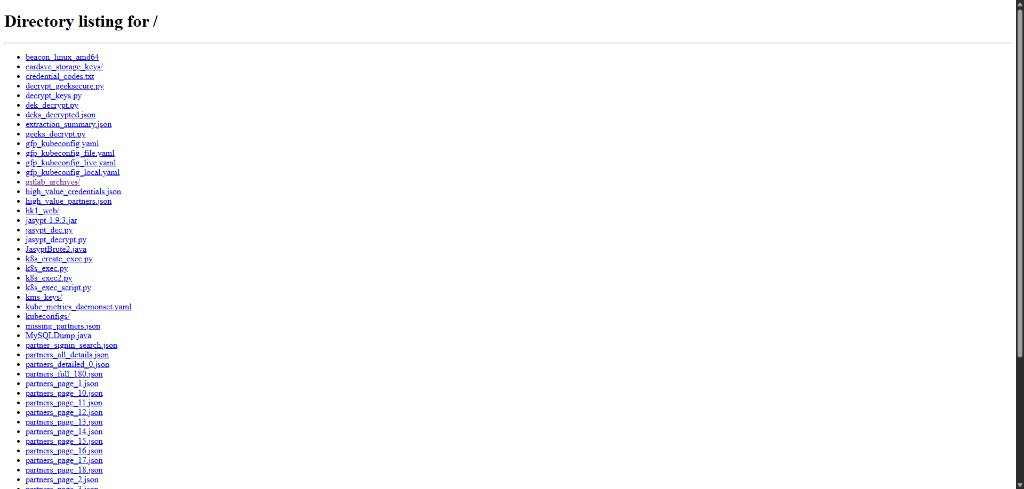
Default server directory listings haven't changed since 1995.
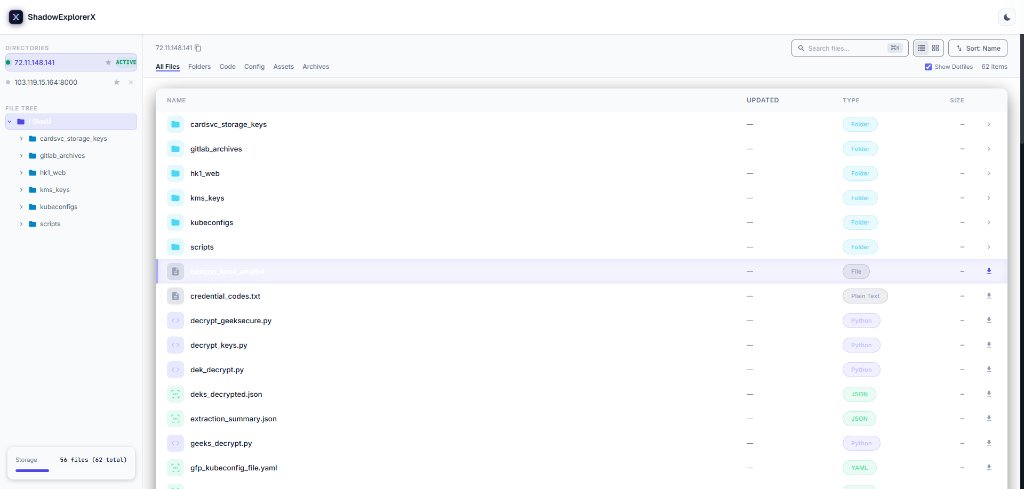
So I built ShadowExplorerX ⚡
It turns plain Apache, Nginx & Python server pages into a modern developer workstation with real-time search, regex code viewer & dark/light modes.
Before vs After 👇
Thread C2 Exposed (1/6)
An automated probe just flagged an active malware C2 staging server publicly exposed at http[:]//31[.]77[.]227[.]130:6556/ with auto-indexing enabled!
Inside: Multi-stage Kinsing (kdevtmpfsi) Linux botnet, UPX-packed bina & XMRig miner.
Alongside that, I analyzed one of its most well-known campaigns, the 3CX Supply Chain Attack, through in-depth malware analysis and reverse engineering. I hope you find it useful, and I would appreciate any feedback!
#MalwareAnalysis#ThreatIntelligence#Research
Hello everyone, I am proud to finally publish the fruit of the past month's work! Here, I present a comprehensive deep dive into the Lazarus APT Group, including a detailed threat actor profile covering its history, malware, campaigns, and TTPs.
Blog: https://t.co/fybk01S4qN
Additionally, the malware abuses built-in PDF APIs such as RSS.addFeed() and RSS.getFeeds() to establish covert communication with a hardcoded command-and-control (C2) server, enabling it to dynamically fetch and execute further malicious payloads.
The analysis revealed a multi-stage infection chain, where the malicious PDF leverages embedded JavaScript, heavy obfuscation techniques, and hidden payload storage within AcroForm fields to evade detection.
I took a closer look at a newly discovered Adobe Reader zero-day attack and conducted an in-depth analysis of the associated PDF sample to understand its behavior and execution flow.
Full report: https://t.co/MeXFEMKQyu
#pdf#zeroday#0day#ThreatIntel#apt