🚀 Optimizing Time-Based SQL Injection Detection Blog Post! 🚀
🛡️ Learn about efficient strategies, practical examples, and tips to enhance your web security testing.
🔗https://t.co/LBtw0nP57h
#CyberSecurity#WebSecurity#SQLi
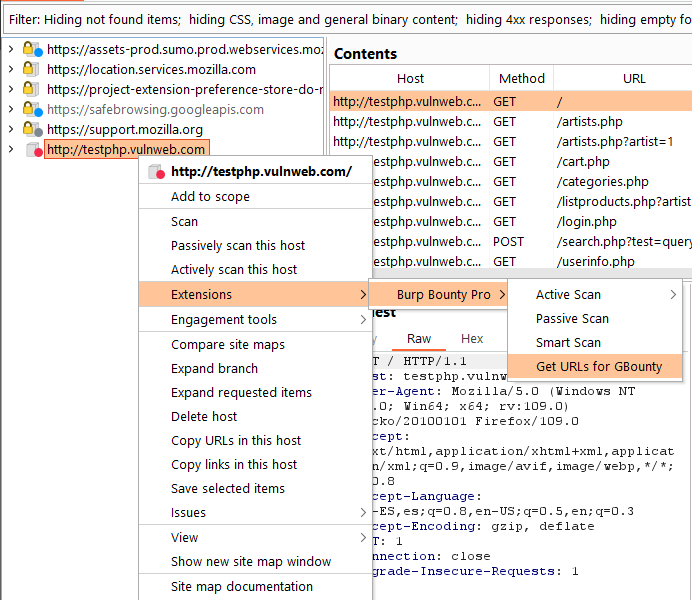
Export to GBounty is a Burp Suite extension that enables users to export selected HTTP requests from Burp Suite into a compressed ZIP file. The exported ZIP file can be utilized with the GBounty scanner.
https://t.co/7mRtT0KhZJ
Exciting news! Bounty Security has open-sourced GBounty Scanner, Multi-Step Profiles, and GBounty Profiles Designer under the MIT license. https://t.co/eA29exsZJQ #Cybersecurity#OpenSource#GBounty
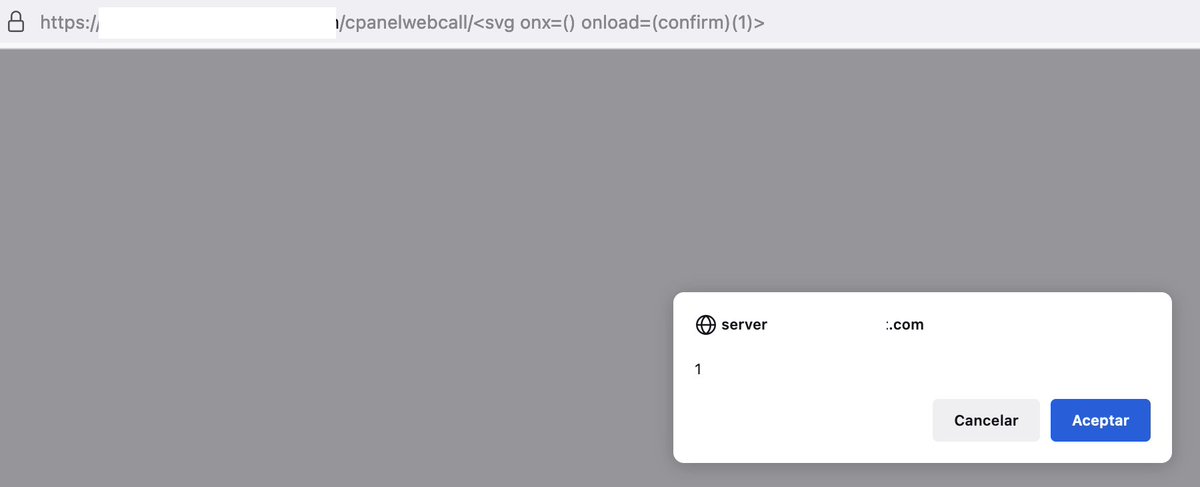
Maybe there was a misunderstanding with my previous tweet, I didn't know there was an XSS bug in cpanel, I read it in the @infosec_au article. Once I read I saw that with the XSS payloads this issue was detected if the path /cpanelwebcall/ was scanned. All credit to @infosec_au
🔥🚀 "Heads up, everyone! ! We have not released any special profiles to detect the CVE-2023-29489 (#XSS in #cPanel) vulnerability, because we already detected it with our current XSS profiles 💯.🔒🌐 #Cybersecurity#InfoSec" 🚀🔥
https://t.co/D8Q5hj094Z
https://t.co/hYNwESPnet
GBounty is a powerful tool that can help you find vulnerabilities in your web applications. With its advanced scanning features and easy-to-use interface, GBounty is a must-have for any security professional. Try it today and see the difference! #BugBounty#PenTesting 💻🚀
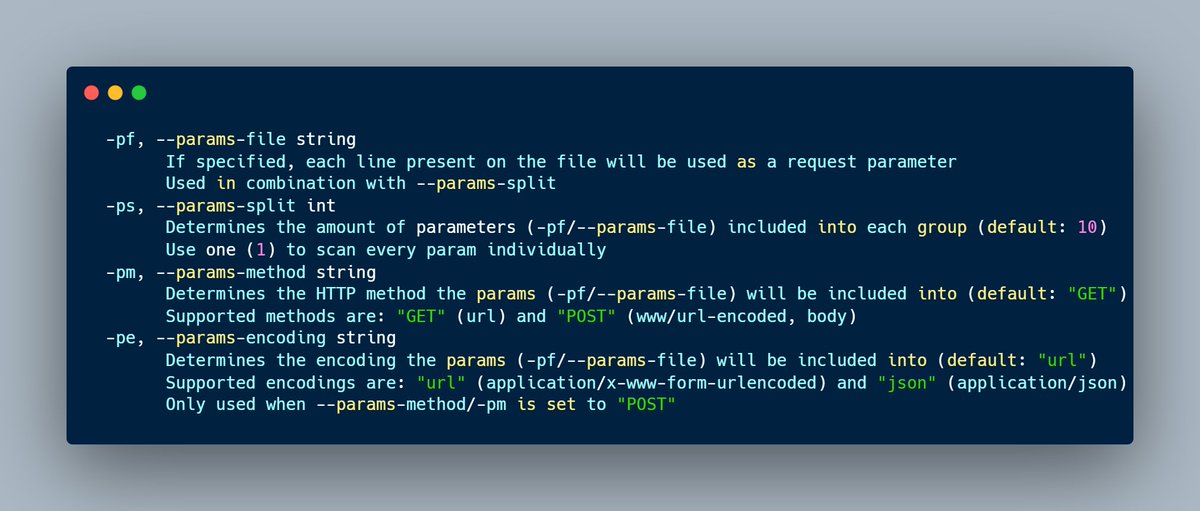
BB Hunters and Pentesters! 🕵️♀️GBounty now supports automated fuzzing of new parameters with our -pf and -ps flags. Simply provide a file with your request parameters and we'll take care of the rest. Upgrade now and take your fuzzing to the next level! 🚀
👉https://t.co/hYNwESPnet
🙌Primer evento del año anunciado! Queremos agradecer a los sponsors que hacen que esto sea posible! gracias @kavak_ar @BurpBounty (@egarme) y @ArtsSEC por confiar en nuestra comunidad!
#BugBounty
🎉I want to announce that from today you can pay with BTC and ETH for Burp Bounty Pro and GBounty products. If you are interested please send me a DM for details. https://t.co/hYNwESPnet
🎉I just published Burp Bounty Pro version 2.6.2!
👉You can now export the burpsuite scope to a .zip file for scanning with GBounty @GBountySecurity
👉More information at: https://t.co/DXxo2SJU8z
🎉🎁Congratulations to the One Year GBounty License winners @MrW0l05zyn, @v1__nc and @sathwik1101! Soon, more surprises and discounts!
https://t.co/hYNwESPnet
Certificate Page: https://t.co/SDyHAA5j2q
🎉I want to announce that from today you can pay with BTC and ETH for Burp Bounty Pro and GBounty products. If you are interested please send me a DM for details. https://t.co/DXxo2SJU8z
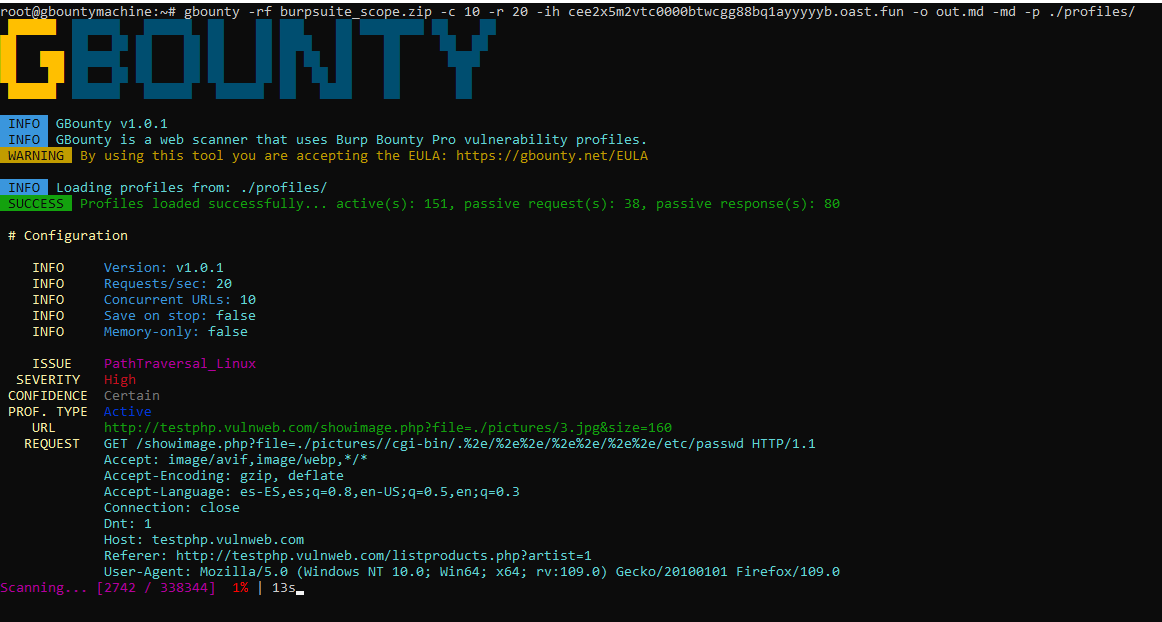
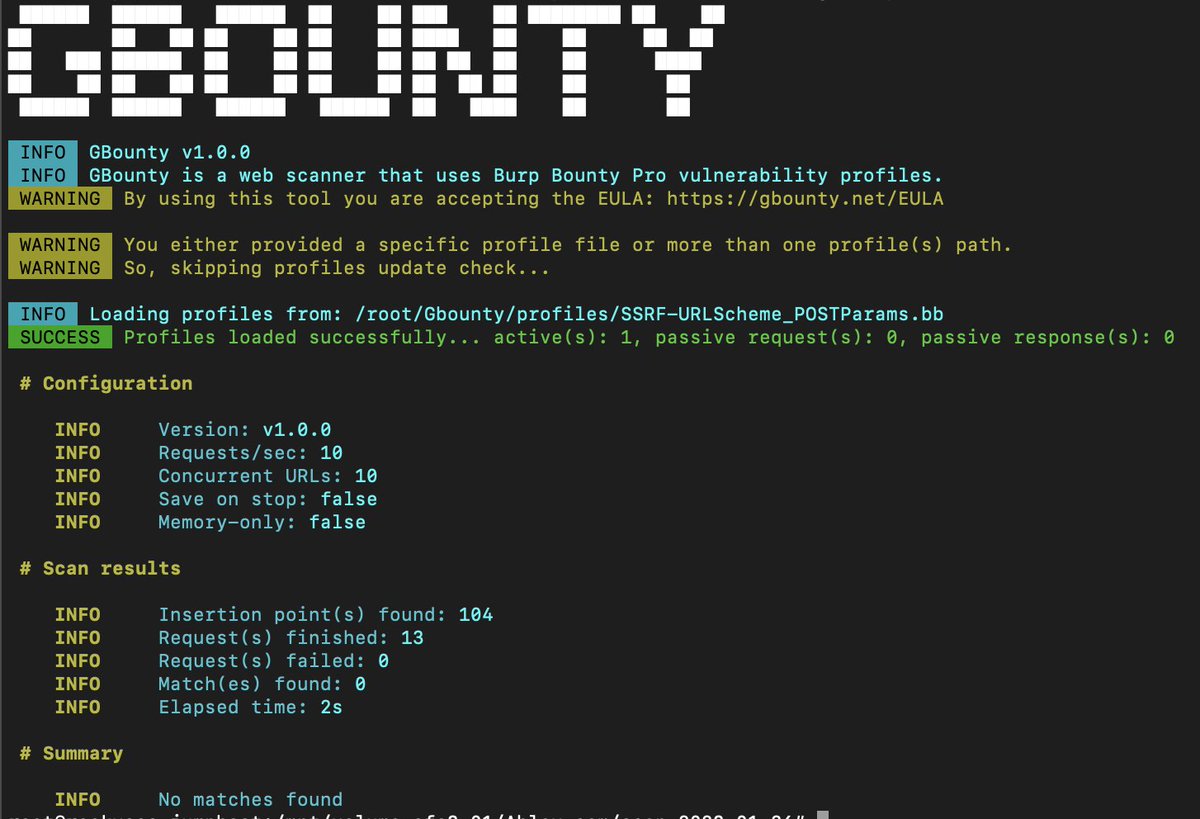
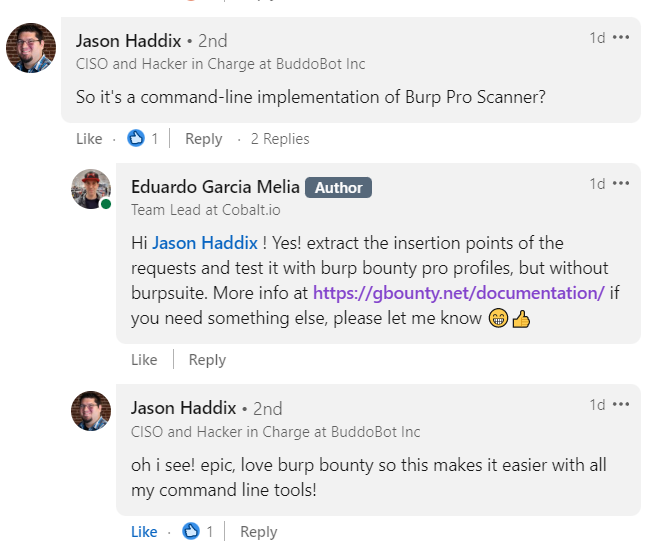
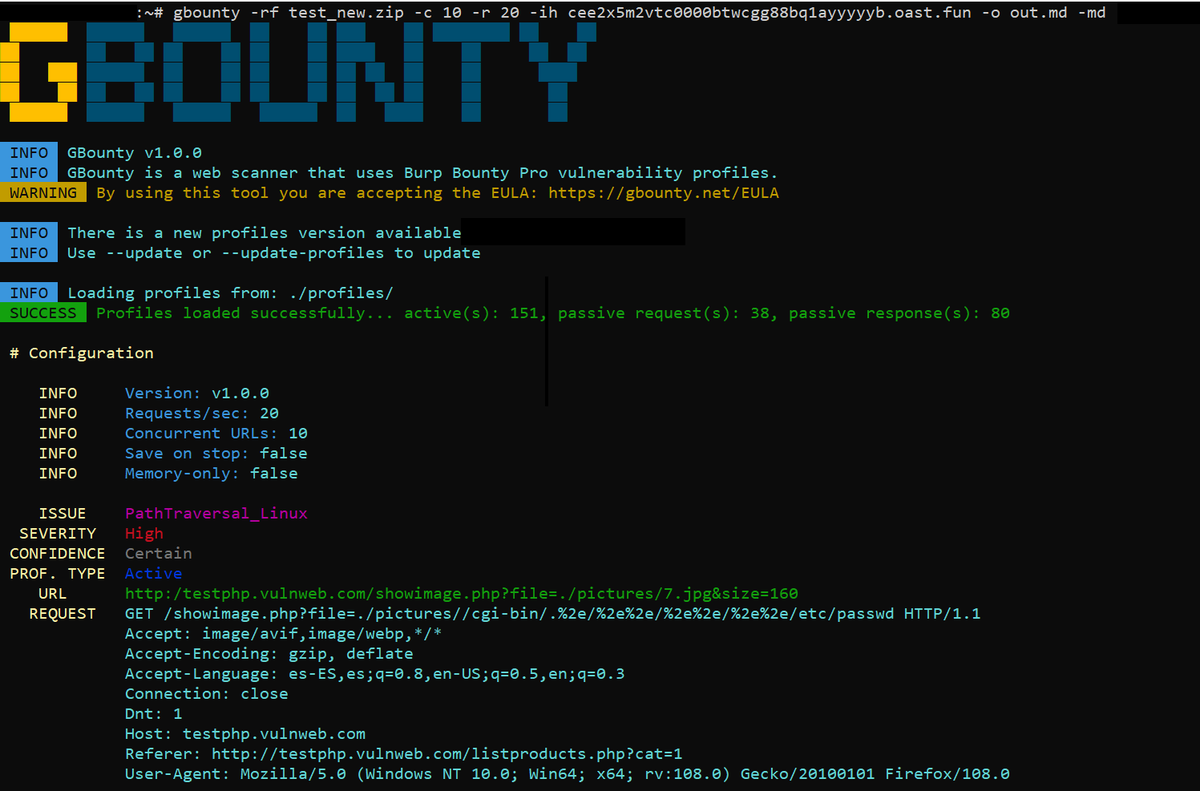
🎉GBounty is a Golang command-line implementation of Burp Bounty Pro Scanner
👉To celebrate the release of the GBounty, I'm giving away three licenses for one year among all the people who RT this post and follow @GBountySecurity
🕐The winners will be announced next february 9
GBounty is a command-line implementation of Burp Bounty Pro Scanner. It extract the insertion points of the HTTP requests and test it with Burp Bounty Pro profiles. You can manage the profiles without Burpsuite, through GBounty Profiles Designer tool.
https://t.co/qPuoB3l32L
Exciting news! 🎉 GBounty, the standalone command line website vulnerability scanner, is now available! 🚀 With its use of the vulnerability profiles of Burp Bounty Pro! securing your web apps has never been easier. Get 30% off with code BOUNTY30.
👉https://t.co/hYNwESPV41