🚨 GoPlus Security Alert:
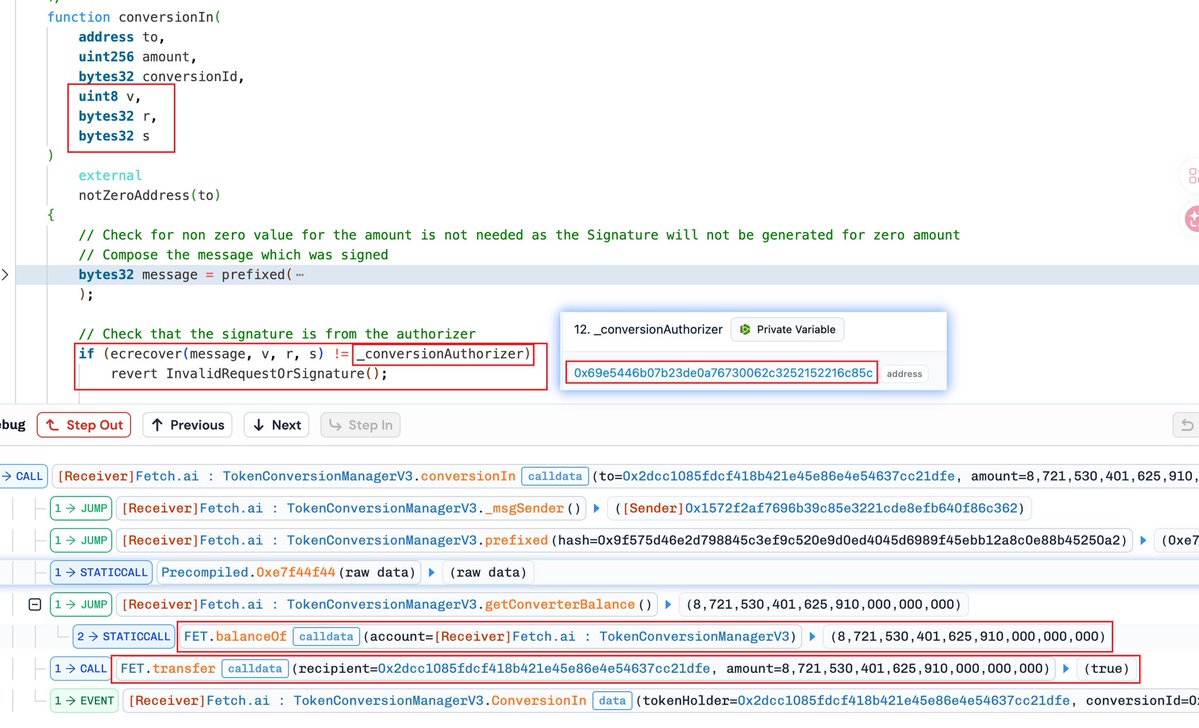
On Sept 20, @Fetch_ai and @nunet_global contracts were exploited. The attacker drained 8,721,530 ethereum:0xaea46a60368a7bd060eec7df8cba43b7ef41ad85 from TokenConversionManagerV3 and illicitly minted 408,532,878 $NTX. The attacker walked away with about $2M.
🔍 Root cause
A leaked @Fetch_ai conversion-authorizer private key, plus conversionIn() with no hard cap and no counterparty lock/burn proof. The contract ran as designed: it verified a valid ECDSA signature, then flushed every FET in the bridge to the attacker. The @nunet_global Deployer sat in the same compromised ops key cluster, so NTX was minted straight to the max cap.
Attacker
0x1572F2af7696b39c85E3221CDE8EFb640F86c362
Compromised @Fetch_ai conversion authorizer
0x69e5446b07b23de0a76730062c3252152216c85c
Compromised @nunet_global NuNet Deployer
0x863F13e5B505f1Eb17803b94EC9d3DaF80092165
Exploited @Fetch_ai contract (FET)
0xab424A430CC09864fA1277A38193111705ADF3A3
Exploited @nunet_global contract (NTX)
0xF0d33BeDa4d734C72684b5f9abBEbf715D0a7935
Payout wallet
0x2dcc1085fDCf418B421E45e86e4e54637cc21dfE
Attack txs
https://t.co/IH0uxnZPYD
https://t.co/x16KaficZq
We're aware of reports of an exploit involving a https://t.co/CwbPmOj7TU token conversion contract. Our team is investigating and will share an update soon.
Please rely only on official https://t.co/CwbPmOj7TU channels. We will never DM you or ask you to move your tokens.
🚨 Low-liquidity token alert:
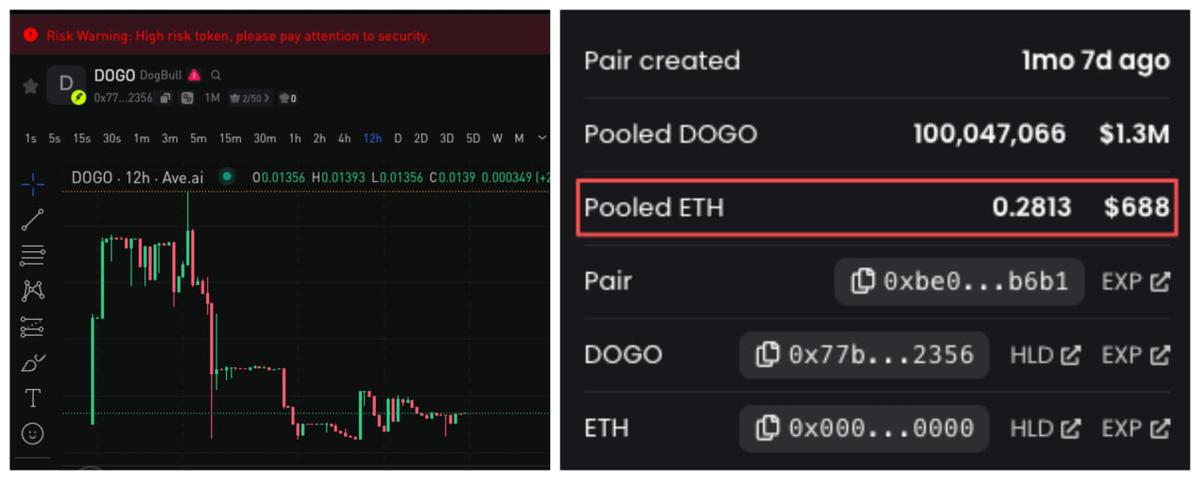
In Season 2 of Community Nominations, @Jimmyfestz nominated robinhood:0x77b0aa38451ccdc1b42587e2f80b9879a7f82356 on #RobinhoodChain: 0x77b0AA38451ccDC1b42587E2f80B9879A7f82356
Extremely thin liquidity with heavy wash-trading risk. Stay away to avoid losses.
🔍 #GoPlus review: reported market cap is ~$13.7M, with ~$1.34M nominal liquidity. Real exit depth in the LP is only about 0.28 #ETH. Inside the $1.39M of 24h volume, we found:
1. Wallet 0xef75…5bae bought 1,692,795.2348 DOGO with 9.383 ETH
https://t.co/yhgIbEdKYG
2. The exact same amount of DOGO was sent to 0x54ff…6edc
https://t.co/5oSFfNryoc
3. 41 seconds later, the second wallet sold that same batch back to the pool and received 9.382981234 ETH
https://t.co/TyU7bQS4KB
The Result: Net cost was only ~0.0000188 ETH + gas, but it printed 18.766 ETH in two-sided volume and logged two active wallets. Dozens of similar wallet pairs were spotted doing one-off ~1.6M buys and sells over the last 24h.
Sells match buys almost perfectly — blatant wash trading designed to fake volume and bait buyers.
📌 A #DeepScan audit of this token contract will be published in a later report. Keep the nominations coming.
1/2
The first "DeepScan Community Nomination" campaign has wrapped up — huge thanks to everyone who nominated 🙌
📢 Round 2 is now live — here's how to join:
1️⃣ Follow @GoPlusSecurity
2️⃣ Comment below: I nominate [Token Name] [Chain] [Contract Address] #DeepScanAudit
3️⃣ Nomination window: Sep 16 – Sep 23 (UTC)
🎁 Rewards: 10 lucky nominators will win 10U each
Selected projects will receive a full three-dimensional DeepScan audit — contract, token security, and liquidity — with the report published for all. Good or bad, on-chain data has the final say.
⚠️ Exploit breakdown: oracle manipulation on Nostra Finance
On Sept 17, the @nostrafinance money market on #Starknet was hit with an oracle price-manipulation attack. About $3.5M was borrowed out against inflated collateral.
The attacker pumped the NSTR oracle from ~$0.006 to $49.5 — roughly 8,000x — then used the overvalued NSTR as collateral to drain other assets. The money market is fully paused. Supply, borrow, and liquidations are all offline.
🔍 Attack flow
▪️ Months earlier (Mar / Aug): accumulated NSTR and pre-positioned collateral
0x06d48ef7
▪️ Sept 17, 05:23: created a fake NSTR/SolvBTC pool with 1.5 SolvBTC one-sided liquidity and hijacked GeckoTerminal’s pool selection
0x3aa300d2
▪️ 05:27–05:47: wash traded the pool and pulled liquidity from the market-making range
0x2d9fb4ed
▪️ 05:47–05:48: swapped through the thin pool and spiked the price to $49.5
0x2d9fb4ed
▪️ 05:48–05:50: borrowed out ETH / STRK / USDC / USDT / WBTC / DAI, ~$3.5M
0x06d48ef7
▪️ 05:51–07:08: dumped via AVNU / Ekubo / JediSwap; 2.2M STRK left the chain through NEAR Intents
0x06d48ef7
▪️ Around Sept 18: funds consolidated
0xa059aaab
💡 This is a classic low-liquidity oracle failure:
1️⃣ A illiquid token was accepted as collateral
2️⃣ The price feed relied on a third-party source — the attacker appears to have added surface liquidity so GeckoTerminal picked the rigged NSTR pool
3️⃣ Cost of attack: ~1.5 SolvBTC plus NSTR stacked months earlier at cheap prices
📌 Attacker wallets
▪️ Borrow account
0x06d48ef7ab62c26e3ef1987c322096cd508e9034c82048783a6b438fc1344bc3
6 borrows + ~80 sells. Interacted with NSTR contracts in Mar and Aug 2026 — this was staged months ahead.
▪️ Manipulation account
0x2d9fb4edec9d5c015c43514ca5a309aab1b2638c3a45ad750d09ee971d0da23
Ran the pump/dump flow.
▪️ Transit wallets
0x0285b4bf99e227c4baed7f9a8c7c673771fe0b75e897f7350729e3e13021321d — received 1.2M STRK
0x074f5318f8d60ad0832068dc0430d0a0e2f9dd0c2e710fb8c032945a3804b57e — received 1.0M STRK
Both immediately bridged out via NEAR Intents.
▪️ Ethereum consolidation
0xA059Aaab82773CAf622DE9d9A0F2dBF9Aa7F3c37 — ~$1.9M
Another ~$1.5M is still sitting in the borrow account.
▪️ Sample txs
https://t.co/U5LSUEBoSs
https://t.co/Dg9C3oBW2Q
On September 17, a manipulated NSTR oracle price enabled one account to borrow approximately $3.5 million worth of ETH, STRK, USDC, USDT, WBTC and DAIv1 against NSTR collateral in the Nostra money market on Starknet.
The Nostra money market is paused: lending, borrowing, withdrawals and liquidations are currently unavailable. We are reconciling the impact on each asset and tracing the funds. The final loss and potential recoveries are not yet known.
We are working with relevant parties on recovery and will share verified updates, including a detailed post-mortem.
Beware of impersonators. Nostra will never DM you or ask you to connect a wallet as part of recovery.
Ongoing updates will be posted in our Discord.
Got drained. Staring at an empty wallet. You tweet for help. DM KOLs. Google guides. Ask AI. In that panic, a lot of people get hit a second time.
Stop scrambling. Stop guessing.
GoPlus just shipped Wallet Theft Detective — a local, read-only Skill that lets your AI Agent hunt down the root cause of the drain.
Built specifically for theft forensics. Covers 20+ common off-chain attack vectors:
• Clipboard hijacks & address swaps
• Infostealers
• Malicious browser extensions
• npm / PyPI / software supply-chain poisoning
• Malicious IDE plugins & fake SDKs
• Fake support, fake job offers, fake meetings & upgrade phishing
• Drainers, malicious approvals, Permit, blind signing & address poisoning
• Seed / private key storage leaks
• Fake wallets & mobile permission abuse
…
Open source. Get your Agent ready before you need it:
https://t.co/zjY81oQhtb
2/2
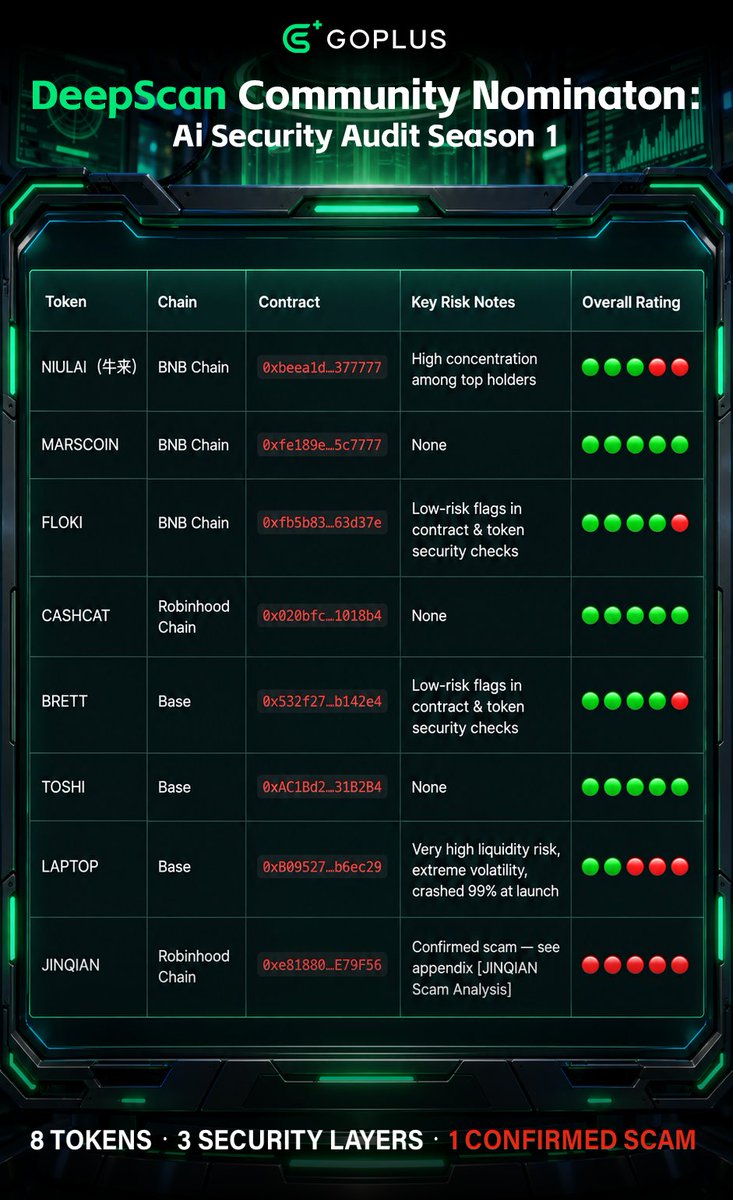
Three highlights from Round 1 :
🚨 We exposed a pig-butchering scam ($JINQIAN)
📉 A perfect-scoring contract still crashed 99% ($LAPTOP)
🔍 Serial token deployments aren't always a red flag (ethereum:0xcf0c122c6b73ff809c693db761e7baebe62b6a2e)
Other audit results are as follows:
1/2
The first "DeepScan Community Nomination" campaign has wrapped up — huge thanks to everyone who nominated 🙌
📢 Round 2 is now live — here's how to join:
1️⃣ Follow @GoPlusSecurity
2️⃣ Comment below: I nominate [Token Name] [Chain] [Contract Address] #DeepScanAudit
3️⃣ Nomination window: Sep 16 – Sep 23 (UTC)
🎁 Rewards: 10 lucky nominators will win 10U each
Selected projects will receive a full three-dimensional DeepScan audit — contract, token security, and liquidity — with the report published for all. Good or bad, on-chain data has the final say.
🚨 GoPlus Security Alert: Watch out for copycat rugs on Arc
Arc Chain's launch is hot — day-one volume passed $144M. While most users are still figuring out how to bridge, copycat rugs of high-cap Launchpad tokens $ARGUS and $TOLLY are already popping up.
⚠️ Stay sharp. Double-check the CA before you trade.
According to GoPlus security research: Of 324,000 token issuances on Robinhood, the main risks that have appeared include business fraud, technical risks, contract vulnerabilities, trading security, and social engineering fraud. https://t.co/g86MiB34kz
1/4
⚠️ Exploit Breakdown
On Sep 15, 2026, a whale’s #Safe wallet was drained via an auth bypass in its strategy executor. Loss: ~$7.8M.
❓ Root Cause
Any caller could set the target to `address(this)` and skip both authorization checks, then `DELEGATECALL` through an already-enabled Safe Module — running arbitrary logic in the Safe’s own context.
The attacker dumped ~2,900 aEthrsETH into a Uniswap v4 pool paired against a worthless PAT token, leaving the victim Safe with nothing but junk LP NFTs.
The original exploit tx was front-run by MEV bot "Yoink", which walked away with the entire rsETH stack.
🔍 Attack Flow
The bug sits in this unverified strategy executor:
0x4f0055926c839D1d960a82CBF84E2eE933958ebC
Not in Safe core. Not in Aave. Not in rsETH.
(1) Intended path: the target must be an allowlisted Safe, and `msg.sender` must be a Module enabled by that Safe.
Set the target to `address(this)` — the executor itself — and both the allowlist check and the Module auth check get skipped.
TermiX × @GoPlusSecurity — Security Agent Free Trial
Pay $19.9 for an AI security audit, get $25 back:
💵 12.5 USDC + 🪙 $12.5 in base:0x0c1dc73159e30c4b06170f2593d3118968a0dca5 + ⭐ 50 TermiX Points
Only 40 slots. First come, first served. 🧵👇
🚨 GoPlus Security Alert: active proposal attack on #Ampleforth
On Sept 12, a freshly funded EOA submitted a malicious proposal on @AmpleforthOrg. Masked as a completed-work grant for SPOT ecosystem analytics tools, it asks to send 2,500,000 USDC from the treasury to the proposer — nearly all liquid treasury funds.
Proposal: https://t.co/obXj2Kk3VW
Status: Pending. No votes. Funds have not moved.
The pass threshold is the risk. 75,000 FORTH to propose, 600,000 FORTH to pass. At the alert-time price of $0.27, ~$160k of voting power could clear $2.5M USDC. Stay sharp.
Proposer / payout
0x730C97E793f6F7c476C6AeB3E1c3fDad4714dd82
87,238.546 FORTH voting power
Delegator
0x38cAaa5782BF8afF646403D567D76b016d5c24D8
Same 87,238.546 FORTH. Delegated to the proposer 19 minutes before submission.
Relay / funder
0x92fc19271fce6d48cd41a0eff6f5dd40f1090d72
Sent 87,238 FORTH + 0.005 ETH gas to the delegator.
GoPlus DeepScan Community Nominations | AI Security Audit Season 1 — Winners
Congrats to the 10 nominated winners below. Each takes 10 USDT:
@zh3352933964827@hnzh239805@Mawarsayu44@Lopyou54804819@0rmid@ShubroSutrk7j@FinaNuruls@xyzjellalz@Web3boyz04@Minionzwis
Notes:
1. Payouts will be coordinated via official DMs shortly. Ignore phishing links and impersonator accounts.
2. Draw run by Grok AI: valid reply handles were sorted, then sampled with a SHA256 seed from the post ID. Fully reproducible.
Which Meme/DeFi project do you want audited for free?
"You Nominate, We Audit" — weekly: Community nominates → DeepScan runs a free AI audit → results drop every Thursday on Space.
Rewards:
🎁 10 random nominators get 10U each, every week
🎙️ Interact with our Thursday Space (tune in / repost / comment), 5 more people get 10U each
How to join: comment below
I nominate [Project Name] [Contract Address] #DeepScanAudit
Only #BNBChain #Base #RobinhoodChain. Contract address required.
If a nominated project has questions about the audit results, come join the Space.
Per DeepScan Community Nominations rank, full review of token security, contract risk, and on-chain liquidity:
$牛来, $MARSCOIN, $FLOKI, $CASHCAT, $JINQIAN, $BRETT, $TOSHI, $LAPTOP. https://t.co/E2La3Iko8c
$LAPTOP crashed 99% after launch. Still worth aping?
An on-chain and smart contract security breakdown.
Token: Hunter Biden’s Laptop ($LAPTOP)
Base contract: 0xB095274743941e953c746F9C228DA9c18Bb6ec29
Snapshot: Sep 10, 2026
⚠️ Overall risk: Extremely high liquidity risk.
Ownership remains highly concentrated. Closely monitor fund movements by the founding team and market makers, watch for new disclosures, and adjust your trading strategy accordingly.
Ⅰ. Price action: From launch to a 99% drawdown
• Sep 9 launch: ~$0.40. A sniper bought 2,268.56 tokens for 900 USDC.
• Sep 9, 12:09: ATH of $199.50. GMGN briefly showed a $257.9B market cap after a 7,716% five-minute spike.
• The initial pool was razor-thin, allowing a single buy to send the price vertical.
• Later that day, the sniper fully exited at an average of ~$111, booking $250K+ in profit—a 278x return.
• Sep 10, 01:14: ATL of $0.7234, down 99.64% from ATH.
• Current range: $0.72–$1.02, showing early signs of stabilization.
• Nominal market cap: ~$335M. FDV: ~$1.02B.
Ⅱ. Liquidity and trading activity
24-hour volume was approximately $36.7M on CoinGecko, with $17.4M routed through Aerodrome.
Liquidity is migrating to Aerodrome:
• Aerodrome liquidity: ~$1.62M
• Share of total on-chain liquidity: ~74%
• Total tradable liquidity: only ~$2.2M
• Uniswap-based liquidity: ~$550K spread across roughly 380 pools
• Liquidity/market-cap ratio: ~0.65%
Any sell order above $50K could cause significant price impact.
The volume-to-liquidity ratio is approximately 17x. That is elevated, but still explainable during a highly speculative launch phase. It is too early to call this wash trading—continued monitoring is needed.
Ⅲ. Holder concentration
• Holders: 31K+
• Largest holder: 30%, identified as the founder allocation under lock
• Nominal Top 10 concentration: 96.32%
• Adjusted Top 10 concentration after excluding custodians, pools, and confirmed locked allocations: ~27.8%
Ⅳ. Contract security: No vulnerabilities or backdoors detected
GoPlus DeepScan AI audit: No vulnerabilities detected.
Full report:
https://t.co/P2WoQtIRGs
GoPlus Token Security: No backdoors detected.
Full report:
https://t.co/HS68Ri2zvw
A clean contract does not eliminate liquidity, concentration, governance, or market-manipulation risk.
Ⅴ. Five critical signals to monitor—in priority order
① Multisig outflows
Watch all outbound transfers from:
`0xd81bf90a`
`0x296f38f1`
`0xeff4d820`
`0x8aeaffde`
`0xcb92b4cb`
Pay particular attention to any movement from the 30% founder allocation before the publicly stated lock expires in March 2027. Any such movement would breach that commitment.
② Upgradeable distribution contract
Monitor implementation changes to `0x38e33d04`, which holds 7.92% of supply.
Its admin, `0x9fc64850`, is a single EOA. Because the contract is upgradeable, the allocation rules could be changed.
③ Aerodrome LP movements
Aerodrome currently holds 74% of total on-chain liquidity. A major LP withdrawal could create an immediate liquidity cliff.
④ Dynamic-fee hook pools
Track whether fees are increased as trading volume grows.
⑤ Prediction-event allocation
Monitor whether the 30% allocation is released according to the announced schedule—or whether its distribution rules are deployed and enforced on-chain.
Ⅵ. Hunter’s public statement vs. on-chain activity
After the crash, Hunter stated on X that:
• The team allocation was locked.
• Nobody on their side had sold.
• He personally had not made a single dollar.
• The crash was mainly caused by thin liquidity, technical issues, and sniper bots.
What the chain shows:
• The 30% founder allocation does appear to be locked. Those 300M team tokens were not directly sold.
• Before launch, a project multisig—`0x8aeaFfdE02E751C04D96cec90D93f93C50Bcc530`—received 100M $LAPTOP, equal to 10% of total supply.
• Its current balance is 57,499,200 tokens, implying net outflows of approximately 42,500,800 tokens.
• Transfers went to addresses associated with GSR (15.5M), G20 (5M), Wintermute (2.5M), and other wallets.
Important distinction: 42.5M tokens transferred does not mean 42.5M tokens were sold.
What can currently be established:
• The project multisig moved approximately 42.5M tokens to market-making, operational, and unlabeled addresses.
• Those tokens were capable of entering the market around launch.
• Wintermute sold at least approximately 466,300 tokens, receiving around $2.08M.
• An unlabeled address holding 14.5M tokens still retained them at the snapshot time, so they should not be counted as sold.
• Transfers to GSR, G20, or exchange deposit addresses do not prove that every transferred token was sold on the open market.
🚨 URGENT: PHISHING ALERT
If you got an email from [email protected] titled “Critical Security Alert: STM32 Entropy Vulnerability” telling you to click a link and run a “device check” — stop. Do not click anything.
That mail is not from Trezor. Their third-party email provider got compromised, and attackers used it to send a fake entropy/RNG advisory.
Same vendor-email blast is also hitting CoinTracking and BitBox users. Treat every “security update” link as hostile. No downloads. No xPub. No seed.
Our third-party e-mail provider has been breached. Please be aware that the email named ‘Critical Security Alert: STM32 Entropy Vulnerability’ is not coming from us, and it’s a phishing attempt. Do not click on any link.
We have taken down the domain, and we are investigating the situation, including how the hackers got access to our legit domain.
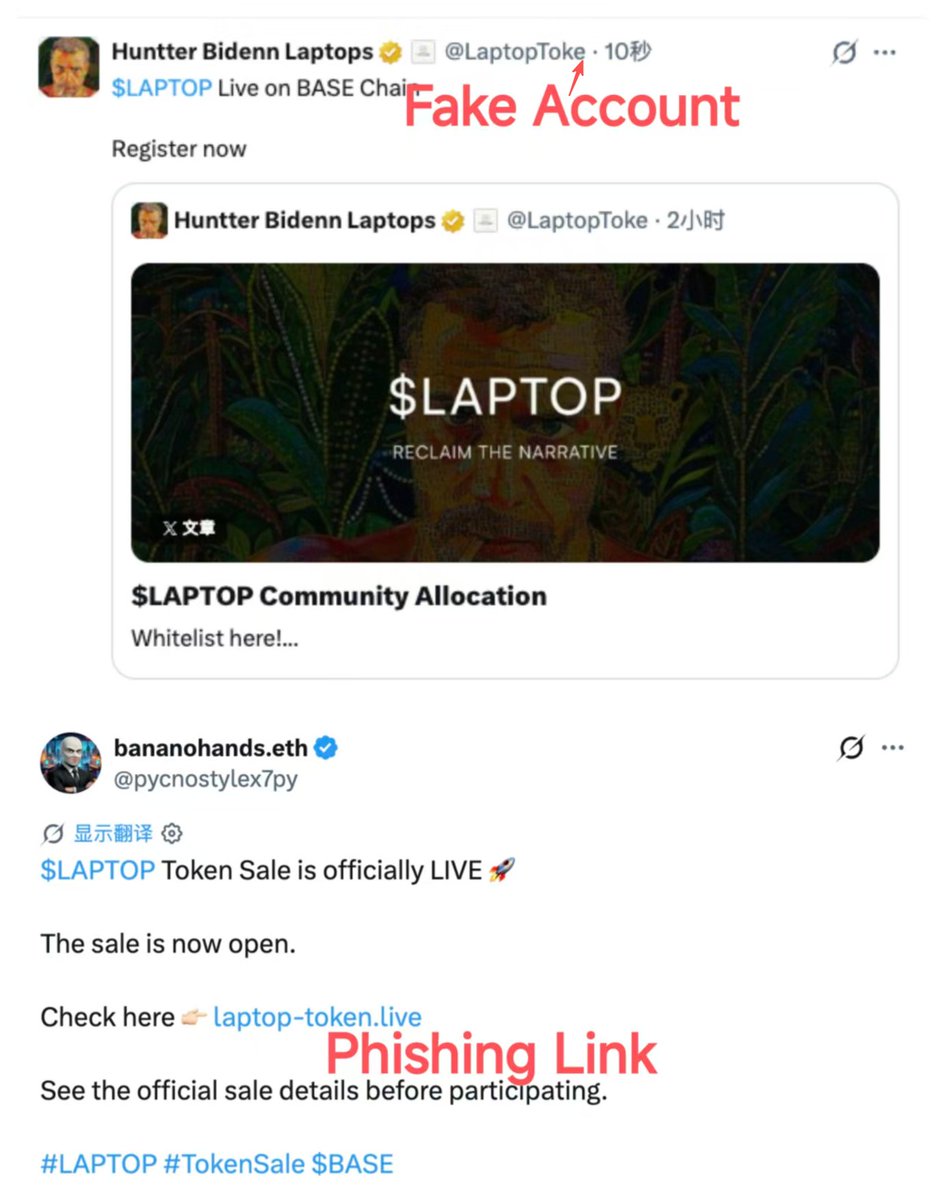
🚨 GoPlus Security Alert: Beware of phishing sites impersonating the $LAPTOP airdrop and same-name copycat tokens with security risks such as unverified contract source code and high taxes.
The $LAPTOP meme coin associated with @HunterBiden is expected to launch with an airdrop soon. Numerous phishing sites are already appearing on X, posing as $LAPTOP airdrop whitelist registrations, eligibility checkers, and claim pages.
Meanwhile, copycat tokens using the same $LAPTOP ticker are being traded across multiple chains. Their contracts may carry risks including unverified source code, high transaction taxes, and the ability to pause trading.
🛡️GoPlus Security Recommendations:
1. Rely only on information from the official website and official X accounts. Verify updates through @HunterBiden and @Laptoptoken.
2. Exercise caution when trading copycat tokens. Always use GoPlus Token Security to check the contract before interacting.
3. Remember the #GoPlus “Four Don’ts” for phishing prevention:don’t click, don’t install, don’t sign, and don’t transfer.
Don’t click unfamiliar links. Don’t install software from unknown sources. Don’t sign wallet transactions you don’t fully understand. Don’t transfer funds to unverified addresses.