📣📣📣 Calling all Chrome bug hunters! 📣📣📣
Rules updates: We're rewarding more types of deep security research, recognizing high-value fixes across more severity tiers, and providing new opportunities for researcher recognition.
For details, see our latest blog post 👇
https://t.co/BwwD6gFDKz
📢 PSA for open-source bug hunters
We are temporarily no longer accepting OSS VRP product vulnerability submissions. This does not impact OSS VRP supply chain reports, or any outstanding reports. As an alternative, we encourage you to find impact across our other VRP programs and submit there instead, or pursue the Patch Rewards Program.
Why is this happening? This pause is due to a significant rise in automated submissions, the vast majority of which are not valid. We will continue to reformat and work on this aspect of the OSS VRP and commit to giving an update in Q1 2027.
https://t.co/nQEkHVfbHS
Introducing PageBreak, an agentic vulnerability discovery tool using deterministic validation to achieve a near-zero false positive rate.
How it works: https://t.co/n3k4vvNhoq
For real-world vulnerabilities PageBreak has discovered 👇
https://t.co/0pZ5rWoWw2
ESCAL8, Google’s annual flagship security conference, is coming to Singapore in October 2026, with a particular focus on AI Agents! 🇸🇬
Check out our blog post to see what's planned in the three main segments of the conference: bugSWAT, Hackceler8, and init.g() 👇
https://t.co/XRMeM5AP2R
📢📢📢 Attention bug hunters!
Want to know more about how brutecat found a vulnerability in Google’s internal APIs, bypassing authorization to exploit the GFile library to gain access to internal filesystems and storage?
If yes, check out his blog post 👇
https://t.co/ehwrnqHJlX
📢 Tracking our VRP rules just got easier!
We are now mirroring our VRP rules and help articles directly on GitHub. Perfect for automating your workflows and tracking changes. 👇
https://t.co/X62wYRF2ed
Teamwork makes the dream work 🙌
Google Bug Hunters now supports sharing the recognition (and splitting the financial reward) for reports you have submitted, but were researched and created in collaboration with other researchers. Details 👇
https://t.co/KuN2dR4CZy
Interested in crypto 🔒?
Check out our latest post which analyzes recent results published by Anthropic and argues that these advances, while significant, do not signal the downfall of cryptography.
https://t.co/kNM1fd6qGs
Check out Tomas' post and article on hacking Google using Git integrations. One of these reports even won him Most Valuable Hacker (MVH) at Google's bugSWAT event in Vegas last year!
The written version of my BSides Riga and @bsidesvilnius talks is up: exploiting git integrations in cloud services, with four bugs I found in GCP (Looker, Dataform), including the one that won me MVH.
https://t.co/HuWlK5dnfj
"brutecat is super talented", "luckily I'm not oncall ;)", "incredible"
These are all real quotes from Googlers after seeing this blog post. Amazing work @brutecat, thank you for sharing!
📢 PSA for security researchers!
In our latest post, we're taking a closer look at how Google Spark (which was recently launched) works, ways to approach bug hunting in Spark, and how to distinguish high-impact vulnerabilities from expected system behavior 👇
https://t.co/37pXXUJBy2
📣Blast from the past📣
This post takes us back to a flaw discovered in 2010: while technology has advanced, the general story of how the flaw was detected is still a great example of effectively identifying and remediating a security issue.
https://t.co/NzKPw5m0Fv
📢 More on Google's approach to post-quantum cryptography 🔐
This time, we're taking a closer look at digital signatures and the complex challenges they present, and discussing the opinionated paths we are taking at Google in this space.
https://t.co/l9Ppmwci45
More on passkeys 🔐!
This time we are focusing on storage options, in particular the differences between using a password manager vs. a hardware security key to store your credentials, and why you might choose one option over the other.
https://t.co/1t5KM94EKm
In April 2026, we held the latest edition of bugSWAT (our live event for security researchers) in Seoul, South Korea.
For more information on this edition's focus, its impact & winners, as well as bugSWAT in general, see 👇
https://t.co/uJaaTARPM7
📣📢 Calling all Android and Chrome bug hunters 🧑💻🔎!
We're updating our Android & Chrome VRP programs to ensure we can continue to reward the most challenging and impactful vulnerabilities researchers find in our products. For details, 👇
https://t.co/hyZzEIampk
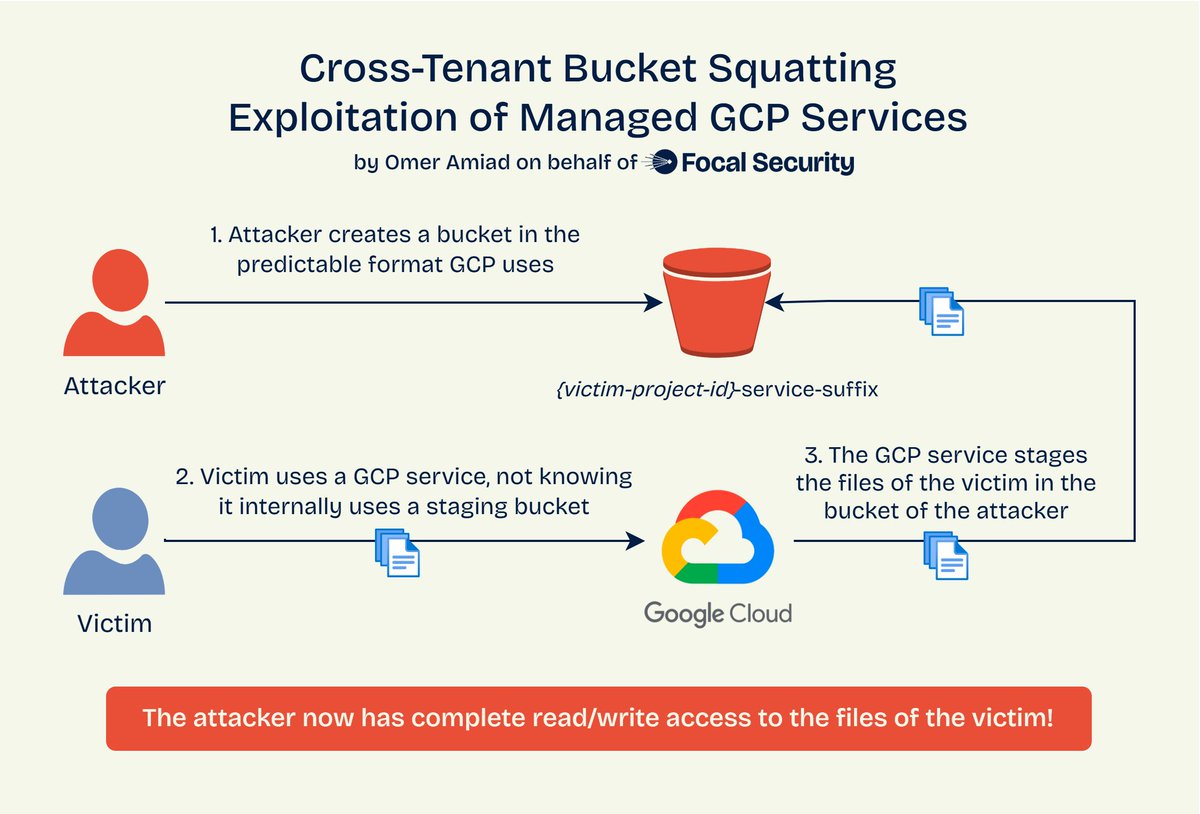
I achieved a cross-tenant #RCE in #GoogleCloud simply by abusing predictable bucket names. 🪣
In my latest research for @FocalSecurity, I look into "Bucket Squatting" - a cross-tenant attack that landed me 3 critical vulnerabilities in GCP.
Here is how it works:
📢📢📢 Attention bug hunters!
The Google VRP is updating its reward model, with a focus on the impact of vulnerabilities and the sensitivity of the data involved. To this end, we're introducing two dimensions: Information Tiers and Action Criticality. 👀👇
https://t.co/QVXiZVBazJ