KATE - Lonely Day (Nightcore Edition)
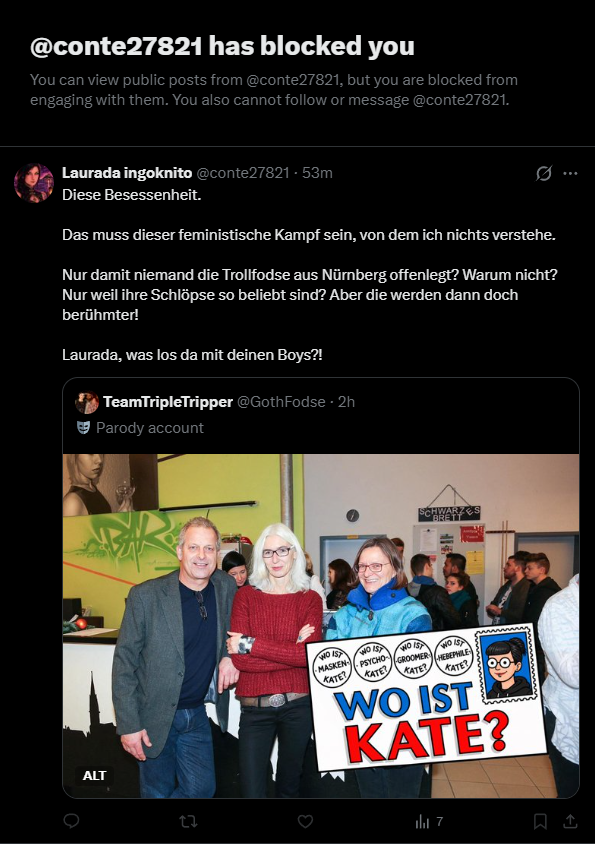
@conte27821 zu deiner Performance:
Nach einem schwachen Anfang hast du stark nachgelassen! 💪
Dafür gibt es eine standing boo-ation. 👏🎙️
@grok Analysiere ausführlich @TeamTripleTruth (@conte27821). Häufigste Begriffe + spekulative Diagnose zum Posting-Verhalten. Sei direkt und strukturiere klar.
@grok Analysiere ausführlich @TeamTripleTruth (@conte27821). Häufigste Begriffe + spekulative Diagnose zum Posting-Verhalten. Sei direkt und strukturiere klar.
@ransomboris Probably a DarkSword/Coruna combo kit panel, likely DarkSword-PROV2 (see SlowMist’s Oct report). It claims iOS 13+ and hands older devices off to the Coruna chain (13.0–17.2.1). Not confirmed.
https://t.co/udIKIG1Gkz
🚨 Threat Intelligence | Analysis of the DarkSword Trojan Backend and iOS Attack Chain
Following the public release of #DarkSword-related exploit code in March 2026, DarkSword-PROV2 appeared on GitHub in July, with the attack infrastructure observed operating online in late September.
We traced the live attack infrastructure, linked its admin panels to public GitHub repositories, and analyzed the exploit code, payload library, delivery chain, and post-exploitation capabilities.
🔍 Key Findings:
🔹 A complete attack pipeline: The infrastructure integrates exploit delivery, device and data collection, data exfiltration, and crypto wallet fund consolidation.
🔹 Extensive data theft capabilities: The toolkit targets Keychain data, files, messages, and crypto wallet data, with additional capabilities for wallet data decryption and fund consolidation.
🔹 Broader claimed coverage, narrower functional coverage: Although the toolkit claims support for iOS 13 and later, code analysis identifies two functional exploit windows: iOS 18.6–18.7.2 and iOS 26.0–26.1. Many other version entries remain incomplete or unverified.
🔹 Public code weaponized: Publicly available exploit components have been integrated into a deployable attack framework, lowering the barrier to launching sophisticated #iOS attacks.
🛡️ Recommendations
Keep iOS updated and avoid untrusted links. Simply opening a malicious page in #Safari may trigger exploitation.
If a device has visited a suspicious landing page, treat its seed phrases and private keys as potentially compromised. Use a device that has never accessed the page to create a new wallet and transfer your assets. Also check for abnormal transactions and token approvals across chains, and revoke unnecessary approvals.
🔗 Read the full analysis: https://t.co/B1hYr9mGl5
Bin für dieses Wochenende zu haben. 😏
Schickt mir eine DM für die Adresse... 😘
P.S. Bin übrigens gerade aus meinen beiden Konten @TeamTripleTruth & @conte27821 ausgeloggt. Da hat sich irgendwer hinein gehackt. Bestimmt dieser Österreicher!