🟧 #HackTuesday 🟧
Hack Tuesday: Week 17 - 23 July 2024
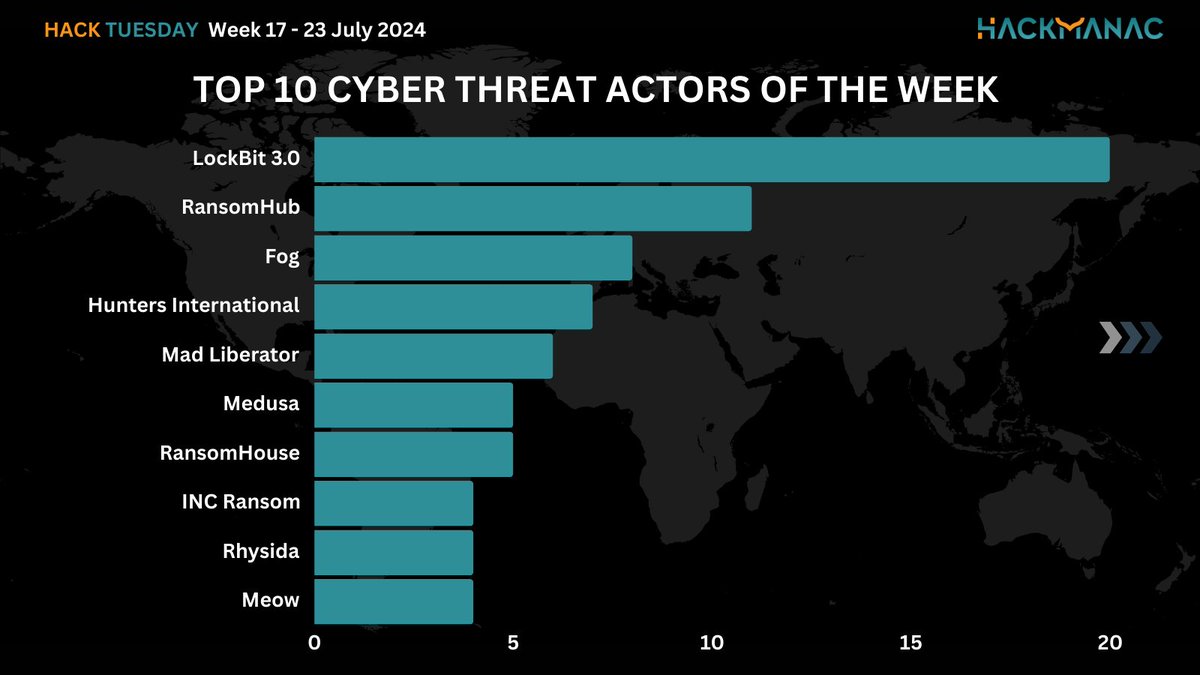
🚨 94 victims by 23 hacking groups 🚨
The most active ransomware group this week is LockBit 3.0 with 20 claimed attacks.
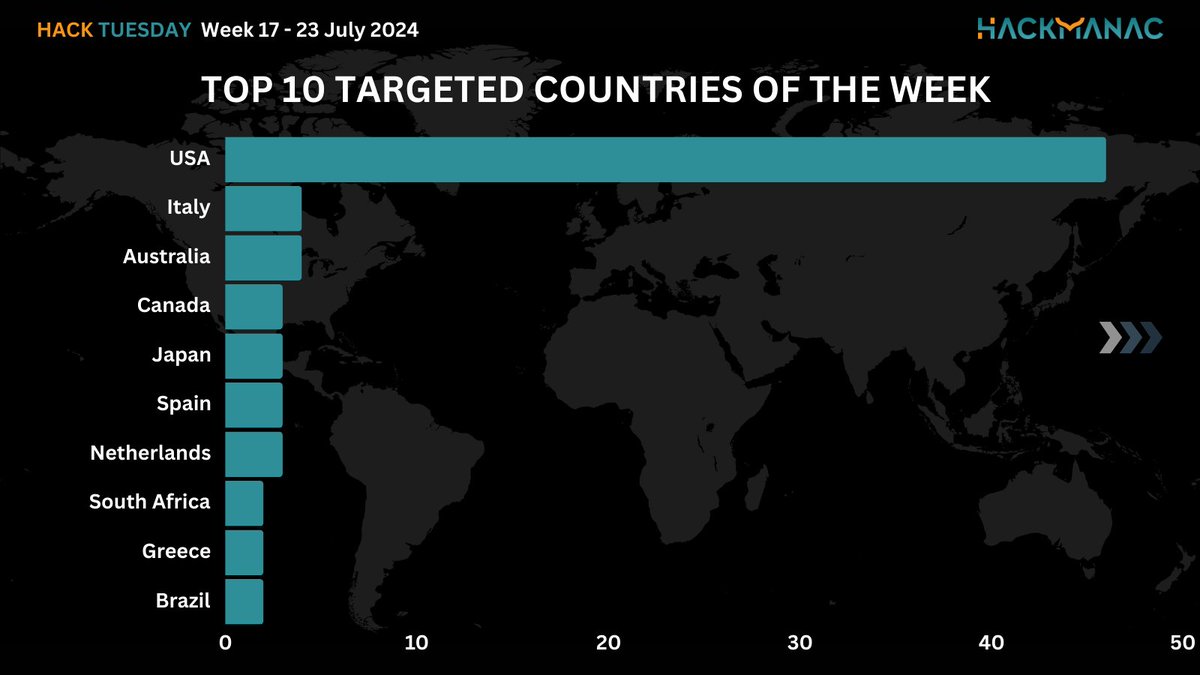
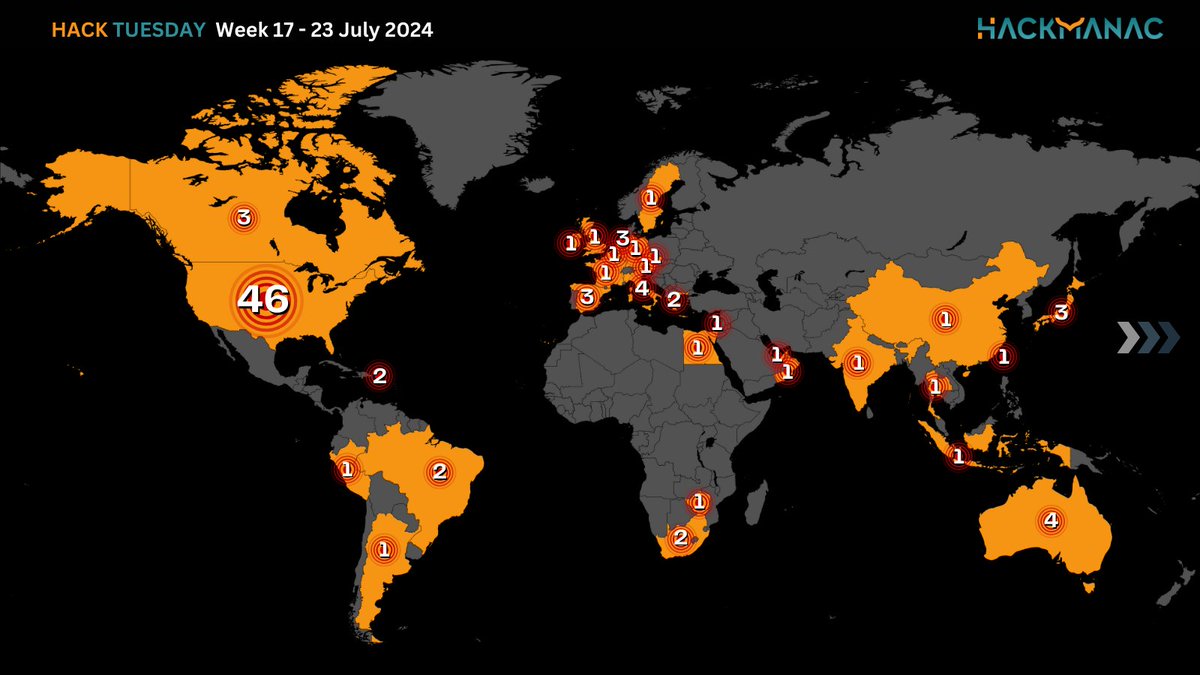
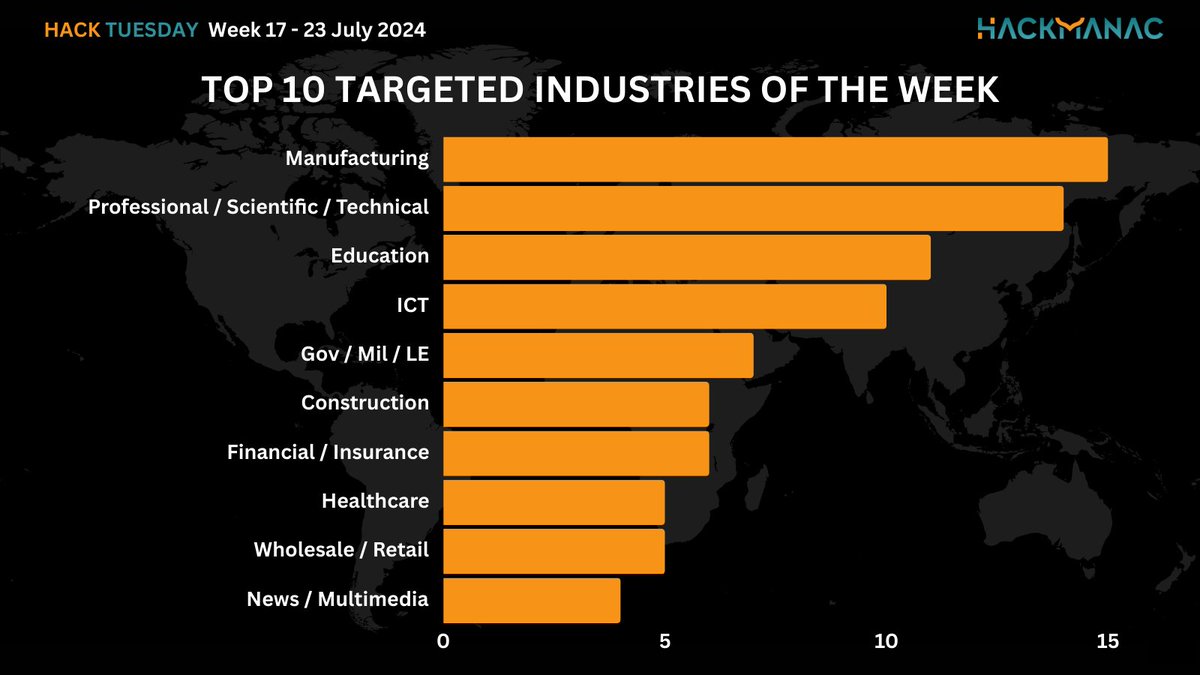
The most affected country is the United States, accounting for 49% of the victims, while the Manufacturing sector is the most impacted, accounting for 16% of the claimed targets, followed by the Professional, Scientific and Technical sectors with 15% and Education with 12%.
The average Cyber Risk Factor is 4.1.
#Ransomware #DataBreach #CyberAttack #HT
🇺🇸#USA#Snowflake
🚨🚨 Hackers Steal Text and Call Records of ‘Nearly All’ AT&T Customers 🚨🚨
In a major data breach, hackers infiltrated a cloud platform used by AT&T, stealing call and text metadata for nearly all of AT&T's cellular customers from May 2022 to October 2022.
The stolen data includes records from AT&T’s cellular customers, customers of mobile virtual network operators (MVNOs) on AT&T's network, and AT&T landline customers who interacted with cellular numbers during this period.
The breach also impacted a small number of records from January 2, 2023.
While timestamps were not included, the metadata reveals which numbers were called or texted.
The breach was traced to the Snowflake data warehousing tool, previously linked to other high-profile breaches.
Read more:
https://t.co/sfgrWHBiBB
#DataBreach
🚨#CyberAttack 🚨
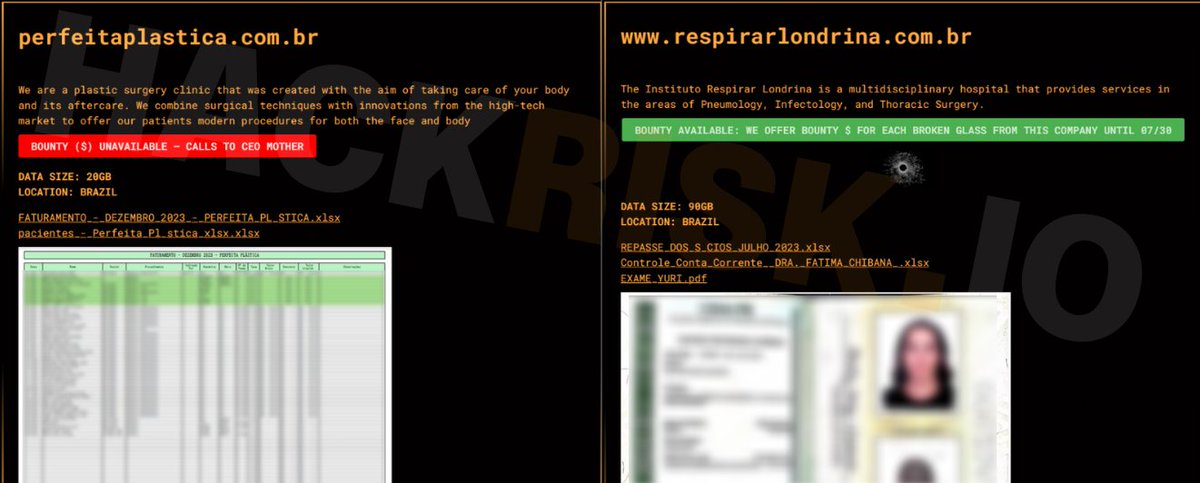
🇧🇷#Brazil: The number of victims on the Ransomcortex data leak site rises to 3.
Shortly after publishing the first attack on Policlínica Dona Anita, Ransomcortex claims to have hit two other Brazilian entities:
Perfeita Plástica - 20 GB allegedly exfiltrated
Instituto Respirar - 90 GB allegedly exfiltrated
#Ransomware
🚨 #CyberAttack 🚨
🇺🇸 #USA, American Golf Corporation
American Golf Corporation has been listed as a victim by the Medusa ransomware group.
Ransom demand: $2,000,000.
The hackers allegedly exfiltrated 154.9 GB of data, including email correspondence, members’ data, orders, full access account credentials (User ID, Passwords, Secret Keys), reports, licenses, passports, and financial data.
Ransom deadline: 20th Jul 24.
American Golf is one of the most experienced and innovative operators in the golf industry today.
#Ransomware
#CryptoFraud
🚨 Multibillion Crypto Fraud and Torture in Southeast Asia 🚨
Two major crypto crime cases have emerged in Cambodia and Malaysia.
Elliptic revealed that the Chinese marketplace Huione Guarantee facilitated $11 billion in scam transactions using tether (USDT). The platform provides scammers with personal data, telecom equipment, and AI face-changing software, and is linked to Cambodian PM's cousin, Hun Manet.
In Malaysia, bitcoin miners have stolen $725 million in electricity since 2018. Authorities seized 2,022 BTC mining machines in October 2022.
Read more:
https://t.co/pK8Y7FQZbT
#BTC #Bitcoin #Crypto #Theter
🚨 #CyberAttack 🚨
🇯🇵Japan Alerts on North Korean Kimsuky Hackers
Japan's Computer Emergency Response Team Coordination Center (JPCERT/CC) has issued a warning about attacks targeting Japanese organizations by the North Korean 'Kimsuky' APT group.
These attacks, which began in March 2024, involve phishing emails impersonating security and diplomatic organizations and carrying malicious ZIP attachments
Full article:
https://t.co/bh6fvaHowR
🇯🇵#Japan#0Day#CyberAttack - Update
Japanese Space Agency JAXA Discovers Zero-Day Attacks
The Japanese Space Exploration Agency (JAXA) discovered multiple zero-day exploits during an investigation into a 2023 cyberattack on its systems.
The attack primarily targeted JAXA’s Active Directory and began with unauthorized access to its Microsoft 365 (M365) services.
JAXA collaborated with Microsoft to investigate and found no breaches of classified data on rockets or satellites. However, personal information in M365 was accessed.
Read more:
https://t.co/aDBLQV1WIq
#JAXA
🚨 #CyberAttack 🚨
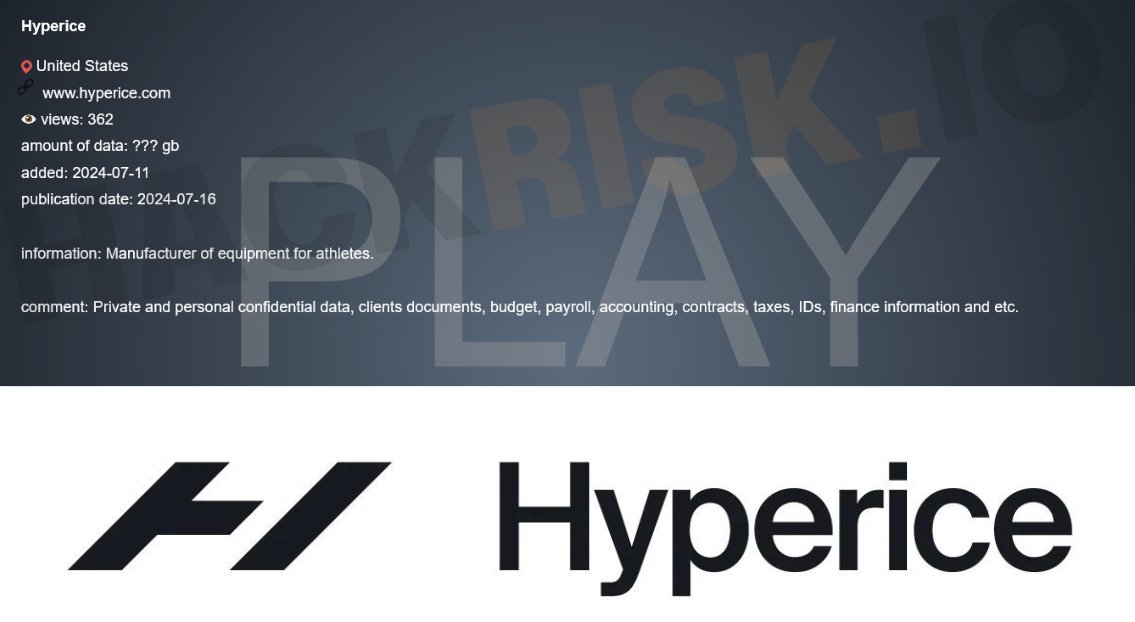
🇺🇸 #USA, Hyperice
Hyperice has been listed as a victim by the Play ransomware group.
The hackers allegedly exfiltrated private and personal confidential data, clients' documents, budget, payroll, accounting, contracts, taxes, IDs, finance information.
Ransom deadline: 16th Jul 24.
#Ransomware
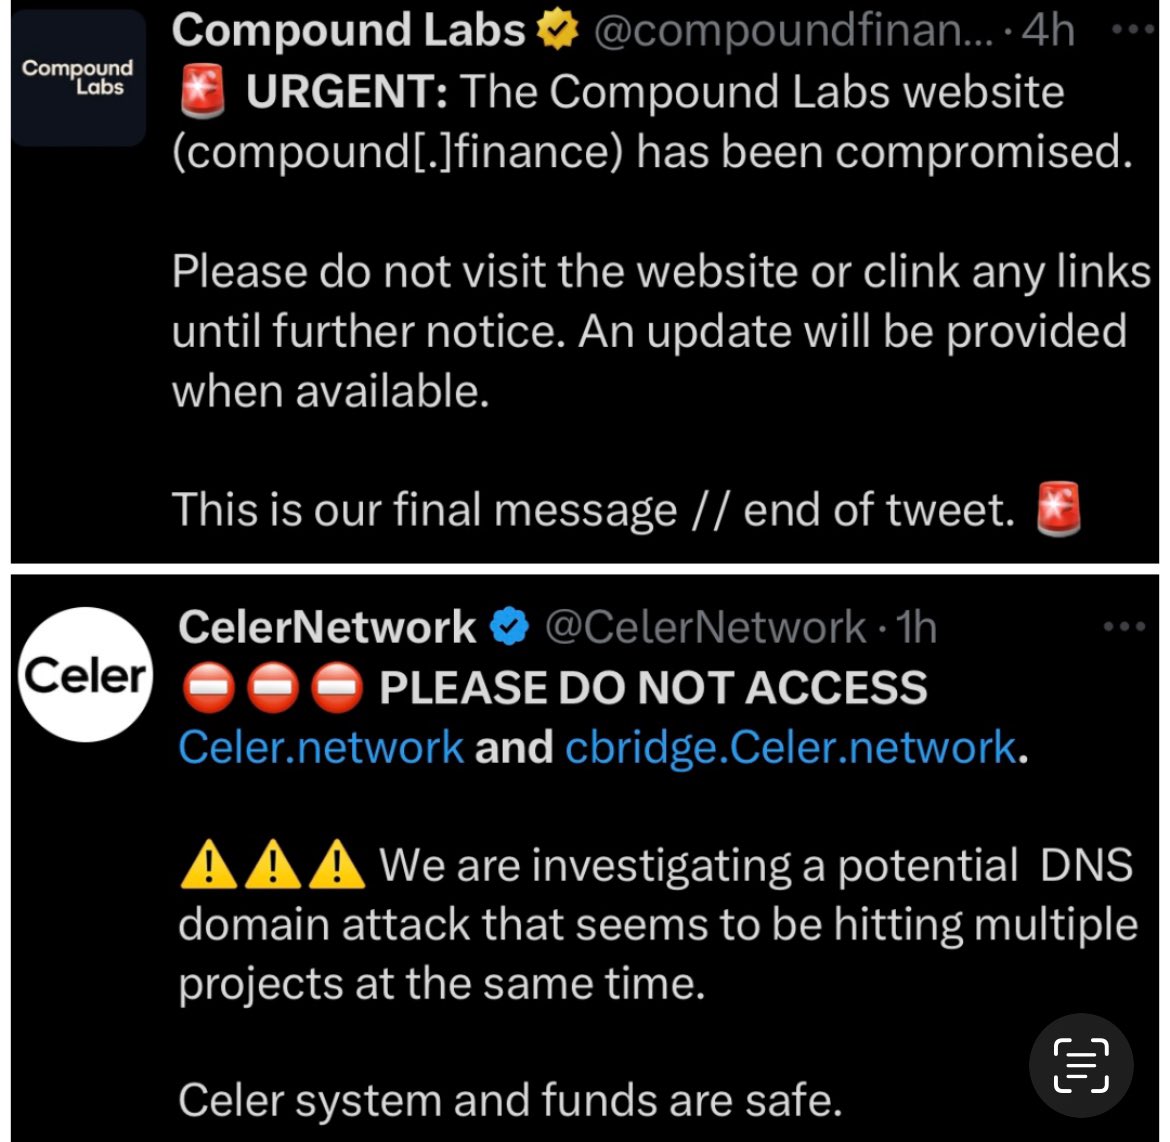
🚨Compound Labs and Celer Network issued warnings within hours of each other, advising users not to access their websites due to reported cyber attacks.
#Crypto
🚨 #DataBreach
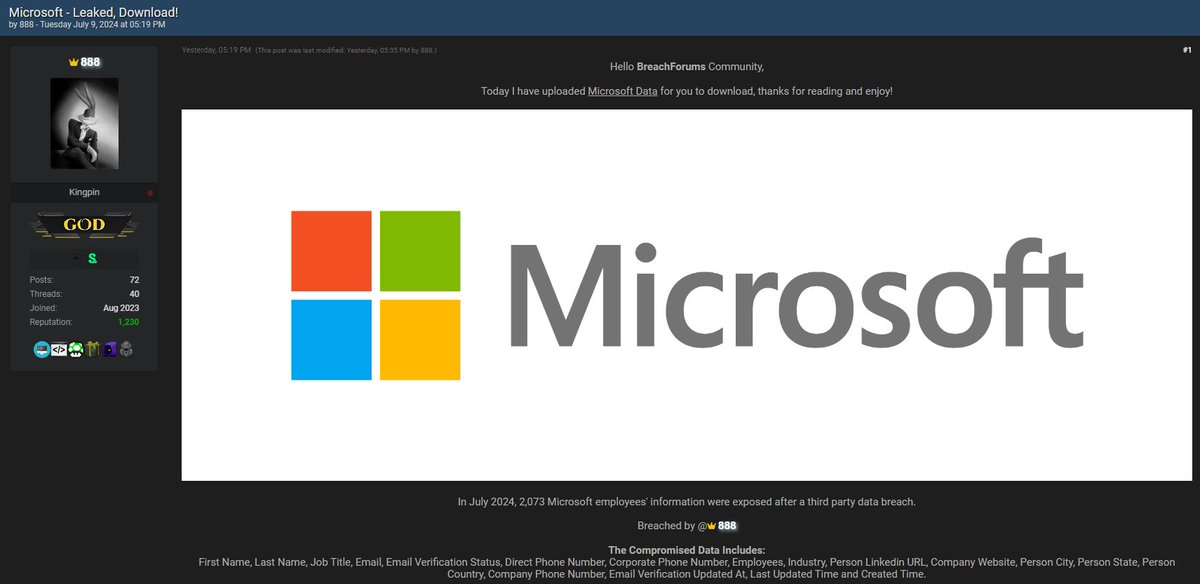
The threat actor 888 enriches its collection of third-party breach claims.
Following the recent Shopify and Nokia incidents, it now allegedly leaks information of 2,073 Microsoft employees.
Among the reportedly stolen data are records such as full names, job titles, email addresses and verification statuses, direct and corporate phone numbers, LinkedIn URLs, company websites, and locations including city, state, and country, as well as company phone numbers.
#CyberAttack #Microsoft
🚨#CyberAttack
🇺🇸#USA, The Heritage Foundation
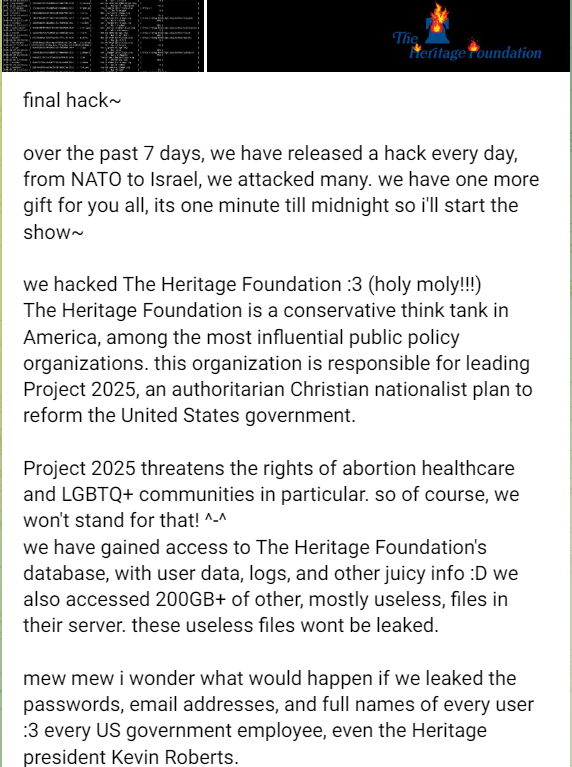
The threat group SiegedSec claims to have hacked The Heritage Foundation, a conservative think tank in America responsible for Project 2025.
They report accessing the foundation's database, including user data, logs, and over 200GB of other files.
Additionally, the hacking group threatens to leak passwords, email addresses, and full names of every user, including US government employees and the Heritage president, Kevin Roberts.
According to Have I Been Pwned, the data contained 72k unique email addresses, primarily used for commenting on articles (along with names, IP addresses, and the comments left) and by content contributors (along with usernames and passwords stored as either MD5 or phpass hashes).
https://t.co/KJYkeZkxDi
#DataBreach #Project2025
🚨 #CyberAttack 🚨
🇧🇷 #Brazil, Usina Alta Mogiana SA
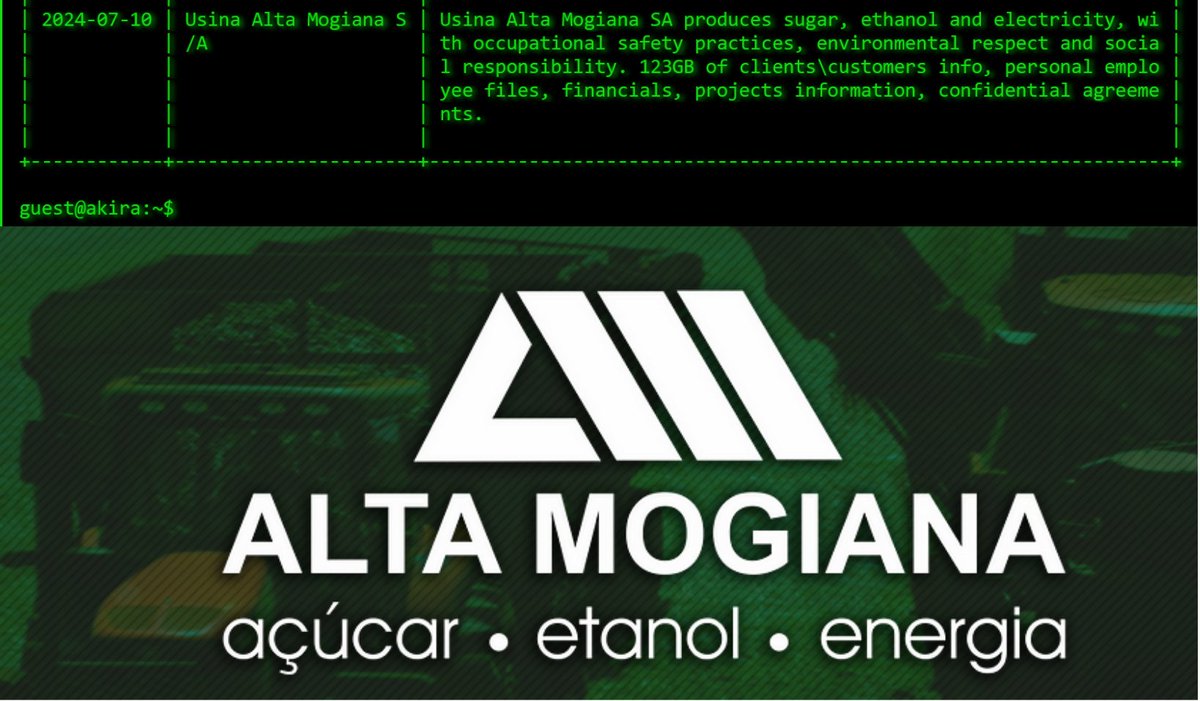
Usina Alta Mogiana SA has been listed as a victim by the Akira ransomware group.
The hackers allegedly exfiltrated 123 GB of data, including clients/customers info, personal employee files, financials, projects information, and confidential agreements.
Usina Alta Mogiana SA produces sugar, ethanol, and electricity
#Ransomware
🚨 #CyberAttack 🚨
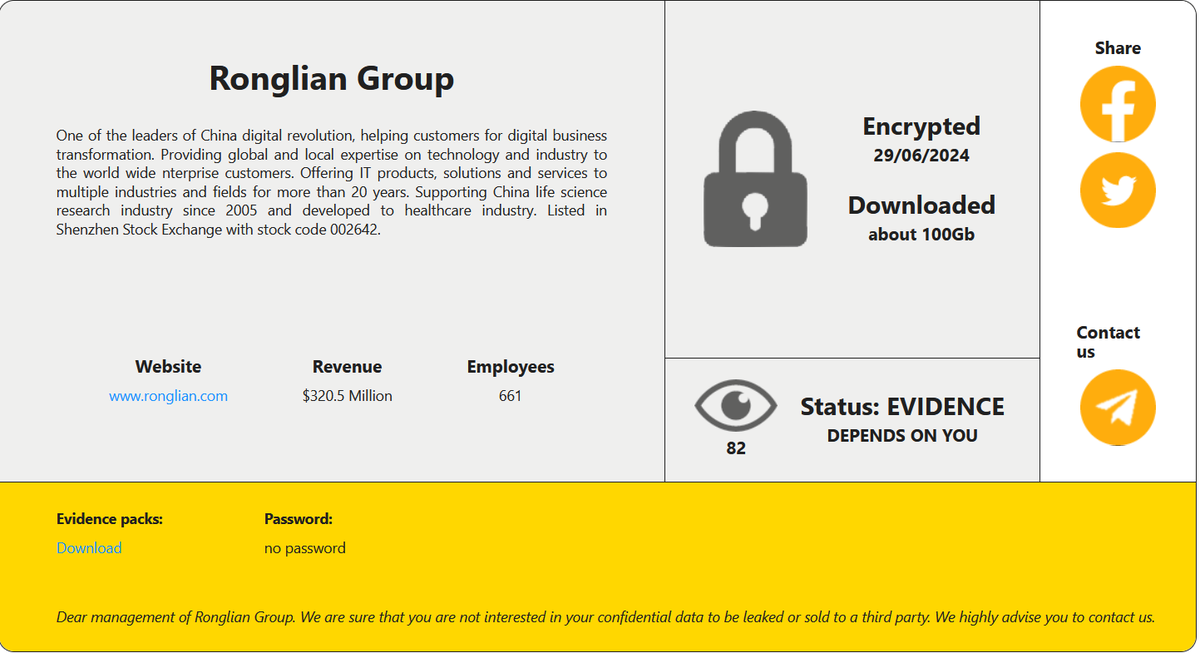
🇨🇳 #China, Ronglian Group 荣联科技大厦
Ronglian Group has been listed as a victim by the RansomHouse ransomware group.
The hackers allegedly exfiltrated 100 GB of data.
#Ransomware
🚨#CyberAttack
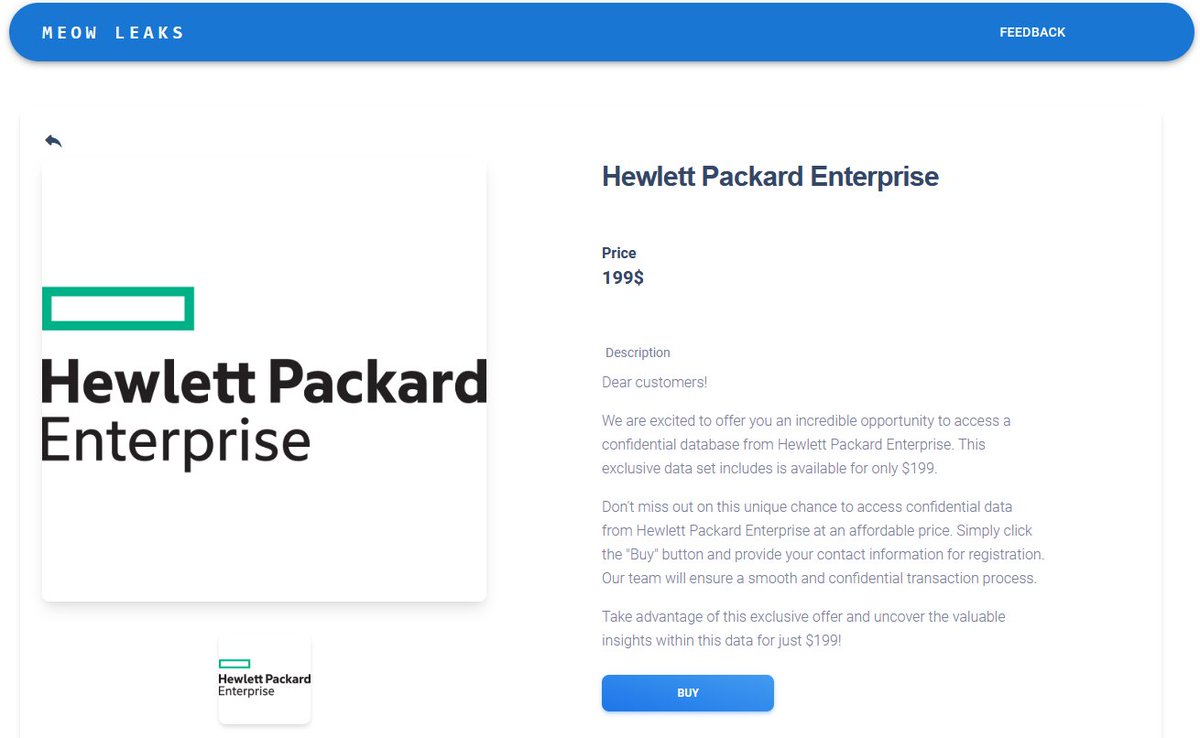
🇺🇸#USA, Hewlett Packard Enterprise
The MEOW hacking group claims to sell a confidential database from Hewlett Packard Enterprise in an "exclusive offer" for $199.
#DataBreach
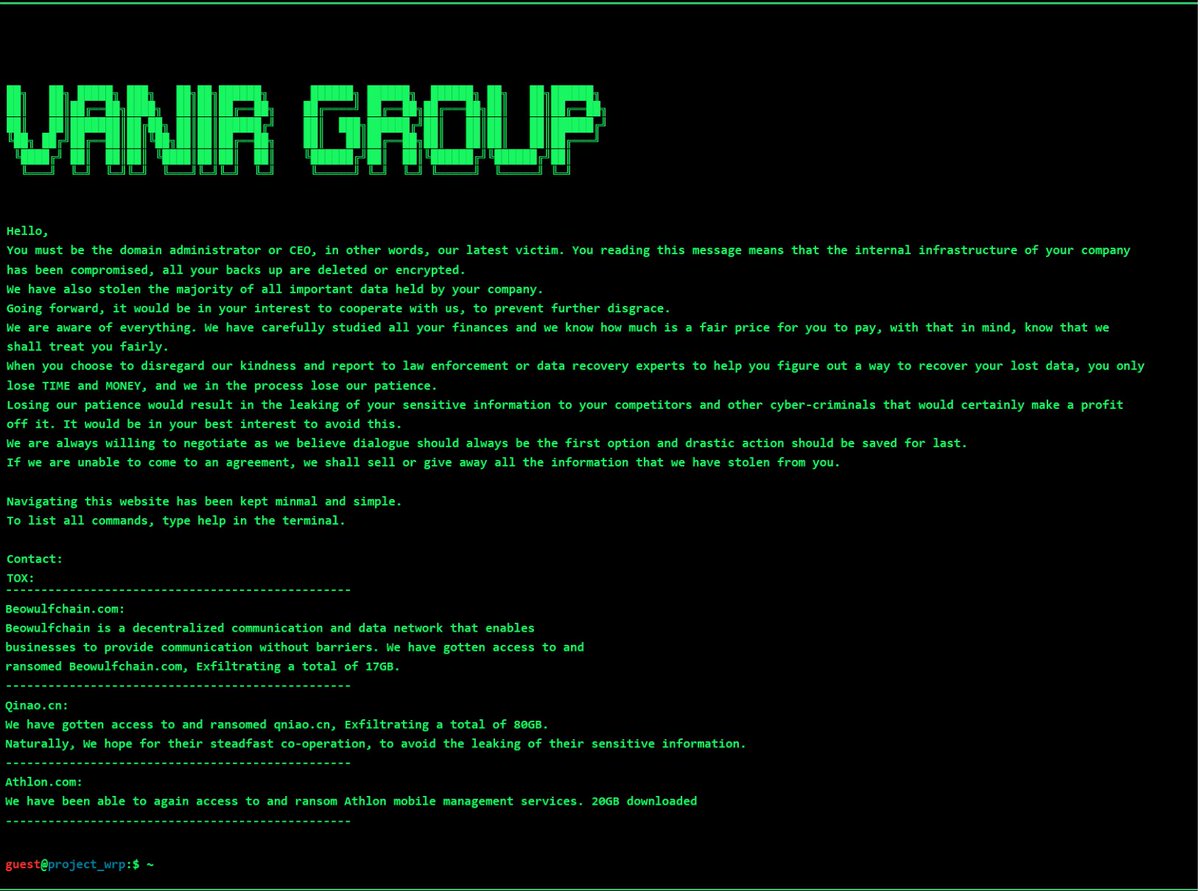
🚨 New #ransomware group: Vanir Group 🚨
Currently, the criminal group's list includes 3 victims:
Beowulfchain[.]com:
"Beowulfchain is a decentralized communication and data network that enables businesses to provide communication without barriers. We have accessed and ransomed Beowulfchain[.]com, exfiltrating a total of 17GB."
Qinao[.]cn:
"We have accessed and ransomed qniao[.]cn, exfiltrating a total of 80GB. Naturally, we hope for their steadfast cooperation to avoid the leaking of their sensitive information."
Athlon[.]com:
"We have been able to again access and ransom Athlon mobile management services. 20GB downloaded."
Thank you, @CyberIL for the intel
#Ransomware
🚨 #CyberAttack 🚨
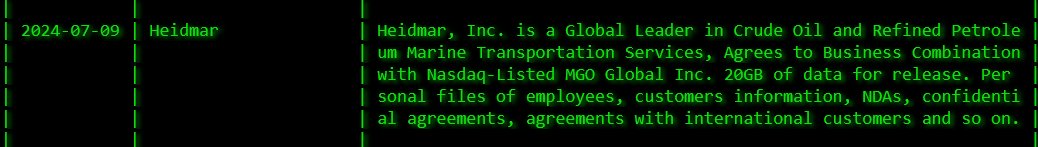
🇬🇷 #Greece, Heidmar Inc.
Heidmar Inc. has been listed as a victim by the Akira ransomware group.
The hackers allegedly exfiltrated 20 GB of personal files of employees, customers' information, NDAs, confidential agreements, agreements with international customers, etc.
#Ransomware