Dias atras @usuariosdigital reportaba una alerta de posible hackeo al @ECU911_ el sistema que se usa en #Ecuador para emergencias de ese pais. Hoy investigando al parecer el hackeo es real y se habla en foros de telegram de venta de informacion extraida. No han emitido ningun comunicado oficial la entidad afectada, esto es muy grave. @Telecom_Ec@EcuCERT_EC@MIT_Ecuador #AlertaDigitalEC
VirusTotal analiza IPv4 públicas para exponer servidores C2 e infraestructura de malware
VirusTotal ha implementado el escaneo diario del espacio IPv4 público para ayudar a los equipos de seguridad a localizar servidores de comando y control
https://t.co/bO5oVFN3y9
No es paranoia, las tecnologías de vigilancia estatal crecen sin control en América Latina https://t.co/M4EYOHTiyU
Sobre el reporte que hicimos con @derechosdigital en el marco del OLAD
Vulnerabilidades críticas en WordPress permiten ataques XSS, SQLi y filtración de datos
WordPress lanzó la versión 7.1.3 el 6 de octubre de 2026 para corregir vulnerabilidades de cross-site scripting (XSS), inyección SQL y divulgación de información, entre otras fallas de seguridad
https://t.co/LBCq7ZUVon
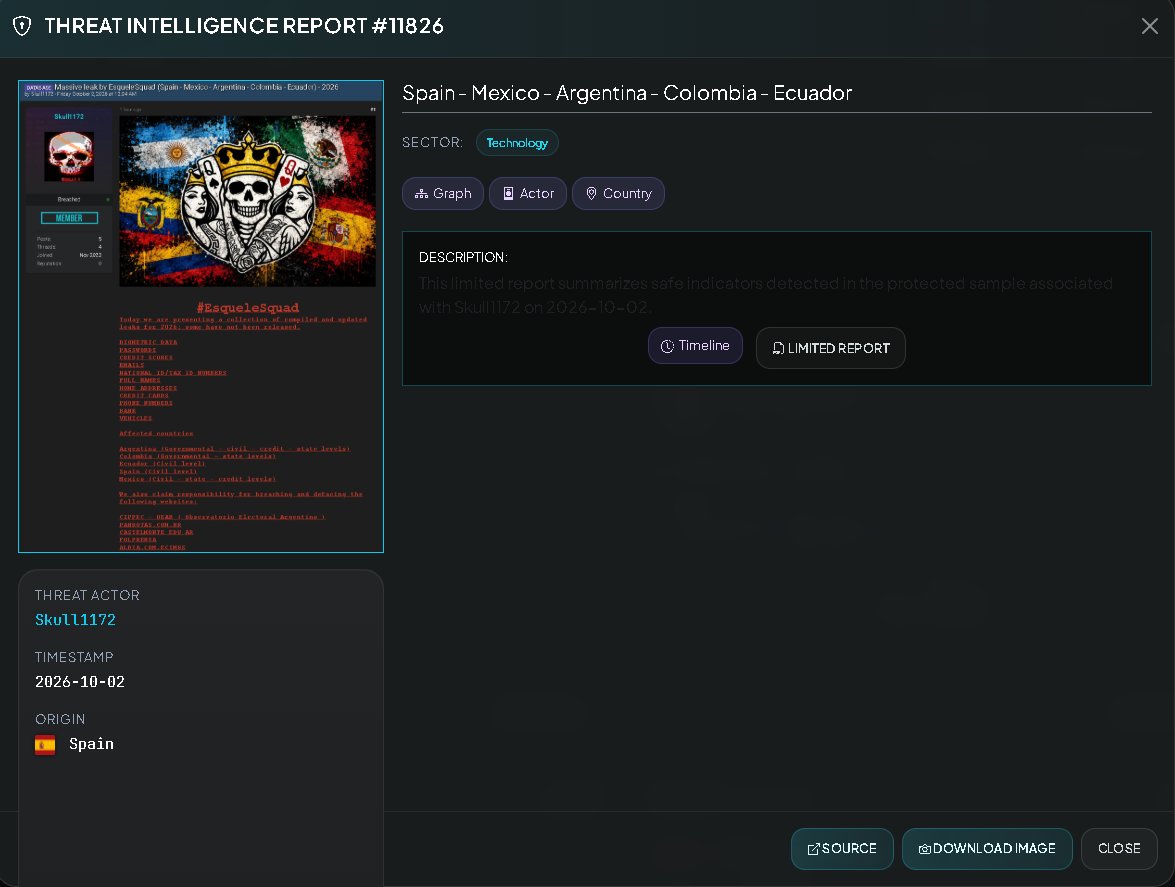
⚠️ CRITICAL PREVENTIVE ALERT 🇦🇷 🇨🇴 🇪🇨 🇪🇸 🇲🇽 🌐: ALLEGED COMPILATION AND MASSIVE LEAK OF 3.4 TERABYTES OF SENSITIVE GLOBAL DATA (ACTOR: ESQUELESQUAD / SKULL1172)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: SKULL1172 / COLLECTIVE: ESQUELESQUAD / DATE: OCTOBER 2, 2026]
The centralized cyber-intelligence system has detected a major post made on underground forums on October 2, 2026, by user Skull1172, representing the EsqueleSquad collective. The report announces the release of a massive, up-to-date compilation of databases leaked during 2026, totaling 3.4 terabytes and over 264 million records across five countries.
It is strictly noted that the veracity of this massive breach and the authenticity of the repositories have not been officially confirmed by the affected government or corporate entities. The definitive status of the leak remains unconfirmed.
Threat Actor / Collective: EsqueleSquad
Reported Total Volume: 3.4 Terabytes / 264,144,000 files and records.
File Formats: JSON, PDF, TXT, SQL, and JPG images.
Affected Countries and Sectors:
Argentina 🇦🇷: Government, civilian, credit, and state sectors.
Colombia 🇨🇴: Government and state sectors.
Ecuador 🇪🇨: Civilian sector.
Spain 🇪🇸: Civilian sector. Mexico 🇲🇽: Civil, state, and credit-related levels.
🔍 TECHNICAL BREAKDOWN OF INFORMATION AND EXPOSED DATA TYPES
According to the description on the underground forum, the massive compilation includes highly sensitive PII (Personally Identifiable Information) records and financial infrastructure data:
Types of Data Included:
Biometric data and passwords.
Credit scores and credit histories.
National ID numbers, identity documents, and tax ID numbers.
Full names, home addresses, and telephone numbers.
Bank records, credit card numbers, and vehicle ownership details.
Corporate and personal email addresses.
Claims of Attacks and Website Defacement:
The group also claims responsibility for intrusions and visual modifications (defacement) of platforms in the region, notably:
CIPPEC - OEAR (Argentine Electoral Observatory).
https://t.co/qvCkO9nwLV (Brazil).
CASTELMONTE EDU AR (Argentina).
FOLPRENSA.
https://t.co/x3lWCdQC1N (Ecuador).
🛡️ TECHNICAL RECOMMENDATIONS FOR PREVENTION AND CONTAINMENT (SOC / CSIRT / GOVERNMENTS)
Regional Incident Response Coordination: Government cybersecurity teams in Argentina, Colombia, Ecuador, Spain, and Mexico must activate emergency protocols to audit exposed state repositories.
Monitoring and Early Warning for Financial Institutions: Restrict access to identity validation platforms and notify banking systems to mitigate the fraudulent use of leaked data.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #EsqueleSquad #DataLeak #GlobalAlert #Argentina #Colombia #Ecuador #Spain #Mexico #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
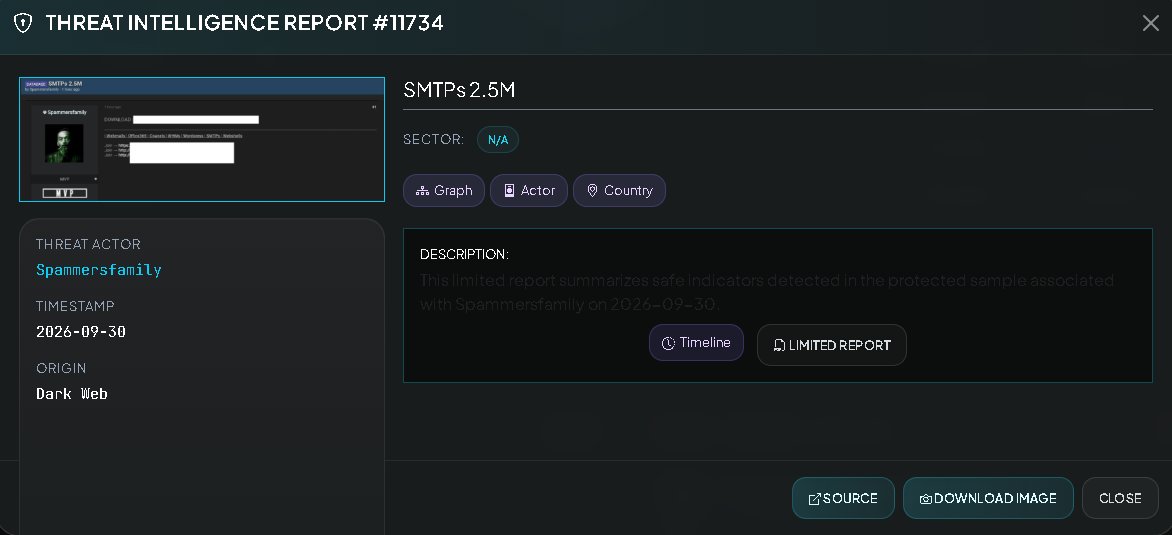
⚠️ GLOBAL PREVENTIVE ALERT 🌐 📨: MASSIVE 🇧🇷 🇮🇹 🇳🇱 🇦🇷 🇩🇪 🇬🇧 🇫🇷 🇺🇸 🇦🇺 🇮🇳 🇨🇴 🇨🇱 🇪🇸 🇪🇨 🇵🇪 DUMP OF 2.5 MILLION COMPROMISED SMTP SERVERS (ACTOR: SPAMMERSFAMILY)
[STATUS: CONFIRMED, EVIDENCE VERIFIED / THREAT ACTOR: SPAMMERSFAMILY / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence system has detected a post on underground forums made on September 29, 2026, by the user Spammersfamily (holding MVP rank). The report announces the public, mass distribution of a compressed file containing 2.5 million compromised SMTP servers, exposing email credentials and highly critical mail-sending gateways on a global scale.
Threat Actor / Group: Spammersfamily.
Activity Type: Mass dump and distribution of SMTP access credentials (mail server databases for mass-mailing campaigns).
Sector: 📨 Email Infrastructure, Telecommunications, and Offensive Cybersecurity.
Geographic Scope: Global, with a significant presence in commercial and government domains across Latin America and Europe.
📊 TECHNICAL STATISTICS AND DATASET METRICS
Automated analysis of the source file (2M SMTPs_20262909134018.txt) yields the following key metrics regarding the exfiltrated volume:
Total Lines Read: 2,487,083 records.
Valid Records: 2,487,026 processed entries.
Invalid Lines: 57 discarded records.
Count by Key Category
Government and Military Domains (.gov / .gob / .mil): 5,520 servers. Latin American Domains: 162,735 servers.
2. Top 10 Most Mentioned TLDs (Extensions)
.com: 1,867,379 records.
.br 🇧🇷 (Brazil): 123,218 records.
.it 🇮🇹 (Italy): 100,895 records.
.net: 42,641 records.
.nl 🇳🇱 (Netherlands): 25,845 records.
.ar 🇦🇷 (Argentina): 15,494 records.
.de 🇩🇪 (Germany): 13,178 records.
.uk 🇬🇧 (United Kingdom): 13,076 records.
.org: 12,769 records.
.fr 🇫🇷 (France): 11,533 records.
3. Breakdown of Detected Government and Military Domains
The dataset includes access to critical state infrastructure across multiple countries, notably:
.gov.br 🇧🇷 (Brazil): 3,044 records.
.gov 🇺🇸 (General US/International): 514 records.
.gob.ar 🇦🇷 (Argentina): 341 records.
.gob.mx 🇲🇽 (Mexico): 299 records.
.gov.uk 🇬🇧 (United Kingdom): 299 records.
.gob.pe 🇵🇪 (Peru): 228 records.
.gov.co 🇨🇴 (Colombia): 187 records.
.gob.ec 🇪🇨 (Ecuador): 160 records.
.mil (Global military): 140 records. Additionally, access has been recorded from domains in Australia 🇦🇺 (.gov.au), India 🇮🇳 (.gov.in), Brazil 🇧🇷 (.mil.br), Colombia 🇨🇴 (.mil.co), Chile 🇨🇱 (.gob.cl), Argentina 🇦🇷 (.mil.ar), and Spain 🇪🇸 (.gob.es).
🛡️ TECHNICAL RECOMMENDATIONS FOR PREVENTION AND CONTAINMENT (SOC / CSIRT / EMAIL ADMINISTRATORS)
Immediate SMTP Credential Rotation: Organizations with domains appearing in the samples must revoke passwords, rotate application keys, and disable exposed service accounts.
Implementation of SPF, DKIM, and DMARC Policies: Strengthen email authentication records to prevent the impersonation of institutional domains by third parties using these leaked lists.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #SMTPDump #Spammersfamily #DataLeak #GlobalAlert #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
#AlertaDigitalEC
Se reporta filtración de datos del personal de @presidencia_ec, ministerios, secretarías y agencias como @SRIoficialEc y contendría nombre e información institucional como teléfonos, email, cargos, direcciones, datos de viajes y viáticos, vía @DarkWebInformer
AWS: datos en la nube irrecuperables por daños de guerra
Amazon Web Services (AWS) ha confirmado que parte de los datos de sus clientes alojados en centros de datos de Oriente Medio son irrecuperables de forma permanente
https://t.co/1pbKMKQHOA
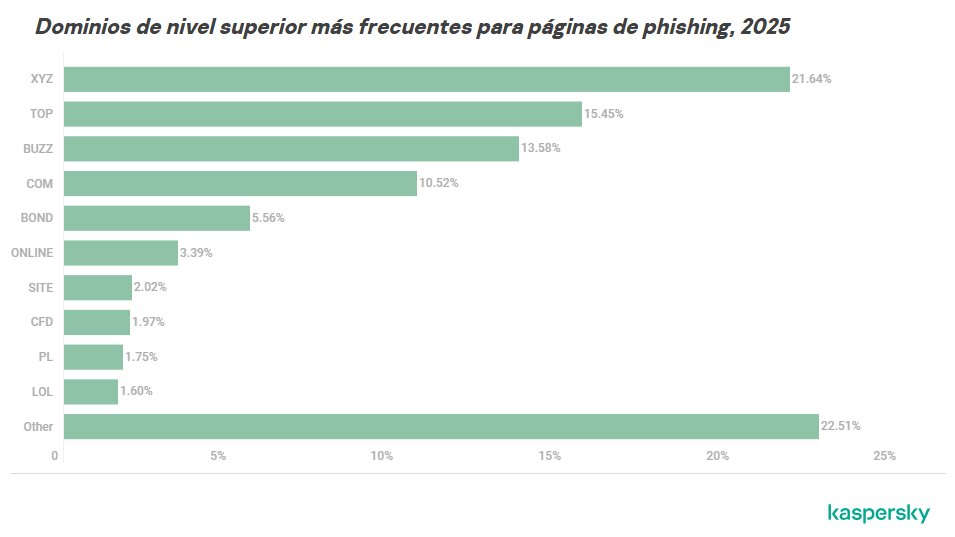
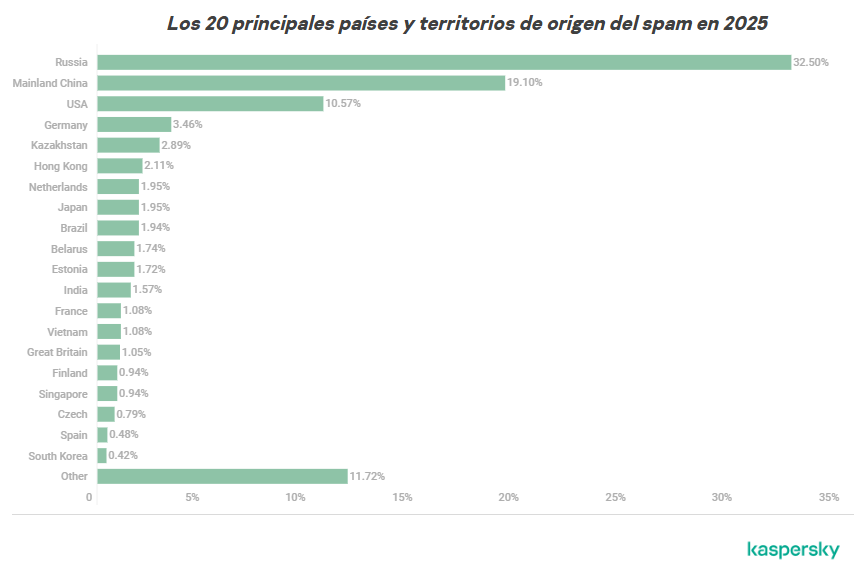
#AlertaDigitalEC#Ecuador 7mo en el top10 global de población* afectada por phishing, según Spam and Phishing Report 2025 de @KasperskyLatino
Los dominios XYZ son los más utilizados para el phishing y el 50% de ataques vienen de Rusia y China
*usuaria de productos Kasperski
Vulnerabilidad en Cliente de Escritorio Remoto de Windows permite ejecución de código remoto
Microsoft ha lanzado actualizaciones de seguridad para corregir la vulnerabilidad CVE-2026-69485 , calificada como importante
https://t.co/X1Hk2PdxxK
⚠️ Remote Desktop Services Failures on Windows Servers Following September Update
Source: https://t.co/8jAEO7bL2U
Windows administrators worldwide are grappling with a disruptive Remote Desktop Services (RDS) bug that surfaced immediately after Microsoft shipped its September 2026 Patch Tuesday cumulative updates. Session hosts running Windows Server 2019, 2022, and 2025 have begun freezing hours after boot, leaving RDP connections stuck at “Connecting…” and preventing logged-in users from disconnecting or logging off cleanly.
The issue traces back to three specific cumulative updates: KB5122876 for Windows Server 2019, KB5122882 for Windows Server 2022, and KB5122871 for Windows Server 2025, all released as part of this month's security rollout.
#cybersecuritynews
Windows told on him: alleged Scattered Spider member Peter Stokes was tied to the May 2025 jewelry retailer breach through a Microsoft Global Device ID, a persistent identifier baked into every Windows install.
Microsoft records showed the device hitting the ngrok signup page at the exact minute the attack account was created, then surfacing on home IPs in Tallinn, New York, and Thailand.
He used a VPN during the intrusion. The device ID followed him anyway.