Fhenix mainnet is live.
What started as an idea to bring FHE-powered confidentiality to blockchains is now production-ready infrastructure, for you to build with.
CoFHE is now live on @arbitrum and @ethereum, bringing confidentiality to onchain assets without compromising composability.
HackenProof is heading to @EFDevcon 8 in Mumbai 🇮🇳
Our CEO @DmytroMatviiv will speak on:
“Stop Re-Investigating the Same Wallet: A Shared Evidence Layer for On-Chain Crime”
📅 Nov 3–6
📍 Mumbai
Looking forward to Devcon in Mumbai!
#Devcon8#Cybersecurity#HackenProof
Tough day for everyone running PHP-powered services.
PoCs are already available on GitHub. If possible, I’d strongly recommend disabling PHP-powered services exposed to the internet until a fix is released. Once the patch is available, apply it ASAP.
Patch expected at 14:00 UTC (16:00 CEST).
We already see exploitations on some production services.
Stay safe.
What should we prioritize funding in the ETHSecurity Initiatives Round?
Join us this Thursday for an X Space with ETHSecurity Badge holders as we go through the initiatives and hear what they think Ethereum security needs most right now.
↓
https://t.co/zR9Fck8wEx
🔍 A new Curated Smart Contract Audit is underway on HackenProof!
DarkSwap is a privacy-focused platform built on NEAR Intents, enabling private cross-chain swaps.
Glad to have @DarkSwapApp on board! 🤝
🎙️ HackenProof is joining Cregis MicUp Vol. 21!
Our CEO @DmytroMatviiv will join @maxrobot5 from @range_org and Bobby T. from @GoPlusSecurity for a discussion on digital asset security, incident response, and AI-related risks.
Hosted by @0xCregis.
🗓️ October 21 | 5 PM GMT+8
Set your reminder 👇
https://t.co/rbiSF6U8vd
🎙️ Cregis MicUp Vol. 21: Digital Asset Security in Practice
🗓️ October 21, 2026 | 5:00 PM GMT+8 | Live X Space
🔗 Set your reminder: https://t.co/FzERVbHIw2
Who can authorize a transfer? How is the recipient checked? What happens if a trusted tool or provider is compromised? For businesses managing digital assets, security depends on decisions made throughout the operation, often well before a transaction reaches the blockchain.
As businesses connect more systems and introduce AI into their workflows, those decisions deserve closer attention. Teams need to understand where funds could be exposed, which controls can limit the damage and how to respond when something goes wrong.
Join Cregis and speakers from Range, HackenProof and GoPlus Security to examine digital asset security through the practical choices businesses face in prevention, incident response and everyday operations.
🎤 Meet Our Panel:
Dmytro Matviiv (@DmytroMatviiv ) , CEO at @HackenProof
Max Grabner(@maxrobot5), Head of Product at @range_org
Bobby T., Head of AI Marketing at @GoPlusSecurity
🎙️ Moderated by Bojun Li, Deputy Marketing Director at Cregis
📋 What We’ll Explore:
🔸 Hidden Exposure
Where businesses may overlook serious risks, and what security incidents reveal about the assumptions they rely on.
🔸 Security by Design
How to structure permissions, transaction checks and operational controls around the risks a business actually faces.
🔸 Response and Recovery
What to prioritize when an incident occurs, from containing the threat and preserving evidence to meeting legal obligations and communicating with customers.
🔸 AI and Operational Security
How AI can introduce new risks through the information it uses, the actions it influences and the systems it can access.
A business may have security tools in place and still be unprepared for a failure between teams, systems or providers. This session will explore how to spot those gaps and make security responsibilities clearer before an incident puts them to the test.
📌 Join us on October 21 and bring your questions.
#DigitalAssets #CyberSecurity #WalletSecurity #AISecurity
We have a winner 🎉
Congrats to @webrainsec! You’ve won a ticket to Web Summit 2026 in Lisbon.
Thanks to everyone who took part. See you at Web Summit 2026 🙌
✅ Good news from @BloFin_Official!
BloFin has increased the rewards for its Bug Bounty Program on HackenProof.
💰 Critical vulnerabilities can now earn up to $10,000.
Ready for the hunt? ↓
https://t.co/YkoDk6tsRL
Crowdsourced security is changing – and we’re taking the conversation to @summit_defi 2026 🇮🇳
Our CEO @DmytroMatviiv will speak on:
“Why Crowdsourced Security Is Dying (Code4rena, Hats Finance, and What Comes Next)”
📅 Nov 1–2
📍 Mumbai
See you at DSS 2026!
#DSS2026 #Cybersecurity #HackenProof
🚨 Big security news for @CetusProtocol! 🐳
Cetus is raising the bar for DeFi security with an expanded Bug Bounty Program in partnership with @HackenProof.
🔒 Critical vulnerabilities: $30,000–$1,000,000
⚡ High: $3,000–$30,000
🛡️ Medium: $100–$1,000
🔍 Low: $10–$100
Up to **$1 MILLION** for critical vulnerabilities! 🤯
A strong commitment to security, transparency, and protecting users across the Cetus ecosystem.
More rewards for white hats. Stronger security for everyone. 💪
Always great to see @CetusProtocol investing in the long-term health of DeFi! 💙🐳
🔒 Good news from @CetusProtocol!
Cetus has significantly increased its maximum Critical bounty on HackenProof!
You will be rewarded based on these tiers:
▪︎ Critical: $30,000 – $1,000,000
▪︎ High: $3,000 – $30,000
▪︎ Medium: $100 – $1,000
▪︎ Low: $10 – $100
Start #bugbounty hunting 👇
https://t.co/HhlRozR5lL
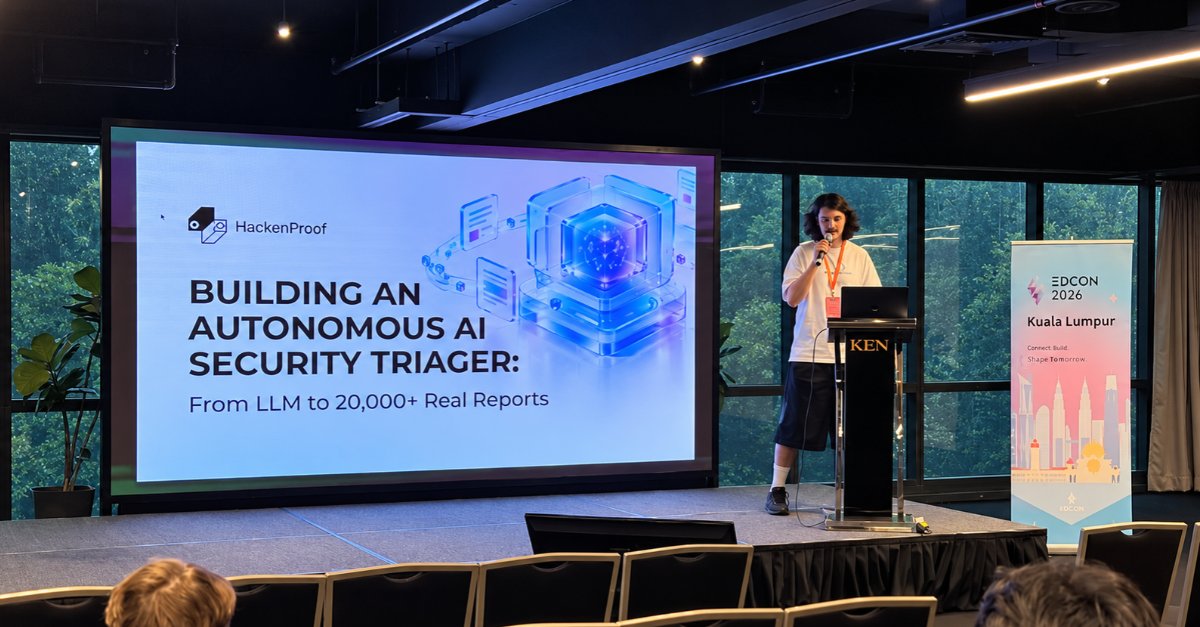
A look back at EDCON 2026 🇲🇾
Our CTO @d0rsky took the stage with:
“Building an Autonomous AI Security Triager: From LLM to 20,000+ Real Reports”
From generic LLMs to real-world vulnerability triage at scale.
Thanks @EDCON_Official for having us!
#EDCON2026#AI#Cybersecurity #HackenProof