Errol Weiss, chief security officer at Health-ISAC, said healthcare organizations shouldn't allow uncertainty over legislation and regulations to delay security improvements. https://t.co/gfq8YGCYiY
"A change in congressional leadership could shift priorities, but health sector organizations cannot afford to wait for new regulations or federal guidance before taking action," Weiss said. "The threats are here now, and the landscape is becoming more challenging and complex, especially as AI gives attackers new capabilities."
#RuralHealth #HealthIT #healthcaresecurity #HealthTech #CISO
Most security leaders are evaluating AI models in a vacuum. Project Glasswing proved that’s the wrong risk boundary. At the CISO Summit, Vellox Labs shared ground-truth findings on how frontier models actually behave when given autonomy, tools, and a live network.
Check out the full slide deck from @BoozAllen, a Health-ISAC Community Services Champion, for the complete findings and architectural recommendations. https://t.co/TTMpFmnb5v
#Cybersecurity #ArtificialIntelligence #FrontierAI #AppSec
Score It, Prove It, Clear It: Medical Device Security in the Enforcement Era webinar by @Medcrypt on Monday, November 16th at 2 PM ET.
Cybersecurity has gone from a footnote to nearly half of FDA’s deficiencies. Yet many teams are still debating how to score vulnerabilities instead of proving they’ve controlled them. Join Medcrypt’s Seth Carmody and Axel Wirth for a look at the current enforcement landscape. They’ll cover where CVSS helps and where it leaves you exposed, and what separated cleared submissions from refused ones in recent anonymized 510(k) reviews.
Register Here: https://t.co/oXoy4DLPiq
Health-ISAC Chief Security Officer, Errol Weiss ...was also clear about the limits of a takedown. "Cybercrime syndicates operate like businesses: when one service gets disrupted, the operators will often try to move to other servers or alternate phishing frameworks.”
https://t.co/L9rw1QZR6m
#cybercrime #Hospital #healthcaresecurity #HealthIT #CISO
This week, Health-ISAC®'s Hacking Healthcare® continues our series examining cybersecurity developments in the Asia Pacific (APAC) region. Join us as we look at a new cybersecurity framework from Australia that has legal and regulatory impact across the Australian economy, despite being non-binding guidance. https://t.co/q2BF5PXBrg
TODAY AT 1 PM ET!
Cyber Crisis Plans That Fail When It Matters Most webinar by Semperis
Register Here: https://t.co/qZdJPU14Qe
The gap often comes down to identity infrastructure, the foundational layer that governs access to every critical system. When that layer is overlooked in crisis planning, restoration stalls. Care delivery suffers. And organizations that thought they were prepared find out otherwise.
This webinar draws on global research and direct incident response experience to examine where healthcare cyber plans break down and what it takes to build genuine operational resilience.
TODAY AT 3 PM ET!
Healthcare Security at Machine Speed: $17M Ransomware & AI Adversaries webinar with Bishop Fox
Register Here: https://t.co/klVmJEs61z
AI is changing how healthcare operates and how adversaries attack it. With average healthcare ransomware demands approaching $17 million, can healthcare security teams detect and respond to attacks as quickly as AI-enabled adversaries can carry them out?
This session connects healthcare security strategy to these operational decisions: how to evaluate response assumptions, assign ownership across departments, and prioritize investments that support continuity of care.
Enjoy some photos from last week's Security Workshop and Exercise in Louisville, Kentucky, U.S. Many thanks to #Humana for hosting the event and to the sponsors who made it possible for attendees to participate free of charge: #360Privacy and @AcalvioTech.
Get ready for an announcement soon listing the 2027 workshop locations!
Hear Health-ISAC President and CEO Denise Anderson address the State of U.S. Cyber Infrastructure at next week's Billington Critical Infrastructure Cybersecurity Summit.
https://t.co/Cj2lmn5HwC
#criticalinfrastructure#informationsharing#CISO
The attack follows a wave of hacks against refrigeration systems at supermarkets across Europe. Authorities are investigating a cyberattack targeting a refrigeration-equipment supplier for the French Blood Establishment (EFS), which oversees France’s civilian blood supply.
In the U.S., the Health Information Sharing and Analysis Center sent an advisory to members warning of the potential risk of attack, said Errol Weiss, the group’s chief security officer.
https://t.co/0BmNMi71US
#BloodSupply #Cyberattack #HealthIT
Health-ISAC’s 2026 Third Quarter (Q3) Health Sector Heartbeat provides observations of ransomware, cybercrime trends, and malicious actor forum postings that could potentially impact health sector organizations. Read the report. https://t.co/NGSOlJFdlA
Health-ISAC observed an increase in cybersecurity incidents and data breaches affecting health sector organizations over the past year. Ransomware events have exhibited a consistent upward trend, with Q3 2026 reaching a record high of 317 events impacting the global health sector.
Health-ISAC identified 3,260 total events across all critical infrastructure sectors in Q3 2026, with the health sector accounting for 9.72% of all attacks—a significant increase from the historical average of 7.5%.
#criticalinfrastructure #healthcaresecurity #healthsystems #ruralhealth #biotechnology #healthcaretechnolog #incidentresponse
Healthcare Security at Machine Speed: $17M Ransomware & AI Adversaries webinar with @bishopfox on Tuesday, November 10th at 3 PM ET!
AI is changing how healthcare operates and how adversaries attack it. With average healthcare #ransomware demands approaching $17 million, can healthcare security teams detect and respond to attacks as quickly as AI-enabled adversaries can carry them out?
Join us for a virtual session on how #AI is changing healthcare security and what it takes to protect patient care and operations, featuring:
🔹 Farzan Karimi, Deputy CISO, Executive Director at Moderna
🔹 Matthew B. Welling, Partner at Holland & Knight
🔹 Zach Moreno, AVP Consulting at Bishop Fox
This session connects #healthcare security strategy to these operational decisions: how to evaluate response assumptions, assign ownership across departments, and prioritize investments that support continuity of care.
Register Here: https://t.co/klVmJEs61z
In the relatively short time span since rapid AI adoption took off, Phil Englert, VP of medical device security at Health-ISAC, says he has already observed changes that will affect how much sensitive data floods systems. As AI becomes increasingly integrated, when a cyber incident occurs, organizations frequently lose patient identifiers, medical records, insurance details, and other clinical or financial data — all considered PHI.
Read more https://t.co/J0aPjFLH8P
#HealthIT #HealthcareSecurity #DarkReading
Join Simon Cowley at the Information, Telecommunications and Electronics Engineering Symposium for an essential session: "Health sector threat environment and securing medical devices/operational technology."
📅 Date: November 19
⏰ Time: 9:00 AM
📍 Event: Information, Telecommunications and Electronics Engineering Symposium
Register now https://t.co/mzL1st2eYm
#CyberSecurity #HealthcareIT #OTSecurity #MedicalDevices #PatientSafety #ITEESymposium #CriticalInfrastructure
Join us on Wednesday, November 11th for the Health-ISAC Security Forum and Tabletop Exercise in São Paulo, Brazil!
⏰ Time: 10:00 AM – 4:00 PM BRT (Registration opens at 9:30 AM)
Whether you are looking to benchmark your organization's incident readiness or connect directly with regional healthcare security peers, this forum offers practical takeaways to fortify our collective defenses.
👉 Reserve your spot today- https://t.co/45vNhmraCb
#HealthcareSecurity #InformationSecurity #IncidentResponse
Health-ISAC Summits offer real postmortems, TLP-governed threat exchanges, and proven defense playbooks from peers who manage the same clinical and regulatory realities every day.
🔸 Actionable intelligence on active sector-targeted threats
🔸 Cyber-physical incident response and downtime planning
🔸 Collaborative working groups focused on medical device & health tech security
⏳ Early Bird Pricing for the Fall Americas Summit Extended to Sunday! Don't miss the preferred rate—register your security team before the new cut-off.
🔗 https://t.co/QTfHGPglt8
#HealthIT #HealthISAC #IncidentResponse #HealthcareResilience
TODAY AT 12 PM ET! Why Incident Response Plans Fail Under Pressure webinar with Reflex Security.
Join this thought-provoking session to explore why even mature security programs struggle during real incidents and what it takes to build a response capability that performs under pressure. #reflexsecurity #howareyourreflexes #incidentreadiness
Register Here: https://t.co/c8D1XLFt7j
Call for Papers for the 2027 Spring Americas Summit in Miami is OPEN! 🌴
This year’s theme, "Rooted in Resilience," celebrates the strength, adaptability, and innovative spirit driving our community forward.
For Health-ISAC members: Your voices are essential! Share your expertise, real-world case studies, and visionary ideas by submitting an abstract to help shape this year's program.
For Health-ISAC industry partners: Maximize your visibility by joining us as an official sponsor. Our updated Sponsor Prospectus is now available, featuring high-impact opportunities to connect your organization directly with leading decision-makers and practitioners.
Member and Member-Eligible Submission link: https://t.co/lm4paLwRAn
Sponsor Submission link: https://t.co/6qM1mFtZkS
Explore sponsorships in the Sponsor Prospectus:
https://t.co/HNvIFjGED9
#HealthcareSecurity #HealthISAC #HealthIT #IncidentResponse #CISO
Score It, Prove It, Clear It: Medical Device Security in the Enforcement Era webinar by @MedCrypt on Monday, November 16th at 2 PM ET.
Cybersecurity has gone from a footnote to nearly half of FDA’s deficiencies. Yet many teams are still debating how to score vulnerabilities instead of proving they’ve controlled them.
Join Medcrypt’s Seth Carmody and Axel Wirth for a look at the current enforcement landscape. They’ll cover where CVSS helps and where it leaves you exposed, and what separated cleared submissions from refused ones in recent anonymized 510(k) reviews.
Register Here: https://t.co/oXoy4DLPiq
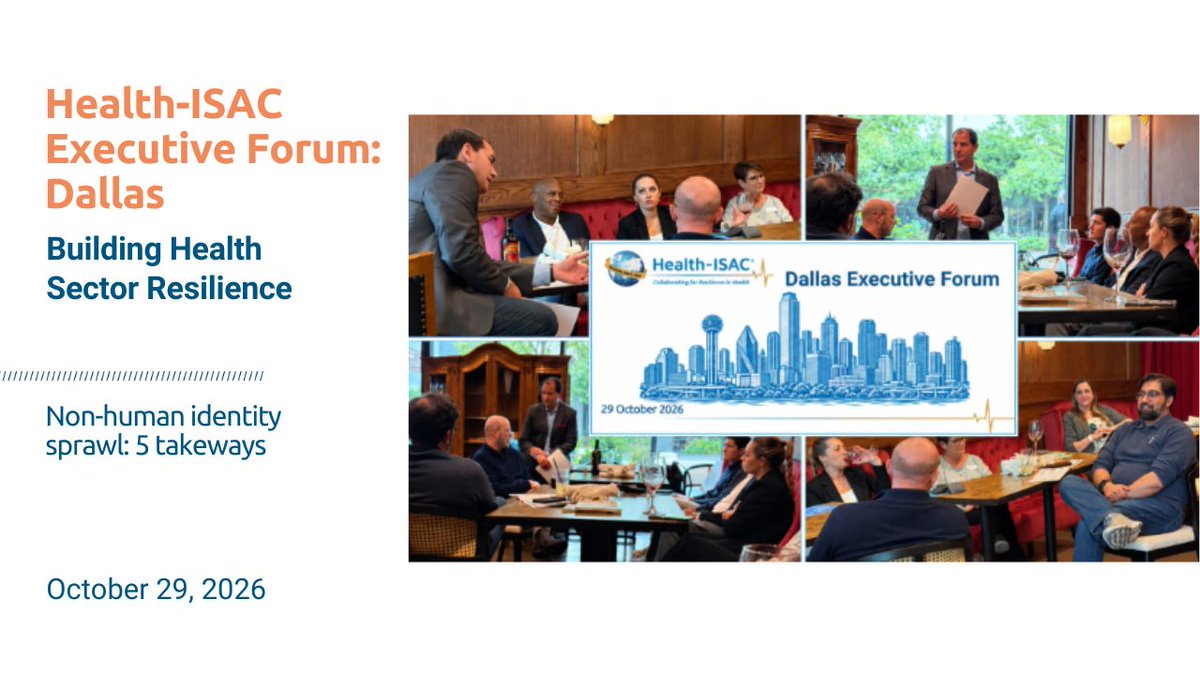
At our recent Health-ISAC Dallas Executive Forum, healthcare cybersecurity leaders gathered to tackle the realities of AI, automation, and identity. The consensus in the room was clear: AI isn’t creating entirely new problems—it is shining an unforgiving spotlight on long-standing gaps in identity hygiene, vendor oversight, and data governance.
Key strategies highlighted by our community in Dallas include:
🔹 Enforce Dual Ownership & Mandatory "Die Dates"
🔹 Prioritize Patient Safety Over Blind Automation
🔹 Back Governance with Binding Contracts:
🔹 Shift from the "Department of No" to Safe Enablement
https://t.co/wAwO0xoBYD
How is your organization managing non-human identity lifecycles and agent governance? Share your approach below. 👇
#HealthISAC #HealthcareSecurity #Cybersecurity #ArtificialIntelligence #IdentityGovernance #HealthTech #CISO