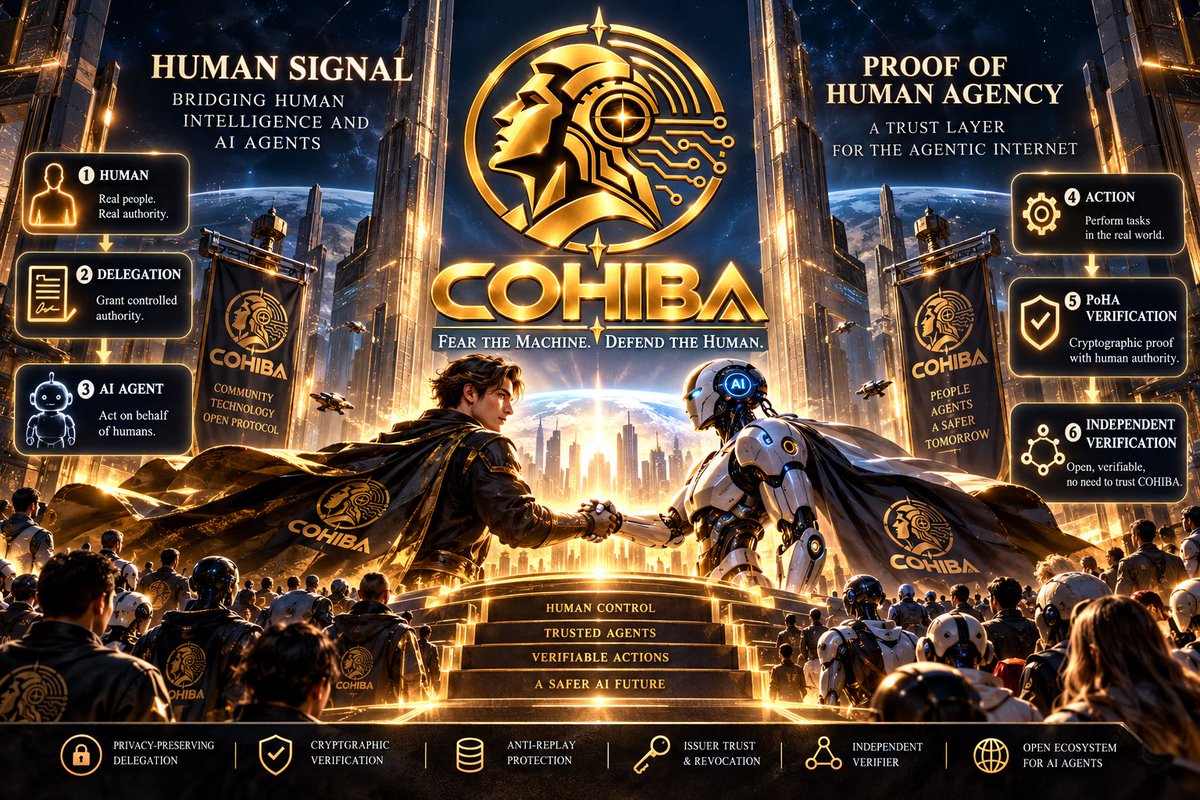
🚀 COHIBA — FROM MEME TO HUMAN SIGNAL
COHIBA may have started with the energy of a meme.
But what we are exploring today goes far beyond the meme.
As AI evolves from simple assistants into autonomous agents capable of communicating, transacting and acting across the internet, we believe a new question is becoming increasingly important:
Who is actually behind an action?
A human?
An autonomous AI agent?
Or an AI agent acting under legitimate authority granted by a human?
This question led us to Human Signal — and to the development of our core protocol thesis:
PoHA — Proof of Human Agency
Instead of only asking whether someone is human, PoHA explores whether a digital action can carry verifiable human authority.
The architecture we are building follows a simple idea:
Human → Delegation → AI Agent → Action → PoHA → Independent Verification
An AI agent may be powerful and autonomous, but its authority should still be cryptographically traceable to the human who authorized it — including the scope of that authority, its expiration and whether it has been revoked.
Human Signal has now progressed beyond the conceptual stage.
Our development work has explored and implemented key components including cryptographic delegation, signed actions, independent verification, issuer trust, credential revocation, anti-replay protection and privacy-preserving mechanisms.
But building code is only the beginning.
Our next objective is much harder:
Prove that the system works without requiring the world to simply trust COHIBA.
That means pursuing three critical milestones:
🔹 Independent security audit
🔹 A real operational Human credential issuer
🔹 External services independently verifying PoHA using their own trust anchors and policies
We are not claiming the problem has been solved.
We are building, testing and attempting to prove that it can be solved.
Because the future of AI may not only depend on how intelligent machines become.
It may also depend on whether humanity can preserve verifiable authority over the machines acting on its behalf.
COHIBA is the community.
Human Signal is the infrastructure.
PoHA is the protocol thesis.
The meme gets attention.
The technology must earn trust.
And as intelligence becomes increasingly autonomous, human agency must remain verifiable.
#COHIBA #HumanSignal #PoHA #ProofOfHumanAgency #AIAgents #AgenticAI #Web3 #DigitalIdentity #AIInfrastructure
@PiCoreTeam@Kosasihg88G Wake up and stop this pathetic act. Go back and help your wife sell her homemade cosmetic creams. The PCT team has the important work covered already. :))) Duc Nguyen
@Kosasihg88G
@PiCoreTeam@Kosasihg88G And he even had the audacity to spread rumors that Nikolas had been in an accident and handed over all the remaining project work to him?? 😂 The writing style gives it away immediately — it’s obviously Idol Duc Nguyen :)))
@Kosasihg88G
And he even had the audacity to spread rumors that Nikolas had been in an accident and handed over all the remaining project work to him?? 😂 The writing style gives it away immediately — it’s obviously Idol Duc Nguyen :)))
Just look at this fraudster! For so long, he has been acting as if he were one of the technical engineers on the Pi Core Team (PCT) at Pi Network.
All he does is throw together a few snippets of code on GitHub, make superficial assessments, and run his mouth as though he were some kind of expert.
Oh, Kosasih, you’re nothing but a scammer! Just shut up and go away!
@Kosasihg88G F*ck
Anyone can participate in an external audit to contribute to the project. Anyone can be an auditor.
However, whether your findings are accepted depends on the project team’s evaluation. Think smarter.
Even you can create your own GitHub account and participate in reviewing, investigating, and evaluating real-world evidence to help identify bugs, vulnerabilities, or propose new ideas.
But remember: a discovery or an idea is yours alone. Whether it is technically sound, relevant to the project, and ultimately accepted is still up to the project team.
Anyone can audit. Anyone can contribute. But acceptance depends on evidence, technical merit, and the project team’s decision.
F*ck kosshasi your fake , report him On X
Dear all 🤨
@Kosasihg88G And then you pulled all those stunts about Nikolas getting into an accident and supposedly handing over the project’s continuation to you. For God’s sake, stop deceiving people. Put an end to this pathetic act and stop misleading others, you bastard.
I’m warning you right now.
Keep running your mouth, expert. Cut the act of impersonating other people.
If I remember correctly, you claimed two years ago that you were the one who created the project. What a liar. All you’re good at is bragging and talking nonsense.
I know you’re a Vietnamese guy. Pathetic.
@Kosasihg88G
Anyone can participate in an external audit to contribute to the project. Anyone can be an auditor.
However, whether your findings are accepted depends on the project team’s evaluation. Think smarter.
Even you can create your own GitHub account and participate in reviewing, investigating, and evaluating real-world evidence to help identify bugs, vulnerabilities, or propose new ideas.
But remember: a discovery or an idea is yours alone. Whether it is technically sound, relevant to the project, and ultimately accepted is still up to the project team.
Anyone can audit. Anyone can contribute. But acceptance depends on evidence, technical merit, and the project team’s decision.
F*ck kosshasi your fake , report him On X
Anyone can participate in an external audit to contribute to the project. Anyone can be an auditor.
However, whether your findings are accepted depends on the project team’s evaluation. Think smarter.
Even you can create your own GitHub account and participate in reviewing, investigating, and evaluating real-world evidence to help identify bugs, vulnerabilities, or propose new ideas.
But remember: a discovery or an idea is yours alone. Whether it is technically sound, relevant to the project, and ultimately accepted is still up to the project team.
Anyone can audit. Anyone can contribute. But acceptance depends on evidence, technical merit, and the project team’s decision.
🚨 Pi Network users are being urged to register with the Quantum Financial System (QFS) to stay safe. 🌐🔐
�� Click on my Telegram link to learn more! https://t.co/LzOwCcL9LJ
🚨 PI NETWORK COMMUNITY ALERT: BEWARE OF MISLEADING TECHNICAL CLAIMS AND UNVERIFIED AFFILIATIONS!
⚠️ GitHub Account Under Scrutiny: KOSASIH
🔗 https://t.co/Kw8lglm7Pf
The Pi Network community deserves transparency, technical integrity, and credible information — not exaggerated technological claims presented without verifiable evidence.
A preliminary review of publicly available repositories associated with the GitHub account KOSASIH raises serious questions about the credibility of several projects referencing Pi Network.
🔴 1. EXTRAORDINARY CLAIMS WITHOUT VERIFIED EVIDENCE
Certain repositories describe capabilities such as:
* Infinite blockchain transaction throughput (TPS).
* Negative transaction latency.
* Quantum-powered blockchain systems with extraordinary capabilities.
* Mechanisms allegedly capable of stabilizing Pi at $314,159.
These claims require rigorous, independently reproducible technical evidence.
Writing ambitious statements in a GitHub README does not make them technological achievements.
🔴 2. NO VERIFIED AFFILIATION WITH THE PI CORE TEAM
There is currently no independently verified evidence establishing that KOSASIH is an authorized member or official representative of the Pi Core Team (PCT).
Creating repositories containing the words “Pi Network,” “Pi Supernode,” or “Pi Blockchain” does not establish official affiliation, technical authority, or control over Pi Network’s infrastructure.
Independent developers must not be confused with official protocol maintainers.
🔴 3. HUNDREDS OF REPOSITORIES DO NOT PROVE TECHNICAL COMPETENCE
Thousands of commits, extensive documentation, and sophisticated terminology cannot replace:
✅ Reproducible performance benchmarks.
✅ Functional software demonstrations.
✅ Independent security audits.
✅ Transparent development histories.
✅ Verified integration with official infrastructure.
AI-assisted programming is legitimate. However, AI-generated documentation or code should never be presented as proof of revolutionary technology without proper validation.
🔴 4. WE DEMAND TRANSPARENCY AND ACCOUNTABILITY
The following questions deserve clear answers:
1. Does KOSASIH have any officially documented affiliation with the Pi Core Team?
2. Where are the independently verified demonstrations of these technologies?
3. Have the systems undergone credible security and performance audits?
4. What technical or economic evidence supports the extraordinary claims concerning Pi’s valuation?
Until these questions are answered, such projects should be treated as independent, unverified initiatives — not official Pi Network developments.
🚨 5. PROTECT THE PI NETWORK COMMUNITY
We encourage community members to verify information through official Pi Network channels.
If documented evidence of impersonation, deceptive representation, or other violations emerges, it should be reported through GitHub’s established reporting procedures.
⚡ FINAL MESSAGE
Pi Network needs genuine innovation, not technological theater.
A GitHub repository is not proof of authority.
A README is not a security audit.
AI-generated code is not proof of a working blockchain.
And extraordinary claims without extraordinary evidence deserve serious scrutiny.
The credibility of an entire blockchain ecosystem must never depend on unverified statements from independent accounts.
REAL TECHNOLOGY REQUIRES REAL EVIDENCE.
#PiNetwork #PiCoreTeam #GitHub #Blockchain #CryptoSecurity #TechTransparency #PiCommunity #Web3 #OpenSource
@PiCoreTeam Official statements and decisive measures are needed to expose and remove these despicable individuals who have no affiliation with the team yet repeatedly distort the truth and spread misinformation.
You filthy, despicable piece of trash! Stop this ridiculous nonsense with your stupid lines of code on GitHub immediately!
Remember this: you are nobody, and you have absolutely no affiliation with the Pi Core Team (PCT).
You have no credibility or qualifications when it comes to software engineering or programming. Stop pretending to be someone important!
Shut your mouth and get lost! We will be reporting your account for impersonation and misrepresentation. F*ck
🔐 Crypto experts are raising a critical concern: what if the cryptography protecting today’s digital assets becomes vulnerable sooner than expected?
At COHIBA, we had already included post-quantum preparation in our Human Signal / SI roadmap.
Our experimental HS/2 now requires both Ed25519 and hash-based SLH-DSA signatures across the authorization chain, connecting human authority, agent permissions and signed actions.
Our goal: make human authorization independently verifiable as AI agents become more autonomous.
This is an experimental implementation, awaiting independent review—not a claim that blockchain wallets are already quantum-safe.
The next steps are clear: independent security review, external pilots and measurable performance.
Preparing early matters. Earning trust requires evidence.
Explore our public verification lab:
https://t.co/MNANw3aUOG
AI owns intelligence.
Humans own authority.
SI enforces the boundary.
#COHIBA #HumanSignal #PostQuantum #AIAgents