@BancoCentralBR is advancing to contract Hypernative to operate a continuous onchain monitoring and fraud intelligence program for Brazil's financial sector.
The engagement follows a proof of value in which we built a BCB-specific detection methodology from scratch: multi-layer agents tracking BRL/crypto volume anomalies across major Brazilian exchanges, cross-exchange synchronicity signals, intraday velocity patterns, and behavioral markers calibrated against known incident fingerprints.
The decisive proof point: a preparatory alert issued 14 hours before a confirmed fraud incident. Several high-confidence alerts generated during the PoC were later associated with confirmed incident activity, supporting the thesis that fraud-to-crypto laundering can produce detectable setup patterns before full dispersion.
BCB is becoming Hypernative's first central bank customer. The program is now live as a productized regulatory intelligence operation, with continuous monitoring, methodology maintenance, onchain investigation support, and dedicated analyst hours.
🔗 Read the announcement (EN): https://t.co/kBpmCHUsYQ
📰 Article in BitNotícias (pt_BR): https://t.co/S5b8U4crW4
You can have a perfect list of your counterparties and still be sunk by a protocol you've never heard of.
Onchain, risk reaches you indirectly. And it moves in minutes, not days.
4/ Thailand's crypto ETF rules went live October 16, starting with bitcoin and ether. Additional assets will be assessed on liquidity, market acceptance, network security, and investor protection.
https://t.co/eKTsh24yqP
3/ The Australian Securities and Investments Commission (ASIC) has begun consulting on digital asset platform standards taking effect April 8, 2027.
https://t.co/gVoILqiOHN
2/ The Brooklyn DA and FBI dismanted a $300K crypto fraud network, seizing 112 servers and 241 domains after earlier site takedowns failed to stop a crypto scam targeting Russian speakers.
https://t.co/NCBLAGXTvO
1/ USDC is MiCA's first "significant" e-money token. From Nov 12, the EBA oversees reserves, liquidity, and redemption plans, while France's ACPR retains governance oversight. The debut of MiCA's dual-supervision model.
https://t.co/0dENc7wEMh
Up until now, asset managers who needed a specific onchain monitor had two choices: file a request with security or build it themselves.
Our Agent Studio adds a third: describe it in plain English, and it builds the agent for you.
Here’s how @wavedigital_ Head of International Portfolio Management describes it 👇
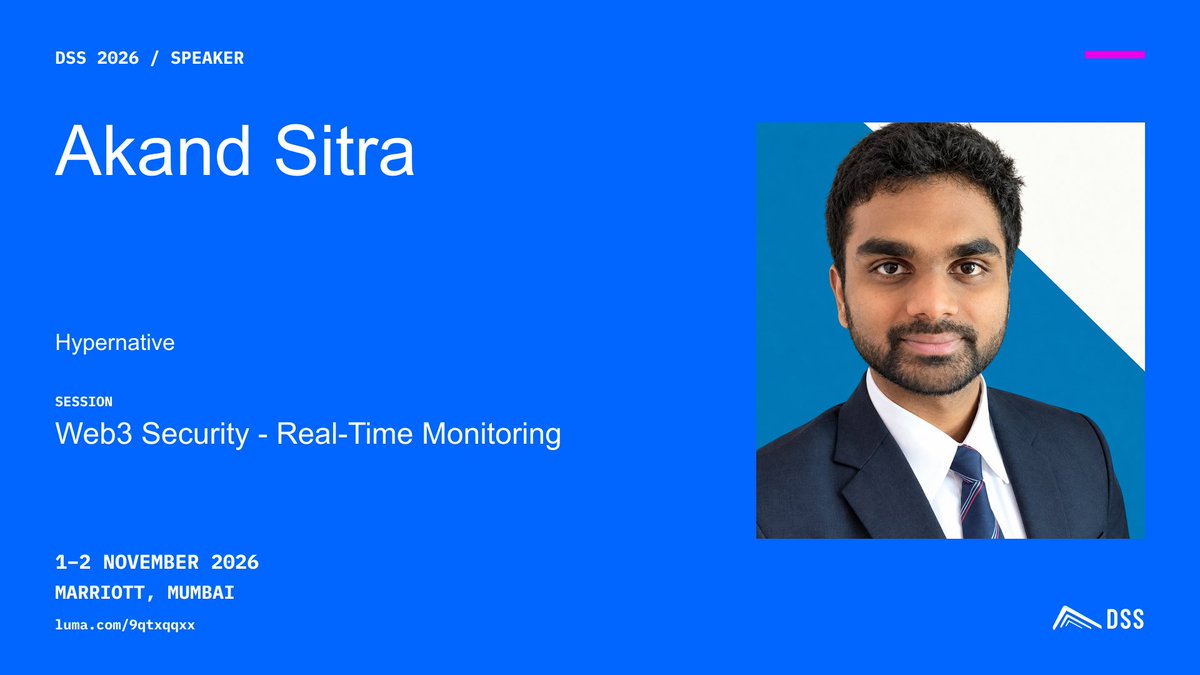
Meet DSS 2026 speaker Akand Sitra.
“Web3 Security - Real-Time Monitoring”
Open a talk and save it to your agenda.
https://t.co/nQwGo2Pc7N
Tickets: https://t.co/RTbPxGH7zF
Step 3 of a governance attack: 🏆️ win the vote.
Attackers use two tactics to manipulate the result.
1️⃣ Wait for low turnout. When few holders vote, quorum is easy to reach.
2️⃣ Vote at the last minute.
Read more in our primer on malicious governance attacks: https://t.co/hR3PIRFs7V
Hypernative is heading to Buenos Aires for Argentina Fintech Forum (
@CamaraFintechAr) on October 29 🇦🇷
Gui will be on the ground meeting with banks, fintechs and exchanges building onchain across the region.
Get in touch to set up a meeting
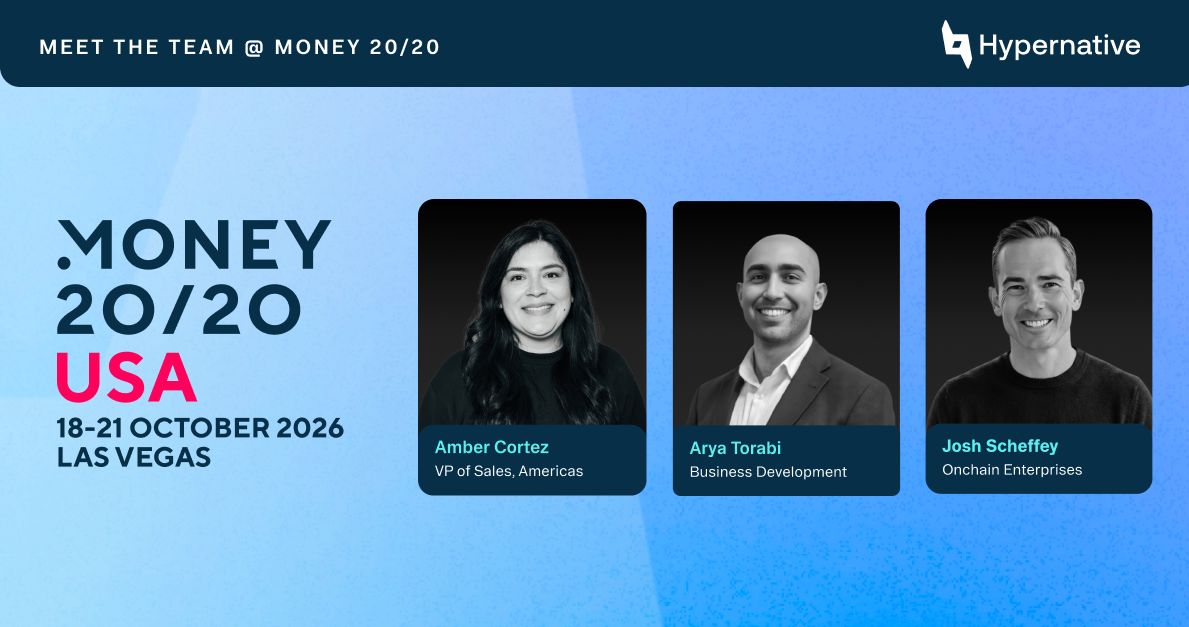
🌎️ Halfway through October and the Hypernative team will be racking up more miles. We're excited to see you at Blockchain Africa, Money20/20 USA, The Digital Asset Conference, Argentina Fintech Forum, Alpaca Partner Summit, The Bridge, Ripple Swell, Merge Madrid, and Stellar Meridian.
Step 2 of a governance attack: ✒️ write the proposal.
Hostile proposals leave tells. Yam's #45 had an empty description. Olas's named a Safe address that had no code deployed.
What to check before the vote: https://t.co/kf4Zf1Z3W9
Post-mortem update.
A protocol pause stopped an attempted exploit.
No user funds were lost.
The issue was in hub reward-vault balance accounting.
A third-party delegated stake could inflate a strategy’s reported balance.
That inflated vault NAV, which then flowed into the junior / Alpha rate.
An attacker deployed a contract targeting this.
The attempt failed.
With support from @HypernativeLabs and @KodiakFi , the issue was flagged and we paused our contracts in time.
The fix has been fork-verified and deployed.
Reported balance now excludes delegated stake.
Deposits and withdrawals are open again.
The protocol is back to normal operation.
Post-fact alerts are cheap. Prevention is hard because automated action needs high conviction and low noise. Hypernative keeps adding public, verifiable cases of it working. Latest: Kodiak’s automated pause stopped an exploit on BeraFarm that could have cost $250K+. Zero funds lost.
On Oct 9, 2026, Kodiak's real-time security monitoring (powered by @HypernativeLabs) detected a malicious contract targeting a vulnerability in an external vault provider's contracts that interacted with Kodiak Islands. NO FUNDS WERE LOST.
As designed, our pre-configured automated response with Hypernative paused all Kodiak Islands within seconds, before the attacker could execute the exploit. The pause closed the route the exploit needed and stopped an attack on an external ecosystem protocol, BeraFarm.
No Kodiak user funds were lost or extractable. The simulation estimated a loss of at least $250K had the exploit succeeded.
Read more about how Kodiak and its ecosystem partners are secured with Hypernative's real-time security: https://t.co/p25hDAxjGL
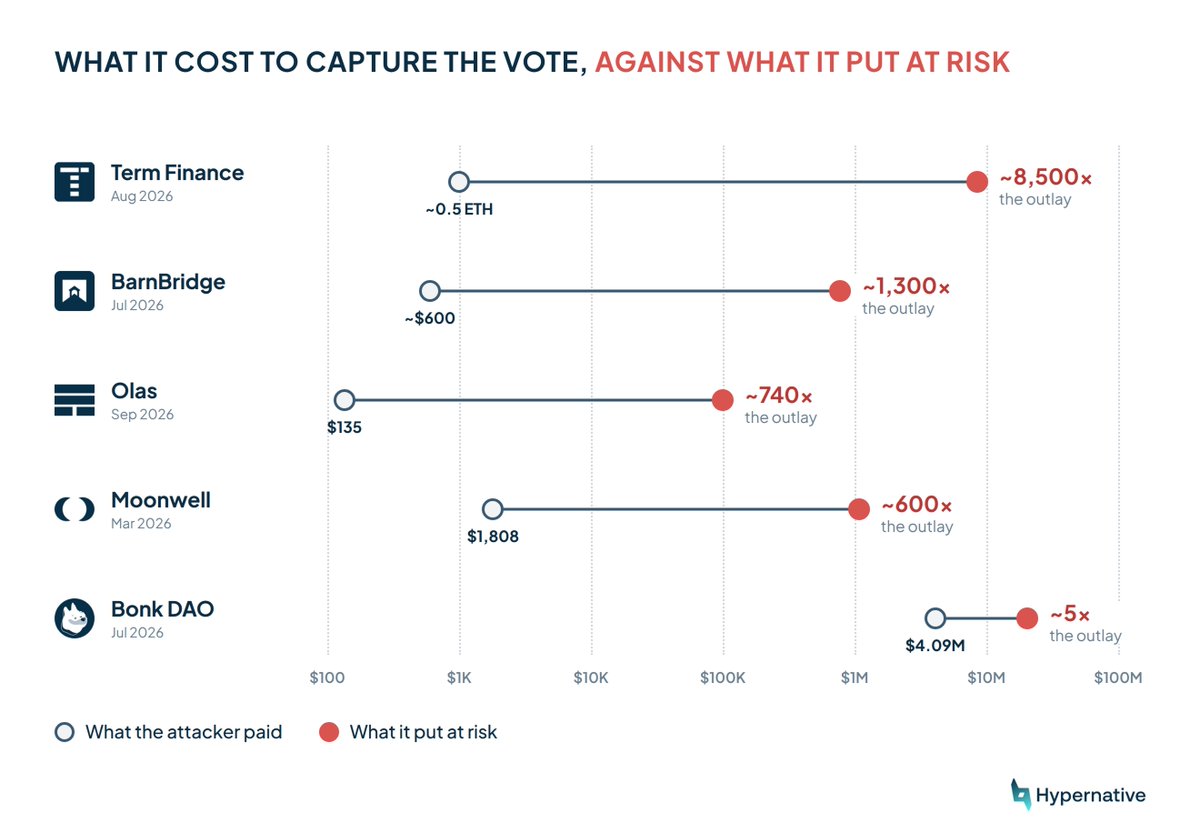
First step of a governance attack: 💰️ buy the votes.
In a healthy DAO, a controlling position is expensive, but dormant ones can cost less than a restaurant bill.
Our primer on malicious governance attacks covers the ways attackers build a voting position: https://t.co/ImJdQwvyTY