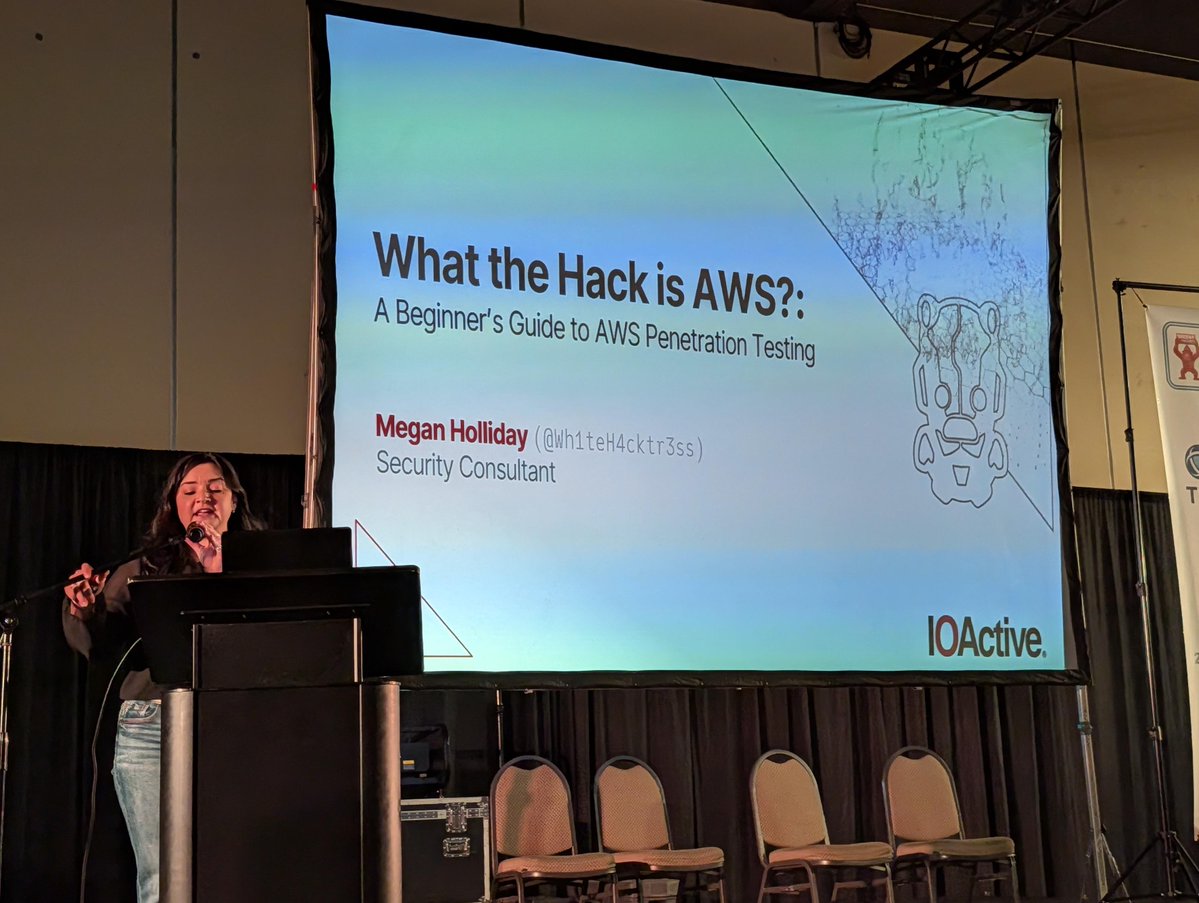
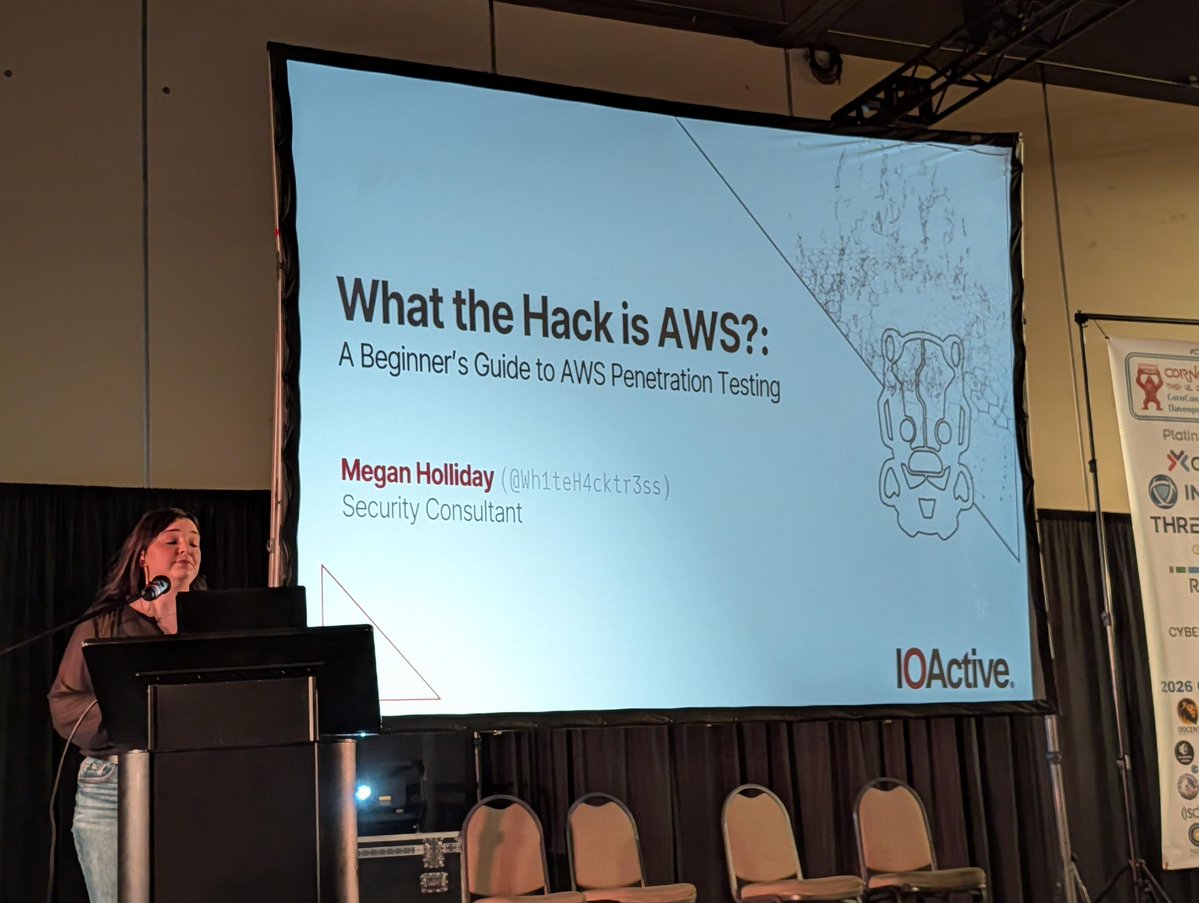
Thanks to everyone who joined Megan Holliday's session at @cornconcyber Conference yesterday! 🌽 Great questions, great conversations, and a packed room. A few highlights below.
Want to see how IOA helps orgs stay ahead of real-world threats? 👉 https://t.co/lJnuyRYKUi
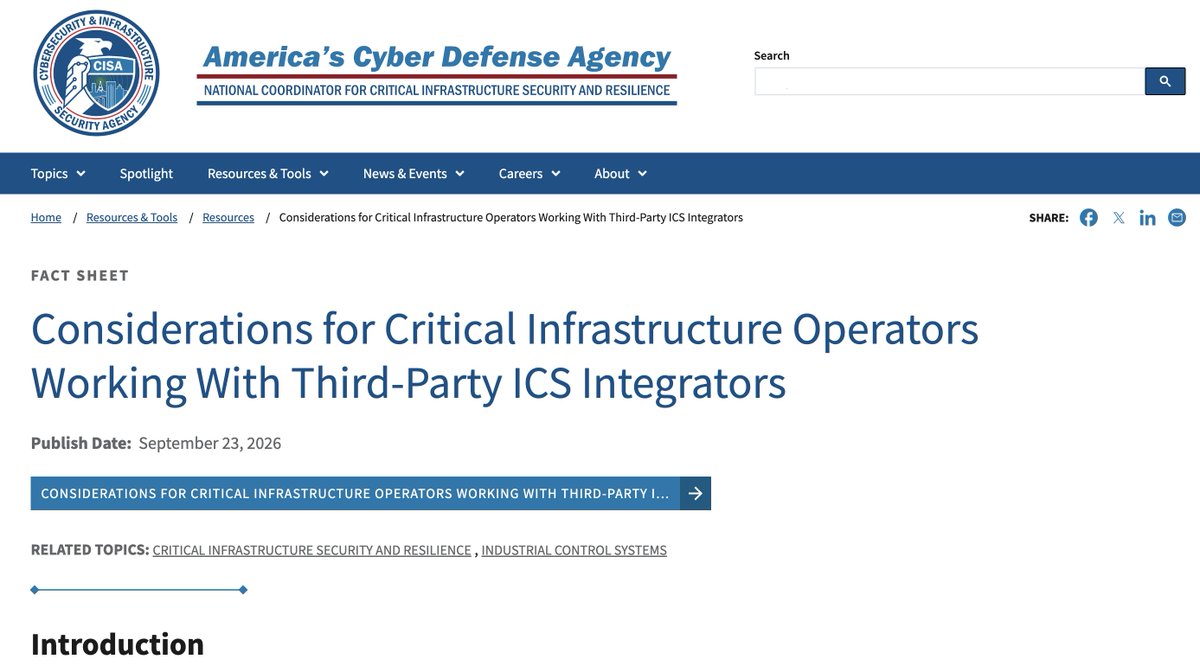
New FBI/CISA guidance raises a question every operator should be able to answer: if your ICS integrator were compromised tomorrow, could you still run your plant? https://t.co/Ci2sIrr7qN #OTSecurity
Asking an LLM to "find all the vulnerabilities" gets you noise. Asking it one testable question anchored in a threat model gets you real bugs.
Carlos Gomez explains the workflow behind two HIGH-severity Angular CVEs: https://t.co/1l7ZVNHIOa
#VulnerabilityResearch#AISecurity
IOActive is proud to sponsor @cornconcyber Conference 2026, kicking off tomorrow, October 1! Don't miss Megan Holliday on October 2 for a practical introduction to penetration testing AWS environments. https://t.co/hO5Uk7XvEN
Is your AI ready for an adversary? IOActive breaks down the most critical AI red teaming techniques organizations need to know in 2026. https://t.co/OWLPUO6M4x
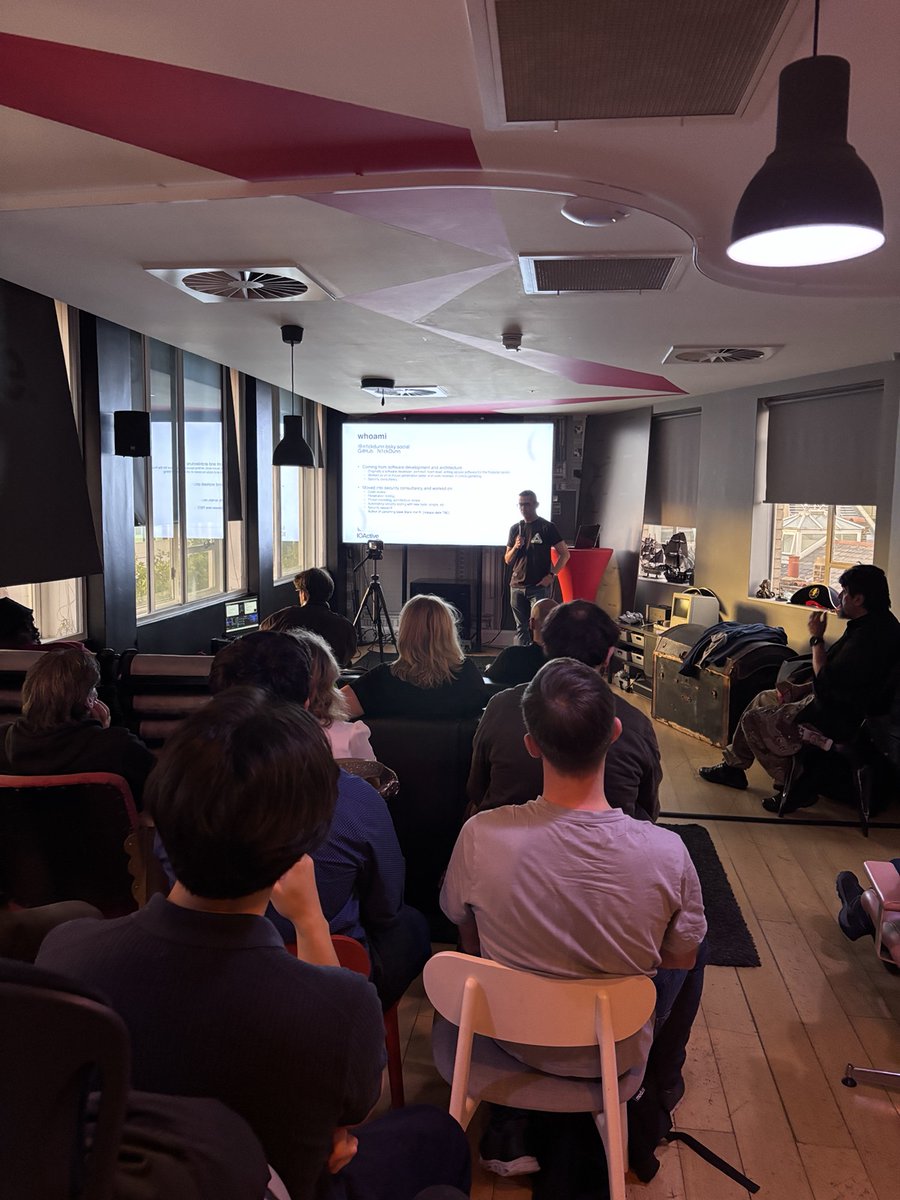
That's a wrap on September's #hacksoho! Thanks to everyone who joined us in London and helped this community keep growing. Huge thanks to Nick Dunn for a great talk on data-bouncing exfiltration.
Internet-exposed OT. Different threat actors. The same fundamental risk.
IOActive examines the NCSC’s latest OT Alert alongside AA26-097A — without conflating attribution — and what CNI operators should prioritise next. https://t.co/MktEIlJUfn
#OTSecurity#ICS#IOActive
We're just a couple of hours from going live with this month's hack::soho.
IOActive Senior Security Consultant Nick Dunn will present "A Stealth and Safety Issue: Exfiltration Using Data Bouncing," followed by an open discussion.
Tune in live! https://t.co/lQbaIEcxCu
Last call: hack::soho is TOMORROW (24 Sept). Nick Dunn is showing how "data bouncing" lets attackers exfiltrate data under the radar. Great talk, great crowd. Grab your spot! https://t.co/pH8hLwQs0q
#hacksoho#cybersecurity#infosec#RedTeam
Organizations managing risk reactively are nearly twice as likely to suffer a breach. These benchmarks show what separates mature IT risk management strategies from vulnerable ones. https://t.co/PVEP7XgXRo
Sun, tapas, and hardware hacking — our Madrid Summer Fiesta had it all. 🎉 Thank you to everyone who came out, and huge props to our team for the great presentations and hosting. Good food, great people, unforgettable day. 🙌 #IOActive#MadridHardwareLab
A UK generator was offline for 4 days after a cyberattack. No confirmed attribution. No disclosed vector. What IS known: attack surface is measurable — and CISA, NCSC, DESNZ and Ofgem are all pointing the same direction.
Our breakdown 🧵 https://t.co/xjqhZW0nPH
Hola!! La semana que viene tenemos un pequeño sarao en el lab de Madrid; habra charlas, comida, bebida y networking! No dudéis en apuntaros y compartirlo.
Podéis apuntaros aquí: https://t.co/DFBSC6GozD
Not all cybersecurity tests ask the same question. Compare the top cybersecurity testing methodologies, from vulnerability assessments to Red Teaming, and find the right fit. https://t.co/n7kBM9EcEZ
CISA just confirmed the July water sector cyberattack was 3x bigger than first reported: 100+ systems, 12 states — not ~30 in Minnesota.
A second advisory (AA26-231A) flags AI-generated exploit scripts targeting Siemens S7 PLCs across 6 sectors. https://t.co/lzqKJve9ts
hack::soho is back Sept 24 in London 🇬🇧
IOActive's Nick Dunn presents "data bouncing" — a stealthy new DNS-based exfiltration technique flying under most defenses' radar. https://t.co/pH8hLwPUaS