Look for some quick defense lessons? Check out my mini-series: 🎄The 12 Days of Defense!🎄 Short videos illustrating key concepts for cyber defenders, SOC analysts, and blue teams everywhere! #infosec#CyberSecurity https://t.co/7L6XTtfhsQ
You guys have done a awesome job @noobarmy_ I know it is hard to maintain server ,it kept crashing initially. But you guys never failed us. By far best CTF I've participated in. All for your dedication ,hard work & Thanks for second round of challenges!
#BestCTF#bugbounty
Last episode of the DAY[0] podcast before the Christmas break goes live in about 10 minutes. Featuring the CISA emergency directive regarding SolarWinds Orion, a PS4 webkit exploit, and XSS for PDFs.
https://t.co/cfd7OzglkH
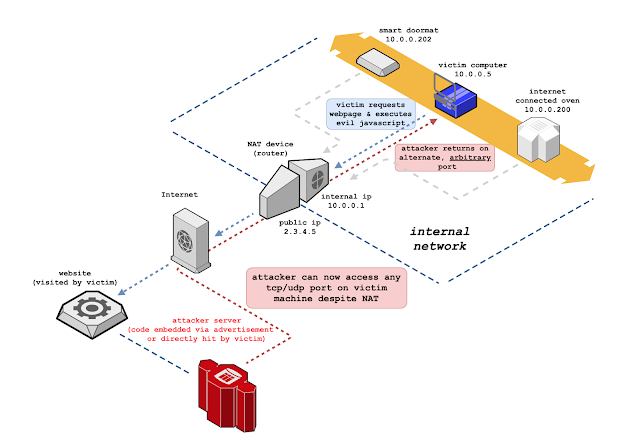
Slipstream - NAT Slipstreaming Allows An Attacker To Remotely Access Any TCP/UDP Services Bound To A Victim Machine, Bypassing The Victim's NAT/firewall, Just By The Victim Visiting A Website https://t.co/0DDrOKEo0h
Hello all, I'm happy to say that we are community partners for VULNCON 2020 by @noobarmy_
N00B_4rMY has organized virtual hacking conference VULNCON 2020
And 24/7 CTF
Prizes worth $11,000 for more info https://t.co/gvoK049nsu
Register for the CTF @ https://t.co/XgTzomou92
We are up with small blogs on 🥰:
1. A quick introduction to YARA:
https://t.co/Esgr01lvro
2.Application of reverse engineering 0x02:
https://t.co/AVUDDCWTRD
3. Social Network Analysis: The Samurai Way:
https://t.co/TYDl8Rk2yX
#osint#malware#reversing
We are happy to release one of our project R4PT0R a malware library , we heartily thank @InQuest ♥️for supporting us with samples for the library & for community , research purposes. Stay Tuned !!
Make sure to check it out at :
https://t.co/krPJsfQxmr
#malware
We are proud to announce @0xAsm0d3us as one of our esteemed speakers who will be speaking on "How not to fail in Bug Bounties [Recon, Automation, Hunting Cloud, and hidden assets]" at VULNCON 2020, Virtual Cyber Security Conference.
Stay tuned for more updates!