[BREAKING] FIFAe World Cup is set to take place in Tokyo, Japan, in January, @EchoMena_ reports.
According to Rocket Street sources, FIFAe has worked with Epic Games to avoid a scheduling clash with the Club League Open dates.
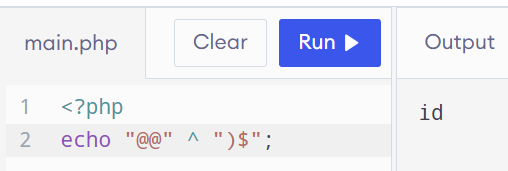
PHP allows bitwise XOR operation of strings so we can "create" words like system, id, curl...
really useful for bypassing some challs that might be blocking strings
some alpha drop for doing inexpensive vuln research.
instead of writing an article on the prompts/process behind this bounty (and more), I am dropping some prompts and the thought process I used as part of this research.
ik you might say prompts don't matter much, frontier models' baseline intelligence can rawdog vuln discovery (and it is true to a good extent), but there is a high chance that you either do not have access to cyber models, or even if you do, they are expensive (and with heavy guardrails). The idea is, these prompts work well with open-weight/less expensive models. Not saying these will outperform the raw intelligence and capabilities of frontier models, but open-weight models perform much better with a bounded/goal-specific approach (where the goal is set, and the search space is massive) rather than open-ended exploration (where the goal is vague, and the search space is massive).
anyway, here are some prompts. I don't need to share much, because you can just create variations of these and apply them wherever you wish.
- find places where the app is supposed to enforce something, but doesn't actually enforce it.
- find security rules that are enforced in one part of the app, but just assumed to be true in another.
- find security assumptions the app relies on, but never actually checks or enforces.
- find places where the app depends on undocumented behavior, and what happens if that behavior changes.
- find operations that are secure on their own, but become vulnerable when you combine or chain them together.
- find cases where the same object can be accessed in different ways, but each way ends up having different permissions.
- find objects whose identity can be changed or rebound to another user, without going through the right checks.
- find requests that get rejected or fail, but still end up changing something or triggering a side effect.
- find security checks that only work if certain events happen in a specific order, and what happens if that order changes.
- find operations where the transaction fails or rolls back, but some of the side effects still happen.
- find things you can still do with an object even after it has been deleted, or access to it has been revoked.
- find state changes that can be reversed or undone by someone who shouldn't have permission to do so.
- find objects that can end up in two contradictory states at the same time, and what operations become possible because of that.
I take such prompts, put it in a mutator (which has threat model of the project I am doing sec engagement), the mutator will mutate the prompts based on the threat model, and spawn swarm of agents, with different starting prompt and a bounded goal, the process repeats till all paths are exhauted, or some new signal is generated, which then feeds back to mutator.
Doing this using a cheap model is very effective and sometimes it might yield you something even expensive models miss, we are just trying to maxximise the search space, from as many angles as possible, and once this process generates enough signals, just use a frontier model to confirm/triage issues, or for finding similar variants of such issues, that's basically it. There is v less moat is making a custom harness (unless you are an elite vuln research who can codify their approach in it or a 100x agentic engineer, I am neither).
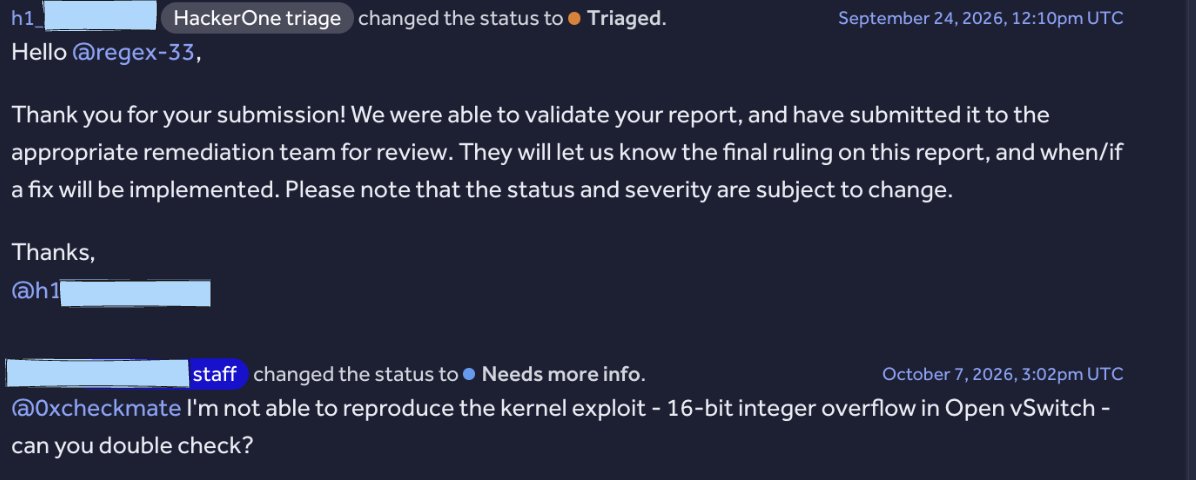
Bug bounty programs are using weak excuses to scam researchers out of critical payouts.
I reported a full sandbox escape to a Kubernetes node as root from normal access in a container to the host node in their infrastructure.
@Hacker0x01#bugbounty
We believe @G2esports G2 Esports has made a grave mistake in terminating its relationship with Perkz over his publicly expressed personal convictions.
“Diversity” must include diversity of thought, belief, and opinion.
You do not have to share someone’s religious, political, or moral convictions to respect their right to hold them. The true measure of tolerance is how we treat people with whom we disagree.
G2 had an opportunity to demonstrate mature, principled leadership by acknowledging those differences without demanding ideological conformity. Instead, it chose exclusion while invoking the very principles of diversity and inclusion that should encourage mutual respect.
An organization that cannot tolerate disagreement within its own ranks is not demonstrating strength, progress, or inclusivity. It is demonstrating an inability to navigate differences with maturity and professionalism.
Tolerance that extends only to those who agree with you is not tolerance. It is conformity masquerading as virtue.
We believe G2 should expect better of its leadership, its organization, and the values it claims to represent.
Weak, pathetic behavior by G2.
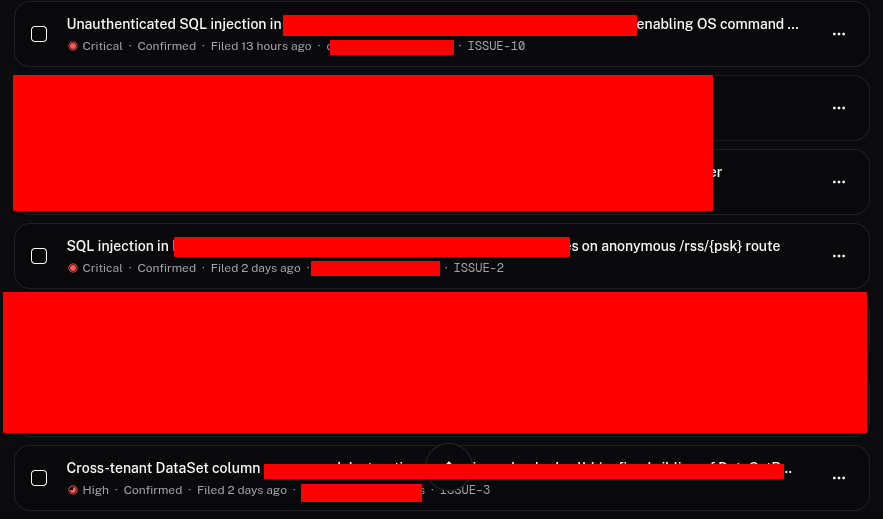
My free version of neo just ran out. The tool was really good on the free version. Its strongest point is escalation of bugs . It escalated 2 of my SQLi findings to criticals .
@LCSOfficial@LyonLATAM How do you become the best if you don’t swing at the king.
It's not whether or not you get knocked down, it's what you do when you get back up.