So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
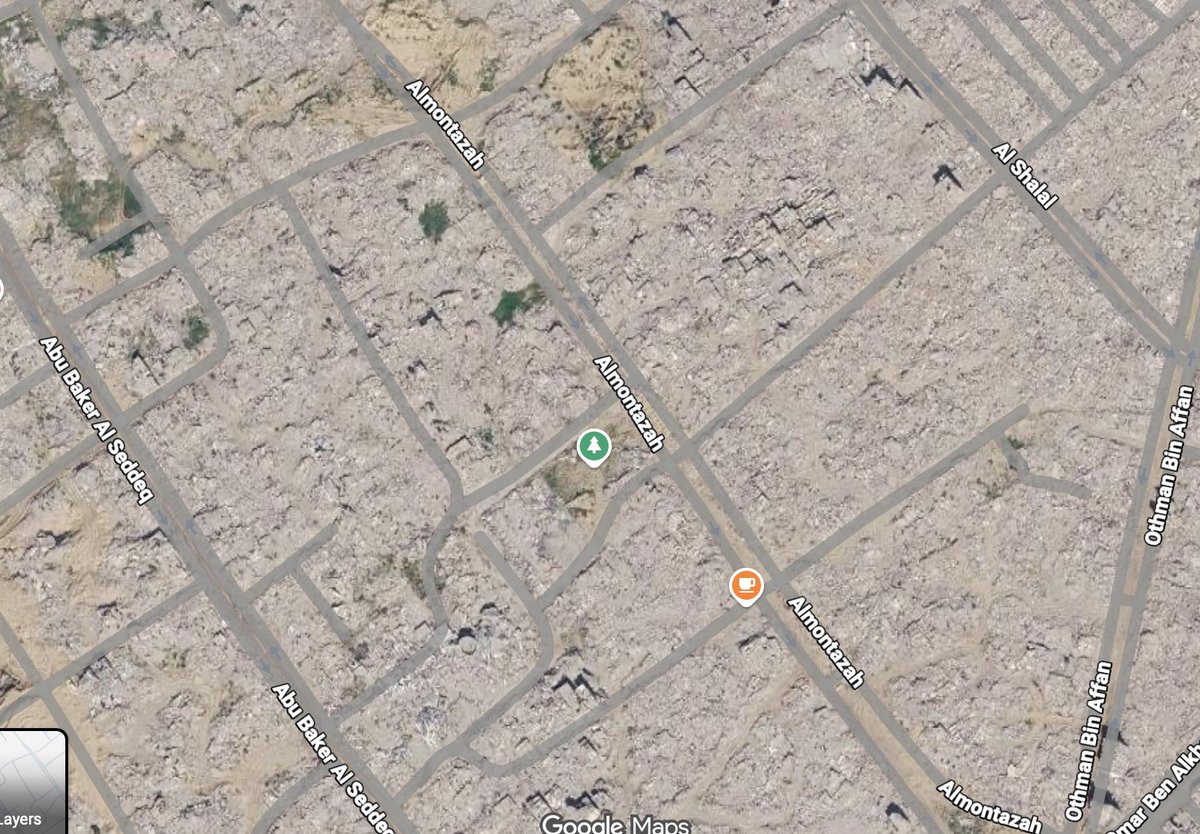
3 years into the genocide initiated by Israel in Palestine, the number of reported people killed has passed 74,000 and over 175,000 injured — a culmination of decades of ethnic cleansing in Gaza.
(https://t.co/c4bWzOI1xn)
@Hi_Mrinal true. I discovered runtime.Gosched() recently and it’s fantastic for allowing things to gather up (without using a hardcoded sleep) before starting an execution job
is there a service that can run a benchmark suite in hardware that isn't shared with other containers?
@modal is nice since you only pay for cpu time, but it runs on shared hardware which makes the results useless, and @codspeed can't run on personal repos for some reason..
i’ve been using poke since last november, and recently it genuinely became unusable.
seems they’re prioritizing response latency over everything else, even spending even a few seconds to understand what the user is actually talking about
"That framing is half-right, and the half that's off matters"
Where in the training data is this abominable sequence of tokens and why is it weighted like 100000x
and now i feel a sudden urge to spawn 50 subagents to explore opportunities in other places where we could see similar wins.
i love this new era. yes we’ll all be homeress pretty soon but at least it’ll be really fun in the meantime.
i wanted to refactor some code just to unify 2 similar execution paths into one, without changing any actual logic.
turns out that somehow allowed the go compiler to inline a function i was calling within a loop and now the whole thing runs 50% faster HUH??
@7amza_7Z7 claude code app is still very buggy and the ux sucks.
also opus-5 is trash, opus-4.8 is just a bit less trash than opus-5. fable is way too expensive for daily usage.
meanwhile codex app is fast and clean, and sol is near ~fable and way cheaper.