SilentClaim has been submitted on @token2049 Origins Hackathon!
SilentClaim is a bug-bounty protocol that pays out on proof, not on a promise.
A whitehat signs the exploit with their own wallet and never broadcasts it. A @chainlink CRE workflow simulates the transaction, reads the balance before and after, and emits only a verdict. On @solana , the bounty program checks that verdict, then pauses the vault and pays in one transaction.
Inspired by the Liquid Network L-BTC incident, where a bounty was negotiated only after funds had moved, and by @0xFlorent_ 's RISC Zero proof-of-drain The trust layer here is CRE instead of a Groth16 seal. The CRE path is cheaper to verify on-chain, whereas the RISC Zero proof is trustless.
Developed by Xp0int team.
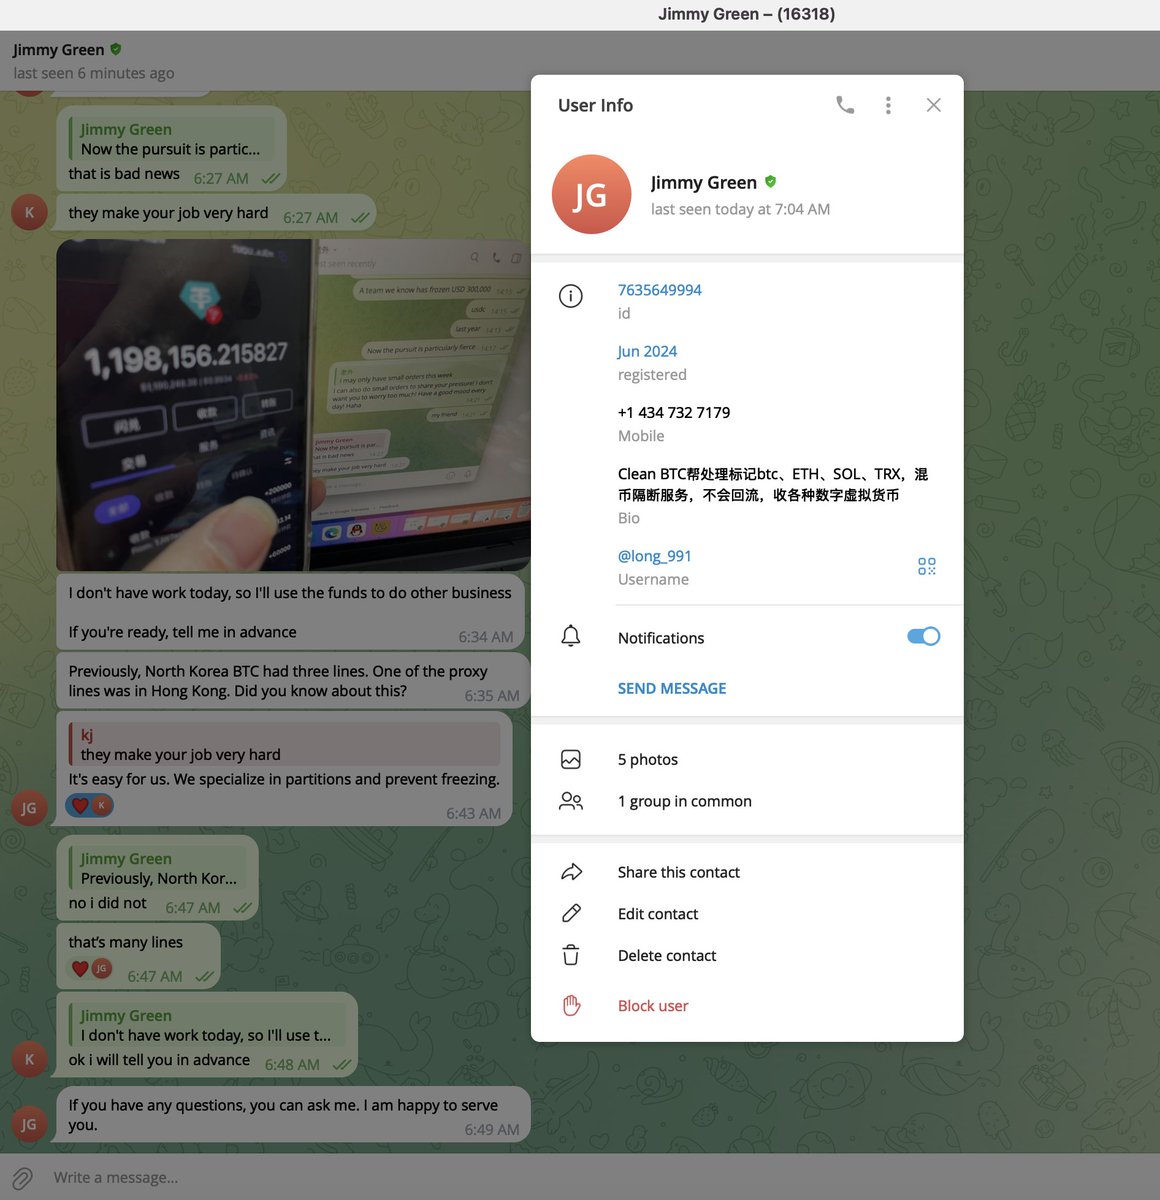
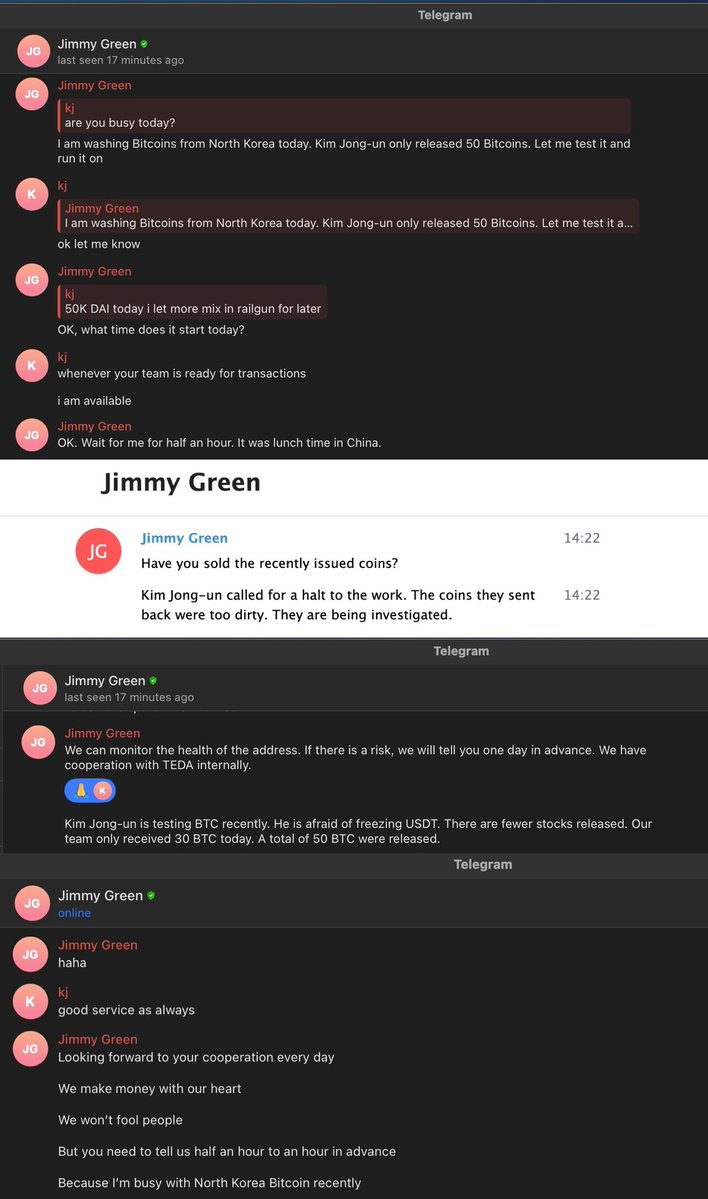
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.