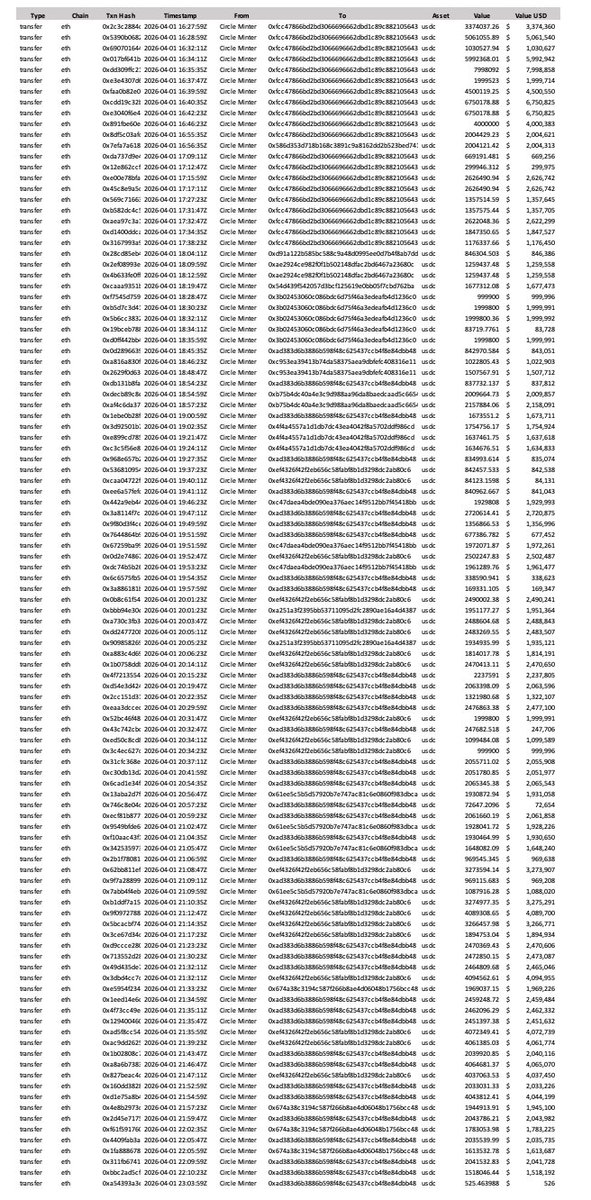
Update: $230M+ USDC bridged via CCTP from Solana to Ethereum across 100+ txns.
6 hours is how long Circle had to freeze stolen funds from the $280M+ Drift hack.
Circle is a centralized stablecoin issuer headquartered in New York and the attack began around 12 pm ET.
Why does our industry allow them to stay silent?
@jerallaire@circle@usdc
This is quite an impressive experiment. Vibe-coding the entire 2030 roadmap within weeks.
Obviously such a thing built in two weeks without even having the EIPs has massive caveats: almost certainly lots of critical bugs, and probably in some cases "stub" versions of a thing where the AI did not even try making the full version. But six months ago, even this was far outside the realm of possibility, and what matters is where the trend is going.
AI is massively accelerating coding (yesterday, I tried agentic-coding an equivalent of my blog software, and finished within an hour, and that was using gpt-oss:20b running on my laptop (!!!!), kimi-2.5 would have probably just one-shotted it).
But probably, the right way to use it, is to take half the gains from AI in speed, and half the gains in security: generate more test-cases, formally verify everything, make more multi-implementations of things.
A collaborator of the @leanethereum effort managed to AI-code a machine-verifiable proof of one of the most complex theorems that STARKs rely on for security.
A core tenet of @leanethereum is to formally verify everything, and AI is greatly accelerating our ability to do that. Aside from formal verification, simply being able to generate a much larger body of test cases is also important.
Do not assume that you'll be able to put in a single prompt and get a highly-secure version out anytime soon; there WILL be lots of wrestling with bugs and inconsistencies between implementations. But even that wrestling can happen 5x faster and 10x more thoroughly.
People should be open to the possibility (not certainty! possibility) that the Ethereum roadmap will finish much faster than people expect, at a much higher standard of security than people expect.
On the security side, I personally am excited about the possibility that bug-free code, long considered an idealistic delusion, will finally become first possible and then a basic expectation. If we care about trustlessness, this is a necessary piece of the puzzle. Total security is impossible because ultimately total security means exact correspondence between lines of code and contents of your mind, which is many terabytes (see https://t.co/boM9vZs3dh ). But there are many specific cases, where specific security claims can be made and verified, that cut out >99% of the negative consequences that might come from the code being broken.
@jon_charb Hyper liquid is in most respects everything wrong with crypto
Founder literally fled his home country to build
Openly facilitates crime and terror
Closed source
Permissioned
According to AK's info and the orderbook, these are ETH 3800 Puts expiring in 14hours from now.
A few of these 1day options trade, but a concerted effort in this specific Strike aligns up with the $15 price tag; 12k+ size.
Perhaps has bought other Strikes too ('I own all' - AK).
Not far from being ITM already. Nice play.
'k-ching'
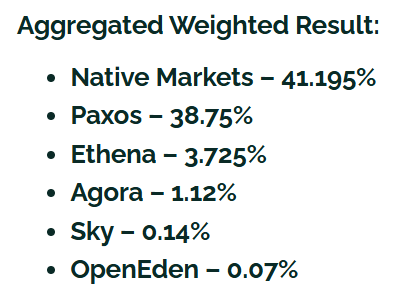
One problem is that once Paxos loses, noone serious will ever do business with HL again
Another problem is HL loses all plausible censorship resistance after this
Do "Native Markets" have the same technical capacity as Paxos to launch & manage a stablecoin?
As a $HYPE maxi, I'm all for staying Hyperliquid & community aligned..
But alignment doesn't matter if the product isn't good or used. I've seen enough stablecoins go to zero.