The project ended.
The employee left.
The app was forgotten.
Did the access disappear too?
That is why visibility matters.
https://t.co/BDBAZTzNtM
#J2MSSP
There is a difference between:
“What software did we buy?”
and:
“What software still has access?”
We think every business should know both answers.
https://t.co/BDBAZTzNtM
#J2MSSP#CloudSecurity
The app nobody remembers may still have access to company data.
Cloud tools are easy to connect.
They are also easy to forget.
What is actually connected to your business accounts today?
https://t.co/BDBAZTzNtM
#J2MSSP#CyberResilience
@PresidencyZA We are always on hand should cybersecurity support be required. J2 – AWARD WINNING MANAGED CYBER SECURITY FOR EVERY SA BUSINESS
SA Mimecast Customer Service Excellence Partner of the Year.
https://t.co/uK9qldFKbE
You cannot protect what you cannot see.
That includes the suppliers, applications and services connected to your business.
J2 MSSP. Here to help.
#J2MSSP#CyberResilience#SaaSSecurity
We do not think outsourcing creates the problem.
Losing visibility does.
If a supplier or SaaS platform can reach your systems or data, that relationship is part of your cyber risk.
https://t.co/BDBAZTzfEe
#J2MSSP#CyberResilience
Your cyber perimeter no longer stops at your own systems.
Suppliers, SaaS platforms and cloud services all extend the digital footprint of the business.
The useful question is:
What are we connected to?
https://t.co/BDBAZTzNtM
#J2MSSP#ThirdPartyRisk
If your website or business systems use PHP, this is one to act on today.
The NCSC has warned of two critical vulnerabilities, with security updates expected from 15:00 BST.
Ask your developer or IT provider whether you are affected.
#J2MSSP#CyberSecurity
We do not expect people to be perfect.
That is why good cyber security uses layers.
Email security. Awareness. Strong authentication. Monitoring.
One mistake should not become the whole incident.
https://t.co/BDBAZTzNtM
#J2MSSP#CyberResilience
Phishing does not need to look amateur anymore.
The email can look right. The login page can look right. Even the MFA prompt can look familiar.
We think the habit matters more than the appearance.
Open the real site yourself.
https://t.co/BDBAZTzNtM
#J2MSSP
The email asks you to log in.
It looks genuine.
Stop.
Open your browser and go to the website yourself instead of using the link.
A small habit can remove a very convincing trap.
https://t.co/BDBAZTzNtM
#J2MSSP#Phishing
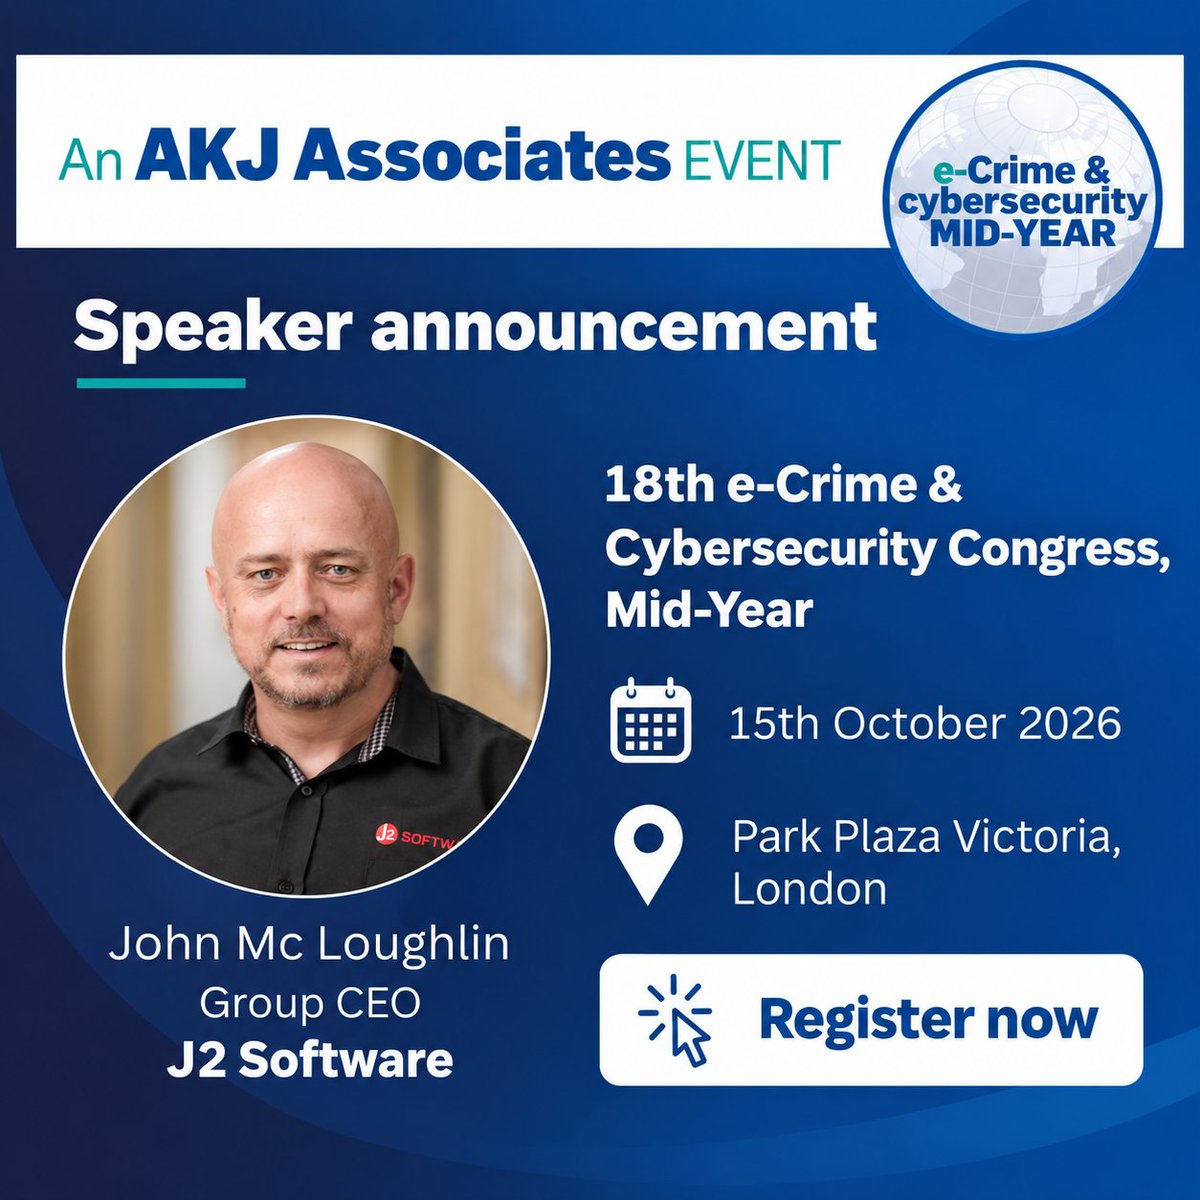
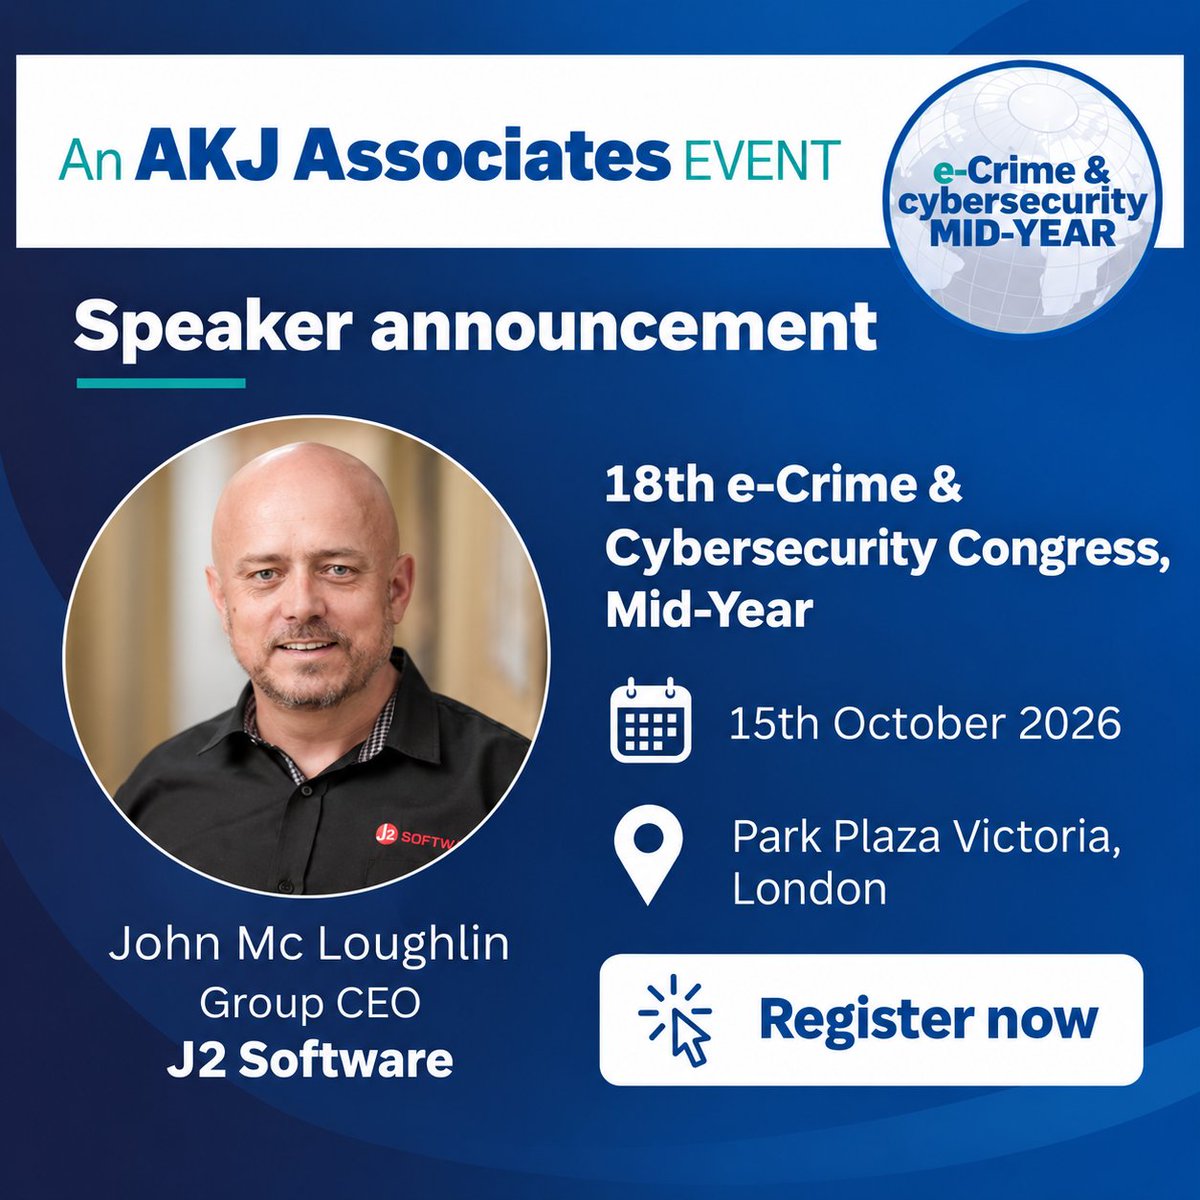
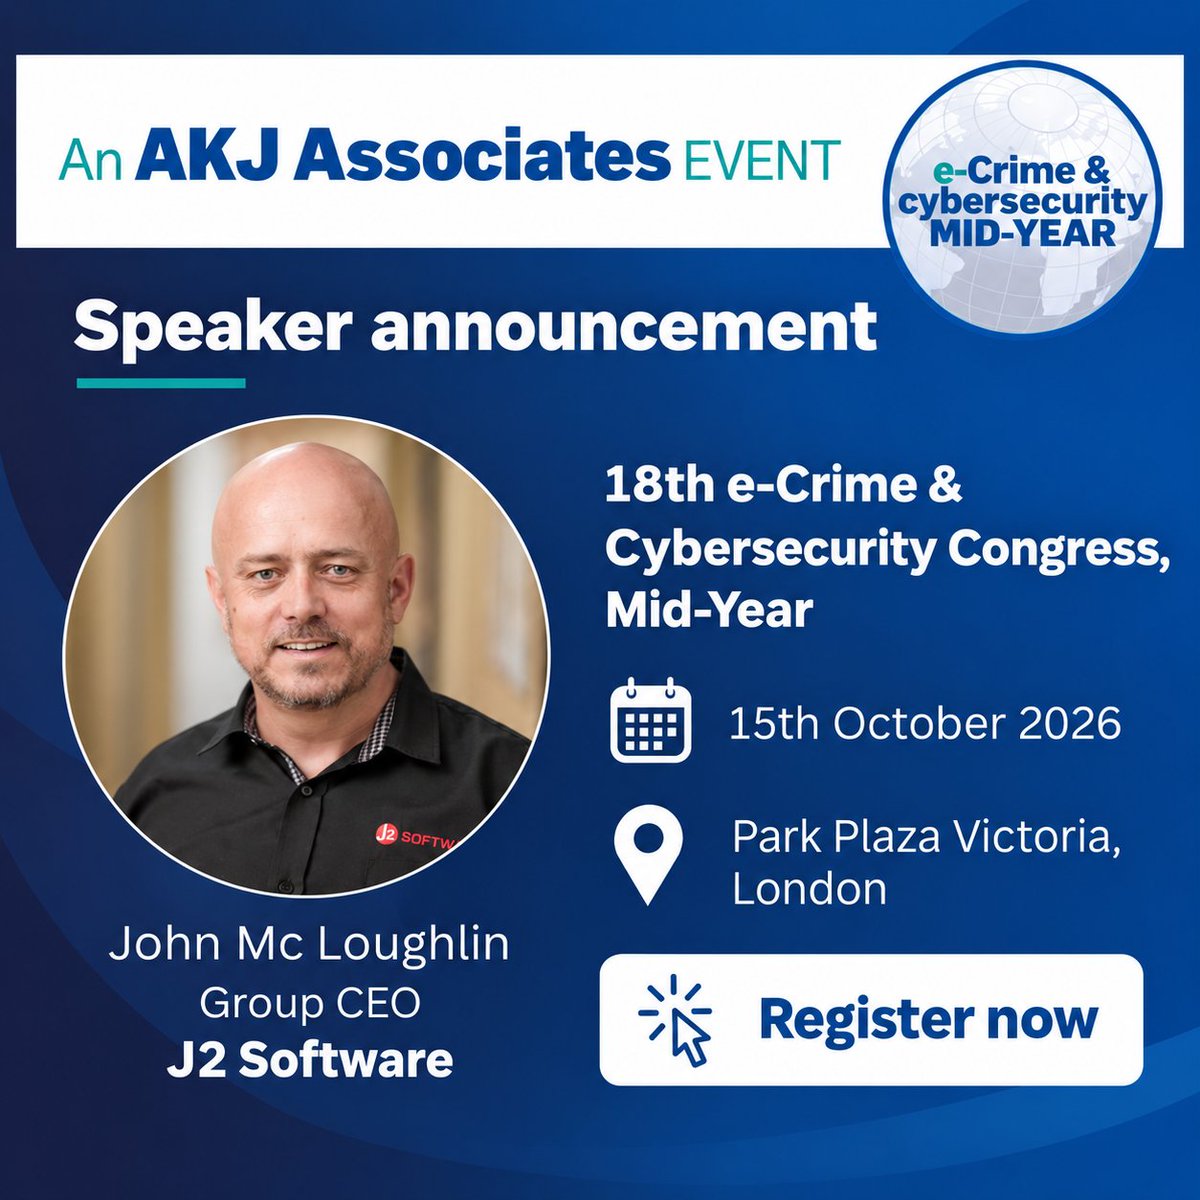
J2's CEO John McLoughlin is speaking in London this Thursday on:
The Million Dollar Conversation: What happens when the criminal isn't breaking into the conversation, they're already in it?
15 October, Park Plaza Victoria.
Book here:
https://t.co/bMkkdUQQkQ
John McLoughlin, Group CEO of J2 Software, is speaking at the 18th Annual e-Crime & Cybersecurity Mid-Year Summit in London this Thursday.
His session looks inside two real-world attacks where criminals quietly became part of legitimate business conversations.
Tomorrow, John McLoughlin from J2 will be exploring two real-world cases at the e-Crime & Cybersecurity Mid-Year Summit where criminals quietly inserted themselves into legitimate business conversations and millions were lost.
Book here:
https://t.co/bMkkdUQQkQ
We spend a lot of time asking whether criminals can get into our systems.
John McLoughlin is asking a different question this Thursday:
Would we know if the criminal was already inside a trusted conversation?
https://t.co/bMkkdURoao
#J2MSSP
Is this really about the weaponisation of food becoming a reality. Is this highlighting some failures in the supermarket cyber security and cyber resilience. Is blaming 'older models that can't be updated' really an excuse?
Ask the experts.
🌐 https://t.co/KsI4mvRJUa
Je condamne fermement la cyber attaque visant des produits alimentaires chez @intermarche@CooperativeU@Leclerc
La sécurité alimentaire nécessite plus d’attention à tous les niveaux. Car l’instrumentalisation de l'alimentation est devenue une réalité.
@UEFrance
Two real attacks.
$1.6m lost in one.
$4m plus personal director losses in another.
The criminals became part of legitimate business conversations and were not discovered until the money had gone.
John McLoughlin tells the story Thursday.
#J2MSSP#CyberResilience
John McLoughlin is speaking in London this Thursday on:
The Million Dollar Conversation: What happens when the criminal isn't breaking into the conversation, they're already in it?
15 October, Park Plaza Victoria.
https://t.co/bMkkdUQQkQ
#J2MSSP#eCrime
Would we know if somebody was using legitimate access for the wrong reason?
ASOS says the affected platforms were locked down and its website and app remained safe to use.
Walked in not hacked...
https://t.co/BDBAZTzNtM
#J2MSSP#CyberResilience
The account can be genuine.
The person using it may not be.
Left a door open?
That is why cyber security is not only about stopping break-ins. It is also about recognising when trusted access is being misused.
https://t.co/BDBAZTzNtM
#J2MSSP#CyberResilience