Need free data? Buy a cheap ledger off a dodgy seller, pull the sim out of the spy implant and enjoy while you can (law enforcement may visit you thinking you are the one making these).
https://t.co/ycMuv98UHh
Announcing dots. Dots work 24/7 for you, learn from your feedback, have their own computer, browser and can be connected to over 4k apps in our ecosystem.
They’re powered by Astra our best model yet. Included in your Pro plan, without drawing down on any of your usage. You can even call a dot while it’s working.
We’re getting you started with your primary dot today and soon you’ll be able to create entire teams of them.
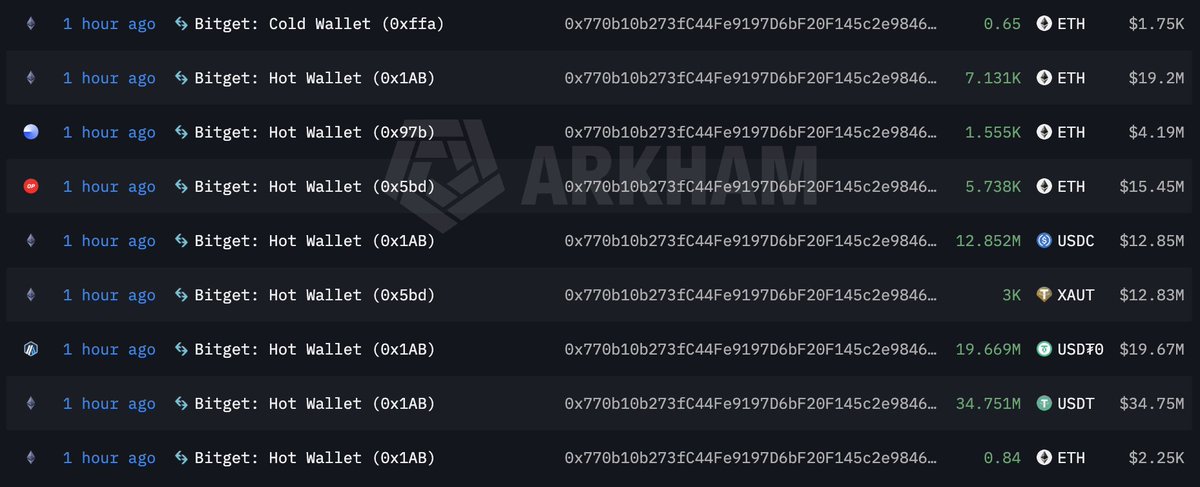
Bitget Wallets Suspected of Security Breach, Over $170M in Assets Moved and Swapped to ETH
Breaking: MLM monitoring indicates that Bitget may be experiencing an ongoing wallet security incident, with three hot wallets and one cold wallet suspected to have been compromised. More than $170 million worth of assets have reportedly been moved out and swapped into ETH, with activity linked to 0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee. The affected wallets are said to still hold about $530 million in assets. The attack vector and total losses remain unconfirmed, and Bitget has not yet publicly responded.
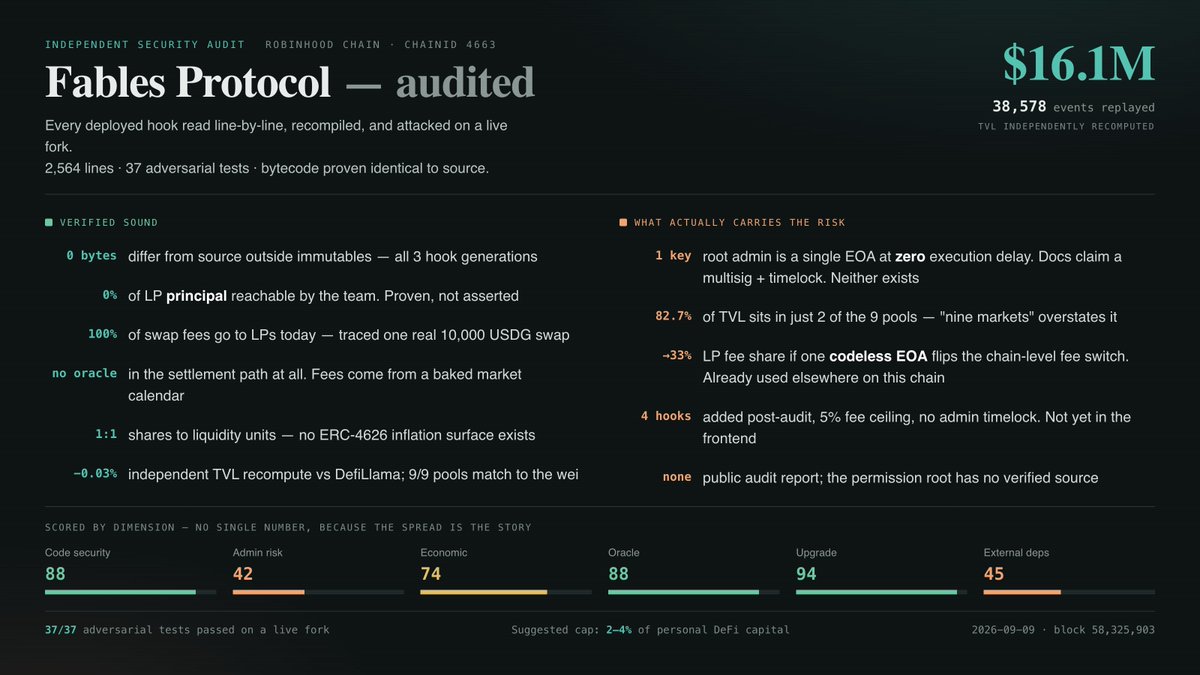
I spent a short auditing @fablesfi — the hook-native ve(3,3) DEX on Robinhood Chain — from scratch.
Not a checklist review. Every deployed hook read line by line, recompiled locally to prove the bytecode matches, then attacked on a live mainnet fork with 37 adversarial tests.
The short version: the contract engineering is genuinely better than most of what I review. What should worry you is almost entirely somewhere else.
Full breakdown 🧵
@RobinhoodCrypto $PROLOGUE #RobinhoodChain #DeFi #RWA #UniswapV4 #ve33 #SmartContractSecurity #DeFiSecurity #TokenizedStocks
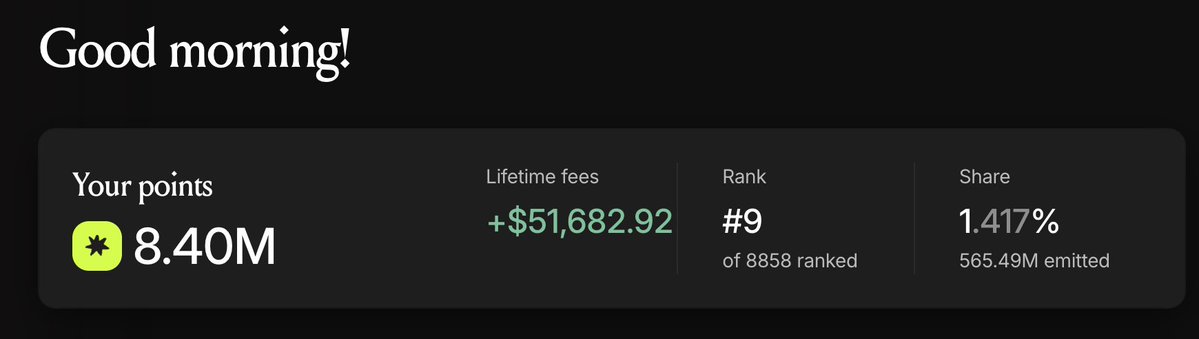
I was pretty late to deposit into @fablesfi, but I still managed to break into the top 10.
Here’s my lightweight audit of the project. The Fables founder @0xlayans also replied in the thread, outlining the improvements they plan to make.
Deposit now, and you’ll be eligible for rewards at TGE in less than two weeks.
Feel free to use my referral code:
https://t.co/O6Z8kWSxdG
@RobinhoodCrypto
robinhood:0xb9972ca7188e511174947e3936a5315ac7073277 #RobinhoodChain #DeFi #RWA
I spent a short auditing @fablesfi — the hook-native ve(3,3) DEX on Robinhood Chain — from scratch.
Not a checklist review. Every deployed hook read line by line, recompiled locally to prove the bytecode matches, then attacked on a live mainnet fork with 37 adversarial tests.
The short version: the contract engineering is genuinely better than most of what I review. What should worry you is almost entirely somewhere else.
Full breakdown 🧵
@RobinhoodCrypto $PROLOGUE #RobinhoodChain #DeFi #RWA #UniswapV4 #ve33 #SmartContractSecurity #DeFiSecurity #TokenizedStocks
NUSD and sNUSD holders may now submit redemption requests through the official Neutrl Redemption Portal subject to the applicable terms and conditions.
The Redemption Program provides NUSD and sNUSD holders with a fixed redemption rate based on Neutrl’s previously disclosed liquid reserves. Users who complete a redemption will receive USDC, and the corresponding NUSD or sNUSD will be burned.
To submit a redemption request, users must connect the wallet holding their NUSD or sNUSD and sign an onchain message to verify ownership of the wallet. The portal will provide the applicable redemption details before a redemption is submitted.
The Redemption Program is expected to remain open until 14 November 2026, subject to the applicable terms and conditions. Users are encouraged to carefully review the full terms and conditions available on the Redemption Portal before submitting a redemption request.
The redemption contract has been reviewed by a third-party security auditor. Users should verify that they are interacting only with the official Neutrl Redemption Portal URL before connecting a wallet, signing a message, or submitting a transaction.
https://t.co/mSGM8QxCX9
Disclaimer: Neutrl is operated by Caverna Auctus Inc. This communication contains forward-looking statements, including as to timing, amounts, and recovery outcomes, which are estimates only and subject to change without notice. Nothing herein constitutes a guarantee of any specific outcome, financial, investment, or legal advice, or an offer or solicitation with respect to any token. All rights reserved.
We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: https://t.co/0EJUnYEgfz
I'm deliberately not collapsing this into one number, because the spread is the finding:
Code security 88
Upgrade risk 94 hooks are immutable. No proxy, no beacon, no delegatecall
Oracle risk 88 there is no oracle to attack
Economic 74
External deps 45
Admin risk 42 one key, zero delay
Attacker holding no keys: I found no path to principal.
Malicious team: 0% of principal, up to 20% of fees.
Suggested cap if you LP here: 2-4% of personal DeFi capital.
I spent a short auditing @fablesfi — the hook-native ve(3,3) DEX on Robinhood Chain — from scratch.
Not a checklist review. Every deployed hook read line by line, recompiled locally to prove the bytecode matches, then attacked on a live mainnet fork with 37 adversarial tests.
The short version: the contract engineering is genuinely better than most of what I review. What should worry you is almost entirely somewhere else.
Full breakdown 🧵
@RobinhoodCrypto $PROLOGUE #RobinhoodChain #DeFi #RWA #UniswapV4 #ve33 #SmartContractSecurity #DeFiSecurity #TokenizedStocks
What actually carries the risk:
▸ The root admin is a single EOA with an EIP-7702 delegation, execution delay ZERO. It can grant itself every operations role in one transaction. I simulated it against live state and it succeeds. The docs' own role table says "Admin multisig, configured AccessManager delay." On chain it is neither a multisig nor delayed.
▸ The team clearly knows how to run a multisig: there's a 2-of-3 Safe. They use it to guard the rewards pot, not the protocol. That's a configuration choice, not a limitation. Two transactions would fix it.
▸ The finding I initially under-rated, then promoted: PoolManager.protocolFeeController resolves to an owner that is a CODELESS EOA. No multisig, no timelock, no relationship to Fables governance at all. At the v4 cap it takes 0.1% off every swap, cutting the LP fee share to 33-44%. This is not hypothetical. It is already switched on for another pool on this chain.
▸ Four new hooks were deployed after my audit began, now serving 13 pools, with a 5% fee ceiling (2.5x the audited ones) and, verified today, no AccessManager admin timelock at all, where the nine audited hooks have 3600s. They hold only team seed capital and the frontend doesn't list them. Yet.