¿Recuerdan REA, el proyecto que hacía ingeniería inversa a cualquier cosa?
Un agente de IA al que le dabas un binario, una app de Electron o un programa compilado, y te devolvía el código. En la práctica significaba que cualquier programa que exista podía ser destripado y reconstruido. Bueno, acaba de llegar su antídoto.
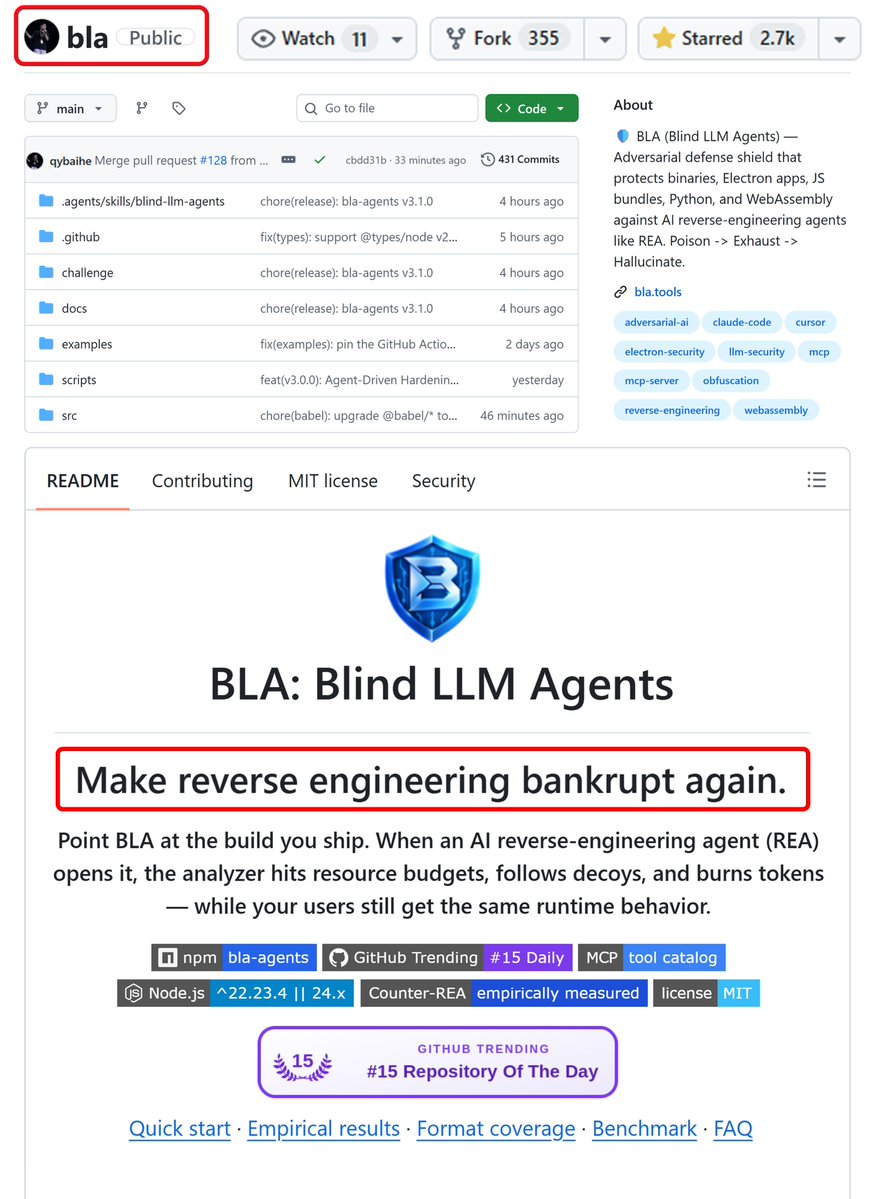
Se llama BLA, Blind LLM Agents, y pasó de 0 a casi 4,000 estrellas en GitHub en mes y medio. La idea es simple: en vez de ocultar tu código, envenenas el análisis. Siembra claves falsas, lógica señuelo y trampas de recursos dentro de tu build. El usuario normal no nota nada; el agente de IA que intenta destripar tu app quema tokens siguiendo pistas falsas, hasta que termina “entendiendo” algo que no existe.
Según el proyecto, el atacante gasta entre 300 y 2,800 veces más tokens. Son cifras propias, nadie las ha verificado todavía. Pero la señal es clara, la ofuscación clásica ya no alcanza; ahora proteges tu código pensando en cómo lee una IA
Es open source, MIT, y está en GitHub https://t.co/cjfK1qqRAs
REA (reverse engineer anything) - F*CKED by chinese student...
solo dev just dropped protection for your app & site & game from reverse-engineering and AI hackers, for free
REA not dangerous anymore.
here's how to use and setup BLA (Blind LLM Agents):
first understand how it works:
• REA opens your app in 1 command, BLA hides traps inside it before you ship
• fake keys and decoy code for AI to chase, plus files built to blow past REA's own limits
• AI burns tokens on dead ends, your users get the exact same app
here's how to set it up for FREE:
1 → open Claude Code in the folder of your app, site or game
2 → say: " install Node.js 24 if I don't have it, build my project, then run npx bla-agents setup and npx bla-agents harden"
3 → it finds your build itself: dist, build, Electron .asar, .wasm, Python, native binaries
4 → it plants fake keys and decoy code, then checks every protected file still runs the same
5 → the step everyone skips: ship the files from the new .bla-hardened folder, not your old build
6 → for sites it protects the JS your site sends to browsers, your server code never leaves your server anyway
7 → want proof? run: npx bla-agents benchmark - before vs after on 14 test apps
paste link on repo below as soon as possible:
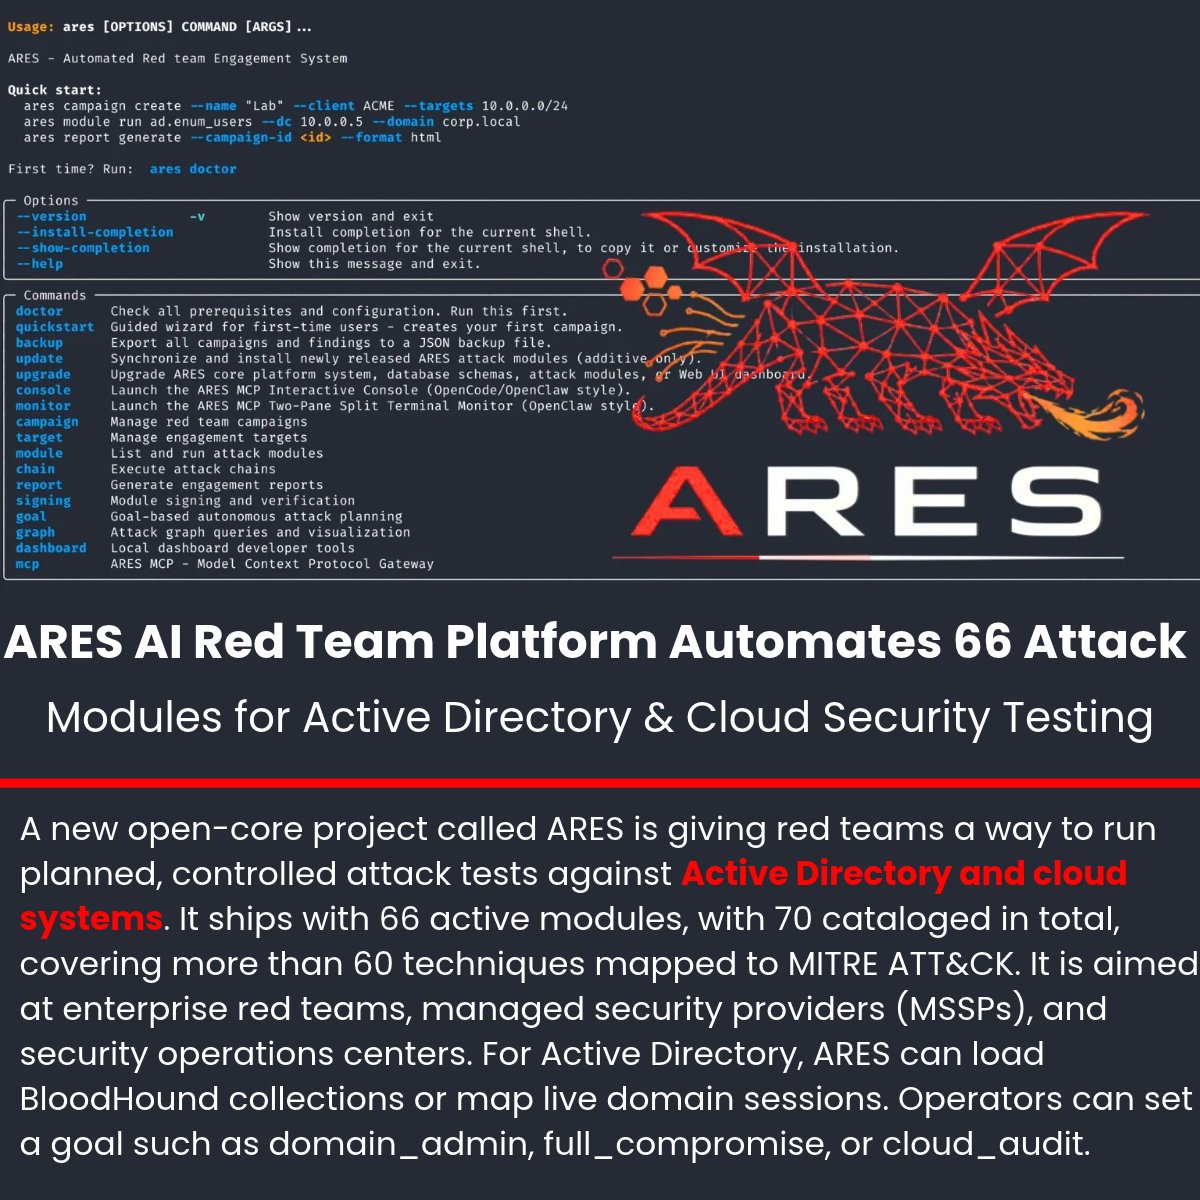
🛡️ ARES AI Red Team Tool Automates 66 Attack Modules for Active Directory & Cloud Security Testing
Details: https://t.co/YAyhduYQAb
A new open-core project called ARES is giving red teams a way to run planned, controlled attack tests against Active Directory and cloud systems.
It comes with 66 active modules, with 70 cataloged in total, covering more than 60 techniques mapped to MITRE ATT&CK. It is aimed at enterprise red teams, managed security providers (MSSPs), and security operations centers.
For Active Directory, ARES can load BloodHound collections or map live domain sessions. Operators can set a goal such as domain_admin, full_compromise, or cloud_audit.
#cybersecurityNews
this is getting f*cking dangerous...
REA creator just dropped 20 GitHub repos to build a f*cking reverse engineering studio:
[01] analysis core
> REA: a single MCP that plugs into everything https://t.co/78k8zO6CUv
> Ghidra: decompiler, free https://t.co/T4UwApebCS…
> GhidraMCP: lets your agent drive Ghidra https://t.co/TJhvovWOVJ…
> ida-pro-mcp: hooks your agent into IDA Pro https://t.co/xm7FUywscM…
[02] mobile & apps
> jadx: turns Android APKs back into Java https://t.co/E4Yg0NKeQN
> Apktool: take APKs apart and put them back together https://t.co/Dx5Mxj6Xst…
> Frida: hook into apps while they run https://t.co/J7VPj371J9
> ILSpy: decompiles .NET https://t.co/dbnyEBZMSU…
[03] binary & low-level
> radare2: RE framework that lives in your terminal https://t.co/0zjfDIkiTm…
> x64dbg: debugger for Windows https://t.co/D4fskuXqhJ
> ImHex: hex editor with its own pattern language https://t.co/tRLAMVCOH4
> angr: symbolic execution engine https://t.co/GNA0rXyuu7
[04] network & runtime
> mitmproxy: sits in the middle and reads the traffic https://t.co/aexBKlRIPt…
> dnSpy: debug and edit .NET apps https://t.co/5VMhkWlxSS
> rizin: the radare2 fork https://t.co/V0eGBoTMBY
> raddebugger: the debugger from Epic Games https://t.co/UR4huJ2fEn…
[05] rebuild & verify
> awesome-ai-reverse-engineering: 122 repos, every one graded https://t.co/nnfVgcjPyD…
> awesome-reverse-engineering: curated by the guy who made REA https://t.co/psahTNrb0m…
> REA workflows: ready-made investigation prompts, ship with REA
> clean-room loop: SPEC.md, oracles and checks until it matches
how it runs: binary -> REA -> SPEC.md -> rebuild -> oracle -> retry
save this, point it at any app and watch it explain itself.
🦆⌨️🛡️ DucKeyLogger | Rubber Ducky + keylogger PowerShell a Telegram
Keylogger stealth que captura teclas, las ofusca con GZip + Base64 y las envía a un bot de Telegram.
Herramienta educativa para red team y concienciación en entornos autorizados.
#ciberseguridad#redteam
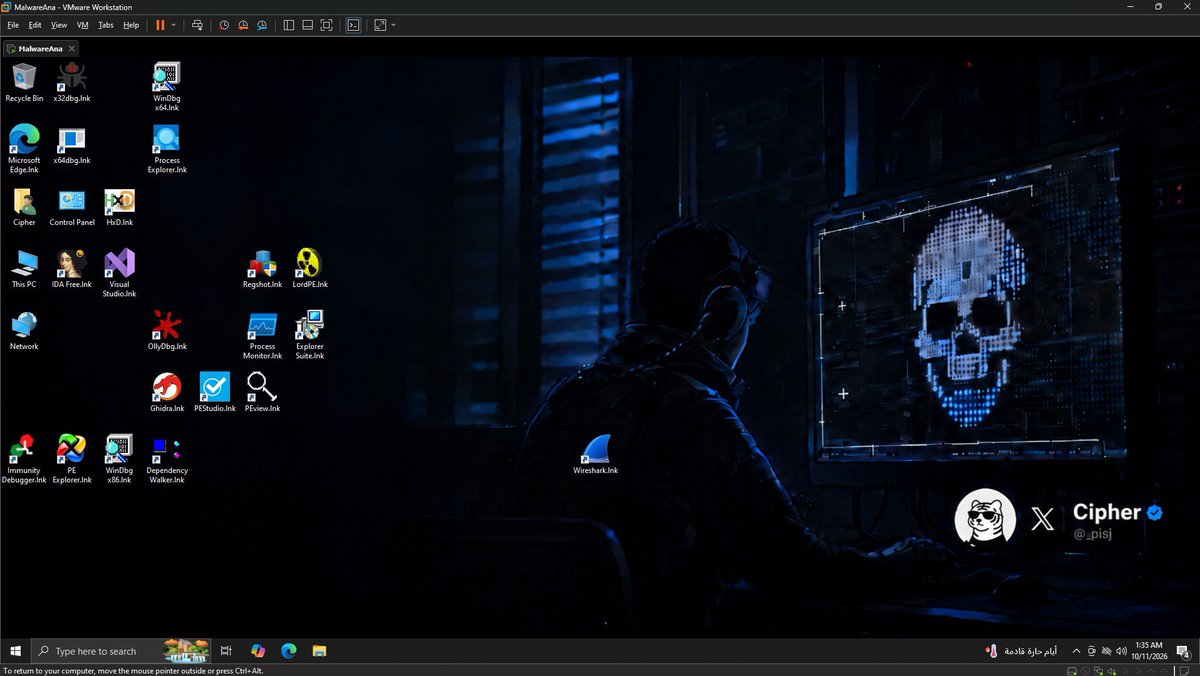
حاليًا أشتغل على بيئة Malware Analysis
بيئة Windows 10 مخصصة لتحليل الـ Malware، طورتها وجهزتها بمجموعة من الأدوات اللي يحتاجها المحلل في Malware Analysis وReverse Engineering وDebugging وDynamic Analysis
الهدف إن تكون بيئة جاهزة للاستخدام على VM وتختصر وقت تجهيز الأدوات من الصفر
باقي بعض اللمسات وبشارككم النسخة قريب بإذن الله
🚨 DEJA DE PAGAR PHOTOSHOP... ESTA ALTERNATIVA ES GRATIS Y PESA SOLO 11 MB
Un desarrollador se cansó de pagar Photoshop y creó su propia alternativa.
Es open source: cualquiera puede descargarlo, modificarlo y adaptarlo a su forma de trabajar.
Se llama Compositor y ya supera las 8.000 estrellas en GitHub.
Tiene lo que más usas de Photoshop:
→ Capas, máscaras y modos de fusión
→ Relleno según el contenido
→ Seleccionar sujeto y quitar fondo
→ Filtro Camera Raw
→ Pincel corrector y tampón de clonar
Sin suscripción. Sin pagarle a Adobe cada mes.
Te dejo el repo abajo 👇
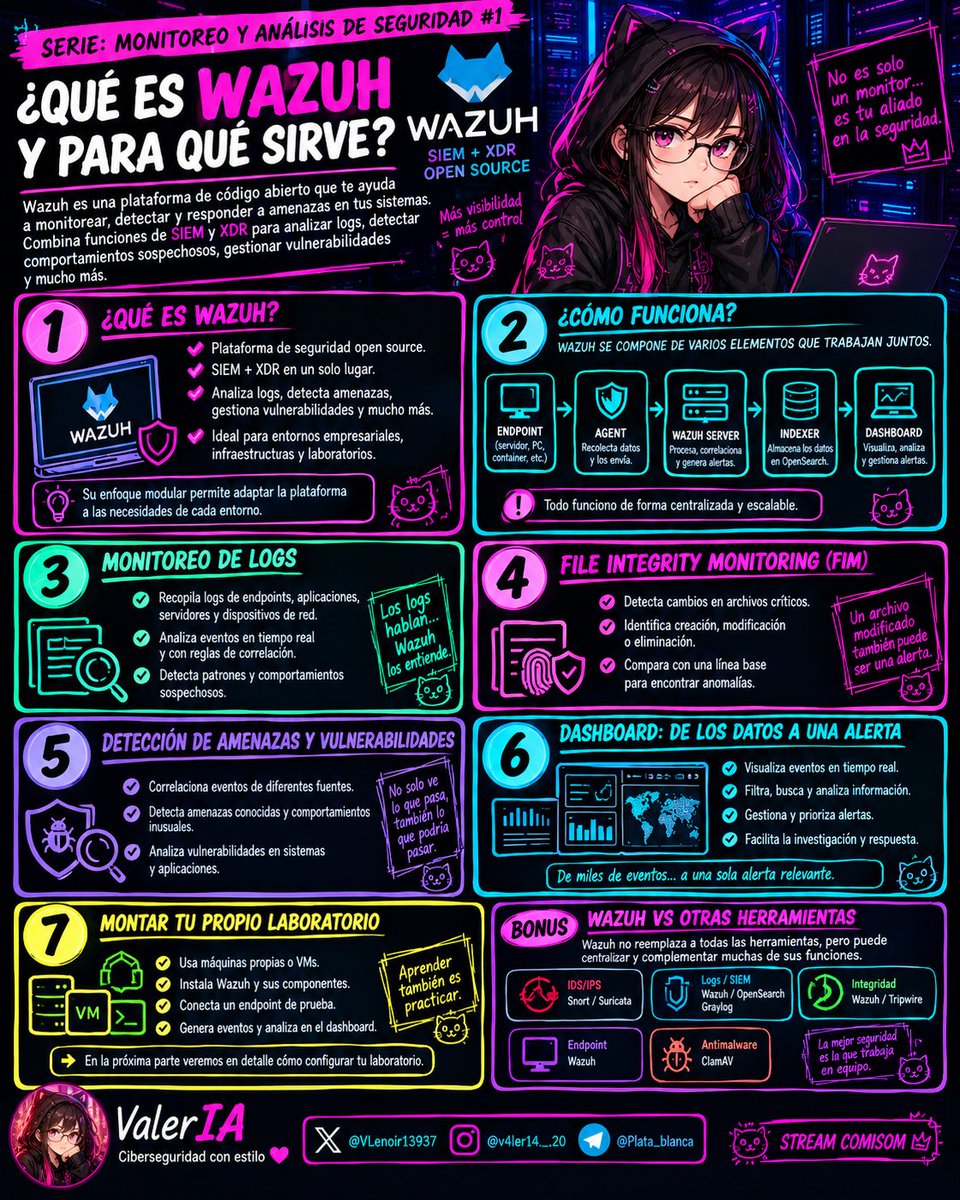
¿Has visto esas herramientas que parecen tener medio centro de seguridad dentro? 👀
Hoy empezamos una nueva serie con Wazuh: una plataforma open source que reúne capacidades de SIEM + XDR para monitorear, detectar y analizar lo que ocurre en nuestros sistemas.
#Ciberseguridad #Wazuh
🚨 ويندوز يشغل أكثر من 200 خدمة في الخلفية وأغلبها لا تحتاجه أصلا
تستهلك المعالج والذاكرة وتجمع بيانات عنك وتبطئ جهازك بدون أن تشعر
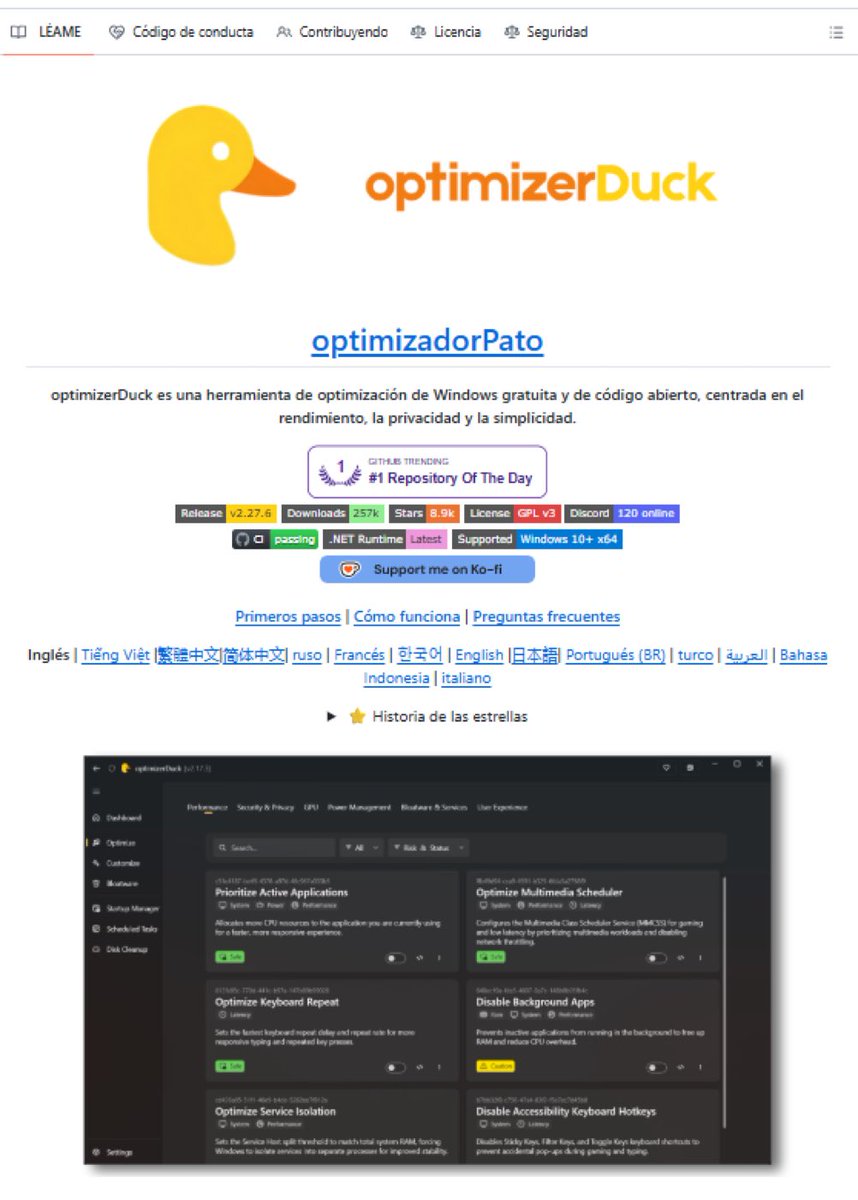
مطور قرر إنهاء هذه المشكلة وصنع optimizerDuck وهي أداة مجانية مفتوحة المصدر لويندوز 10 و11
⚙️ ماذا تفعل:
▫️ أكثر من 35 تعديلا للأداء والخصوصية والبطارية
▫️ تحكم في أكثر من 200 خدمة مع توضيح درجة الخطورة لكل واحدة
▫️ حذف البرامج المثبتة مسبقا مع معاينة قبل الحذف
▫️ تحسينات لكروت شاشة AMD وNVIDIA وIntel
🔄 والأهم أن كل تغيير يمكن التراجع عنه لأنها تنشئ نقطة استعادة إجباريا وملف تراجع لكل تعديل
بدون تثبيت وبدون إعلانات وبدون تتبع وبدون نسخة مدفوعة وتعمل بدون إنترنت
جهازك القديم يستحق فرصة ثانية 😉
10 GITHUB REPOS FOR PEOPLE WHO WANT TO BUILD LIKE A CYBERSECURITY ENGINEER.
1. Velociraptor — hunt for threats across endpoints.
https://t.co/mJtbpgIZm0
2. osquery — turn your machines into queryable security data.
https://t.co/GoWsLLbD3F
3. Sigma — write detection rules that work across security tools.
https://t.co/SFeRcd0M0S
4. YARA — identify and classify malware by patterns.
https://t.co/mhk4LAx8m1
5. Zeek — powerful network security monitoring.
https://t.co/bkS73AWn4s
6. Suricata — open-source network threat detection engine.
https://t.co/HAtEVvF9uj
7. MITRE ATT&CK — map real-world adversary tactics and techniques.
https://t.co/8oNH7EGTi6
8. TheHive — collaborative incident response platform.
https://t.co/n7fV8ol4Zo
9. MISP — share, store and correlate threat intelligence.
https://t.co/rD3kINMNEa
10. SpiderFoot — automate open-source intelligence gathering.
https://t.co/3hYACJugSv
All are open-source.
Bookmark this. Cybersecurity gets way more interesting when you can actually build with the tools.
سيبرانيين 👨💻
أداة ممتازة لمتخصصين #DFIR
والتحقيق الرقمي،
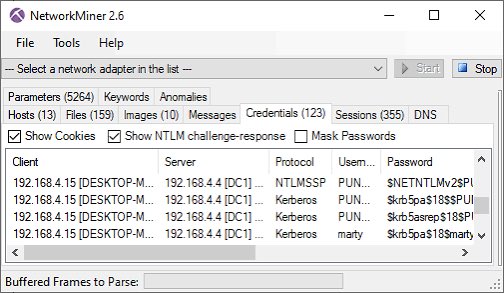
🔎 #NetworkMiner
تساعدك في تحليل
الـNetwork Traffic
واستخراج المعلومات
من ملفات الـPCAP
بدون الحاجة لتحليل كل #Packet يدويًا.
تقدر تستخرج منها
Files, Credentials, Hosts,
Sessions
وDNS وغيرها من البيانات،
وتفيدك في تتبع الاتصالات
وفهم وش صار داخل الشبكة أثناء التحقيق. 🕵️♂️🛡️
🔗 https://t.co/xoAwEMhkgA
#DFIR #CyberSecurity
10 GITHUB REPOS BRINGING AI INTO CYBERSECURITY
AI isn't just changing how we build software.
It's also changing how security teams find, test and fix vulnerabilities.
1. PentestGPT
AI assistant for reasoning through penetration testing workflows and findings.
https://t.co/9ZcItviCti
2. Caido
Modern toolkit for intercepting and analyzing web traffic during security research.
https://t.co/E2yv2L2Jge
3. HexStrike AI
Connect AI agents with cybersecurity tools through an MCP-based framework.
https://t.co/wVj3W9dqJ2
4. Strix
AI-powered security testing for investigating applications and finding vulnerabilities.
https://t.co/xlYhXK5975
5. Nuclei
Fast, template-based vulnerability scanner for applications and infrastructure.
https://t.co/Vr7yol06Oq
6. Semgrep
Code-aware security scanning that helps catch vulnerabilities before deployment.
https://t.co/UXshu3HJIF
7. Gitleaks
Find exposed API keys, passwords, tokens and other secrets in Git repositories.
https://t.co/gzbcvI0c3R
8. OWASP Amass
Discover domains, subdomains and infrastructure to understand external attack surfaces.
https://t.co/xpX7sLwzf2
9. Wazuh
Open-source platform for security monitoring, detection, vulnerability management and log analysis.
https://t.co/KzY46IlhYq
10. Prowler
Assess cloud environments against security best practices and compliance frameworks.
https://t.co/JYRDnoAogJ
Save these repos if you're exploring AI-powered cybersecurity.
🚨 WINDOWS EJECUTA MÁS DE 200 SERVICIOS EN SEGUNDO PLANO Y LA MAYORÍA NO LOS NECESITAS
Gastan recursos, recopilan datos y mantienen activas funciones que probablemente nunca has usado.
Alguien se cansó y creó optimizerDuck: una herramienta gratis y open-source para Windows 10 y 11.
Esto es lo que hace:
→ más de 35 ajustes de rendimiento, privacidad, batería y sistema
→ control de más de 200 servicios, etiquetados por nivel de riesgo
→ eliminación de bloatware con vista previa antes de borrar nada
→ optimizaciones para GPUs AMD, NVIDIA e Intel
→ todos los cambios se pueden revertir
Y lo mejor: antes de tocar nada te obliga a crear un punto de restauración y genera archivos para deshacer cada ajuste.
Sin instalador, sin anuncios, sin telemetría y sin versión premium. Funciona incluso sin conexión.
Repo en comentarios 👇
اكتشفت كنز مدفون على GitHub 💎
أول ما جربته قلت:
أنا ليه كنت بدفع لـ YouTube Premium؟ 😂
اسمه Invidious… وغيّر لي طريقة استخدام يوتيوب تمامًا:
🚫 بدون إعلانات
🔐 بدون حساب Google
👀 بدون تتبّع
📥 تستورد كل اشتراكاتك دفعة وحدة
🖥️ وتقدر تستضيفه بنفسك وتتحكم فيه بالكامل
والأغرب؟ 👀
مفتوح المصدر + مجاني = 0€ شهريًا. 💸
يعني بدل ما تدفع كل شهر، عندك مشروع مفتوح المصدر تقدر تشغله بنفسك.
حسّيت إني لقيت كنز وقلت لازم أطلّعه لكم 😂💎
حطيت الرابط في أول تعليق… لا تفوّتونه 👇🏼
🚨 Phishing Awareness in 30 Seconds
A quick look at how phishing campaigns can use convincing email and social-engineering tactics. 📧🔐
Learn the red flags. Verify before you click. 🛡️
#PhishingAwareness#CyberSecurity#EmailSecurity#InfoSec