Last week @KatNovakovic and I represented @Citi at @openuk_uk State of Open Con '24. Elizabeth Lumley, Deputy Editor of @TheBanker (@FT), said "I'd never heard a case study from a bank presented with such clarity and transparency before".
🎥 Watch it now:
https://t.co/oUtIjs19QA
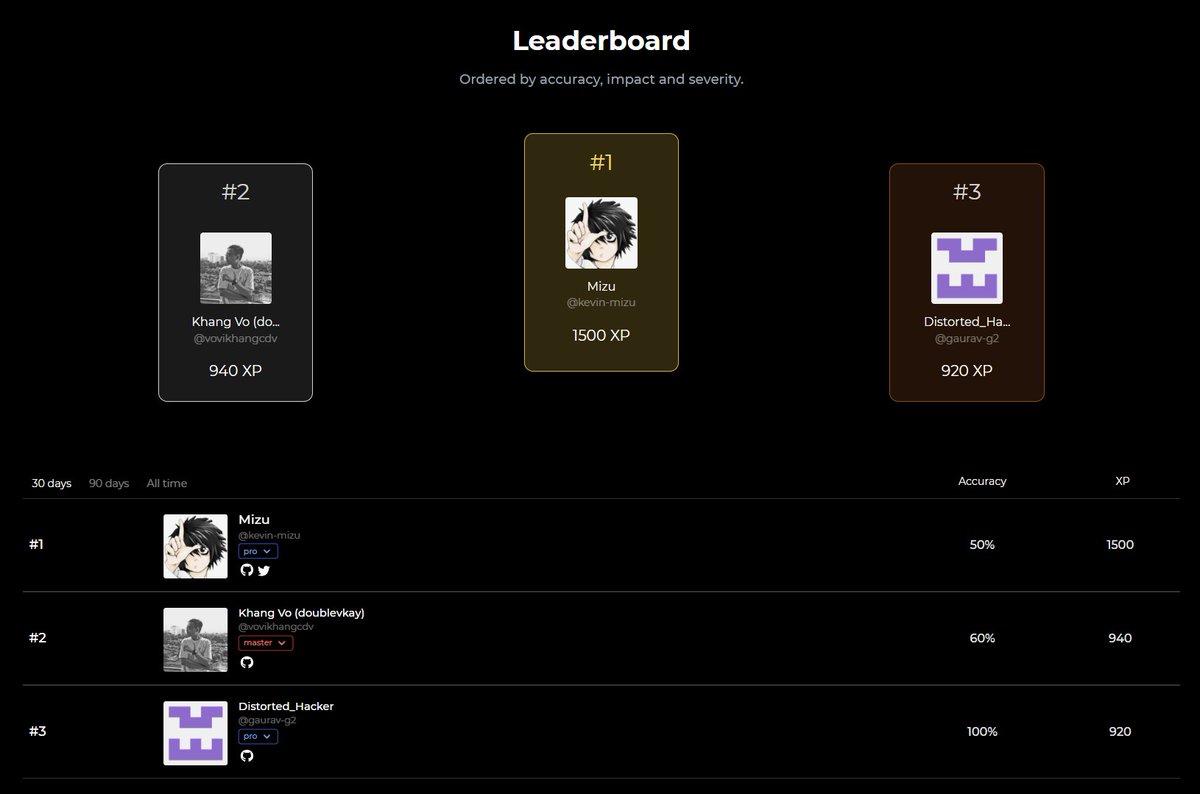
I have submitted 18 reports, 9 validated, and 4 CVEs in a month. Just small things for the beginning, but yeah, glad that I end up at the #top2 leaderboard (30 days) on @huntrdev. Appreciate the #CodeQL help!
Wish you all happy hacking!😁
Welcoming @getoutline to https://t.co/yT0C1APRvB 🤝
With up to $2000 in rewards per vulnerability, and a super-responsive maintainer (@tommoor ♥️), this is a bug bounty programme you won't want to miss.
Report now:
https://t.co/L8KAfdTcoi
I have found a high severity vulnerability in @momentjs - one of the most depended-upon packages on @npmjs.
The vulnerability has been found with CodeQL, reported on @huntrdev. It is also my first #CVE, first #bugbounty, and the first GHSA credit.😄
https://t.co/c50sBmi5Ts
Learn about Unverified Password Changes and how you can snag quick vulnerabilities in web applications. Plus, see how you can go through the process of submitting your first bug on @huntrdev
https://t.co/0BpLVwKNMF
It’d be kind of cool if someone consolidated CVEs / writeups by the language used to write the software. Like on https://t.co/GtWtmy6lVp you can search for reports on repos that use c, python, golang etc. maybe this is already a thing and I don’t know?
When @drawio says security-first, they mean it. Read through one of our latest write-ups for an Arbitrary Code Execution Through Sanitizer Bypass, fixed by @davidjgraph:
https://t.co/VuIZSD8P1E
+50 FOSS projects have been added to our bug bounty program:
✅ Rewards up to a mega-$1200
✅ Rewards for maintainers (always)
✅ Expanding our pledge for a sustainable open source ecosystem
New projects include @junitteam@Google@kotlin@EclipseFdn@TheASF + more...