They broke a 66-year-old algorithmic barrier.
Dijkstra still ran up to four times faster.
In 2025, researchers beat Dijkstra’s asymptotic bound for sparse directed graphs by escaping its hidden sorting cost. Then another team implemented the breakthrough and tested it on graphs with ten million vertices.
Dijkstra won.
The recursion cost more than the sorting it removed.
Big O wasn’t wrong. It simply answered a different question from the one production systems face. A better complexity class does not automatically mean faster software.
Before shipping your next optimization, ask: faster under whose assumptions?
Hey @X algorithm
Looking to #connect with people interested in:
- Full Stack
- DevOps
- AI Tools
- AI Security
- Vibe Coders
- SaaS
- Startups
Say hi & let's grow together
Microsoft didn’t upload 38 terabytes of private data to GitHub.
It uploaded permission to reach it.
In 2023, researchers at Wiz discovered a GitHub link shared by a Microsoft AI researcher. Hidden inside the Azure URL was an overly permissive SAS token.
According to Wiz, that single link exposed workstation backups, passwords, secret keys, and more than 30,000 internal Teams messages.
The token even included write permissions.
There’s no evidence the exposed files were altered or deleted before Microsoft revoked the token. But the incident reveals a dangerous blind spot:
We inspect the content we share.
We rarely inspect what our links can unlock.
Before you paste a cloud URL into GitHub, Slack, an AI tool, or a support ticket, ask:
What access is leaving with it?
Code Smart. Prompt Secure.
https://t.co/5Mb0gq1SyE
Anthropic just walked away from a $6 billion acquisition of Decart.
8x faster inference. 100-person team. Nvidia-backed.
And they still said no.
Here's what nobody is talking about:
As AI inference gets 8x faster - developers will use AI tools 8x more.
More AI usage = more prompts = more credentials accidentally pasted into models.
Speed is incredible.
But the security gap grows with it.
While Anthropic prepares for IPO - developers are still pasting API keys into Claude every single day.
SecureIntent catches every one of them. 🔒https://t.co/5Mb0gq2qoc
#Anthropic #Decart #AI #DevSecurity #Developers #infosec
One leaked credential.
One autonomous AI agent.
Six steps to a full attack chain.
The scary part? The agent didn’t need an attack plan. It built one itself.
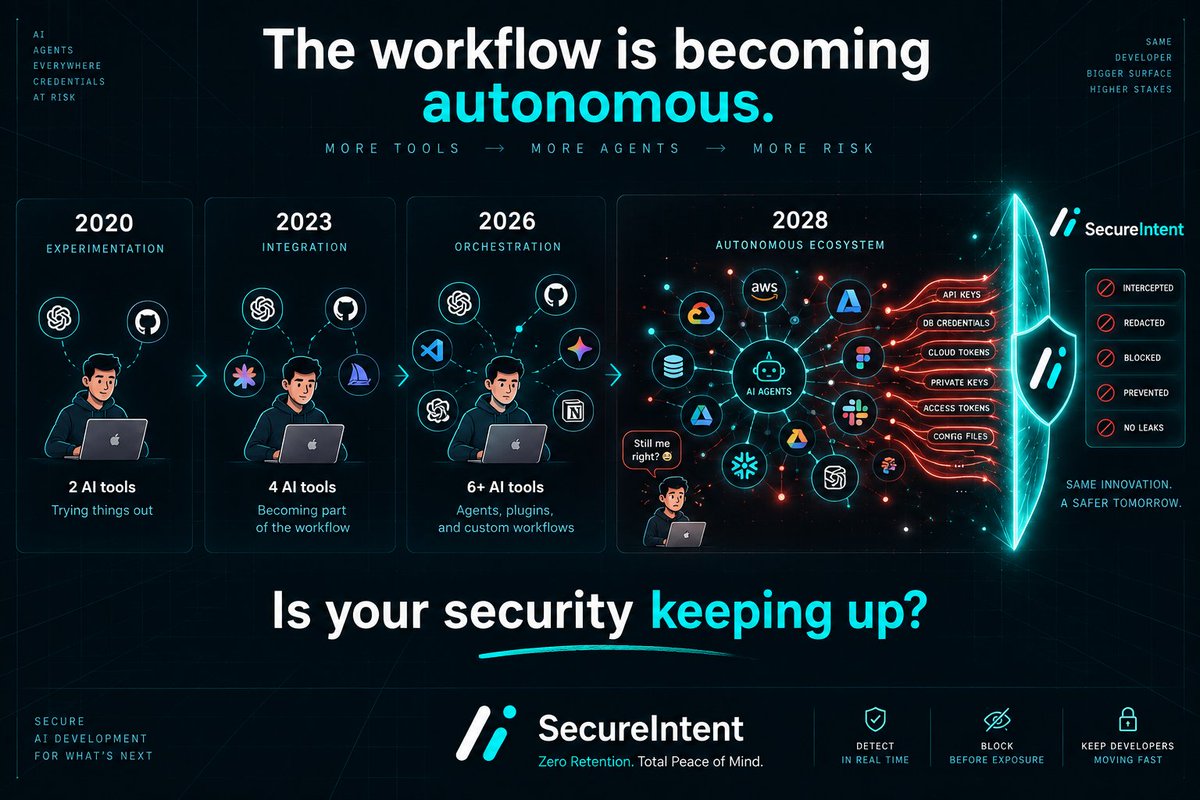
In 2020, the average developer used 2 AI tools.
In 2026, it's 6+.
By 2028, your IDE won't just suggest code.
It will autonomously open PRs, deploy to production, provision infrastructure, and call external APIs - all without you touching a keyboard.
Every one of those actions requires a credential.
Every credential is a potential breach.
The attack surface isn't growing linearly. It's compounding.
The question isn't whether agentic AI will be part of your workflow. It already is.
The question is whether your security posture is keeping up.
SecureIntent + Firefox 🦊
LIVE.
Another browser.
Same mission.
Keep sensitive data where it belongs - even when you're moving fast with AI.
Try it and tell us what you think. 🔐
Built an AI-powered digital clinic platform for @emergentlabs BuilderFest 🚀
AI notes, online booking, payments, invoicing & team access, all in one place.
Check it out and drop an upvote 👇
https://t.co/5H0L9n1jyE
#emergent#builderscontest@emergentlabs
Developers don't leak secrets because they're careless.
They leak secrets because their tools make it too easy.
Copy a connection string to debug an issue -> paste it into ChatGPT -> problem solved -> secret exposed.
The workflow made sense in the moment. The security team finds out six months later.
This isn't a people problem. It's a tooling problem.
SecureIntent is the missing layer between how developers actually work and how security teams need them to work.
Silent. Automatic. Zero friction.
Install it once. Never think about it again.
🔗 https://t.co/5Mb0gq2qoc
Built an AI-powered digital clinic platform for @emergentlabs BuilderFest 🚀
AI notes, online booking, payments, invoicing & team access, all in one place.
Check it out and drop an upvote 👇
https://t.co/5H0L9n1jyE
#emergent#builderscontest@emergentlabs
Every year, developers ship faster.
Every year, secrets sprawl faster than that.
GitGuardian's 2026 report found 28.65 million hardcoded secrets in public GitHub commits last year alone. A 34% increase.
The largest single-year jump ever recorded.But the number isn't even the scary part.
The scary part is what happened to the threat model.
Frontier agentic AI has removed the human bottleneck that used to make old leaked credentials "safe by obscurity." A secret sitting dormant in a two-year-old commit can now be discovered, classified, and weaponized - autonomously, in minutes.
64% of secrets leaked in 2022 are still valid today. They were always exploitable. Now they're instantly exploitable.
The credential you forgot about is the one that will get you.
SecureIntent intercepts secrets before they leave your machine. Before they reach a repo. Before they reach an AI tool. Before they become a durable path that an autonomous agent can exploit.
The only secret that can't be weaponized is one that was never exposed.
🔗 https://t.co/5Mb0gq2qoc
We're building SecureIntent with you. 👋
Join our first ever Customer Advisory Board Meeting - and we want YOU in the room.
📅 Thu, Aug 13, 2026
⏰ 9:30pm – 10:00pm IST
💻 Online on Google Meet
What's in it for you?
- Share feedback directly with our team
- Get early access to new features
- Help shape the SecureIntent roadmap
- Connect with a community of developers
Your feedback. Our roadmap. Let's build a secure future together.
Link - https://t.co/SmZoswIDRI
What if you could debug with AI without ever leaking a credential?
That's why we made SecureIntent.
The first browser-level extension that intercepts secrets before they reach any AI model.
Just install it. It does the rest.
And we're just getting started -
- Mozilla Firefox extension coming soon
- Desktop app launching soon
One tool. Every platform. Zero leaks.
https://t.co/5Mb0gq2qoc
383 developers. 59 ratings. 4.9 stars. ⭐
When we started, we had one goal:
Make sure no developer ever has to go through the panic of a credential leak again.
383 developers later - we're just getting started. 🙏
Thank you for trusting SecureIntent with your most sensitive data.
If you haven't tried it yet - now's the time.
Link in replies .
Hot take:
Your security team can't protect you from yourself.
They can:
✔️ Block malicious IPs
✔️ Monitor network traffic
✔️ Enforce access controls
✔️ Scan for vulnerabilities
They can't:
❌ Stop you from pasting your DB password into ChatGPT at 2am
❌ Prevent your AI agent from committing .env files
❌ Intercept credentials before they leave your browser
The biggest security gap in 2026 isn't your infrastructure.
It's the 2 seconds between copying a secret and pasting it somewhere it shouldn't go.
🏡 Rooms Available – Open Viewings This Week! 🏡
Looking for a great place to live? We have a modern ensuite room & a spacious double room available! ✅ Great location ✅ Comfortable & well-maintained ✅ Ideal for professionals
#LondonRentals#RoomToRent
https://t.co/FONNJA3Qo2