🇸🇬 Our OSINT Masterclass is coming home — to #Singapore.
After taking the series across the region, we're hosting this one on home ground. StealthMole's free, invitation-only OSINT Masterclass is built for government cybersecurity practitioners, incident response, intelligence, and financial-crime teams — and it's a hands-on working session, not a lecture.
Led by Louis Hur, Founder & CEO of StealthMole, you'll watch a live dark web investigation on real APAC threat data — threat-actor profiling, Telegram and dark web forum cross-tracking, and a demo of our newly launched tracking module — then go hands-on to check your own agency's exposure, with our engineers right beside you.
📅 Thursday, 10 September 2026
🕑 2:00 – 5:00 PM SGT (3 hours)
📍 AirView Building, #02-01, 2 Peck Seah Street — 5-min walk from Tanjong Pagar & Maxwell MRT
What you'll walk away with:
✅ A 1-month StealthMole license
✅ A live, real-data investigation you won't see in any webinar
✅ Hands-on time to assess your agency's actual exposure
🍕 Pizza and refreshments afterward for casual networking
Conducted in English. Seats are limited to 20, and as this is an invitation-only session for government agencies, please register using your official government email.
👉 https://t.co/pjcu53FRmd
#OSINT #DarkWebIntelligence #Cybersecurity #IncidentResponse #StealthMole #ThreatIntelligence
🌍 Ransomware is a global threat.
Over the years, 180+ countries and territories have had organizations listed on dark web ransomware leak sites after their data was stolen.
This chart highlights the top 50 affected countries, along with the overall global distribution of ransomware leak victims.
The data clearly shows that while the United States accounts for nearly half of all published victims, ransomware operations have impacted organizations across virtually every region of the world.
#Ransomware #DarkWeb #CyberSecurity #ThreatIntelligence #DataBreach #OSINT #StealthMole
We’re proud to be a Bronze Sponsor of SINCON 2026.
Join one of Singapore's leading cybersecurity conferences, where industry experts, practitioners, and the community come together to learn, collaborate, and share ideas through inspiring keynotes, technical talks, hands-on workshops, and interactive Kampungs.
Enjoy S$150 OFF your SINCON 2026 Full Conference Pass with the following discount code:
🎟️ CODE: SINCON26-SPONSOR
🔗 Get your tickets here: https://t.co/N0XSTQV5qH
📅 15–16 October 2026
📍 voco Orchard Singapore
We hope to see you there!
#SINCON2026 #InfosecIntheCity #SINCON #CybersecurityConference #CybersecuritySG
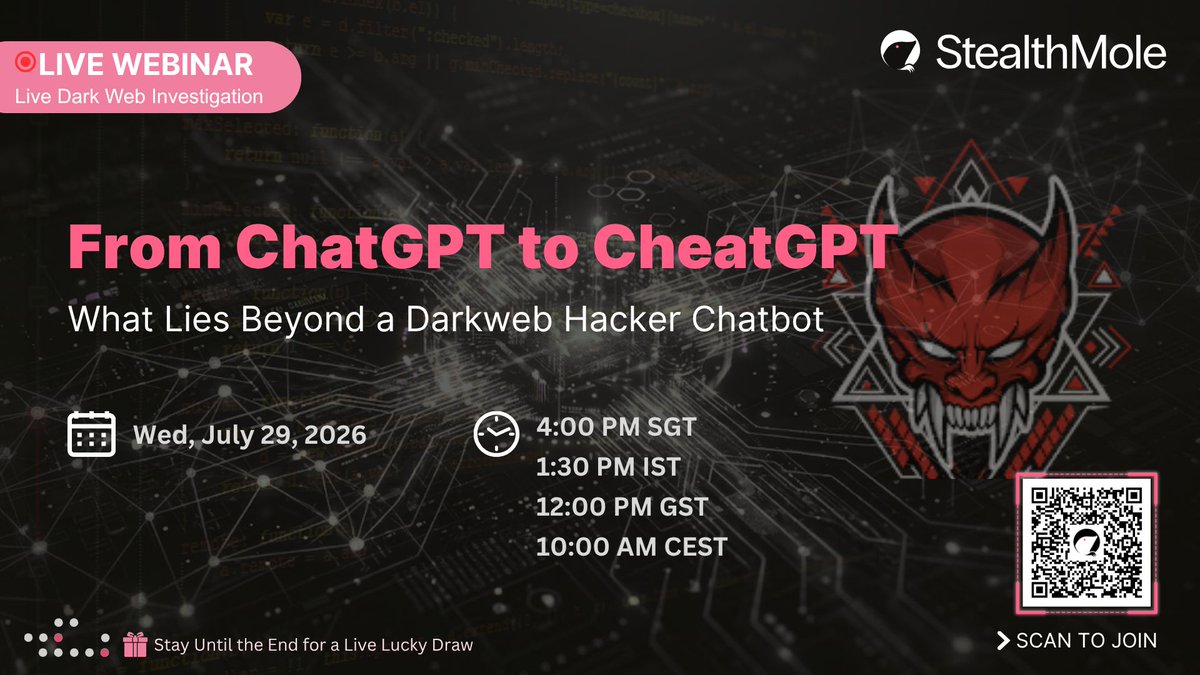
🚨 Happening TOMORROW: From ChatGPT to CheatGPT 🕵️♂️
What happens when dark web cybercriminals get their hands on generative AI?
CheatGPT isn't just a theoretical threat—it’s an "unrestricted" AI-powered hacking assistant operating across onion domains, mirror networks, and crypto payment channels.
In our latest investigation, we pulled a single Bitcoin thread and uncovered a massive web connecting CheatGPT directly to WormGPT and FraudGPT.
Join us TOMORROW as we walk through this investigation and discuss the growing "AI-as-a-Service" trend in cybercrime.
📅 Date: Tomorrow, July 29, 2026
🕓 Time: 4:00 PM (Singapore Time)
🔗 Register Here: https://t.co/hlgbp7b1fJ
📖 Read the Report: https://t.co/iidDphfGKi
#CyberSecurity #ThreatIntelligence #DarkWeb #GenerativeAI #AISecurity #StealthMole
🙏 A big TQ to @stealthmole_int our Networking Sponsor for supporting the OB1 2026 community.
👁️ If you see the @stealthmole_int team at @offbyoneconf , don't hesitate to introduce yourself. You never know where a conversation might lead.
🎟️https://t.co/cgS0IXzJRb
The Many Faces of ModernStealer: Tracing an Underground Military Data Network
Using StealthMole to follow these traces across dark web forums and Telegram, this investigation examines the digital footprint surrounding ModernStealer and the identities that appear to intersect with it. Rather than assuming that every matching alias belongs to the same person, the report follows the identifiers themselves, looking at where they reappear, how the connections develop, and what those overlaps can tell us about the network operating behind a series of military and government data offerings.
https://t.co/twM3K6YQKB
🇮🇩 StealthMole OSINT Masterclass is coming to Jakarta!
This Friday, August 7, StealthMole will host an exclusive, complimentary OSINT Masterclass in Jakarta.
Led by Louis Hur, CEO of StealthMole, the session will feature practical insights and live demonstrations, including real-world dark web tracking using StealthMole.
📅 Date: Friday, August 7, 2026
🕑 Time: 2:00 – 4:00 PM
📍 Venue: TBD
Participants will also receive:
🎁 A StealthMole license featuring our brand-new tracking module
🎧 A chance to win AirPods in our lucky draw
☕ An opportunity to connect with our team over coffee
Seats are limited for this session, so please register as soon as possible!
Register here: https://t.co/RdqI1apcZC
We look forward to reconnecting with our partners in Jakarta and sharing the latest developments in OSINT and dark web intelligence.
#StealthMole #OSINT #DarkWebIntelligence #CyberThreatIntelligence #Cybersecurity #Jakarta #Indonesia
🚀 In just 6 months, the StealthMole Intelligence Hub has doubled from 40+ to 80+ Dark Web intelligence postings.
Our research focuses on tracking Dark Web criminals, threat actors, illicit platforms, and underground communities across more than 20 categories—including cybercrime, fraud, extremism, data breaches, botnets, infostealers, ransomware, and emerging threats.
Explore the latest intelligence and stay ahead of evolving threats. 🔍
https://t.co/12cld0LKD4
#DarkWeb #CyberThreatIntelligence #ThreatIntelligence #ThreatActors #Cybercrime #OSINT #CyberSecurity #StealthMole
🚨 New Darkweb Threat Intelligence Live Dashboard
We’ve updated our Threat Intelligence live dashboard.
Just provide any domain name, and we can generate a full intelligence report instantly.
The report includes exposure insights such as:
• Compromised credentials
• Leaked documents
• Infected machines
• Dark web intelligence
🔎 See an example:
https://t.co/Fx6p3bIcnk
We also support 8 different real-time alert integrations.
📩 Interested? Contact us: [email protected]
#ThreatIntelligence #CyberSecurity #DarkWeb #OSINT #CTI
@stealthmole_int This is fantastic, Cyber threats don't wait for procurement cycles, and too many agencies are left playing catch-up due to budget constraints.
🚀2026 Free Trial : AI-Powered Intelligence for GOV
🍄To support those on the front lines, StealthMole is opening an exclusive Zero-Cost Support Program for verified Government and Law Enforcement agencies.
Get immediate access to our 8 Newly Released AI Investigation Tools designed to accelerate your dark web lead generation.
🌼The Offer
1️⃣ FREE 1M Pro License: Full access to the premium service
2️⃣ NEW 8 AI Investigation Features & Onboarding with...
FREE Expert Training: Onboarding sessions for your team.
🍎How to Claim (For LEA & Enterprise Only)
1️⃣ Sign up at: https://t.co/NkeS2oOT4F
2️⃣ Message me once registered, and I will upgrade your account.
🌵Why StealthMole
Cyber threats don't wait for budget cycles. Eliminate the barriers of cost and complexity. Start using targeted, AI-powered intelligence today. This offer is strictly limited to verified Government
#StealthMole #CyberInvestigation #AI #DarkWeb #LEA
From Dark Web Pages to Blockchain Trails: The Red Room Case
This investigation demonstrates how Red Room–linked activity can persist despite deliberately unstable and short-lived web infrastructure. While domains and pages changed frequently, the operational elements underpinning access, particularly payment mechanisms, showed continuity that could be observed and evaluated over time. Examining these elements provided insight that would not have been apparent through site-level analysis alone.
The case also reinforces the importance of separating exposed infrastructure from functional infrastructure. Not every wallet, domain, or reference surfaced during the investigation played an active role. Meaningful conclusions were possible only by correlating where elements appeared with how they were actually used, allowing inactive or placeholder components to be distinguished from operational ones.
More broadly, this report illustrates how combining dark web monitoring with blockchain analysis enables a more reliable understanding of services designed to minimize their footprint. By aligning contextual exposure with verifiable financial behavior, it becomes possible to move beyond surface-level claims and assess operational patterns with greater confidence. As dark web platforms continue to rely on disposable infrastructure, this approach remains essential for identifying what persists when visibility is intentionally limited.
https://t.co/bdtxI5olTj