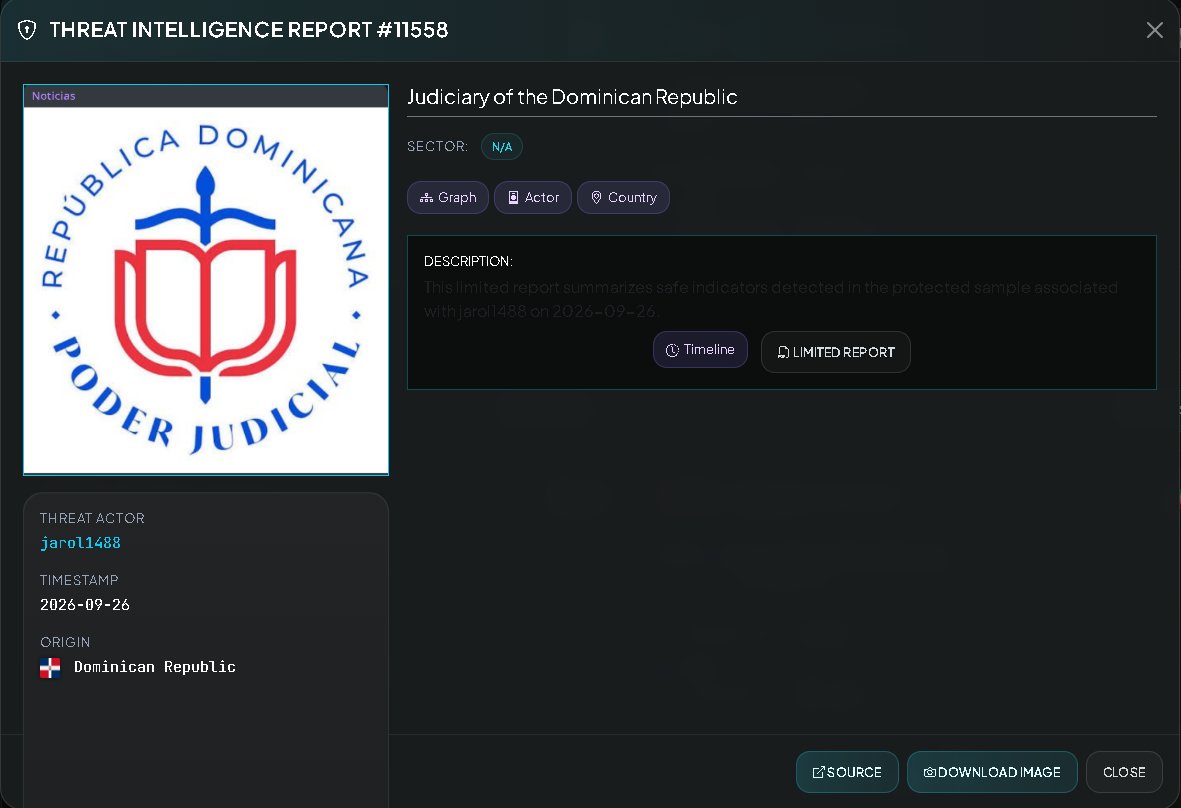
⚠️ CRITICAL PREVENTIVE ALERT 🇩🇴 ⚖️: ALLEGED MASS LEAK OF OVER 4.5 MILLION RECORDS FROM THE DOMINICAN REPUBLIC JUDICIARY
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: JAROL488 / DATE: SEPTEMBER 26, 2026]
Centralized cyber-intelligence monitoring has detected a new post on underground forums and channels, attributed to the threat actor "jarol488." The alert announces the release and public availability of a database containing 4,563,652 lines of information linked to the Dominican Republic Judiciary.
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by Dominican judicial authorities. The definitive scope of the files remains unconfirmed.
Threat Actor: jarol488.
Victim / Affected Entity: Dominican Republic Judiciary (https://t.co/644vT2ugLQ).
Sector: ⚖️ Government / Justice, Courts, and State Legal Registries.
Target Country: Dominican Republic 🇩🇴.
Reported Data Volume: 4,563,652 lines of structured information.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / JUDICIARY)
Forensic Audit of Servers and Repositories: IT teams within the Dominican Republic Judiciary must immediately isolate and audit database servers and public inquiry portals to determine the initial extraction vector. Link Verification and Reporting: Request the immediate blocking and removal of the external download repository (gofile. io) associated with the leak to mitigate the spread of the records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #Judiciary #DominicanRepublic #JusticeSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ CRITICAL PREVENTIVE ALERT 🇩🇴 🛡️: ALLEGED DEFACEMENT AND COMPROMISE OF MILITARY INFRASTRUCTURE IN THE DOMINICAN REPUBLIC
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE BUT NOT OFFICIALLY VERIFIED / DATE: SEPTEMBER 25, 2026]
Centralized cyber-intelligence monitoring has detected a new alert originating from social media and website defacement tracking platforms. The alert was disseminated by the account "La Resanha Sec" and attributed to the operator "azraelzer0d4y." The report announces the compromise of government/military top-level domains (.mil.do).
It is strictly noted that the veracity of this compromise and the actual scope of the intrusion have not been officially confirmed by Dominican Republic authorities. The status of the infrastructure remains unverified.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / DEFENSE)
Forensic Audit of Military Web Servers: Incident response teams in the Dominican Republic must immediately isolate and audit the server hosting "plataformadigev. https://t.co/PbkbI5tVEW," reviewing access logs to determine the initial intrusion vector.
Administrative Access Restriction: Revoke compromised credentials and secure remote desktop services or control panels exposed to the public network. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ3laQ
Quotes and services: https://t.co/sx3BM5zJdi
#Cybersecurity #ThreatIntel #Defacement #MilitarySecurity #DominicanRepublic #LaResanhaSec #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
I just watched someone spend $3,000+ on tech certifications that got them zero job offers.
Here are 10 tech certifications that will actually make you money in 2026:
Los medios sin seguidores no son nada, dejemos de seguir medios que están en contra de la dominicanidad.
-Diario libre; es propiedad de Grupo punta cana y los Rainieri.
-CDN37; es propiedad de Manuel Estrella
-N digital; propiedad de Nuria Piera