The safety largely comes from the agent harness, rather than the model itself.
On the Surface Ultra, you can run models locally using something like llama.cpp. NVIDIA has some recommended configurations here: https://t.co/p8DNmcHuWB
You then connect your agent harness of choice (Codex, Pi, Hermes, etc.) to that local model. The harness determines what tools the model can access and enforces things like approval prompts, sandboxing and permission controls.
So running the model locally doesn't inherently make it safe. It's how you allow the agent to interact with your system that matters.
Qwen 3.8 27B (Unsloth quant) running fully local on the Surface Ultra on battery.
331 tokens in 10s, 32.27 tok/s.
Asked it "What can you do?" and it confidently introduced itself as Claude 😅
Honestly, no clue yet if it's useful to anyone but me 😅 If you're on Windows on ARM, give it a scan and tell me what it finds. It's open source, so feel free to contribute and make it better.
Microsoft Store: https://t.co/EyzScOcjZ3
GitHub: https://t.co/zgxuZJZuYf
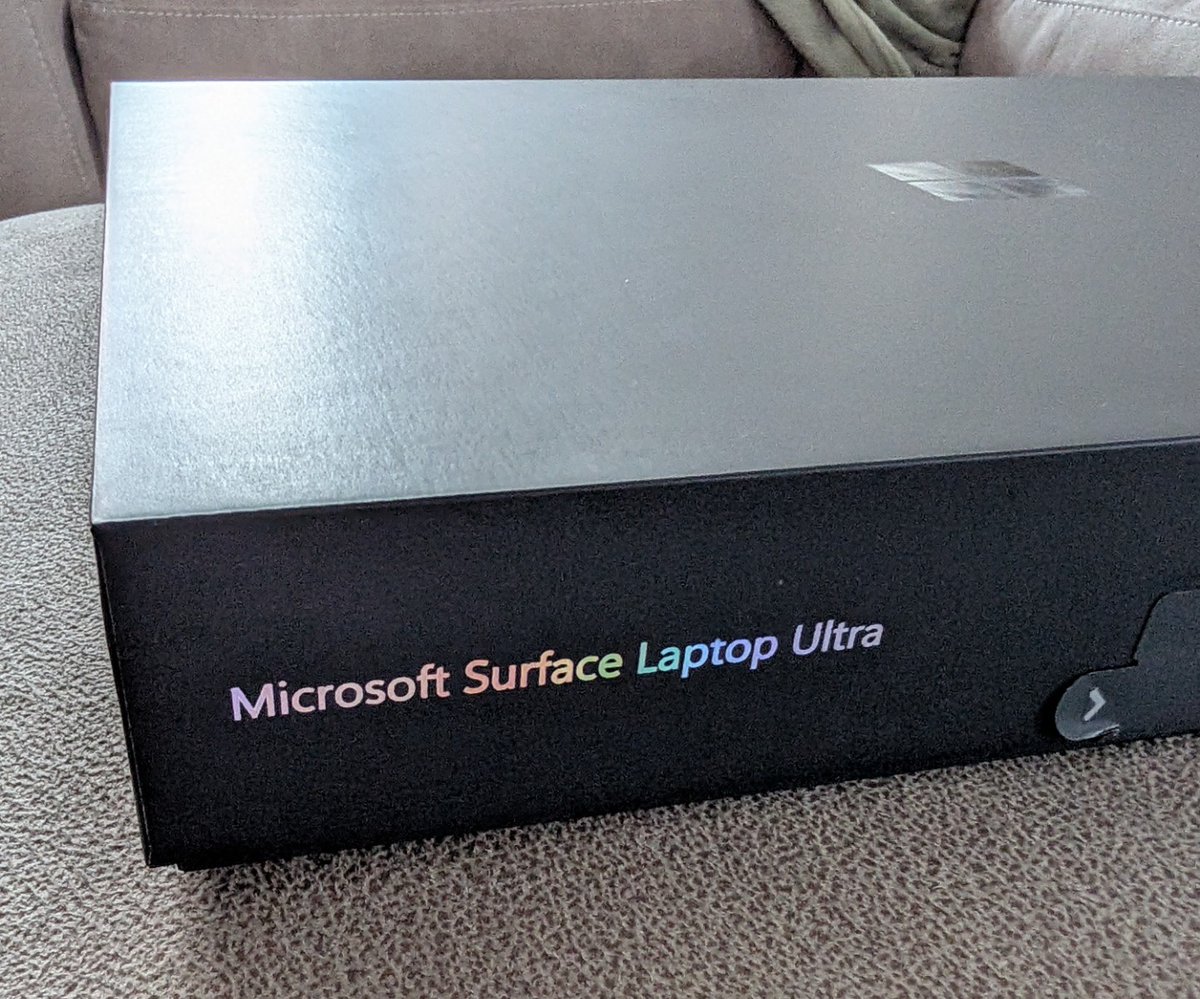
I picked up a Surface Laptop Ultra and realised how easy it is to end up running x64 apps on Windows on ARM without knowing, even when a native ARM64 build exists.
So I thought my first project on the new machine should be an app to find them. Meet ArmAware 🧵
Private by design: no account, no telemetry, no backend. Scans run locally and offline by default.
Optional online checks go through Windows Package Manager to Microsoft's catalogs, and your app list is never uploaded.
@surface Honestly, everything. But definitely looking forward to testing some local AI! I would've gone 128GB if it hadn't been out of stock in the UK. 👀
Day 25/
We are doubling all usage limits for all Pro 100/200/500 tiers and Business Premium, effective today.
We heard your kind feedback and won’t be reducing usage limits for Pro 200, so your Work and Codex usage will stay the same. We’re also going to continue offering extended limits for dots for now, and usage of your dot will still continue to be separate from your default usage.
And we'll of course also keep shipping better models and other efficiency improvements that increase your effective usage over time.
A lab says an AI model asked to write a detection rule tried to upload a test string to a bucket in Beijing. Its reasoning said it would use no tools.
The sandbox had no route out, so nothing left. Log what agents do, not just what they say.
https://t.co/NlzMotpvHR
Treat connecting to a remote MCP server like running untrusted code. Pillar Security reports that opencode on Windows and WSL (before 1.18.33) let a malicious remote server run code during OAuth sign-in. The fix shipped as a refactor, with no advisory. Update, allowlist your servers, and log the OAuth callback and any child processes your agent spawns.
https://t.co/CH5ZALUS4j
Left a VPN on, opened ChatGPT, met a "dot" called Jimmy. Turned the VPN off and it was gone. Turned it back on days later and it had been doing stuff the whole time 🤔 Anyone else in the EU/UK seen one?