HTTP Method Tampering in action!
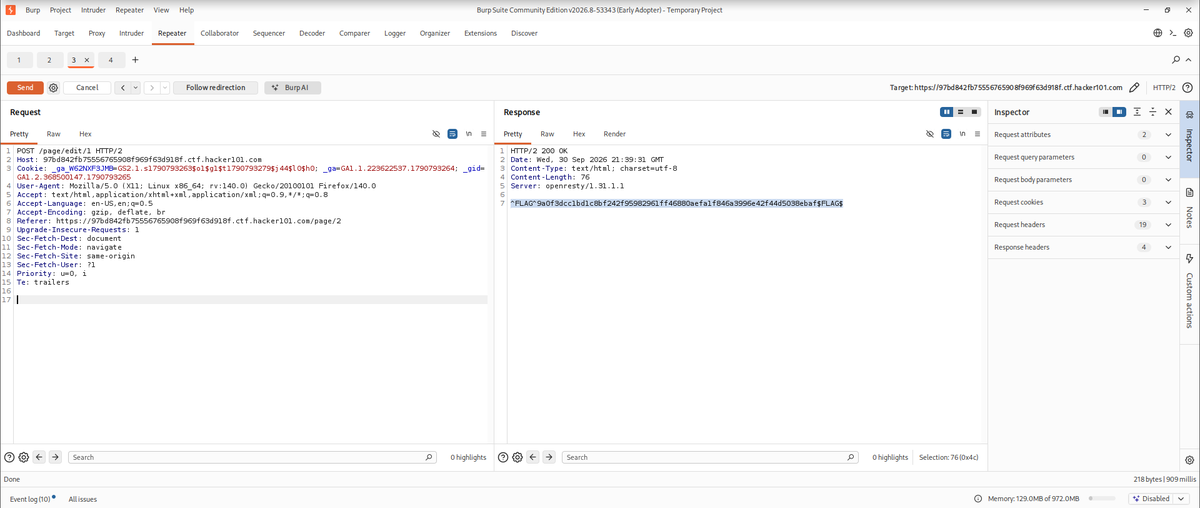
Swapped the request method to POST on an edit endpoint, bypassed access control, and got the flag.
If backend rules only filter GET, attackers will just switch the verb. Enforce auth globally!
#Cybersecurity#CTF
GUIDs prevent IDOR by making user IDs unpredictable. But if an app leaks a victim's GUID in a response or redirect, the defense is dead.
An attacker just copies it and takes over the account.
#BugBounty#Cybersecurity
@Cybergez Yeah, most applications should be doing this by now. But with the advent of AI, insecure coding practices is becoming quite dominant again as most people skip over the fundamentals.
Password reuse is a disease, but devs must step up too. Why aren't all apps using cryptographic salts?
A salt (Pwd:name123 + Salt:qv3#$>) makes hashes unique, stopping rainbow table attacks.
Use a password manager. Secure is a myth, but it beats generic passwords
#Cybersecurity
Cybersecurity is about defying logic.
Developers design systems expecting normal behavior. Our job is to break those assumptions and test everything they thought we would never try.
#Cybersecurity#BugBounty
Glad to be back sharing the journey! Check out my HTB writeups below and please drop your reviews or feedback, I would love to know what you think: https://t.co/bU5mdausEO
I’ve been quiet lately, but for good reason. Out of almost 1,000 applicants, we thank God I was called up for a security internship interview.
The security and automation coding questions were a massive reality check on how much more there is to learn.
2️⃣ picoCTF: Cracked the admin's SQLite password hash using Hashcat, then bypassed the MFA prompt by decoding the Flask session cookie to find the OTP sitting right there in plaintext!
2FA is useless if the implementation logic is flawed! 🎯
#Cybersecurity#Infosec
Breaking 2FA Logic 🔓
Two different 2FA bypasses today!
1️⃣ PortSwigger: Bypassed the OTP screen entirely by changing the URL from /login2 to /my-account because the session was granted too early.
Reconnaissance
Reviewed HTTP Auth & Rate Limiting, but spent the evening deep in Google Dorking and live passive recon.
Passive recon is the absolute foundation of hacking. Don't touch the target's server until you know exactly what you're looking at.
#OSINT#Cybersecurity
Bypassing IP Blocks 🕸️
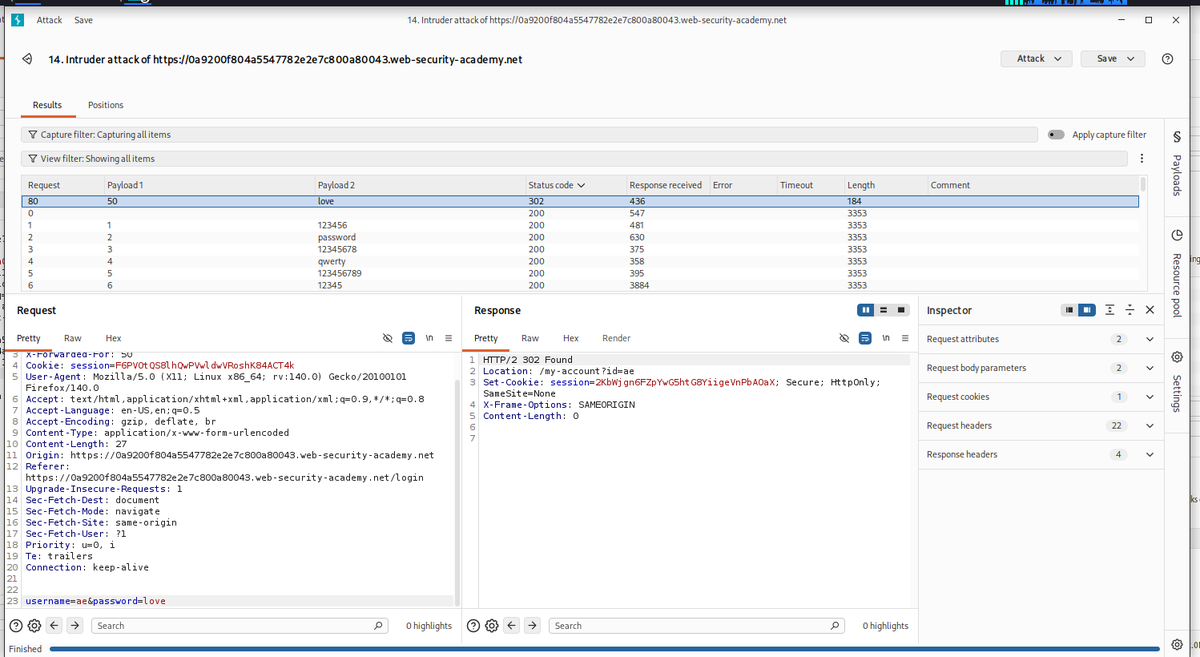
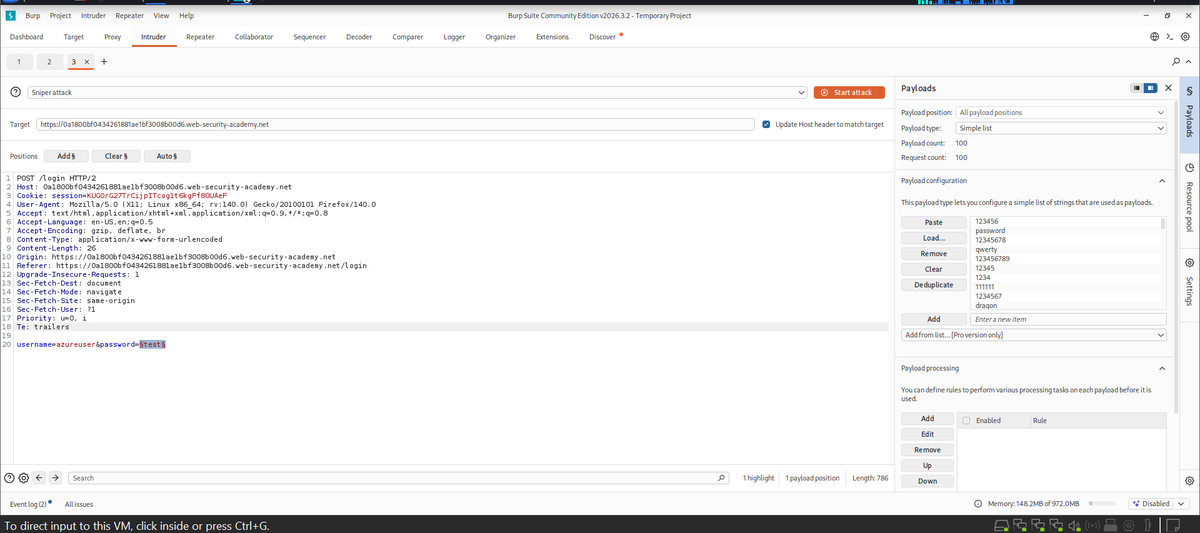
Target blocked my IP after 3 failed brute-force attempts. The flaw? A successful login resets the counter!
I Used Burp Intruder to alternate between a known valid login & brute-forcing the victim. Block bypassed! 🎯
#Cybersecurity#Infosec
Untop say I dey find SIWES placement, you dey run phishing attack on me. 😂😂 Who dey pay intern $1,600 per month? The 'Bcc: me' just made it too obvious.
Omo, tell your threat actor to improve their attack strategy! 😭😭🚩 #Cybersecurity#Phishing
HTB Included
Chained an unauthenticated TFTP upload with an LFI to get RCE, pivoted off creds sitting in a leaked .htpasswd, then rode an lxd group membership straight to root by mounting the host fs into a container.
Small bugs stack fast.
#HTB#Pentesting#Cybersecurity
1️⃣ Spoofed past the rate limiter by rotating fake IPs via X-Forwarded-For with Burp's Pitchfork attack
2️⃣ Forced heavy password hashing to leak the valid username through response timing alone
Making a server talk when it doesn't want to never gets old. 🎯
#Cybersecurity
Used Burp Intruder's Grep-Match to catch the missing punctuation, isolated the real username, and cracked the password from there. Human error really is the ultimate vulnerability. 🎯
#BugBounty#Infosec#Cybersecurity#Pentesting
Hunting Typos 🕸️
The developer tried to shut down username enumeration by returning a generic 200 OK for every login attempt. Almost worked — except for one typo in the error message that only showed up for valid usernames.
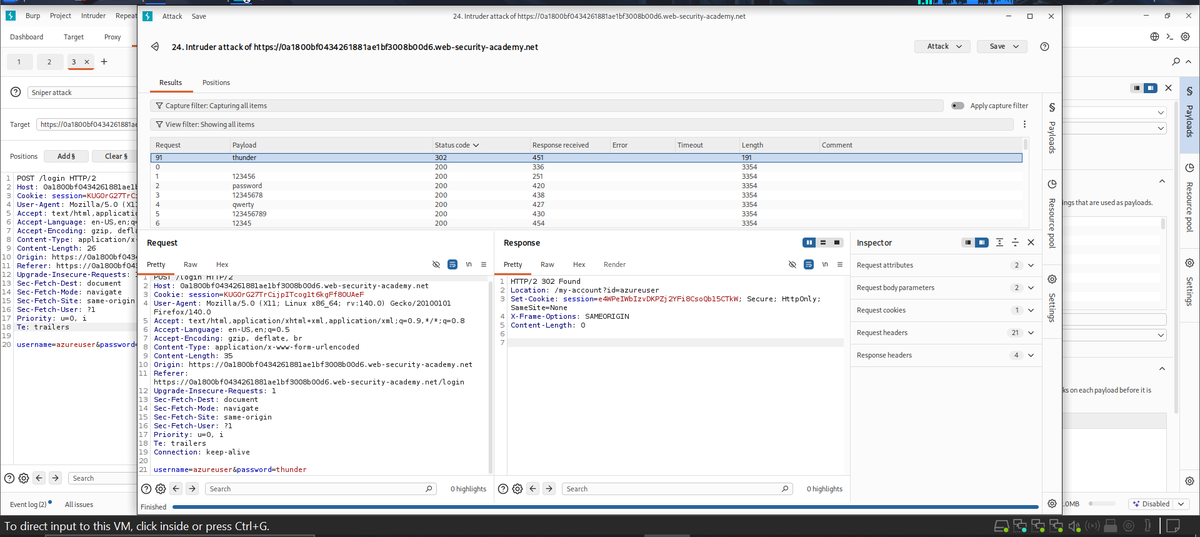
My biggest takeaway? Brute-forcing isn't really about the attack : it's about knowing what to look for in the responses. Found the valid login by catching a single 302 Found sitting quietly in a sea of 200 OKs. 😇
#BugBounty#Infosec#Cybersecurity#Pentesting