🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
A penetration tester is asked to test a production payment system, but the signed scope only includes the company’s staging environment. What should the tester do FIRST?
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
PenTest+ is about decisions, not just definitions.
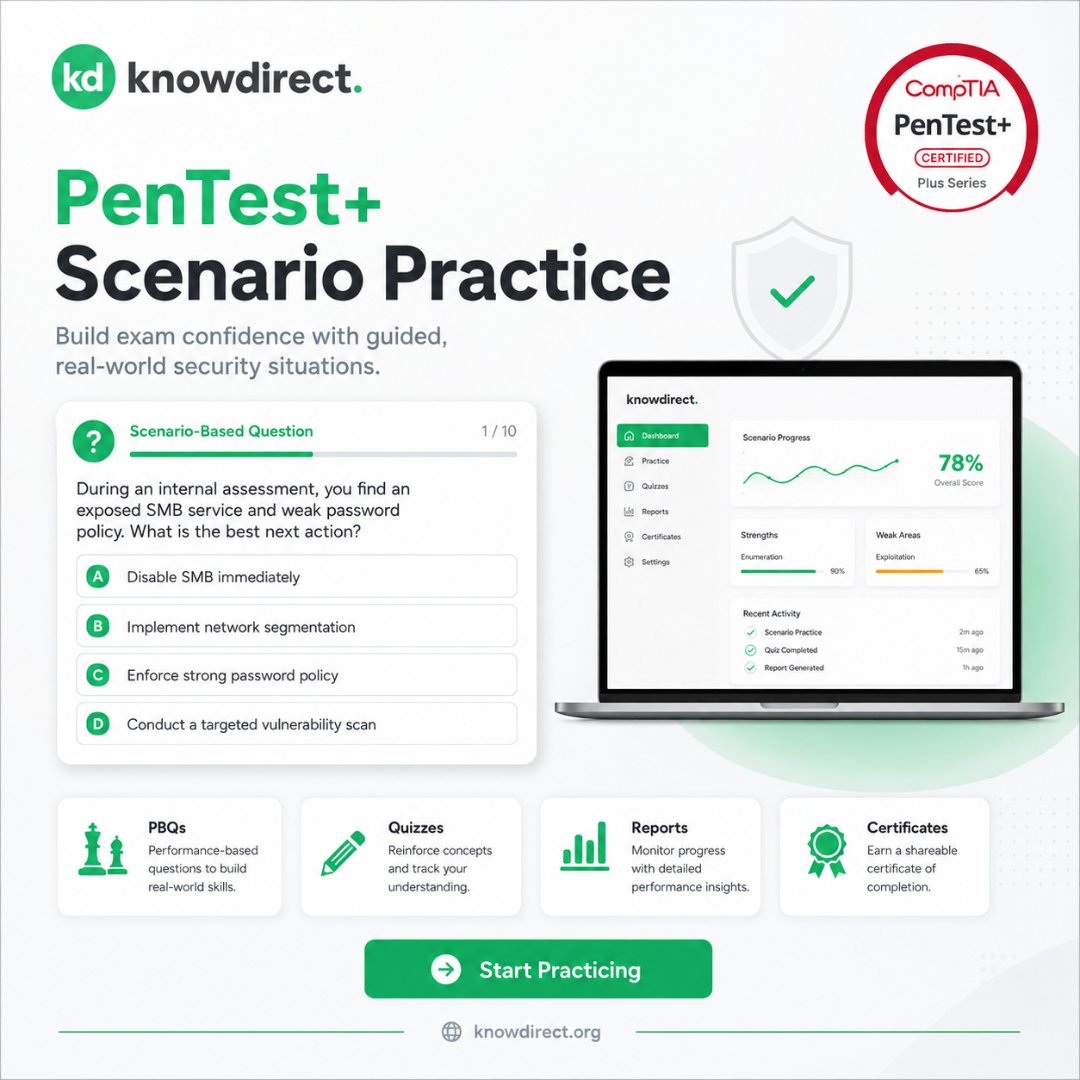
Scenario: exposed SMB service + weak password policy during an internal assessment.
What is the best next action?
Practice real-world security scenarios with KnowDirect.
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
A vulnerability scanner reports a critical issue, but the tester suspects it may be a false positive.
What should the tester do NEXT?
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
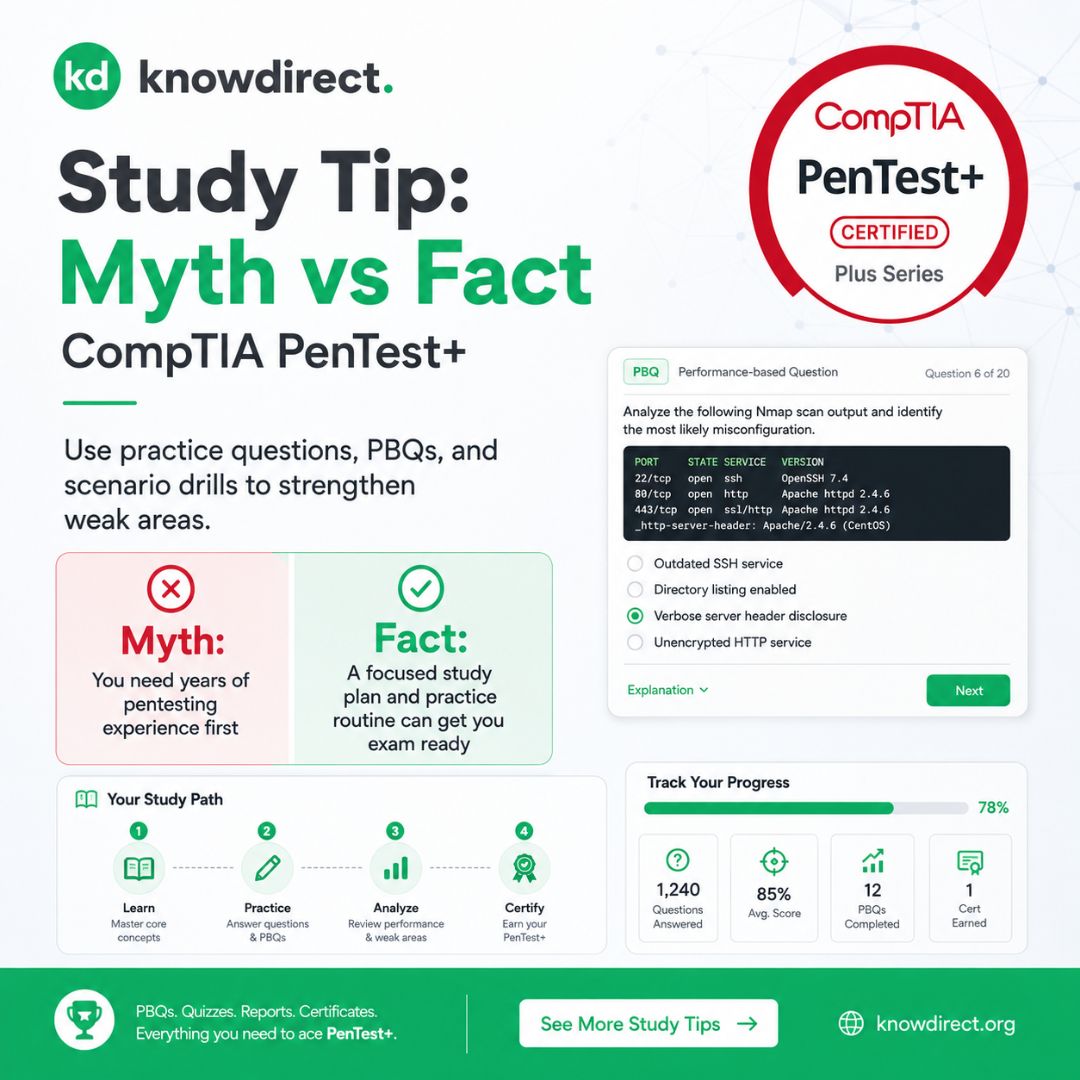
PenTest+ myth: You need years of pentesting experience before you start.
Fact: A focused study plan with PBQs, scenario drills, and progress tracking can help you build exam confidence.
Start with weak areas. Practice consistently.
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
A tester gains access to a Linux host and wants to identify the current user and group memberships.
Which command is BEST?
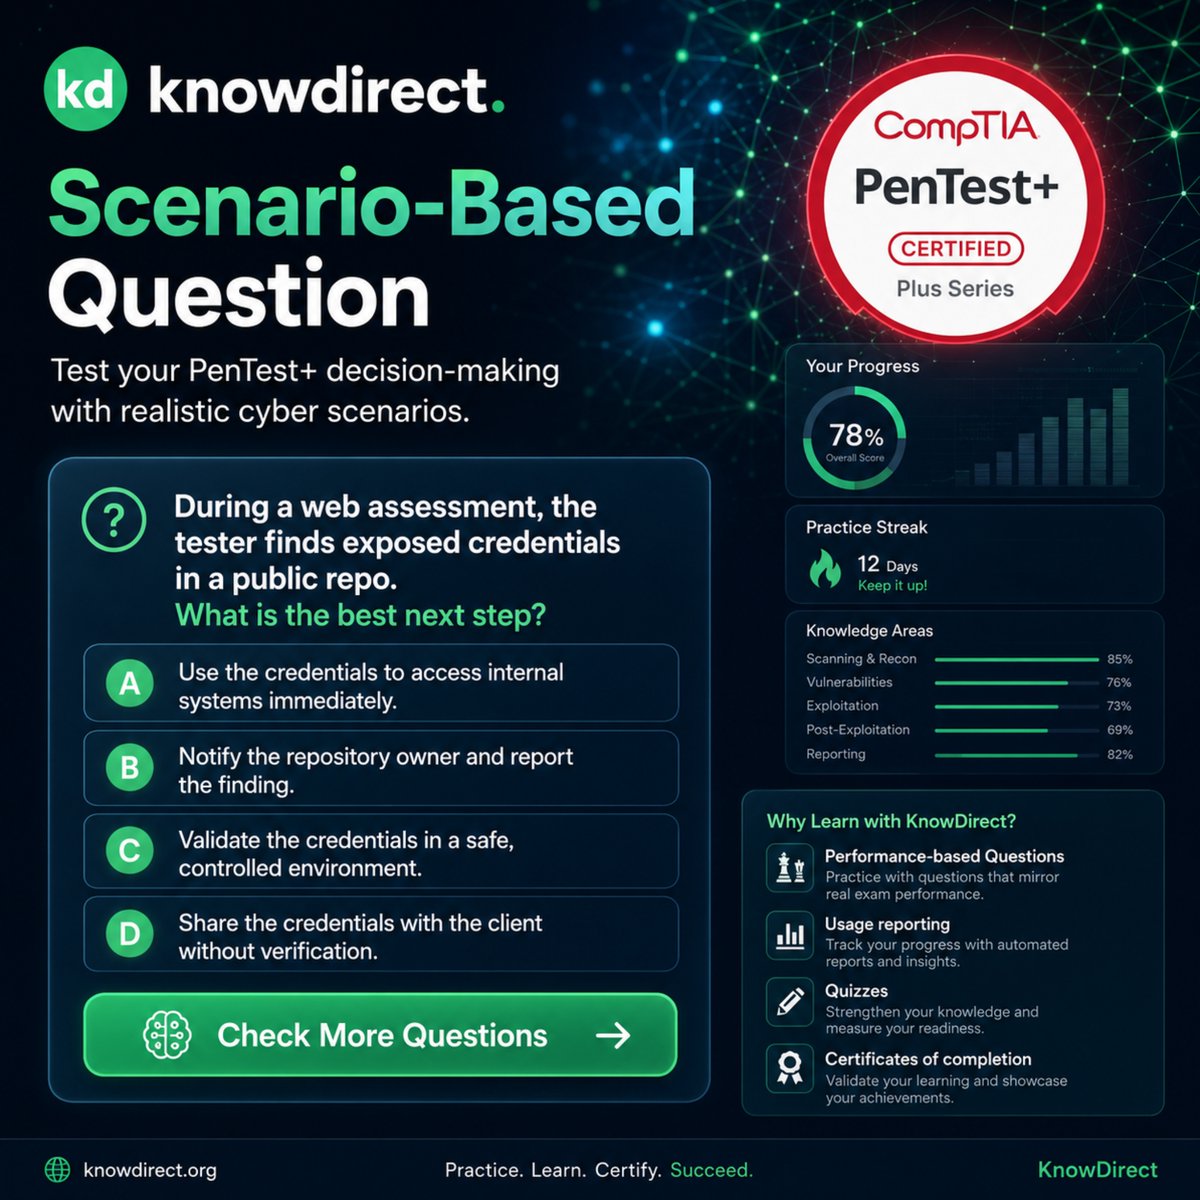
PenTest+ scenario:
You find exposed credentials in a public repo during a web assessment.
Best mindset: stay in scope, document the finding, and report it responsibly.
PenTest+ tests judgment, not just tools.
#PenTestPlus#CyberSecurity#EthicalHacking#CompTIA
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
A tester gains shell access to a Linux host and wants to check which commands the current user can run with sudo.
Which command is BEST?
PenTest+ quick check:
Gathering target information before exploitation = Reconnaissance
Small clues like this matter in scenario-based cybersecurity questions.
#PenTestPlus#CyberSecurity#EthicalHacking#ExamPrep
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
A penetration tester discovers a vulnerable server that is not listed in the approved scope document. What should the tester do FIRST?
PenTest+ quiz challenge:
Which method is best for enumerating subdomains during a penetration test?
A. WHOIS lookup
B. DNS zone transfer
C. Port scanning
D. SSL certificate analysis
Comment your answer.
#PenTestPlus#CyberSecurity#EthicalHacking
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA PenTest+ Exam
During testing, a login form returns a database error after the tester enters ' OR '1'='1 into the username field.
Which vulnerability is MOST likely present?
PenTest+ prep tip:
Do not just memorize tool names.
Learn when to use them.
Reconnaissance, vulnerability analysis, exploitation concepts, and reporting all matter.
Practice smarter with realistic exam-style questions.
#PenTestPlus#Cybersecurity#EthicalHacking
🌍 OFFICIAL WEBSITE: https://t.co/R9bbknKDaT
#KnowDirect Pop Quiz - #CompTIA Network+ N10-009 (V9) Exam
An administrator wants to collect interface statistics and device health information from switches and routers. Which protocol should be used?