I woke up today to see the Java Champion nomination posts and I can only say I’m truly happy and humbled to join this amazing group.
I hope to liveup to the standards of a champion and promise to continue supporting this incredible community as I always have.
Long live #Java! 🥳
Java 27 is almost here❣️
Join us tomorrow at 15:00 UTC for a 3 hour livestream featuring live coding, technical deep dives and conversations with the guests from the JDK team and community.
See you live 👇
https://t.co/RmcPdirwyu
#Java#JDK27#AI
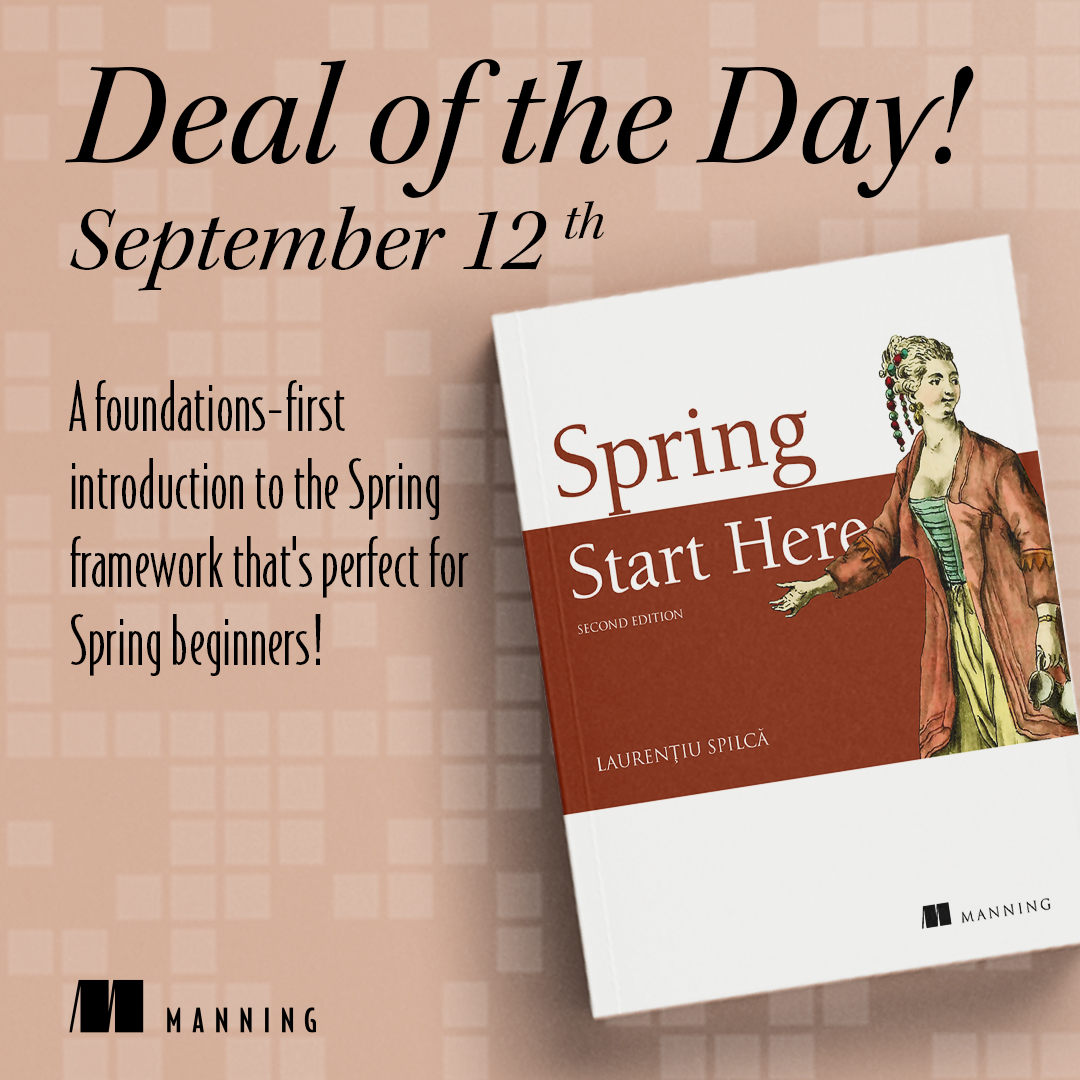
Save 45%, only on Sept. 12th!
Today, you can save on Spring Start Here, Second Edition by @laurspilca and other related titles: https://t.co/Pd4R4EXAnt
Learn the main ideas of Spring: configuration, beans, web endpoints, data access, and application structure.
@404Niels@ManningBooks If you just start with Spring I recommend you my Spring Start Here. If you already have some experience with it you can go for Spring Boot in Practice. But that is just for the start. Even APIs which look like a simple subject give a lot of opportunities to learn.
The best technical books don't just teach a framework — they teach the foundations behind it.
Spring Start Here, Second Edition by @laurspilca helps you build a solid understanding of Spring through hands-on projects, whether you're learning it for the first time or updating your skills with Spring Framework 7 and Spring Boot 4.
Now in MEAP and 50% off through July 15th: https://t.co/BLlDdfVJ6e
Most security issues don't begin with an attacker.
They begin with a trusted input that shouldn't be trusted, permissions that are too broad, an exposed API, or a vulnerability introduced during development.
Today's Deal of the Day features four books on building security into your systems from the start:
• Software Security for Developers by @laurspilca
• Authorization in Action by @windley
• Secure APIs by @JoseHaroPeralta
• Grokking Web Application Security by Malcom McDonald
Explore what else is half off: https://t.co/ETBEtolGDT
Software Security for Developers by @laurspilca & @asaikali one of the best books about security I read. Starts with the reasons behind security failures, then dives into crypto, TLS, OAuth2, K8s, and more. A must read for devs and beyond
🔗https://t.co/1q42UR7nq7
@ManningBooks
@NickWilson73@ManningBooks Happy to hear this. And yes, you are right. We should also think about a book designed at a higher level at some point to cover other subjects from ways of working to infra for example.
A lot of software education teaches developers how to make things work, but not always how to make them secure. That becomes a problem when vulnerabilities start with architecture, dependencies, config, or day-to-day coding decisions.
Software Security for Developers by @asaikali and @laurspilca covers practical secure development for modern cloud and Kubernetes environments.
Now in print and 50% off through May 29th: https://t.co/NuGeDVNeY9
In this fully revised second edition, Java veteran Laurențiu Spilcă @laurspilca updates coverage of new Java tools and adds methods to save time and effort using AI.
Today, you can SAVE on Troubleshooting Java, Second Edition by Laurențiu Spilcă and other related titles: https://t.co/GXqmscfptM
In this fully revised second edition, Java veteran Laurențiu Spilcă updates coverage of new Java tools and adds methods to save time and effort using AI.
Building secure software isn't optional, but most resources bury what you actually need.
Software Security for Developers by @asaikali and @laurspilca focuses on using built-in security features in Java & Spring with no theory overload.
Watch Laurențiu on @GOTOcon Book Club: https://t.co/31rucTTIo7
The book: https://t.co/x0pjRJW8Ga
#GOTOpodcast: @laurspilca joins Thomas Vitale to break down Software Security for Developers.
*encoding vs hashing vs encryption
*rolling your own “quick” solution
*trusting AI-generated code
*skipping PKI and certificates because… yeah
🎧 https://t.co/uXmDK0HJ6p