an OpenAI model used an 0x project default recovery seed "concert load couple harbor equip island argue ramp clarify fence smart topic" available online for creating testnet accounts, to get testnet funds. and it was reported as "misalignment" and compared to hacking!
What's truly insane is not that this happened — it's shameful, but bad process is everywhere — but rather that seemingly every root certificate store maintainer let an organization at which this could happen become a CA.
I can't practically test because I don't have an Android device running an old version of Firefox. Have you checked to see if you have setting somewhere that are blocking OneCRL updates? But in any event — my point was that you don't need to e.g. avoid insecure wifi networks because of this. Which you don't — even as part of the <1% of people driving Firefox for Android… you can just update it.
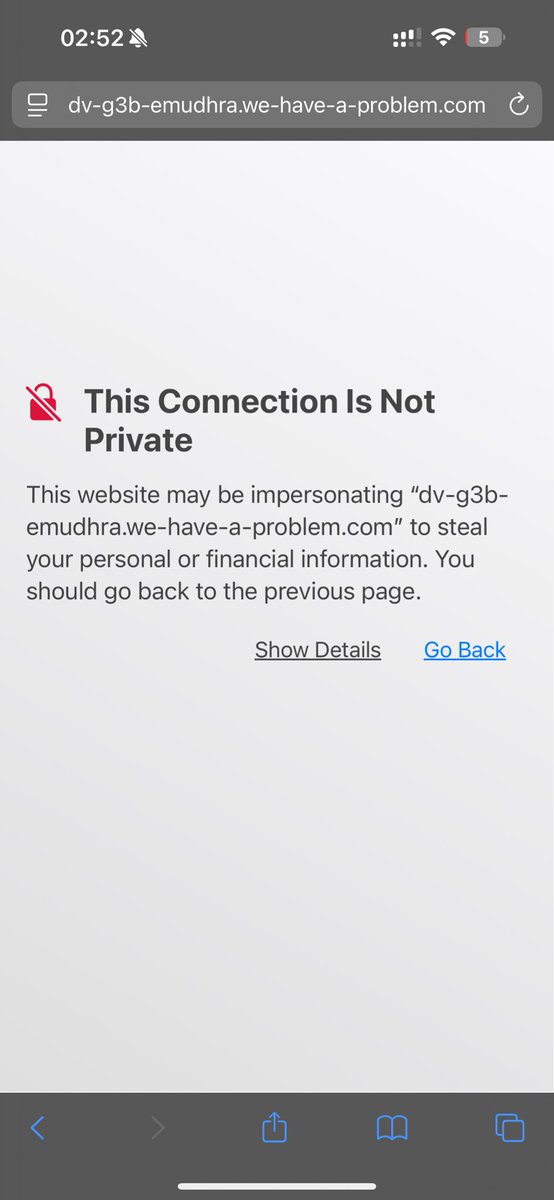
Or, instead of engaging in mid-aughts security theater, you could just untrust the eMudhra root certificates, which has already happened if you're running iOS, macOS, Windows, mainline Android 14+, or any mainstream browser.
PSA: Do NOT use public WiFi or shady DNS servers for the next few weeks.
SSL is practically broken and you can be attcked with an MITM attack. Your ISP and other intermediaries can also spy on you. Use a trusted VPN.
It will take a few days at least to flush out this crap CA.
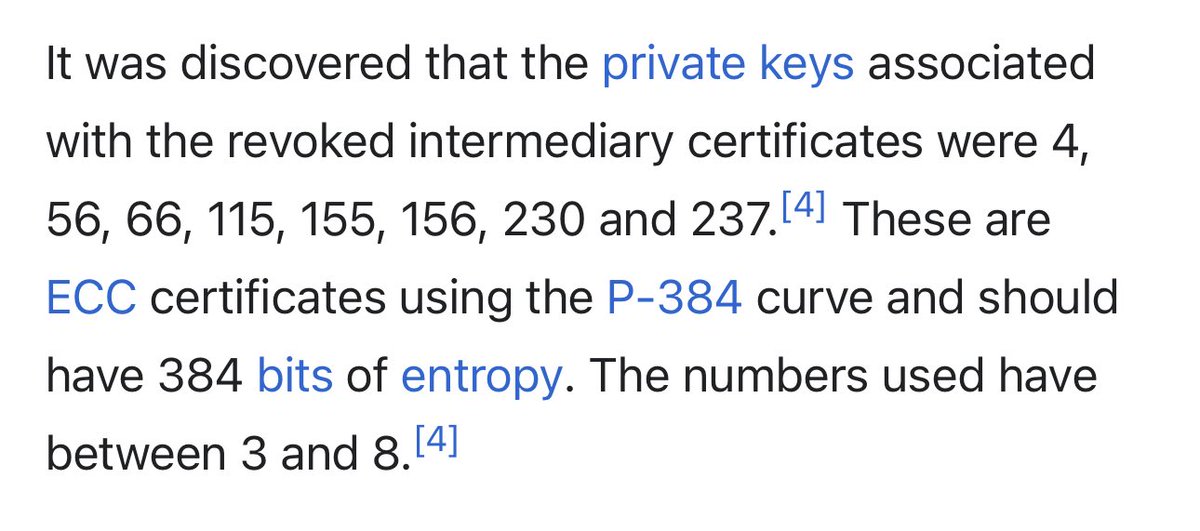
Following the discovery that eight eMudhra intermediate certificates use weak keys, Cloudflare is deploying mitigations and releasing client updates. We explain the impact, our response, and what customers and developers should do next. https://t.co/lYGxHb3PHS
@Mudit__Gupta That's not true. Google has maintained a similar killswitch since Android 14, and Mozilla invalidates certs via their own OneCRL infrastructure, including on Firefox for Android, and actually responded to this incident super early, on the 17th (https://t.co/vWWmqotEr4).
No Linux system uses any affected eMudhra certificate as part of its code-signature chain, so actually that won't happen, and it's unclear how an uncompromised "forgotten Linux machine"
or "IoT device" or "Docker container" or "CLI tool" (?) would wind up installing "safely-signed malware" anyway, unless you're suggesting "relentless" MITM attacks, which is a rather remarkable postulate.
One thing I learned from accidentally chemically castrating myself for five days is that there are levels to your dick not working. I've seen things you people wouldn't believe.
Many users don't update their shit, which is why Apple (etc.) has a force-pushed remote update-free kill switch for bad certs, which was activated yesterday. If you're running a device that doesn't receive cert updates in a timely fashion AND that doesn't let you update them yourself… sure, stay off untrusted networks. But why are you running Windows 8 Mobile?