Another Breach in Public Sector Data Security
Just received a disturbing message claiming the NWSDB customer system has been hacked by a group demanding ransom in crypto.
🛑 Our citizens’ data is not safe
📎 Pension Leak Details: https://t.co/MxhrH2sYEO
#CyberSecurity#SriLanka
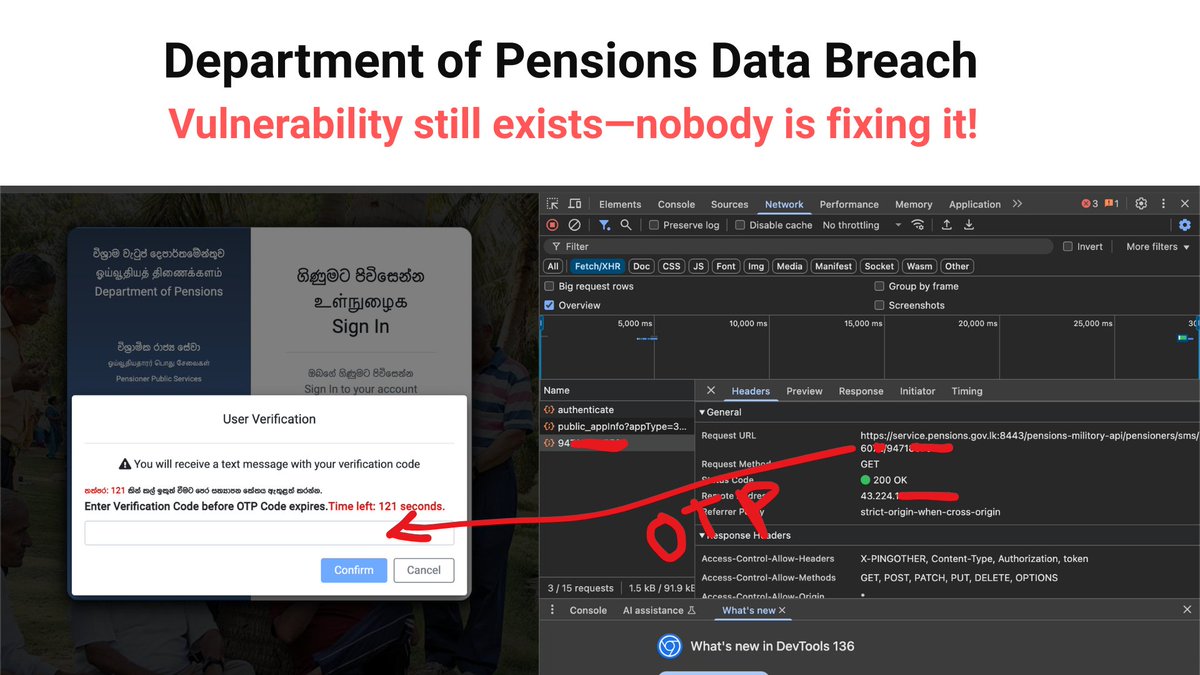
Sri Lanka 🇱🇰 Pension Department Data Breach – Vulnerability Still Exists and Nobody is Fixing It!
⭕️ "No data lost in cyberattack on Pensions Dept, systems restored" – The Department of Pensions
This is an absolutely false statement.
⭕️ The breach likely wasn’t even caused by sophisticated hacking – it’s probably due to EXPOSED PUBLIC API ENDPOINTS that anyone can access.
⭕️ These endpoint are still open, a person with basic IT knowledge can easily write a simple script with just a few lines of code and extract the entire database. This is basic web scraping, not even "hacking".
⭕️ The department has inadvertently created undocumented public API endpoints that expose their entire database to the world.
⭕️ After the initial data dump on the dark web, the department introduced an OTP authentication. However, this OTP implementation is laughably flawed.
⭕️ The OTP is generated on the front end (your browser) and sent to the back end for "verification." It’s like showing you the PIN on screen and then asking you to type it back. This provides zero actual security while creating dangerous false sense of security.
⭕️ Every W&OP scheme member’s complete data has been compromised: Name, Address, NIC, Phone, Photo, Gratuity amounts and Workplace details. Thousands of retired government employees, military, and police families are affected. (Anyone can enter the generated number shown in your browser and access the information.)
⭕️ Pensioners are prime targets for scams. Scammers now have everything needed to target Sri Lankan pensioners. They can call knowing exact ID numbers, addresses, pension amounts, and workplace history.
Tell your parents/grandparents: NEVER share personal info, OTPs, or card numbers with callers – even if they know your details. Hang up and verify independently.
⭕️ Considering the inclusion of military personnel and public data, this should be considered national security emergency affecting the public servants and most vulnerable citizens and security personnel. Every hour of delay puts more lives at risk.
⭕️Someone needs to immediately shut down the Pensions Department login portal (https://t.co/XpQ0p0mXu7). Conduct a full security audit and notify all affected individuals at once. immediately.
Note: We came across this over 48 hours ago and reported it to the relevant authorities through multiple independent channels capable of independently verifying the information. However, no action has been taken so far, and the vulnerabilities remain unresolved.
#SriLanka #PensionDepartment #DataBreach
@NewsWireLK What happened to the Kotahena girls' case? After the Grade 5 teacher incident made headlines, this case seems to have quietly disappeared from the spotlight. It feels like once a new controversy emerges, the previous ones are pushed aside, leaving justice hanging in the balance.
@FT_SriLanka What they offer is just a loan against FD You don’t need AI to give a loan against FD, every bank does this. What is expected to have is to give an unsecured loan with AI assistance by analysing the customer data etc with the bank, this post is a bit misleading. @SampathBankPLC
@numberslka Technically as per the IR Act, if you have only employment income (your source of income is purely from employmen) on which PAYE (APIT) is deducted, you don't need to file t6ax return!!
@NewsWireLK This news about visa-free entry is incorrect. As of now, the Thai embassy has not implemented such a policy. This misinformation is causing significant inconvenience to travelers. Please verify and correct your sources before publishing. #TravelAlert#FactCheck