Volaris Group announces the acquisition of LoginRadius Global, a Canadian-based provider of enterprise-level customer identity and access management solutions. LoginRadius Global will continue to operate independently within the Security Portfolio of Volaris Group.
Read the full news here - https://t.co/B7CGQtPUKL
Freedom is about trust, security, and the confidence to move forward as a nation.
This 4th of July, we celebrate independence in every form - from the history we share to the digital spaces we protect!
Here’s to experiences that are open, secure, and built for everyone.
Happy 4th of July! 🇺🇸
#4thofJuly #IndependenceDayUSA #Freedom
Happy Canada Day 🇨🇦
Today, we celebrate the spirit of innovation, diversity, and resilience that defines Canada.
At LoginRadius, we’re proud to be built in Vancouver and inspired by the values this country stands for - trust, inclusivity, and forward thinking.
Here’s to building secure, seamless digital experiences that bring people together.
#CanadaDay #ProudlyCanadian #Innovation #DigitalIdentity
At LoginRadius, we recommend our customers to keep tabs on the MFA alerts and failures. This World Environment Day, let's bring that same responsiveness to the physical world.
The climate change signals from Mother Earth are loud and clear - let's make sure we're paying attention and doing our part. 🌍💙
#worldenvironmentday #nowforclimate
At LoginRadius, we manage identities, but mothers create them. This Mother’s Day, we’re celebrating the original "Identity Provider" 💙💙💙
#MothersDay#HappyMothersDay#MothersDay2026
Our new year resolution is to pioneer Agent-Ready Identity for a Safer, AI-driven World.
Wishing everyone a prosperous and successful New Year ✨
And a big thank you to all our customers, partners, and employees who shaped everything we built in 2025.
#LoginRadius#NewYear2026
2025 = year of AI exploration 🔍, and 2026 = year of AI maximization 🚀
Here is the LoginRadius countdown to 2026.
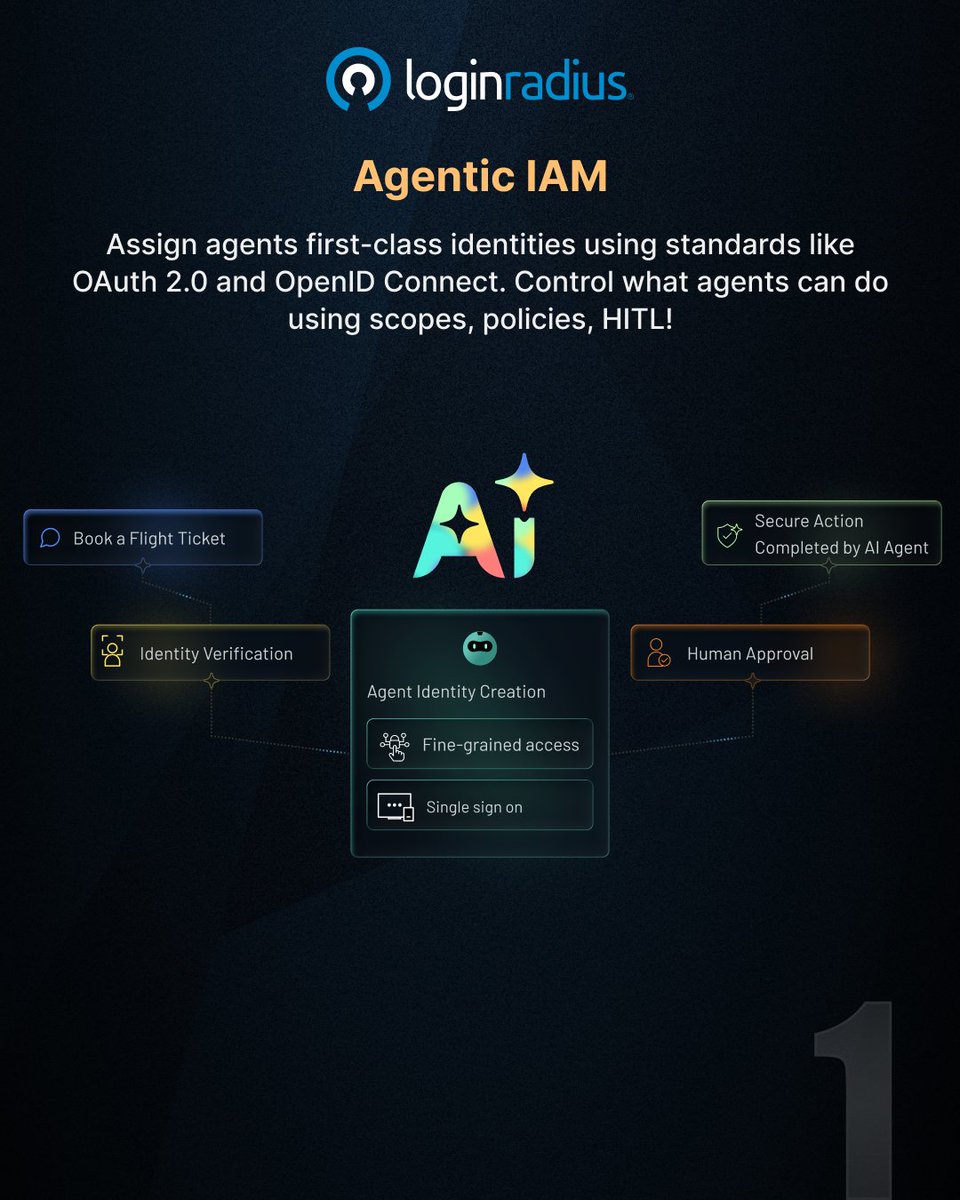
AI is now a partner in auth branding, risk-scoring, and more!
The Dawn of AI in identity. 🌅✨
#AgenticIAM#AIIdentity#FutureOfAuth#LoginRadius
While you're busy making memories and sharing gifts with the ones you love, we're working behind the scenes to keep your digital world safe.
Wishing you a season of pure magic and the peace of mind that comes with perfect security. 🎄🎁
#CyberSecurity#IdentityManagement #LoginRadius #MerryChristmas #DigitalIdentity
Global players will always be relevant. But it is more about how trust is enforced across users, machines, and agents in specific environments. Local context matters a lot more. That’s where domestic platforms can compete meaningfully, especially in identity, cloud, and API security.
@khalilApriday The next inflection point is machine and agent identities. Anyone entering IAM today should expect the field to extend well beyond human users.
Bot proliferation and deepfakes are forcing a rethink of how trust is established online. This gets at a core issue of the AI era. How do you establish trust without over-collecting identity data? Trust mechanisms that reduce reliance on static credentials while preserving privacy are going to matter a lot more.
This tracks with what we’re seeing across healthcare. Identity isn’t just an IT control anymore. It is foundational to patient safety, clinical access, and continuity of care. When clinicians can’t access systems reliably and securely, care slows down. That’s why IAM is becoming non-negotiable.
@origon This feels like the right direction for agentic systems. Once agents have memory, tools, and autonomy, identity and access boundaries become just as critical as orchestration.
Never a headline anyone wants to see. This is especially concerning because email server access tends to be one of those breaches where the full impact isn’t immediately visible. It’s not just about messages, but about how deeply email is woven into access, recovery, and coordination across systems, which raises the stakes of even a short-lived compromise.
This is the uncomfortable reality of identity sprawl. When dormant users and NHIs hold most of the power, risk becomes structural. NHIs are the real wake-up call. They don’t log in, don’t rotate naturally, and rarely get reviewed. Governance has to evolve past human-centric assumptions.
This fragmentation is exactly why passwords keep failing at scale. Federation, zero trust, and emerging decentralized models shift the focus from static credentials to continuous verification around who the user is, what they’re accessing, and under what conditions. That’s where security and usability finally align.
@eurofounder If you’re allowing personal devices for work, you also own the responsibility of defining what’s acceptable. A VPN by itself isn’t the issue, unclear boundaries are. Security protocols only work best when expectations and controls are established before access is ever granted.
@TheHackersNews Attackers didn’t get smarter users, they just got better at standing in the middle. That’s why the conversation is shifting from “add MFA” to “remove what can be replayed.”
@GoogleDeepMind If an agent can plan, find gaps, and roam the web without getting lost, that’s already more disciplined than most of my browsing sessions. Excited to see how it performs.