@TeamARKAD (Invite FR roster)
👤LFP
- 16+ yo | Fluent 🇫🇷
- Rank: Peak Immo 3+
- Role: Smoker
- XP: T2-T3, premier Invite, scrims, tournaments…
- Available for LANs
- Coachable, available, hard worker, good comms & team play.
📩DM Open
Team ARKAD 🔥 (Invite FR)
LF Assistant Coach
- XP T3-T2 min, T1 = plus
- Coaching indiv. + micro, praccs, scrims, officielles
- Objectifs court/moyen/long terme par joueur
- Profil crédible, qui sait s'imposer
- Bénévole, projet visant le T2-T1
DM Open 📩
Team ARKAD 🔥 (Invite FR)
LF Analyste
- XP T3-T2 min, T1 = plus
- Analyse de fond : scouting, stats, map/comp, rapports de scrims
- Retours individuels pour faire progresser chaque joueur
- Bénévole, projet visant le T2-T1
DM Open 📩
@TeamARKAD (Invite FR roster)
👤LFP
- 16+ yo | Fluent 🇫🇷
- Rank: Peak Immo 3+
- Role: Smoker
- XP: T2-T3, premier Invite, scrims, tournaments…
- Available for LANs
- Coachable, available, hard worker, good comms & team play.
📩DM Open
Team ARKAD 🔥 (Invite FR roster)
👤 **LF1**
- 16+ yo | Fluent 🇫🇷
- Rank: Peak Immo 3+
- Role: Smoker
- XP: T2-T3, premier Invite, scrims, tournaments…
- Available for LANs
- Coachable, available, hard worker, good comms & team play.
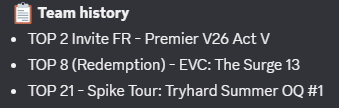
- TOP 2 Invite FR - Premier V26 Act V
LFT 2027
Resetting for the new year and hungrier than ever. Had a rough start to the year, but after a quick break, I’m fully recharged and ready to dominate!
Can flex any roles outside of Sentinel - Highest impact on Smoke or Duelist
DMs open for trials! RTs appreciated!
I am looking for new opportunities for 2027
My contract with Mandatory has ended so I’m exploring my option for the next season as duelist/flex but prefer duelist Open to all regions.
Contact in DM. VERY HYPE TO PLAY 🫡
LFT 2027
I am still under contract until end of 2026 with @NAVIValorant , but they allowed me to explore my options.
- Flex / smoker open to learn others roles
- Open to offers from all regions
I’m hungry and more motivated than ever for what’s next. I can’t wait to have another opportunity to show what I can do.
Contact : @Blitzcvt or [email protected]
🎁GIVEAWAY TIME !
On s'associe avec @o2switch pour vous faire gagner un petit bout d'Azeroth
À la clé :
🔥 La figurine Main de Ragnaros
🖥️ 1 an d'hébergement o2switch
🎁 Un pack de goodies o2switch
Facile de participer 👇
🔁 RT ce post
💙 Follow @o2switch et @MandatoryGG
Un bout de loot légendaire à la maison, ça vous tente ? 👀
⏳ Tirage au sort dans 7 jours !
Bonne chance à tous, que RNGesus soit avec vous 🍀
#MANDATORY #o2switch #WorldOfWarcraft #WoW
CONCOURS : LE MAILLOT DE L’ANNÉE ! 💙💙
On te fait gagner le maillot pro de la saison 2026 de la @KarmineCorp 🎁
Pour participer :
➡️ RT & like ce post
➡️ follow @celio & @KarmineCorp 🍀
Tirage au sort le 11/07 !
Un gros giveaway pour fêter notre victoire au Major Paris de Rocket League ça vous dit ? On dit merci Razer pour ce stuff de compétition 😁
À gagner :
🎧 1 casque Blackshark V3 Pro PS5
🎮 1 manette Raiju V3 Pro PS5
👕 1 maillot Eternals
Pour participer :
✅ RT + Like ce tweet
✅ Follow @KarmineCorp & @RazerFrance
🍀 TAS le 02/06, bonne chance à tous !
[SOURCES] France 🇫🇷 has set their VALORANT roster for the 2026 Esports Nations Cup:
🇫🇷 CyvOph
🇫🇷 Veqaj
🇫🇷 Kada
🇫🇷 sh1n
🇫🇷 TakaS
🇫🇷 Happy (HC)
Full Report by @anonimotum ⬇️
https://t.co/TsjclMKE4W
‼️🚨 BREAKING: An AI found a Linux kernel zero-day that roots every distribution since 2017. The exploit fits in 732 bytes of Python. Patch your kernel ASAP.
The vulnerability is CVE-2026-31431, nicknamed "Copy Fail," disclosed today by Theori. It has been sitting quietly in the Linux kernel for nine years.
Most Linux privilege-escalation bugs are picky. They need a precise timing window (a "race"), or specific kernel addresses leaked from somewhere, or careful tuning per distribution. Copy Fail needs none of that. It is a straight-line logic mistake that works on the first try, every time, on every mainstream Linux box.
The attacker just needs a normal user account on the machine. From there, the script asks the kernel to do some encryption work, abuses how that work is wired up, and ends up writing 4 bytes into a memory area called the "page cache" (Linux's high-speed copy of files in RAM). Those 4 bytes can be aimed at any program the system trusts, like /usr/bin/su, the shortcut to becoming root.
Result: the next time anyone runs that program, it lets the attacker in as root.
What should worry most: the corruption never touches the file on disk. It only exists in Linux's in-memory copy of that file. If you imaged the hard drive afterwards, the on-disk file would match the official package hash exactly. Reboot the machine, or just put it under memory pressure (any normal system load that needs the RAM), and the cached copy reloads fresh from disk.
Containers do not help either. The page cache is shared across the whole host, so a process inside a container can use this bug to compromise the underlying server and reach into other tenants.
The original sin was a 2017 "in-place optimization" in a kernel crypto module called algif_aead. It was meant to make encryption slightly faster. The change broke a critical safety assumption, and nobody noticed for nine years. That bug then rode every kernel update from 2017 to today.
This vulnerability affects the following:
🔴 Shared servers (dev boxes, jump hosts, build servers): any user becomes root
🔴 Kubernetes and container clusters: one compromised pod escapes to the host
🔴 CI runners (GitHub Actions, GitLab, Jenkins): a malicious pull request becomes root on the runner
🔴 Cloud platforms running user code (notebooks, agent sandboxes, serverless functions): a tenant becomes host root
Timeline:
🔴 March 23, 2026: reported to the Linux kernel security team
🔴 April 1: patch committed to mainline (commit a664bf3d603d)
🔴 April 22: CVE assigned
🔴 April 29: public disclosure
Mitigation: update your kernel to a build that includes mainline commit a664bf3d603d. If you cannot patch immediately, turn off the vulnerable module:
echo "install algif_aead /bin/false" > /etc/modprobe.d/disable-algif.conf
rmmod algif_aead 2>/dev/null || true
For environments that run untrusted code (containers, sandboxes, CI runners), block access to the kernel's AF_ALG crypto interface entirely, even after patching. Almost nothing legitimate needs it, and blocking it shuts the door on this whole class of bug...
@VeqajVLR Ils ont fait un très bon choix. Depuis que je t'ai vu en ligue française j'ai toujours pensé que tu méritais de jouer en VCT avec le niveau que tu montrais. En tant qu'enjoyer de MDR et fan KC mais avant tout fan de Valo je te souhaites de réussir ton année pro chez FNC !
Les #VALORANTChampions c'est terminé, mais on continue de vous régaler !
On vous fait gagner :
🔸 9 pulls à capuche Born to Burn
🔸 20 t-shirts Born to Burn
Pour participer : Follow @OMENbyHP_fr et RT+like ce post
Dis-nous en commentaires lequel tu aimerais bien.
TAS dimanche
We lose 2-3 to @NRGgg
What a year we’ve had. So many core memories despite no trophy! Thank you for sharing them with me!❤️
ON THAT NOTE.. WE WON’T STOP UNTIL WE LIFT A TROPHY AGAIN. I WILL WORK MY SOCKS OFF FOR IT!!!🕺
#GetYourBoastees