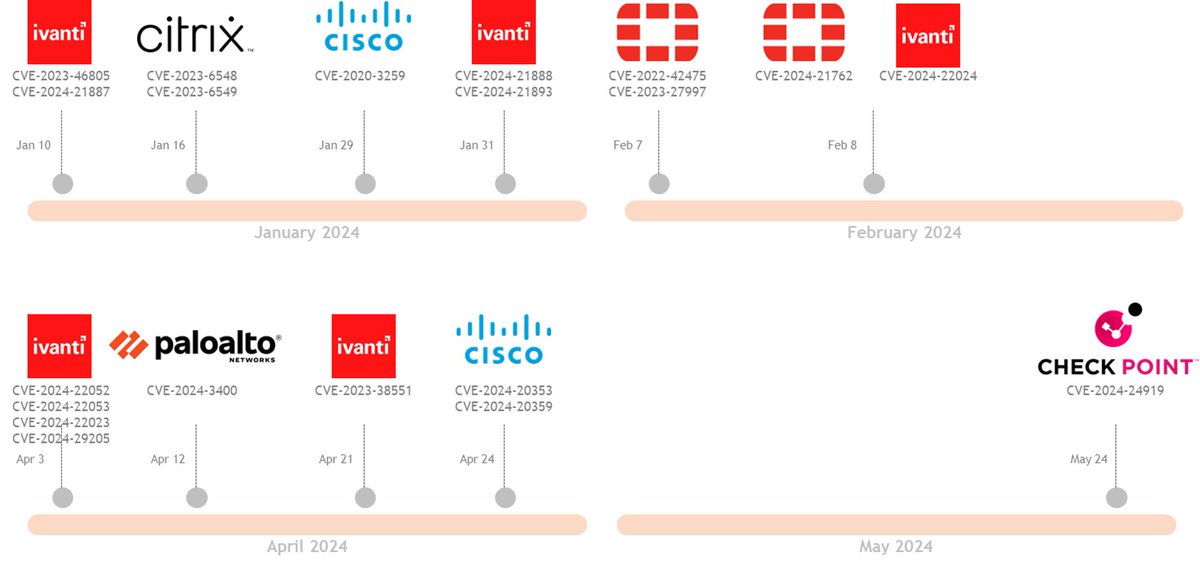
🚨9.8 vulnerability reported for Ivanti🚨
Zero Day Initiative reported a 9.8 vuln for Ivanti is incoming. No word on which product.
Someone wanna work on some cyber threat memetelligence? I need coffee… ☕️
Ivanti a publié des correctifs pour de nouvelles vulnérabilités affectant Connect Secure et Policy Secure Gateways. Elles pourraient conduire à l'exécution de code arbitraire ou à un déni de service (DoS). External ICT a également été mis à jour.
https://t.co/ol9PKZtksC
🔐📱iOS 17.4 corrige 4 failles de sécurité
Apple a publié la mise à jour iOS 17.4 qui corrige des failles de sécurité importantes, dont 2 activement exploitées par des pirates.
Failles corrigées :
- 2 failles du noyau permettant de contourner les protections de mémoire du noyau.
- 1 faille d'Accessibility permettant à une application de lire des informations de localisation sensibles.
- 1 faille de Safari Private Browsing pouvant afficher brièvement des onglets verrouillés.
Mettez à jour votre appareil dès que possible pour bénéficier de ces correctifs de sécurité.
2023 Zero-day vulnerabilities Summary
R1 - 14 Jan 2024
H/T @uuallan@pancak3lullz for the original idea
(I was missing yours, so I made my own but included all zerodays, not just initial access for ransomware as the original was.)
"Apple's "Find My" location network can be abused by malicious actors to stealthily transmit sensitive information captured by keyloggers installed in keyboards.
https://t.co/i6Aos0qETd
Tempête #Ciaran en approche… Apéro avec quelques plans de #Eunice 😊 Avec @erwan_poirier29 , on croise les doigts pour que la lumière soit au rendez-vous avec une mer déchaînée !
https://t.co/1nrEmj6u9o ⚓️
September, 2023: Nicknamed, "#BloodyTokens ", Microsoft misconfigured an #Azure storage bucket exposing over 30,000 internal #Microsoft#Teams messages and 38TB of private AI research data
Enforce #privacy & #security best-practices on #Windows, #macOS and #Linux, because privacy is sexy !
Web site: https://t.co/D22fJG8KPv
Open source tools: https://t.co/OiC4jrpnfE
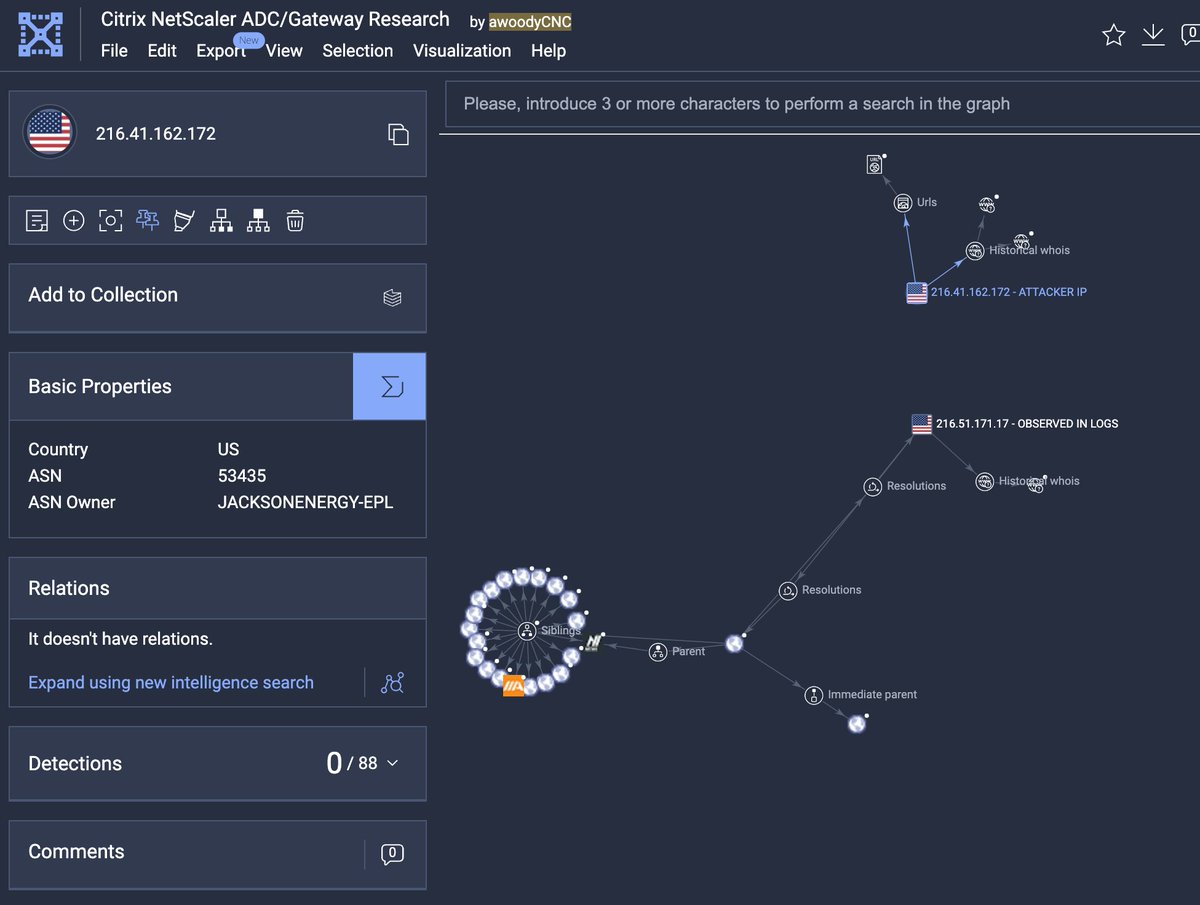
Finally! Someone put the two IP IOCs related to the #Citrix Netscaler ADC vuln CVE-2023-3519 in a Virustotal Graph, which allows me to share them
216[.]41[.]162[.]172
216[.]51[.]171[.]17
https://t.co/gmZaVnzkC6
On June 17, 2023, a new initial access broker under the alias "Br0k3r" registered on one of the underground forums. The Group-IB Threat Intelligence team has found out that this threat actor is one of the first to conduct private access sales through their own website: brok3r7bhcblynwpoymgarr6zwcy4ttfbhkhcmotz4lw2gcsuojgaeqd[.]onion
As shown in the screenshots, the threat actor offers to sell access to companies worldwide, including domain administrator credentials, active directory users credentials, DNS zones and other information about the victim's network.
A total of 45 initial accesses to corporate networks of different companies were available for sale and 2 accesses have been sold. The discovered access offers are related mostly to US, UK, UAE, Taiwan, and Switzerland companies. The largest number of victims were found in the following sectors: healthcare, real estate, financial services, transportation, and manufacturing.
Companies' revenue ranges from at least $5 million to $1.2 billion, which indicates security issues in both small companies and big corporations, regardless of company location and industry. Just like we predicted in the Hi-Tech Crime Trends 22/23 report, initial access brokers are one of the top threats to watch in 2023👀 https://t.co/qpSyPLqX75
#DarkWeb #InitialAccessBroker #CorporateNetwork