FINALLY, THE VIDEO IS LIVE! 🔥
If this video gets 1K likes and similar engagement to the recent one, I’ll drop the next video showing how to create custom Claude Skills using:
• Medium articles
• H1 disclosed bug bounty reports
• My own personal bug-hunting methods
• Open-source bug-hunting skills
I’ll also add the prompts used in this video and the upcoming video to my Medium articles, along with a more detailed guide.
https://t.co/Hcp0Dr2wJ0
Finally, the wait is over! 🔥
I know a lot of beginners have been waiting for this because there hasn’t been a single complete guide showing how to set up Claude Code for bug bounty hunting and using the DeepSeek API at a very affordable cost.
In this video, I’ll walk you through the entire setup step by step, and you’ll also see how powerful DeepSeek V4 Flash is for real-world bug hunting tasks.
Trust me, the results will surprise you.
🎥 Watch now and level up your bug hunting workflow.
https://t.co/tOnpkzGKq0
Nebula Security is now backed by Y Combinator.
We’re celebrating by bringing you the world’s first Android 17 root demo — “IonStack”, a url click can let attacker fully control your phone.
This is not only an Android root demo. We’re bringing you a full chain browser-to-kernel exploit with two 0-day vulnerabilities affecting Firefox before v151.0.2 and all Linux distros in 15 years. "IonStack" demonstrates how bad actors can control your phone by sending a malicious URL, but good news, Nebula Security found it before attackers do.
Both 0-day were found by our code scanning agent, VEGA, overshadowing any vulnerabilities found by Mythos or any scanner you name it.
VEGA has demonstrated its extraordinary capability in finding critical bugs in the world’s most complicated software: operating systems and browsers. It can spot the same vulnerabilities in your codebase too.
VEGA support full scan and incremental scan that can integrated into your CI/CD flow. We launched VEGA within YC companies and received overwhelmingly positive feedback. Now it is open to all enterprise customers in private beta.
Book a demo with us: https://t.co/eXHKhnE8gC
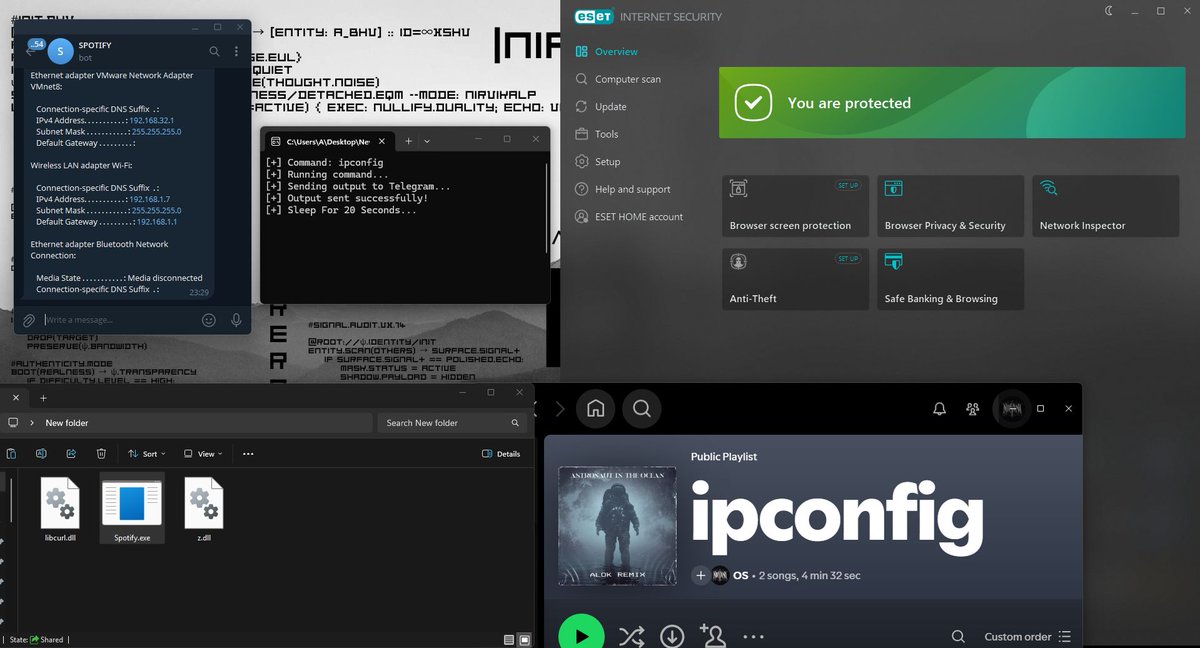
Your firewall sees Spotify traffic.
It may not see a command channel.
Came across SpotifyC2, a Windows security research PoC that uses:
- Spotify playlist titles to deliver commands
- A local client to execute them
- Telegram to return the output
No traditional C2 server.
No obviously malicious infrastructure.
Just trusted cloud services being used in ways defenders may not expect.
A useful reminder: allowlisting a domain does not mean the activity behind it is safe.
Interesting research for anyone working in threat detection, EDR, network security, or cloud abuse detection.
Tool: https://t.co/cknPN7q7BY