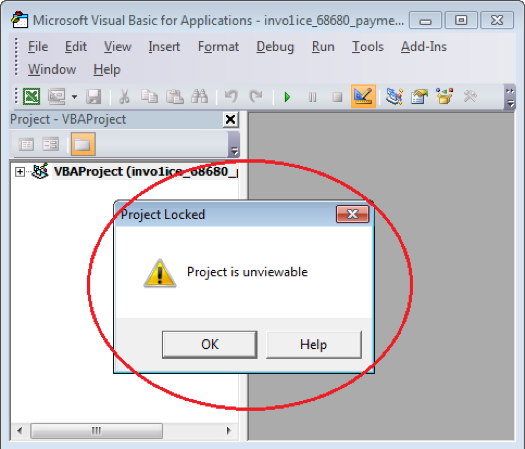
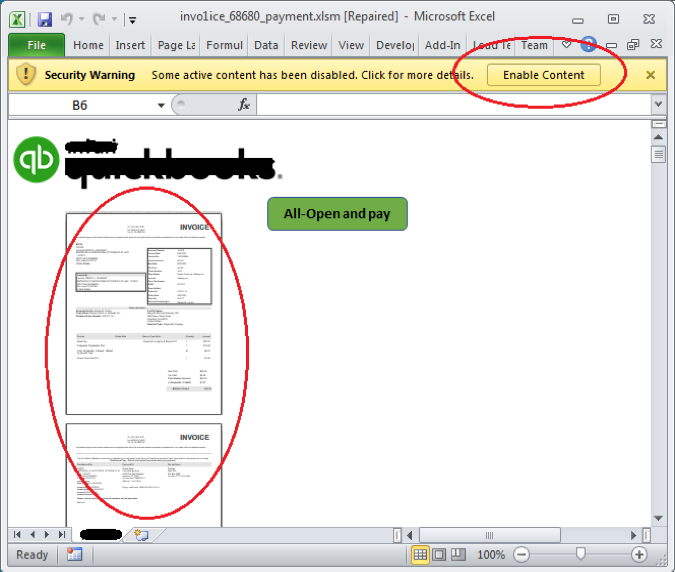
Watch Out! A new #malware campaign spreading QakBot banking trojan returned with new tricks up its sleeve to target government, military, and manufacturing sectors.
Read more: https://t.co/E2EirRIUBS
#infosec#cybersecurity
Days ago, #FortiGuardLabs captured a #phishing campaign leveraging a malicious MSFT Excel doc delivered as an email attachment and spread with a new variant of #Dridex Trojan #malware. Learn how it is capable of stealing sensitive info from its victims: https://t.co/8GnN9k3zYM
Your company may be contacted by a non-malicious hacker who found a vulnerability on your website. Here is what you should do in response to such a message to avoid public uncoordinated vulnerability disclosure. #Advisory#Security#VulnerabilityDisclosure https://t.co/pWDB5kM1uK
Schon unseren aktuellen Job des Monats gesehen? Wir suchen einen
Network and Security Support Engineer zur Unterstützung unseres Teams in Hagen. Interesse geweckt? Dann schnell zum Blogbeitrag: https://t.co/iSF5C7R4EG #ITJobs#Jobs#IT
#Phishing attacks are an all-too-common occurrence in both corporate and personal networks. Here are some tips to help you recognize the warning signs of a scam: https://t.co/S6Q6IYjems
In a malicious MS Word doc, we recently discovered an auto-executable malicious VBA code that can spread and install NanoCore RAT software on a victim’s Windows system. Here's how it propogates: https://t.co/IQmJ4TYzny