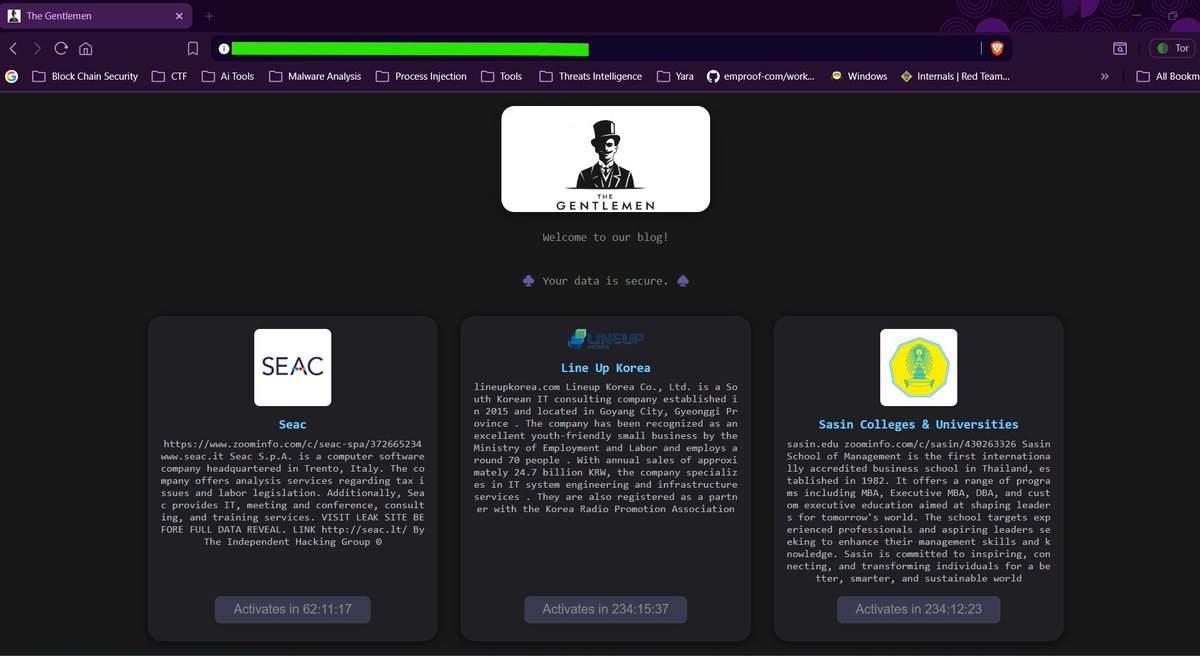
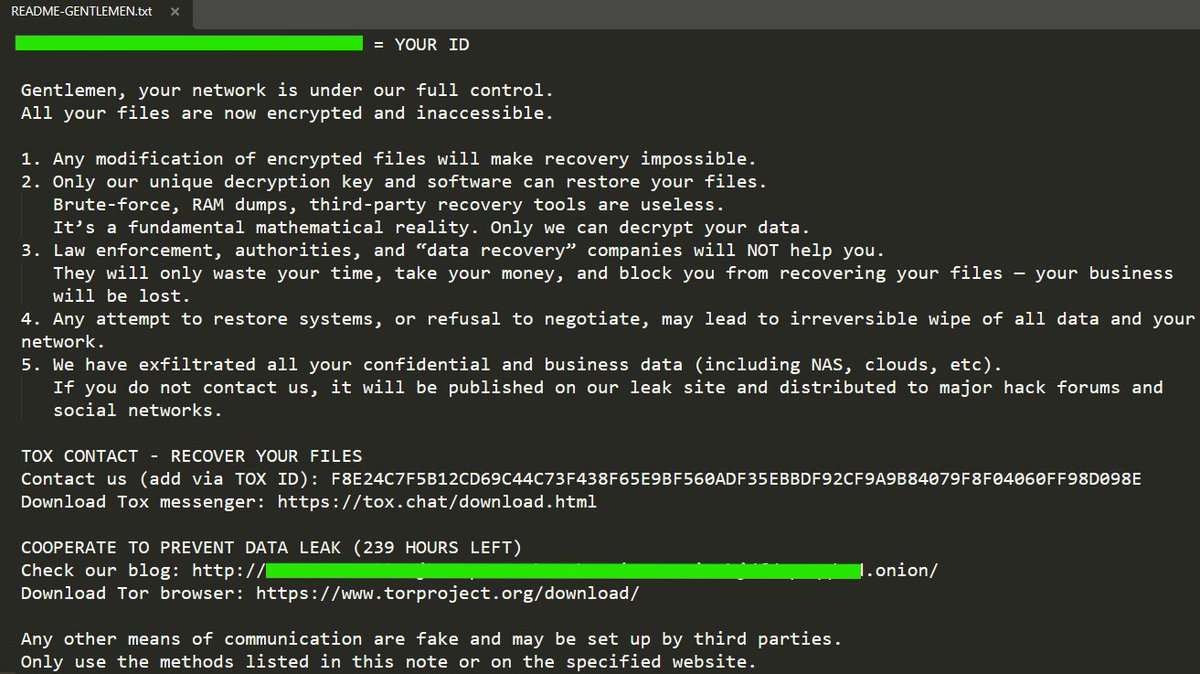
Published my first Threat Intelligence Report on The Gentlemen Ransomware Group.
I analyze the attack lifecycle, execution behavior, encryption logic, target regions, and MITRE ATT&CK mapping.
Report: https://t.co/tfeT5Jl33q
#ThreatIntelligence#Ransomware
صباح الفل
محتاج حد full stack يكون شاطر و اشتغل علي اكتر من project و اتعامل مع payment gateways
يكون متفرغ الشهرين الجايين دول , ابعتلي الCV في رسالة و لينك لمشروع او اتنين اشتغلت عليهم قبل كدا
❗️ Samsung's Galaxy S26 was remotely hacked three times on Day One of Pwn2Own Ireland, while Google's Pixel 10 survived a $300,000 attempt.
Researchers earned $388,500 for 32 zero-days and also broke LiteLLM, Sonos, Philips Hue, Oracle's Autonomous AI Database and OpenAI Codex.
VinSOC leads with $97,500 as Day Two gets underway with KAIST targeting the Pixel 10 over USB.
🥷 Now we can inject a payload into a remote process without using VirtualAllocEx and WriteProcessMemory.
No need to suspend the target process
New technique to evade EDRs:
Github: TwoSevenOneT/InjectSetConsole
#redteam#pentest#antimalware
Hijacked YouTube channels are pushing an emerging infostealer.
We're tracking #REVSTEALER: at least 17 compromised channels advertising free game cheats, funneling viewers to 2 malicious domains.
The stealer itself is built for long-term operation:
- Sandbox scoring: 10 weighted checks, self-terminates at a score of 7+
- App-Bound Encryption bypass: reads the decrypted key from browser memory under debugger control
- EtherHiding: fallback C2 stored in a Polygon smart contract, swappable without touching the binary
- Gaming focus: session cookies from Steam, Battlenet, and Roblox, feeding account resale markets
- 4,700 related samples hit VirusTotal in the past year.
Our team observed 4 follow-on modules that haven't been publicly documented until now.
Full analysis, whitepaper, YARA rule, and an IDAPython string decryption tool by @k33b0i, @soolidsnakee and @DanielStepanic:
Blog: https://t.co/4jGSZ2Tidg
Whitepaper: https://t.co/P8yqn0uCdT
I just published a detailed analysis about Stealc info stealer, a deep dive article about C/C++ stealer, the report involves
- in detailed code analysis
- config extractor
- yara rule
- IOCs
https://t.co/Daieg4YF1M