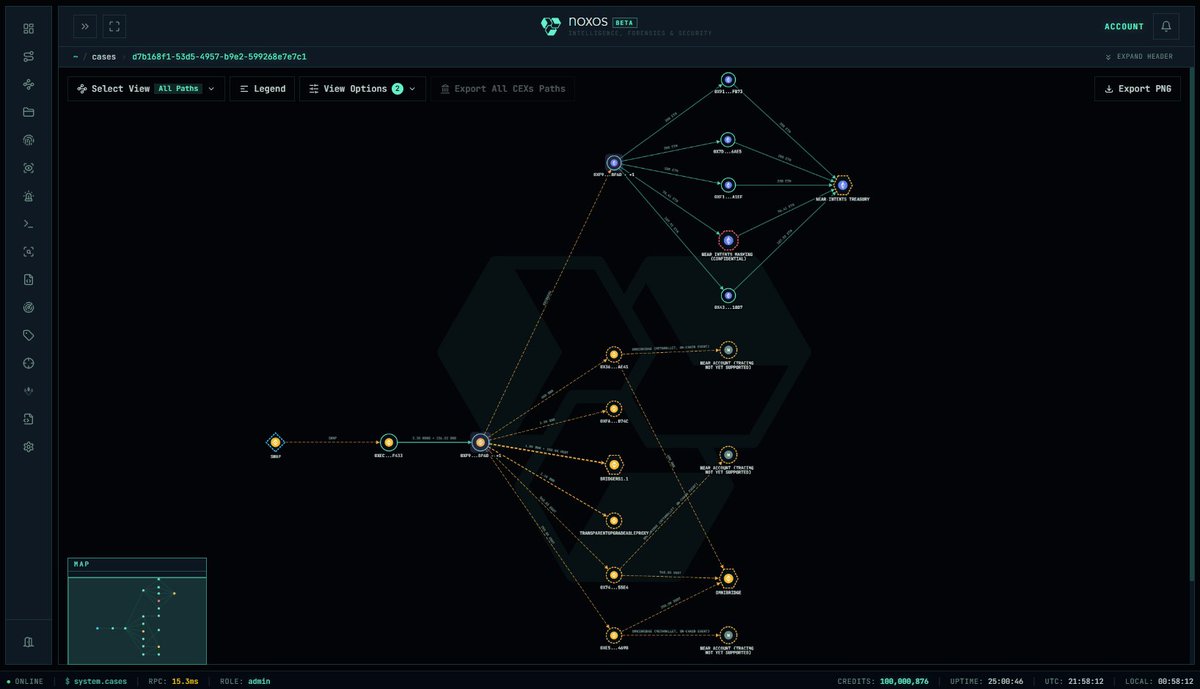
It looks like the same malicious actor hit @Barn_Bridge again. This time for $118K:
https://t.co/sGU8aVxFNM
The funds were converted to 64 $ETH and transferred to the same address holding the remaining 415 #ETH from the yesterday attack:
https://t.co/ynHbxk3zW3
Noxos Intelligence will keep monitoring the case!
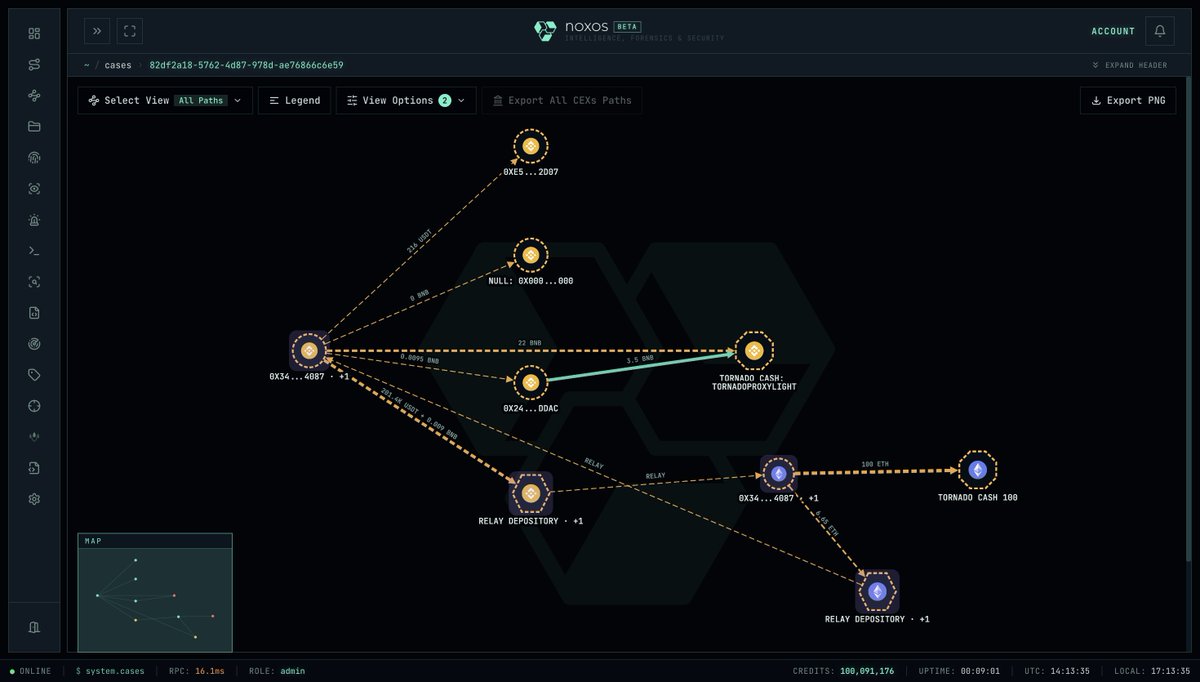
On July 16th, CrowdRingCircle (众环CRC) was exploited, with total losses of ~$200k.
We ran an investigation with our HYDRA engine and found that the funds were routed (obfuscated) through the Relay bridge.
22 $BNB were deposited to #TornadoCash on #BSC.
The rest was bridged to #Ethereum, where 100 $ETH were deposited to #TornadoCash.
Earlier today we spotted an X post from two weeks ago where a user shared that his wallet had been compromised — $150k lost across various assets on #Solana.
We ran a quick scan with our HYDRA engine and traced the funds to a #Binance deposit of 10,000 $SOL.
For anyone still wondering: HYDRA isn't just for EVM chains.
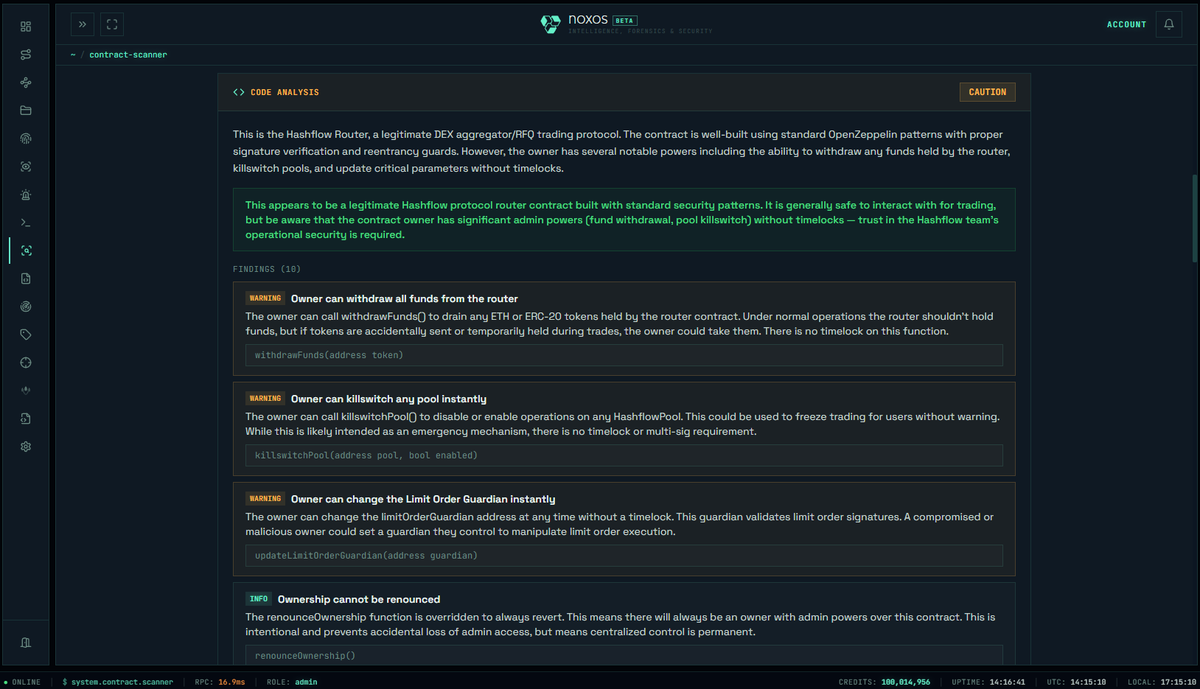
Meet PROMETHEUS — the engine built for everyone in Web3.
For investigators: when funds hit an unknown contract address and you're not sure how to treat it — is it a swap? A stake? A contract built purely for obfuscation? PROMETHEUS saves you time and keeps you on the right path.
For traders and daily on-chain users: find out what a contract actually does before you interact with it. That knowledge saves money, headaches, and a lot of bitter lessons.
For protocol owners: about to partner with or integrate an external protocol? Check it first.
The built-in Code Analyzer breaks down contract behavior in detail, so you can interact with confidence.
#SmartContractSecurity #Web3Security #DeFi #OnChain #Crypto
We traced the funds from the @42dao_official exploit, which caused losses of ~$1M.
Most of the funds were bridged from BNB Smart Chain to Ethereum.
The funds were deposited into Railgun on both chains — $3k $USDT on #BSC and $1M $USDC on #ETH.
The case is under monitoring.
Noxos Intelligence's CERBERUS monitoring engine alerted us that the malicious actor has begun laundering the stolen assets from the @Barn_Bridge protocol exploit through #TornadoCash, in multiple deposits of 1 and 10 #ETH.
Another 148 $ETH was transferred to a separate wallet five days ago on the #Ethereum chain:
0x6e6738C1a4b58588E4e9Ec74A9072978b09E78df
The funds remain dormant there.
On July 22, @BSquaredNetwork was exploited for 8.591M B2 tokens worth ~$3.8M.
The malicious actor bridged the funds from BNB Smart Chain to Ethereum using bridges including Near Intents (via masked transactions) and Bridgers.
Laundering of the proceeds continued on Ethereum, again through Near Intents masked transactions:
https://t.co/KtlxlZEBDJ
Noxos Intelligence will keep monitoring the case.
Yesterday, July 23, the @VerusCoin Ethereum bridge was exploited for ~$7.5M.
The attacker drained a mix of assets — ETH, tBTC, scrvUSD, USDC, USDT, EURC, and MKR — then routed everything through Relay, consolidating into 3,900 ETH.
From there, the funds were deposited into Tornado Cash in batches of 100 ETH.
Links ⬇️
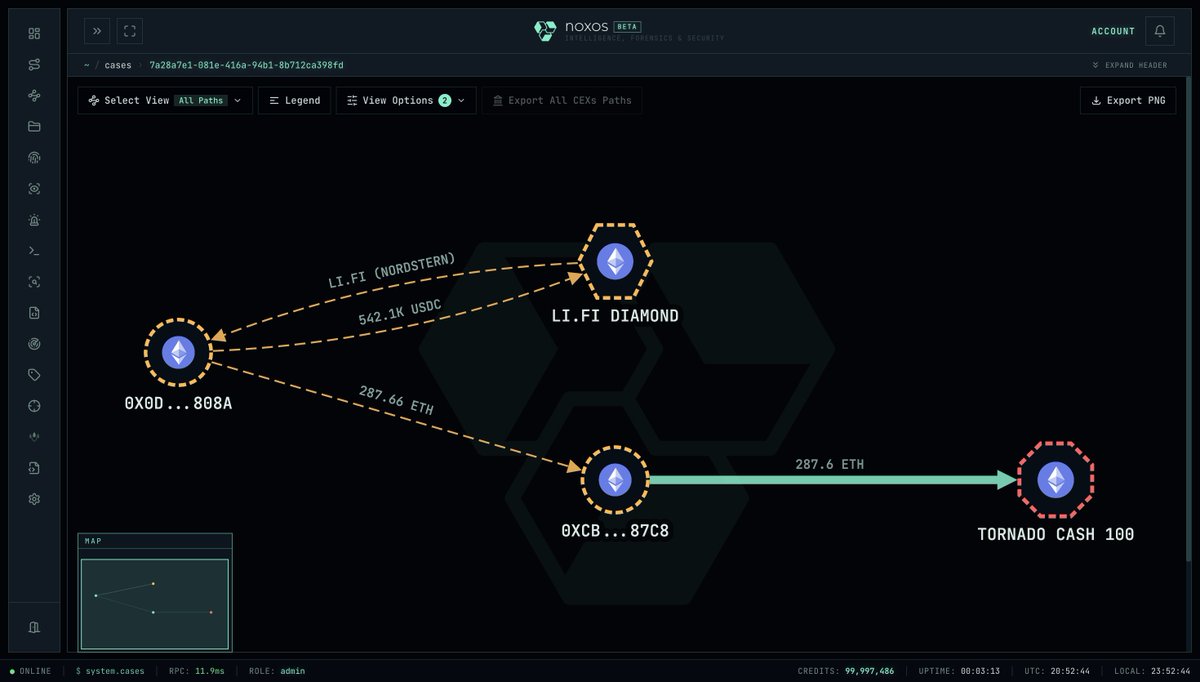
On July 24th, DeBond protocol was exploited for ~$542K.
Noxos Intelligence's HYDRA engine traced the flow: the stolen 542K #USDC was swapped for #ETH via LiFi, moved to a fresh wallet, then deposited into Tornado Cash — as shown in the image.
Noxos Intelligence isn't just for investigators — we're building tools for everyday on-chain users too.
PROMETHEUS, our smart contract checker, is one of them. Scan any contract before you interact and avoid walking into a trap. https://t.co/tK1bLL6cZe
Most crypto crimes end up in the same place: Railgun, Tornado Cash, Blender, and the rest.
Malicious actors rely on mixers, blenders, and choppers — the whole kitchen — to launder stolen assets. It's no secret that once funds enter these protocols, they effectively step into the dark forest. But that shouldn't automatically mean a dead end for tracing, stamped "Case Closed."
We've been aware of this problem since Noxos Intelligence was just a name on a whiteboard, and we started asking ourselves "What can we do about it?" from day one.
That's why we're announcing that Noxos Intelligence's De-Anonymizator is officially under development.
It's a hard problem — complex architecture, heavy infrastructure — so support for different protocols will roll out in stages, and access will be tightly controlled to prevent abuse. We want to stop the bad guys, not help them. From what we've seen in testing so far, the results are promising. And honestly, even a single crime solved by our engine will be reward enough for the effort.
In the meantime, we'll keep testing and fine-tuning our flagship HYDRA tracing engine against real exploits reported to the public — and we'll keep demonstrating the power of Noxos Intelligence here on our X account regularly.
We've also had people reach out asking to put our engine through its paces before we go live. So if you're a crypto crime investigator — or just an enthusiast who wants in — feel free to contact us and join the testing team.
We're aiming to officially launch the software workstation in the upcoming weeks.
So keep an eye on this account, stay tuned, and most importantly — stay safe!
A live demo of HYDRA, the tracing engine behind Noxos Intelligence.
Follow illicit money across chains. Built for private investigators, businesses, and law enforcement.
got drained for 1.24 SOL ($102.71) 3 days ago, just saw
idk how this happened 😭
I didn't connect my wallet to any site or something...
trx was made from:
-ChY2GxYJvm3GgA3t58R7ueseydFwPQXpw3M5BMNxe7Lq (my wallet)
to
-2nihkn5Bcbyf1viHHrcCamM9mRgKA2AGW6hjqV7udSY5
need help..
@ChanniGreenwall Exactly. That’s the shift we’re pushing toward — from “trust the team” to “verify the logic.” If users can’t inspect or understand the contract, they’re relying on reputation by default, and that’s where most exploits hide.
Crypto scams happen every day, and many rely on malicious smart contracts to harm people.
A favorite tactic is leaving the contract code unverified, making it harder for everyday users to spot the trap.
Noxos Intelligence's LANTERN engine is built to expose those traps and protect you. It doesn't just reconstruct the code — it detects malicious intent and gives you a full explanation of the contract's logic.
Stay safe!
#CryptoSecurity #Phishing #CryptoScam
Yesterday, several investigators flagged that the 10.6K $ETH (~$18.5M) from the #HashFlare scam — untouched for over 3.5 years — had started moving.
We took the opportunity to test our engine against a real-world case, and the results are astonishing.
Tracing through bridges, and instant exchanges like Near Intents, HiFi, Aeroswap, and ChangeHero we followed the flow and part of the funds are now moved to $BTC.
Soon, you will be able to trace funds easily and get trustworthy data at an affordable price.
Today we are one step closer.🫡